A solution to operationalize actionable data and insights to secure any organization. Anomali ThreatStream provides curated access to the a global repository of threat intelligence, delivering enrichment, contextualization, and detection of known and emerging threats.
N/A
Trellix Helix
Score7.1 out of 10
Enterprise companies (1,001+ employees)
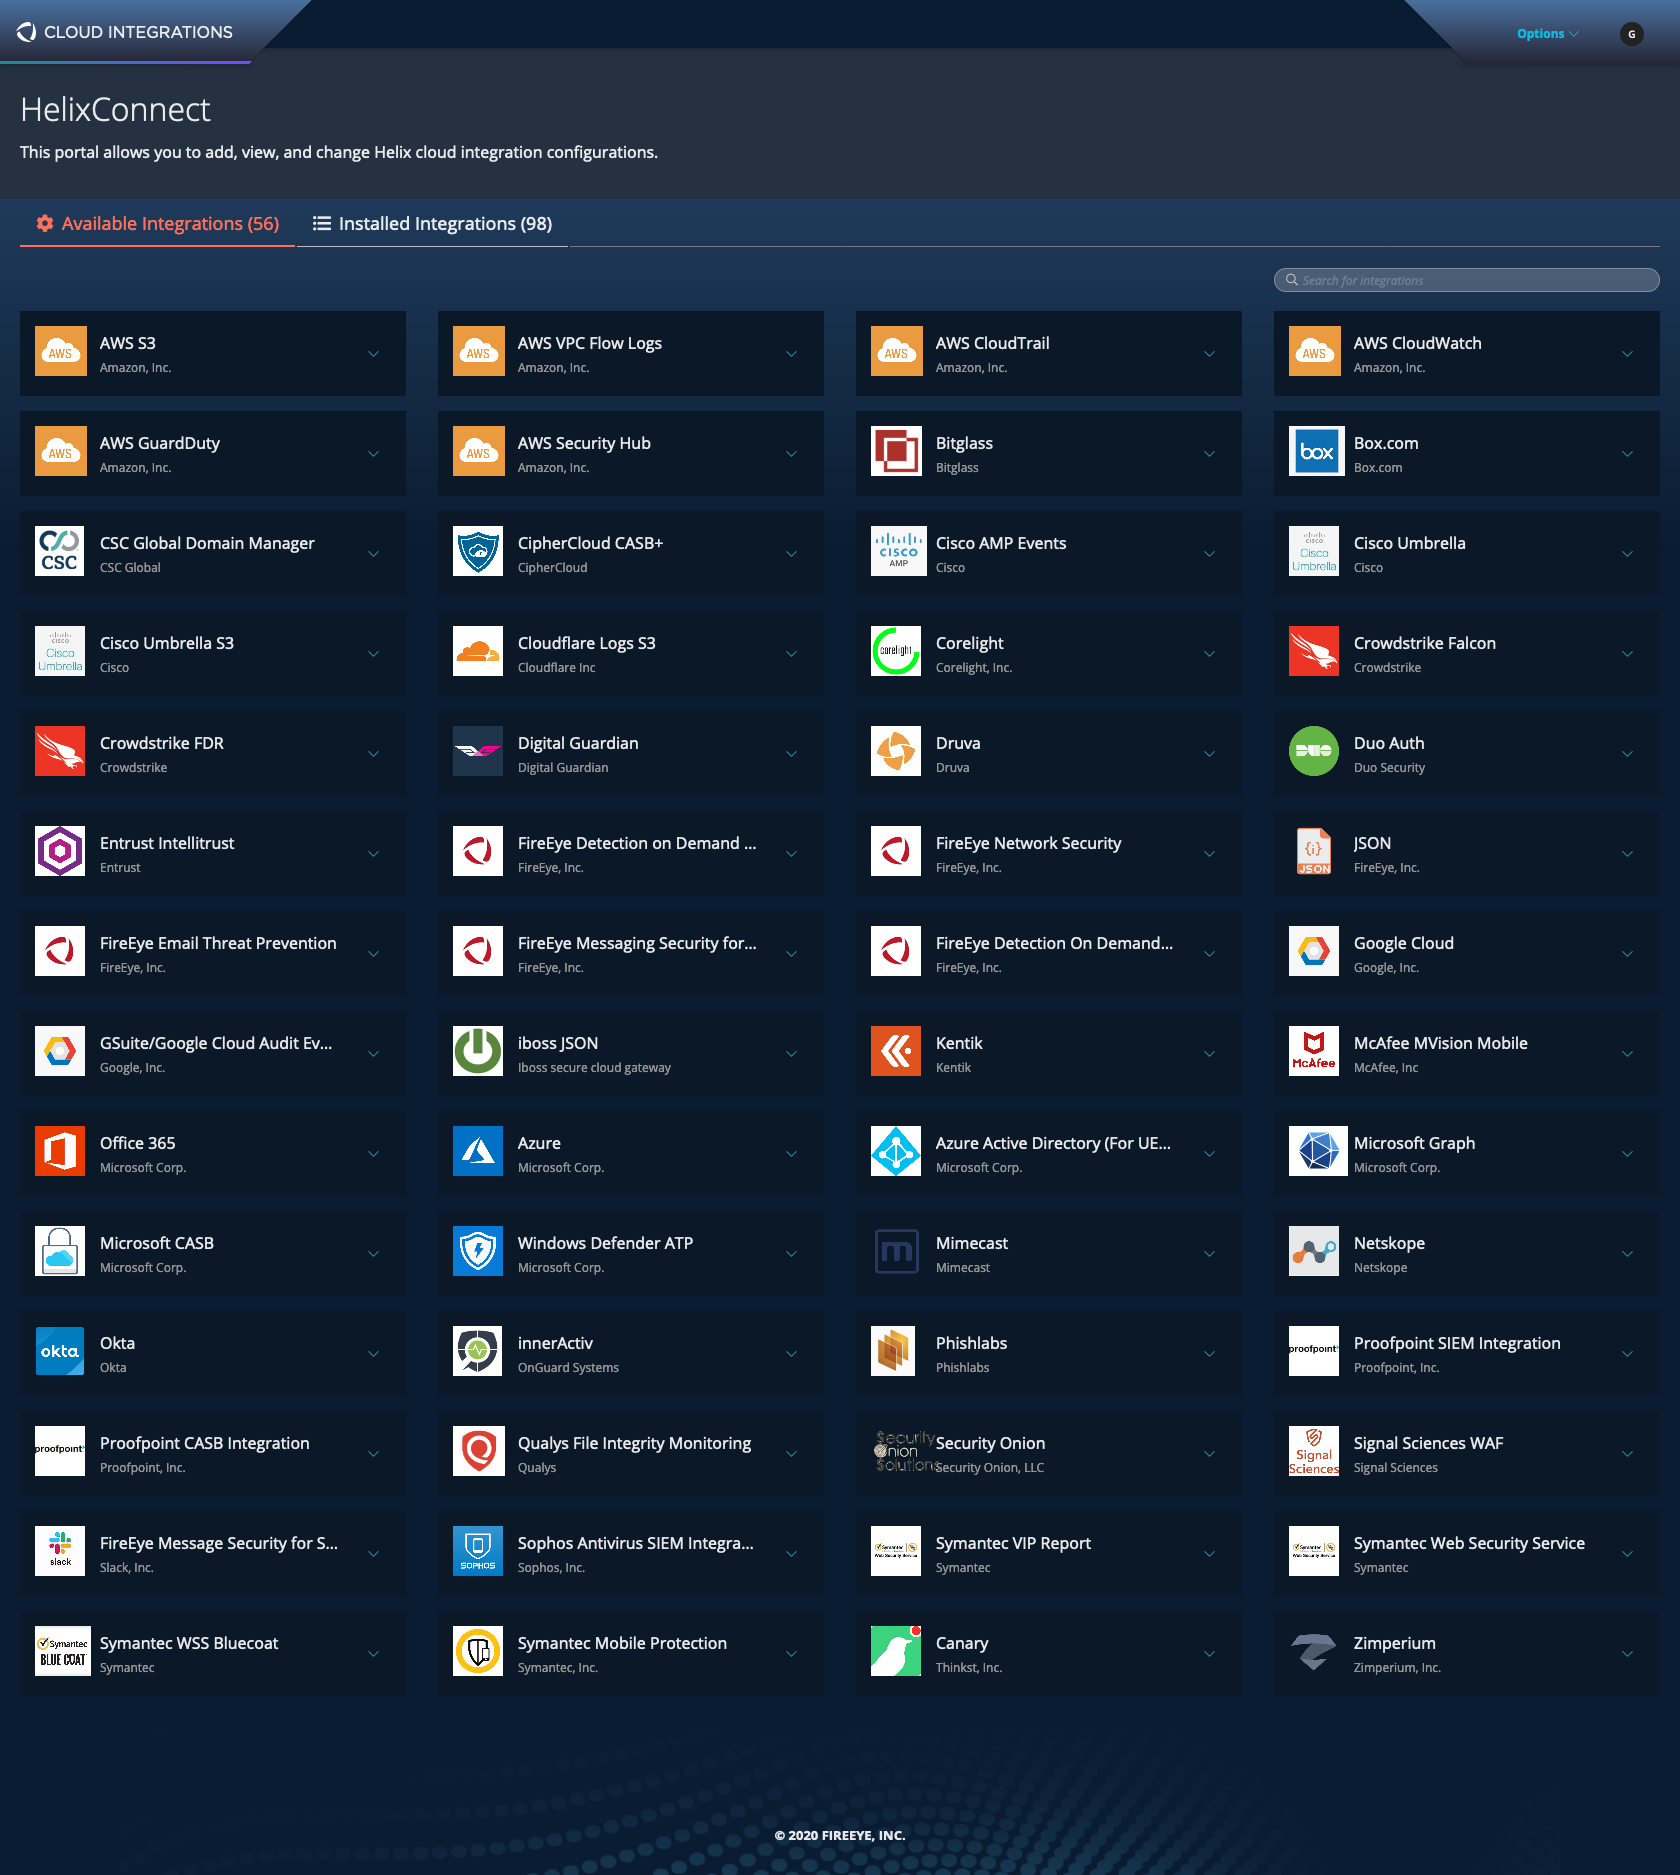
Trellix Helix (formerly FireEye Helix) is a SIEM solution providing a non-malware threat detection solution.
$0
Events per second
Pricing
Anomali ThreatStream
Trellix Helix
Editions & Modules
No answers on this topic
Helix Console
$0
Events per second
Helix Enterprise
$0
Events per second
Offerings
Pricing Offerings
Anomali ThreatStream
Trellix Helix
Free Trial
No
No
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
Yes
Entry-level Setup Fee
No setup fee
Optional
Additional Details
—
—
More Pricing Information
Features
Anomali ThreatStream
Trellix Helix
Security Information and Event Management (SIEM)
Comparison of Security Information and Event Management (SIEM) features of Anomali ThreatStream and Trellix Helix
Feature
Anomali ThreatStream
-
Ratings
Trellix Helix
9.6
3 Ratings
19% above category average
Centralized event and log data collection
00 Ratings
9.93 Ratings
Correlation
00 Ratings
9.93 Ratings
Event and log normalization/management
00 Ratings
9.03 Ratings
Deployment flexibility
00 Ratings
9.73 Ratings
Integration with Identity and Access Management Tools
Anomali ThreatStream is excellent in scenarios where we deliver Managed Security Services to customers. It offers exhaustive volumes of information in the form of threat bulletins, IOCs, Threat Actor profiling, and details related to campaigns in the wild which can be used to a great extent by MSSPs. For an enterprise SOC, I believe it is a little less suited purely because of the pricing aspect as it is slightly towards the expensive side of the spectrum.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Great for organizations that are considering improving their operational security by utilizing their threats intelligence capabilities. It offers a great collection and analysis of security events and provides solutions to solve them. When considering a solution that is secure and can provide very extensive visualization of your environment for threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The user interface, perhaps there is some room for improvement although it is good already.
Confidence assigning process for IOCs needs to be more robust and transparent.
While integration with SIEM solutions is a cakewalk, there is definitely added value if SIGMA rule conversion and YARA rule creation are provided from the platform.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Many of the products that can be used to be ingested into a security event management software can be cumbersome with threat streamThere are many opportunities to continue fine-tuning the environment and providing great context in regards to threat research. When compared to other products threat stream stands out from usability and features.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It offers extensive visibility thus easy detection of threats and easy mitigation practices. Utilization of its threats intelligence capabilities thus early detection of incidents and maximization of security investments. Offers great integration of cloud resources with existing security tools thus ensuring seamless performance and all-time security for the organizational resources.
We have seen a positive ROI as the security monitoring is taken to the next level when it is augmented with threat intel data that Anomali provides.
Our customers are very satisfied with the periodic threat reports that we send, which are created using Anomali ThreatStream.
The overall business objectives are met as Threat Intel is one of the most important pillars when it comes to providing security services, and we use Anomali ThreatStream extensively for that.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info