TrustRadius: an HG Insights company

Appknox vs. Black Duck Software Composition Analysis (SCA)

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Appknox

    N/AN/AAppknox is an on-demand mobile application security platform designed to help Developers, Security Researchers, and Enterprises to build a safe and secure mobile ecosystem using a system plus human approach to outsmart hackers. The vendor states they have been successful in reducing delivery timelines, manpower costs & mitigating security threats for Global Banks and Enterprises in 10 + countries. Appknox…N/A

    Black Duck Software Composition Analysis (SCA)

    Score10 out of 10
    N/ABlack Duck is a software composition analysis tool acquired and now supported by Synopsys since 2017.N/A
    Pricing
    AppknoxBlack Duck Software Composition Analysis (SCA)
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    AppknoxBlack Duck Software Composition Analysis (SCA)
    Free Trial
    YesNo
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    YesYes
    Entry-level Setup FeeOptionalOptional
    Additional DetailsContact the Synopsys Software Integrity Group (SIG) Sales team at https://www.synopsys.com/software-integrity/contact-sales.html for more detailed pricing information.
    More Pricing Information
    Best Alternatives
    AppknoxBlack Duck Software Composition Analysis (SCA)
    Small Businesses
    Rencore Code (SPCAF)
    Score8.8 out of 10
    No answers on this topic
    Medium-sized Companies
    Trend Vision One Email and Collaboration Security
    Score9.9 out of 10
    No answers on this topic
    Enterprises
    Checkmarx
    Score7.6 out of 10
    No answers on this topic
    All AlternativesView all alternativesView all alternatives
    User Ratings
    AppknoxBlack Duck Software Composition Analysis (SCA)
    Likelihood to Recommend
    -
    (0 ratings)
    10.0
    (5 ratings)
    Usability
    -
    (0 ratings)
    8.0
    (1 ratings)
    Support Rating
    -
    (0 ratings)
    8.2
    (2 ratings)
    User Testimonials
    AppknoxBlack Duck Software Composition Analysis (SCA)
    Likelihood to Recommend
    Appknox
    No answers on this topic
    Black Duck Software
    If you are using a lot of open-source libraries, which is most likely, this is a must-have to ensure no known vulnerabilities slip into production
    Incentivized
    Read full review
    Pros
    Appknox
    No answers on this topic
    Black Duck Software
    • Quick inventory scan: Black Duck helps us scan the code repositories in no time. And quickly list the components and I now really know what is in my code.
    • Security and License risk management: Black Duck being rich in its knowledge base about the vulnerabilities and license issues of open source components, quickly compares the identified inventory to the Black Duck knowledge base and lists all the vulnerabilities and license issues in the code.
    • Integration for automatic scanning: Black Duck is part of devops which provides us automatic scanning. Black Duck is not just for devops but also SecOps.
    Incentivized
    Read full review
    Cons
    Appknox
    No answers on this topic
    Black Duck Software
    • License model based on usage is costly.
    • Documentation is extensive, but often confusing.
    • Black Duck Hub could use some feature improvements for more robust governance capabilities
    Incentivized
    Read full review
    Usability
    Appknox
    No answers on this topic
    Black Duck Software
    If you don’t know how to scan for the language, it isn’t entirely user friendly
    Incentivized
    Read full review
    Support Rating
    Appknox
    No answers on this topic
    Black Duck Software
    Support seems very responsive.
    Incentivized
    Read full review
    Alternatives Considered
    Appknox
    No answers on this topic
    Black Duck Software
    Black Duck is an obvious choice, with its versatility, integration, best enterprise support and on top of the list the knowledge base Black Duck has. Vega or Grabber also scans the application and tells about vulnerabilities. But it can never be compared with the feature set of Black Duck. Black Duck can also generate reports.
    Incentivized
    Read full review
    Return on Investment
    Appknox
    No answers on this topic
    Black Duck Software
    • It is hard to measure ROI since Black Duck Hub saves us from costly legal battles that have thankfully never had to happen.
    Incentivized
    Read full review
    ScreenShots

    Appknox Screenshots

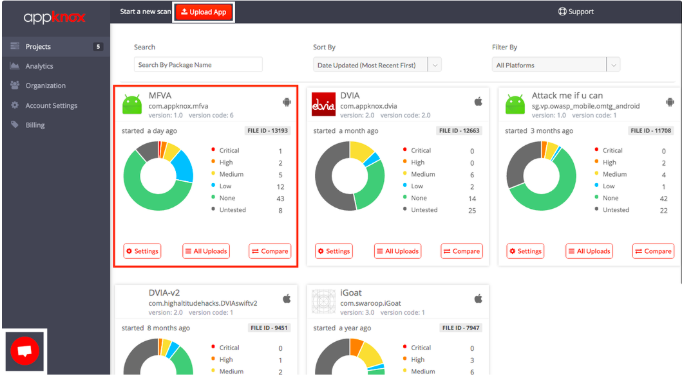
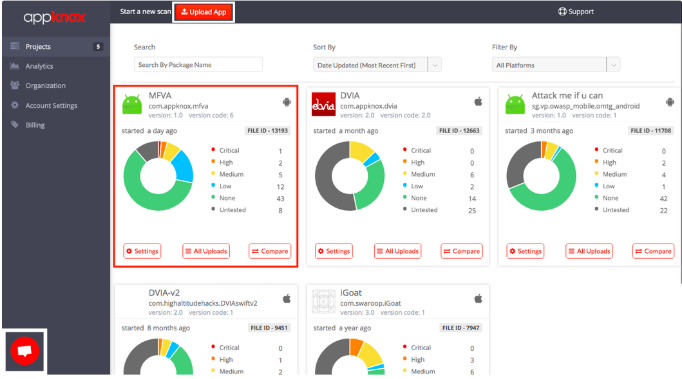
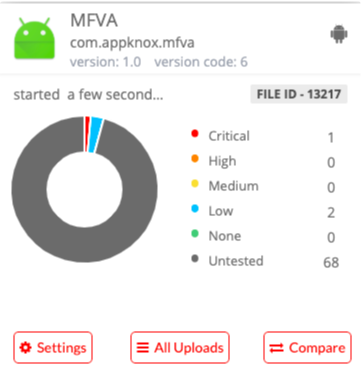
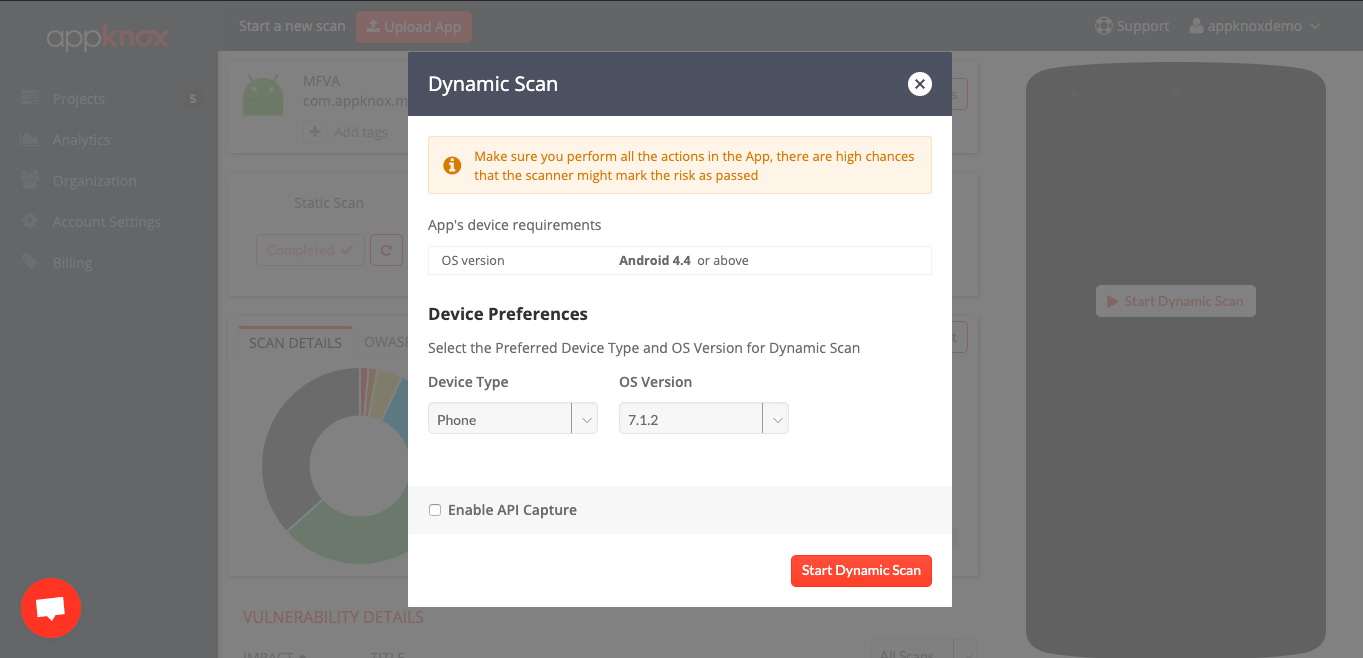
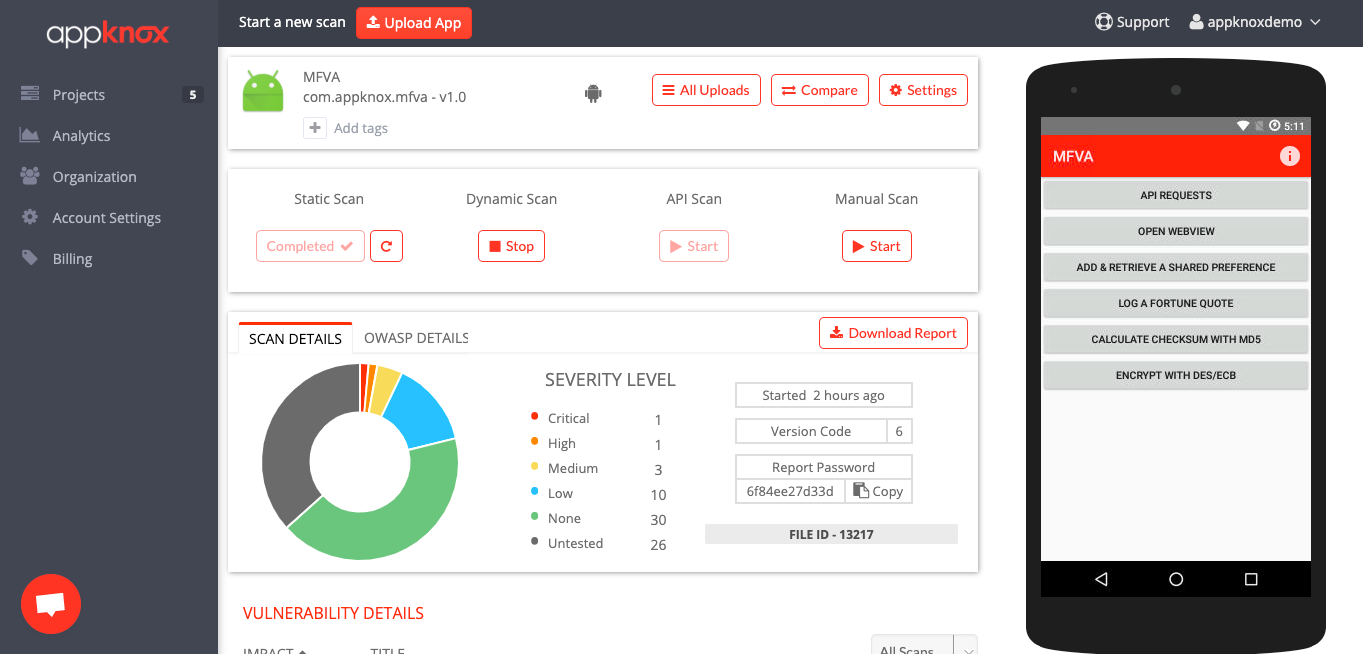
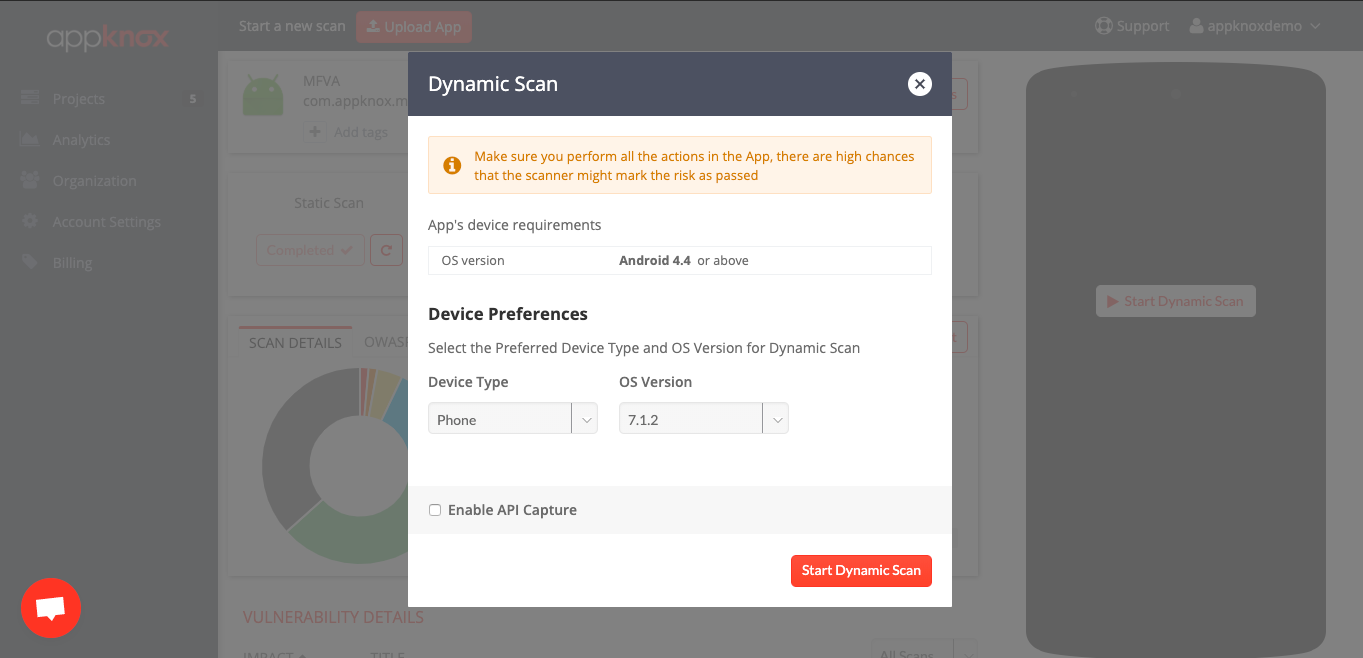
    Screenshot of Appknox automated scanner is easy to use and has vast API compatibilities which make it simple to integrate into the mobile Application Development cycle, providing complete automation of SAST, DAST, and Application Program Interface(API) Testing.Screenshot of FileID: This is a unique serial number get auto-assigned by the dashboard and has multiple use cases such as compare feature & look for assistance. Namespace: The namespace or bundle ID are fetched from the binary itself, as based on the namespace the scanner curates different uploads and creates new projects. Platform: This is the second category based on which the scanner differentiates between two files having the same namespaces. The dashboard supports IOS, Android & Windows Application. Version & Version Code: These details are Auto-fetched from the binary and can be used for later for comparison & tracking uploads over time.Screenshot of Static Application Security Testing (SAST) can be considered as testing an application from the inside out by examining its source code or application binaries for issues based on the configuration which point towards a security vulnerability.Screenshot of A Dynamic Application Security Testing (DAST) analysis is generally specifically designed to detect conditions indicative of a security vulnerability in an application while in its running state.Screenshot of A Dynamic Application Security Testing (DAST) analysis is generally specifically designed to detect conditions indicative of a security vulnerability in an application while in its running state.Screenshot of If this function is enabled, the scanner will detect & capture all the API calls made & API End Points used during the dynamic scan session.

    Black Duck Software Composition Analysis (SCA) Screenshots

    Screenshot of Black Duck helps you find and fix your highest-priority vulnerabilitiesScreenshot of Use Black Duck to comply with open source license obligations and to verify compliance with all open source license  termsScreenshot of Black Duck automatically creates tickets in your activity tracking applications like Jira for both policy violations and vulnerabilitiesScreenshot of Black Duck's vulnerability ImpactAnalysis indicates whether a vulnerability is actually being called by your applicationScreenshot of The Black Duck security advisory gives the information you need to address security risks and make the fixScreenshot of Black Duck generates a Bill of Materials which gives you a complete and detailed inventory of all open source identified in your codebase