AutoRABIT is a DevSecOps provider that allows working off the Salesforce platform, protecting users from outages and vulnerabilities experienced by those working directly within Salesforce.
N/A
Checkmarx
Score7.5 out of 10
N/A
Checkmarx, an Israeli headquartered company with US offices, provides a suite of application security software delivered via the Checkmarx Software Security Platform. Individual modules and capabilities include Checkmarx Static Application Security Testing, Checkmarx Software Composition Analysis, Checkmarx Interactive Application Security Testing (CxIAST)
N/A
SonarQube
Score8.7 out of 10
N/A
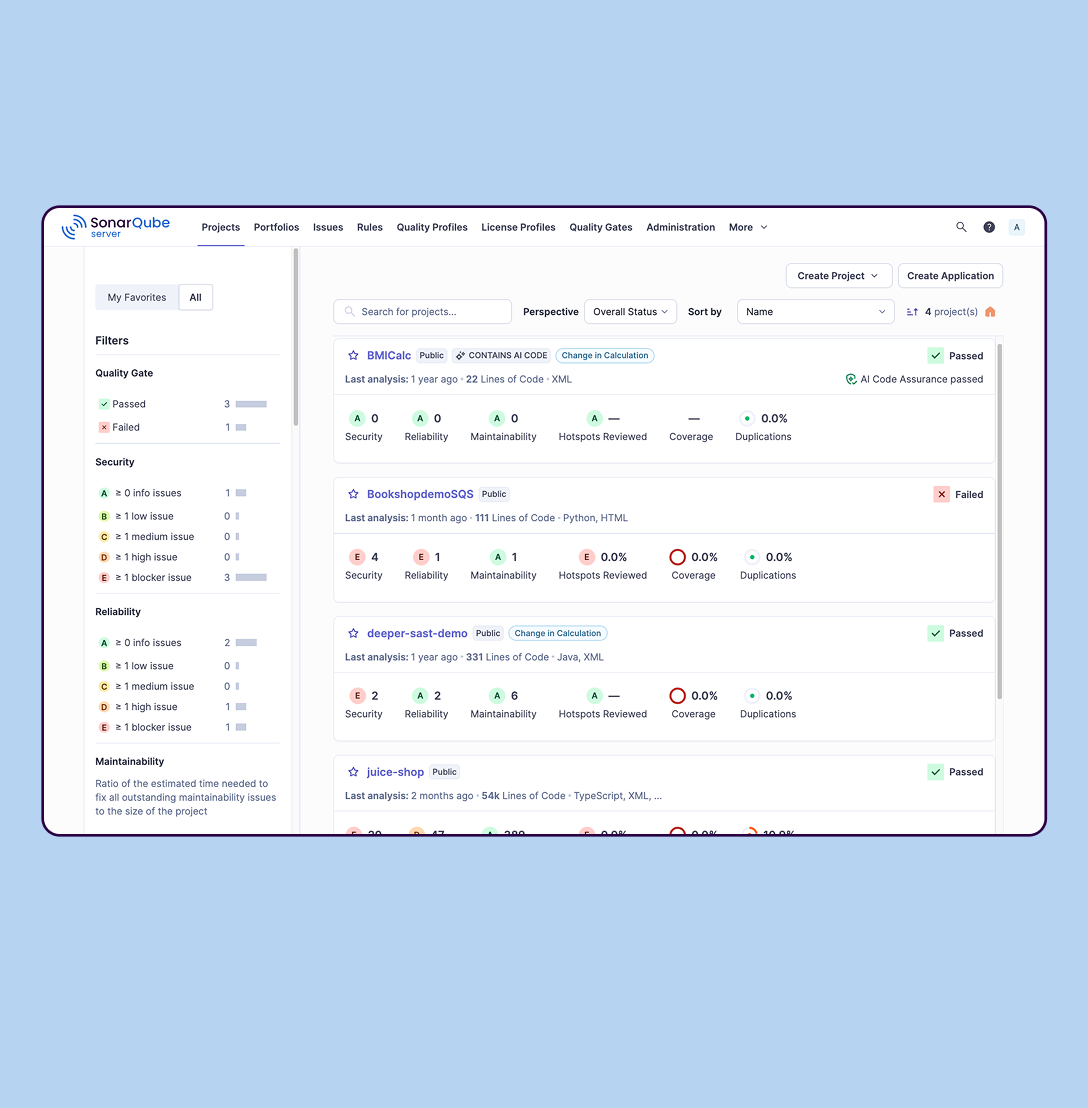
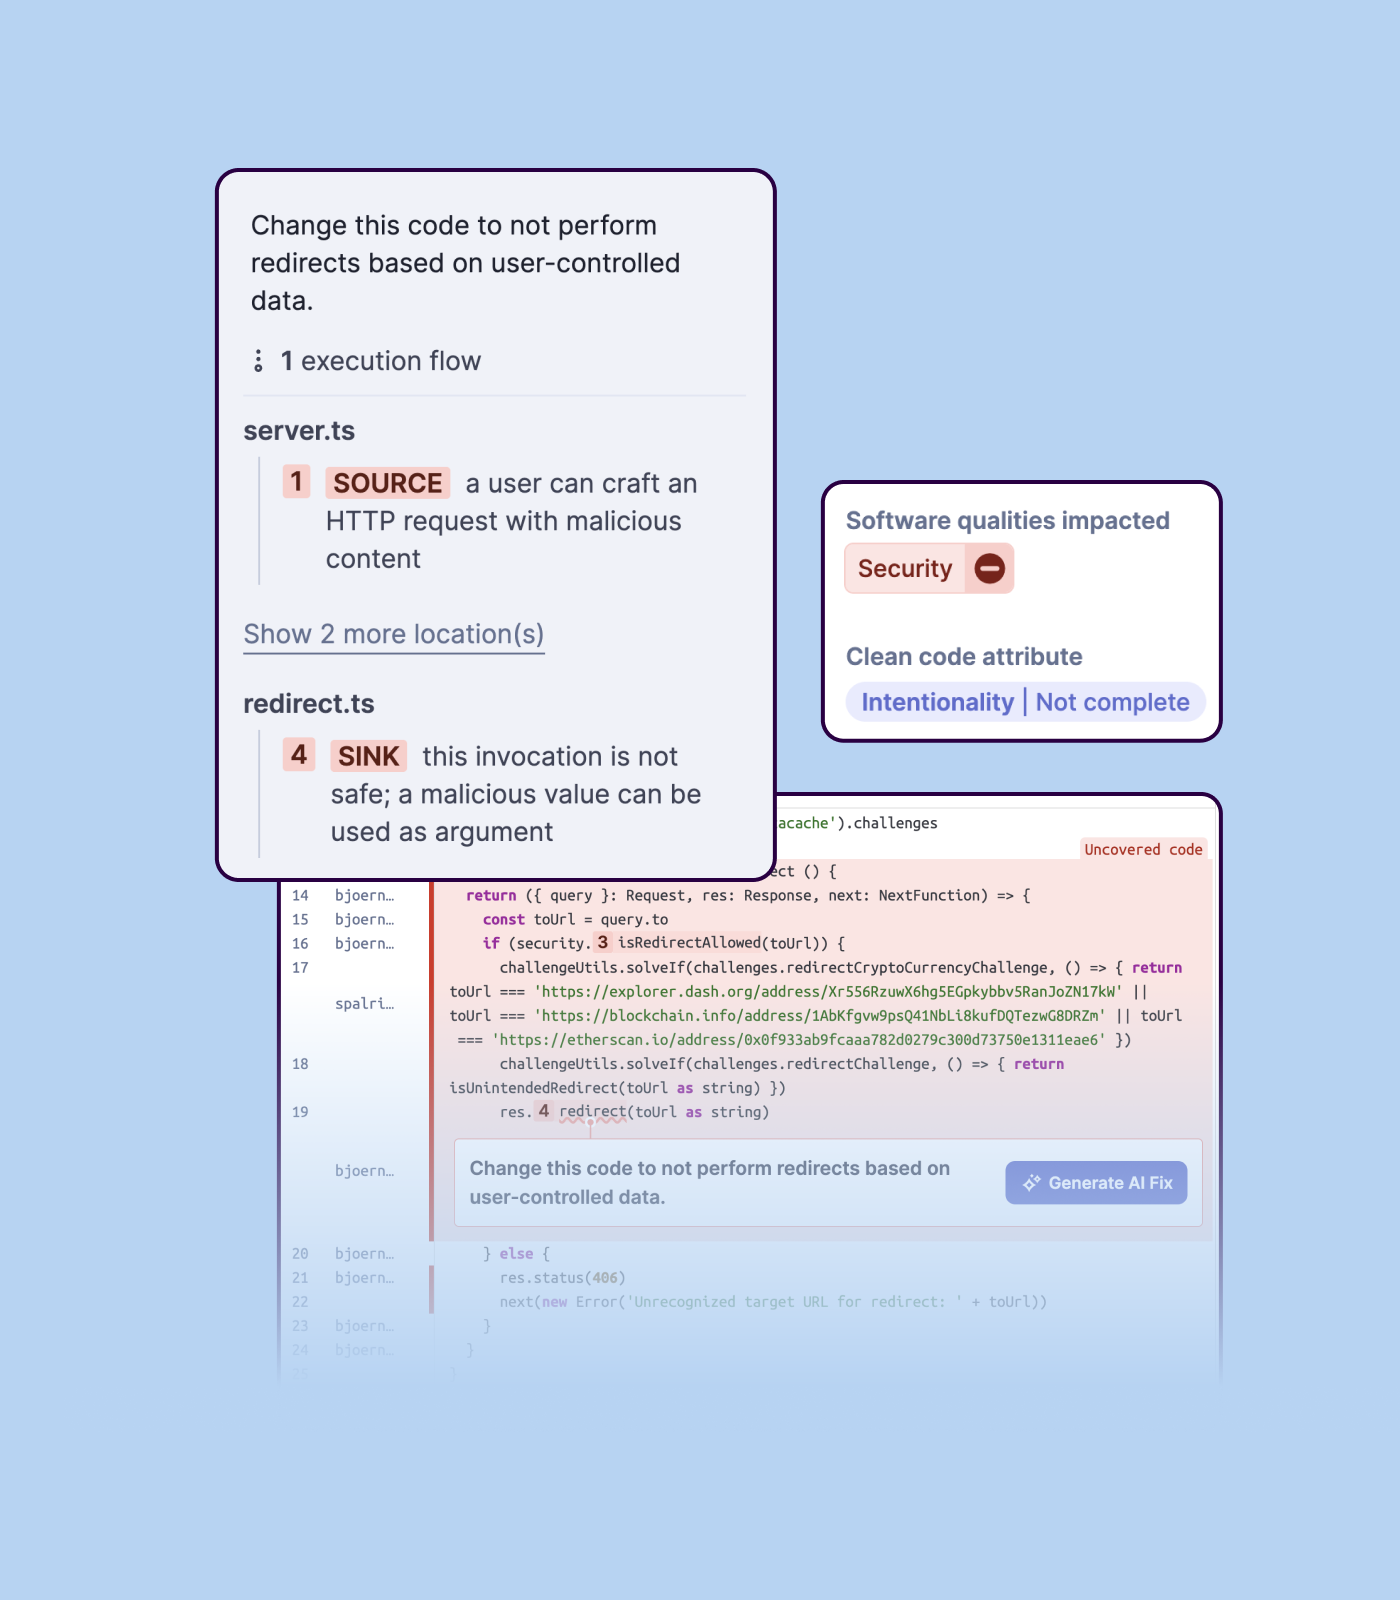
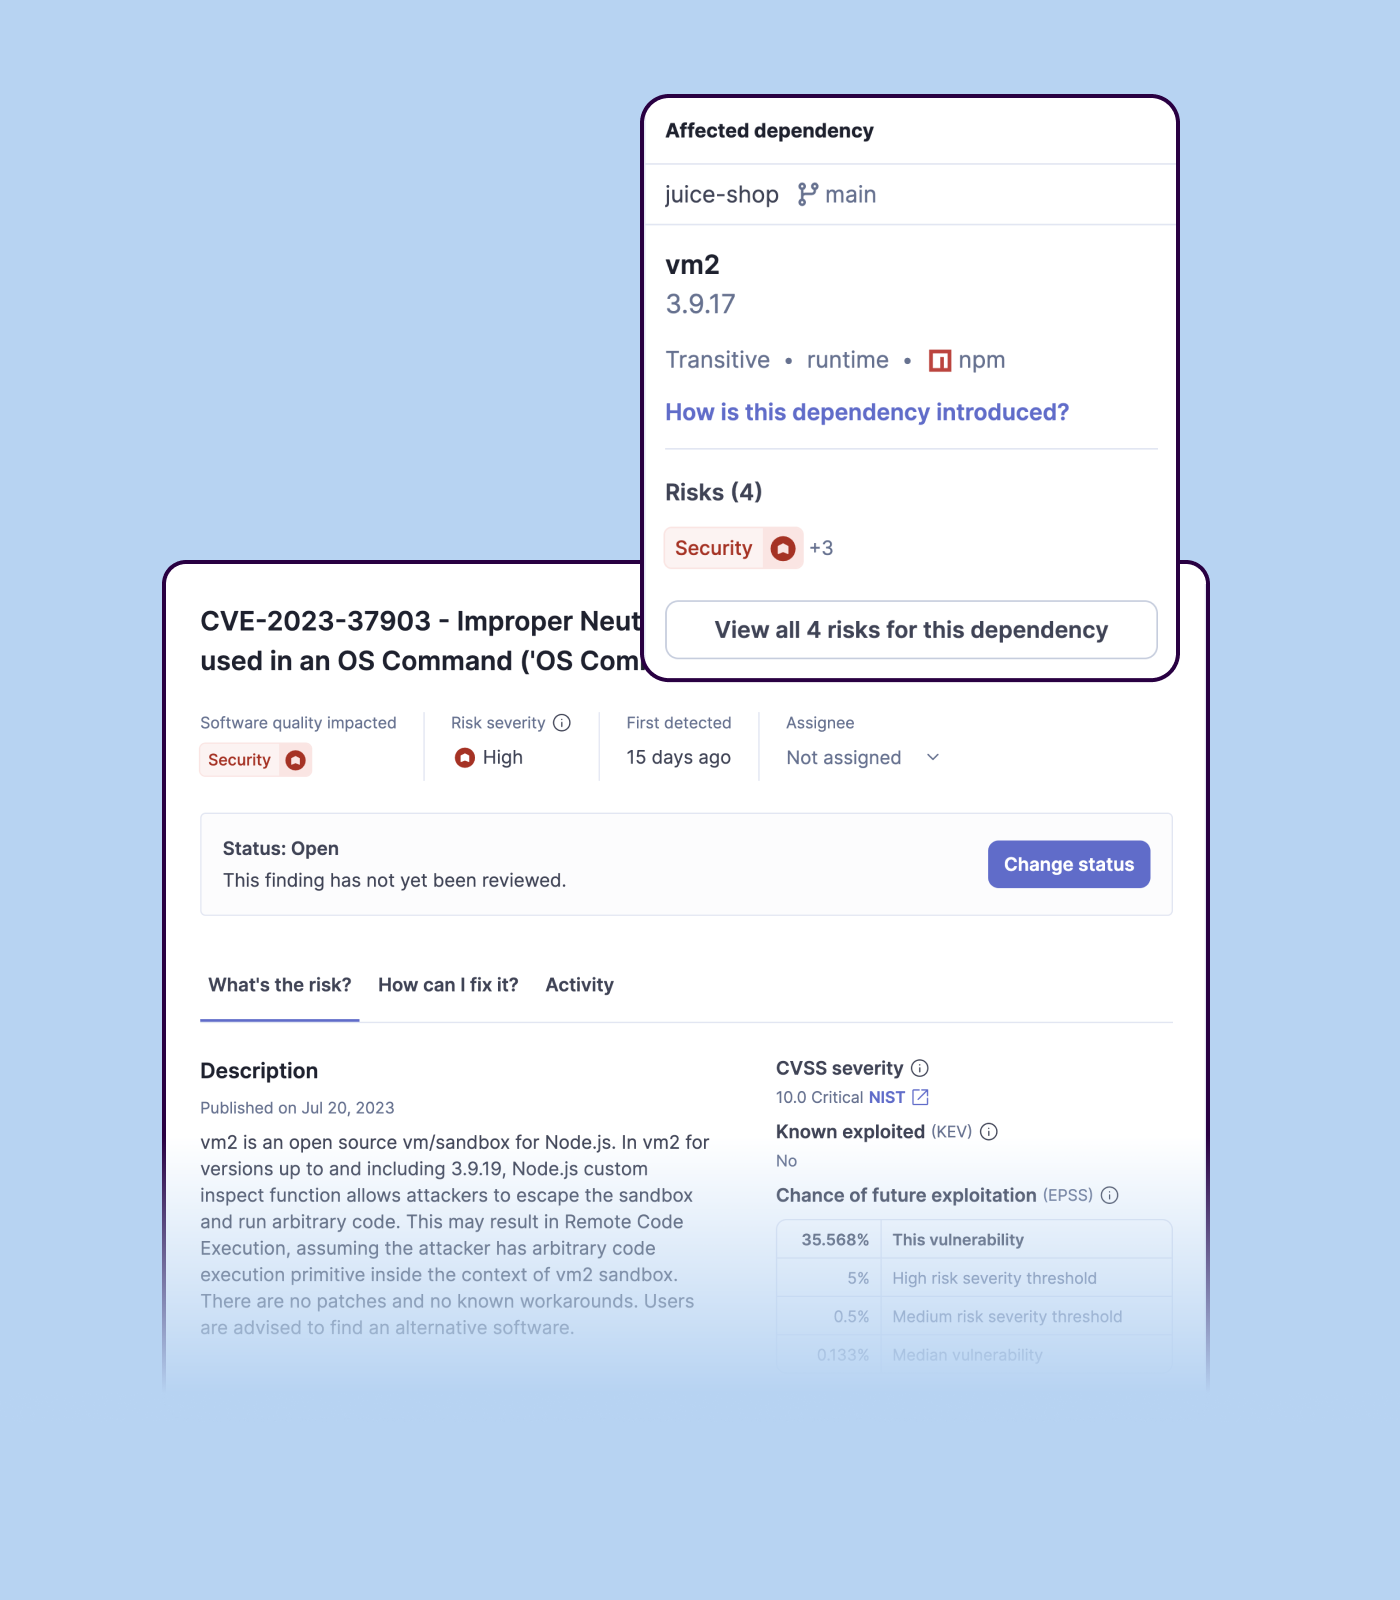
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
$34
per month Recommended for teams <50 developers
Pricing
AutoRABIT
Checkmarx
SonarQube
Editions & Modules
No answers on this topic
No answers on this topic
SonarQube Community Build
$0
(open source)
Self-managed: Developer
Starting at $720 annually
per year per installation
Self-managed: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Teams
Starting at $34 per month
per month per installation
Self-managed: Data Center
Contact sales for pricing
per year per installation
Offerings
Pricing Offerings
AutoRABIT
Checkmarx
SonarQube
Free Trial
No
No
Yes
Free/Freemium Version
No
No
Yes
Premium Consulting/Integration Services
Yes
No
No
Entry-level Setup Fee
No setup fee
No setup fee
No setup fee
Additional Details
Contact vendor for pricing information
—
—
More Pricing Information
Community Pulse
AutoRABIT
Checkmarx
SonarQube
Considered Multiple Products
AutoRABIT
No answer on this topic
Checkmarx
No answer on this topic
SonarSource Sarl
Verified User
Chose SonarQube
Getting SonarQube instead of the other tools we tested was an easy choice. Snyk was way too much limited to only Docker images and dependency analysis at that time. And Checkmarx was very hard to adapt to our needs : configuring custom quality gates was way too much of a …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose SonarQube
Some are still under consideration. Pricing is a big component. Some FOSS products have been considered is at par (at least for our needs) or catching up. Although the amazing support in the community weighs hard on the value. So, if it went away...so would some arguments …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AutoRABIT is well suited- 1. Continuous Integration and Continuous Deployment 2.AutoRABIT provides a centralized platform to orchestrate and automate release activities, ensuring consistency and compliance across environments.AutoRABIT is a comprehensive DevOps platform with associated costs. Less appropriate. Organizations with limited budget or resources may find it more cost-effective to use alternative tools or manual processes for Salesforce development and release management.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you are going with SAST process or want to improve overall security posture then go for it like integrating it with post deployment steps. If you are more concerned about proactive controls better choose other options such as pee-commit hooks and CI security. Also choose other tools for DAST and API scans.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
user interface can be overwhelming and complex for new users
AutoRABIT offers integration with various Salesforce tools and platforms, some users may find the integration options limited or lacking flexibility.
Depending on the size and complexity of Salesforce orgs, some users may experience performance issues with certain AutoRABIT functionalities, such as deployments or data migrations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Their API based customizations which I leveraged to create an ASPM package, which is developer friendly and can extend above the dashboard features, other ones are UI which is great and feels clutter free. Menu and navigation is also good so as support. Only drawback is sometimes scan takes longer which I feel so can be reduced
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Checkmarx is easier to integrate with development tools and gives quick feedback during coding, which is helpful for developers. Veracode is more focused on scanning and reporting for compliance, but it’s more complex to set up. We chose Checkmarx because it fits better into our development process, offering faster scans and more useful suggestions for fixing problems
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AutoRABIT can significantly streamline Salesforce development and release management processes, reducing manual effort and time spent on repetitive tasks.
By automating testing, code quality checks, and deployment processes, AutoRABIT helps ensure consistency and reliability in Salesforce deployments.
While there is an initial investment associated with implementing and licensing AutoRABIT, the long-term cost savings from reduced manual effort, decreased deployment errors, and improved productivity can result in a positive ROI over time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)