Cisco Threat Response automates integrations across select Cisco Security products and accelerates key security operations functions: detection, investigation, and remediation. Threat Response integrates threat intelligence from Cisco Talos and third-party sources, which adds context from integrated Cisco Security products automatically so you know instantly which of your systems was targeted and how.
N/A
Microsoft Defender for Cloud
Score8.7 out of 10
N/A
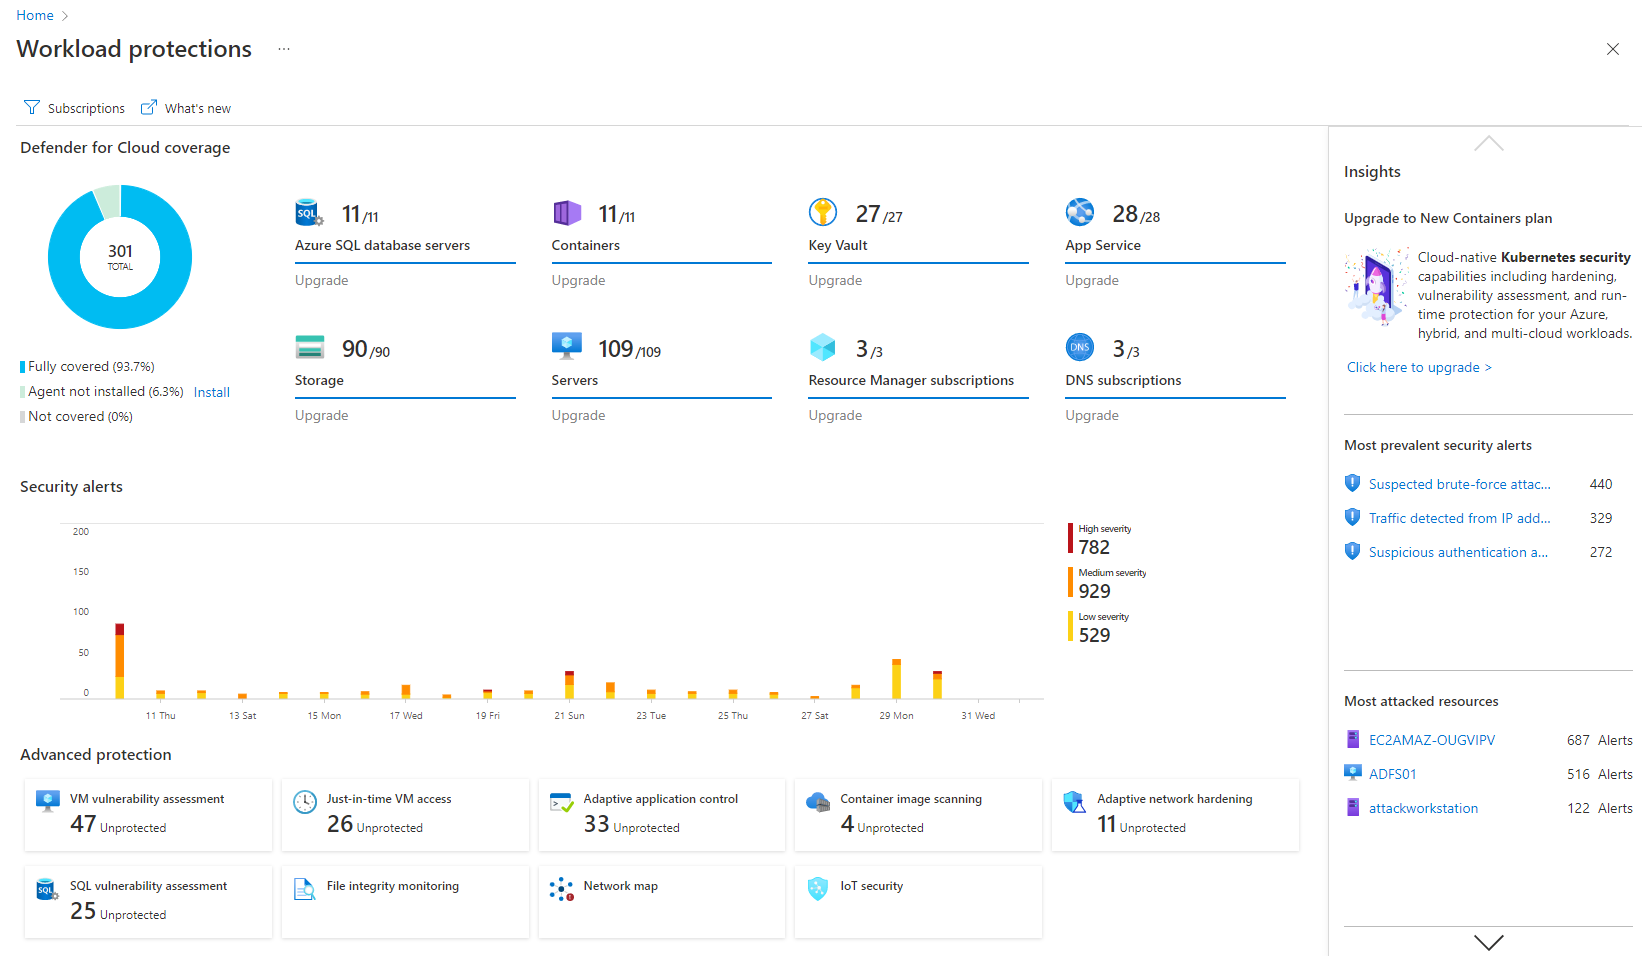
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
This is perfect for organisations with small or limited security teams who want to get more from their Cisco and third-party investments. With Secure Endpoint makes detecting and responding to threats much easier. Any organisation looking to overhaul its security infrastructure or even wrap around its cloud-first strategy with solutions such as Intune should seriously look at Cisco’s suite of products. I’ve implemented Secure Endpoint, Umbrella, and Duo for customers primarily using Intune for device management, and the cool new insight features in Cisco SecureX really help with visibility over their estate.
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
So the product enables end users to get visibility into their security environment, not only across the Cisco products but across the third-party products as well. The product also automates detection and response. So the product really offers end-user efficiency in the security operations center.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Of course, many companies prefer to obtain security from the cloud; however, not all of them prefer it, which is why having a local implementation would allow these companies to also use said software as their ally for their security.
Working with this software can be simple, that is, any threat can be visualized with greater precision, but when it comes to managing its orchestration, it is a bit complex.
Its integration with other software can be simple but with others it is not, that is why it would be ideal if all of them could be carried out in the same way.
Integrating with a larger number of third party software would be of great help, to further enhance the analysis and detection of threats.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A lot of the look and feel of both products is quite similar. There's several best practices on visualization that are followed in both and integration of common telemetry is comfortable and quick. But while Microsoft ATP offers deep insights into mostly the Microsoft environment and a limited view into other common sources, SecureX shines in all the non-client areas Microsoft's product seems lackluster in.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info