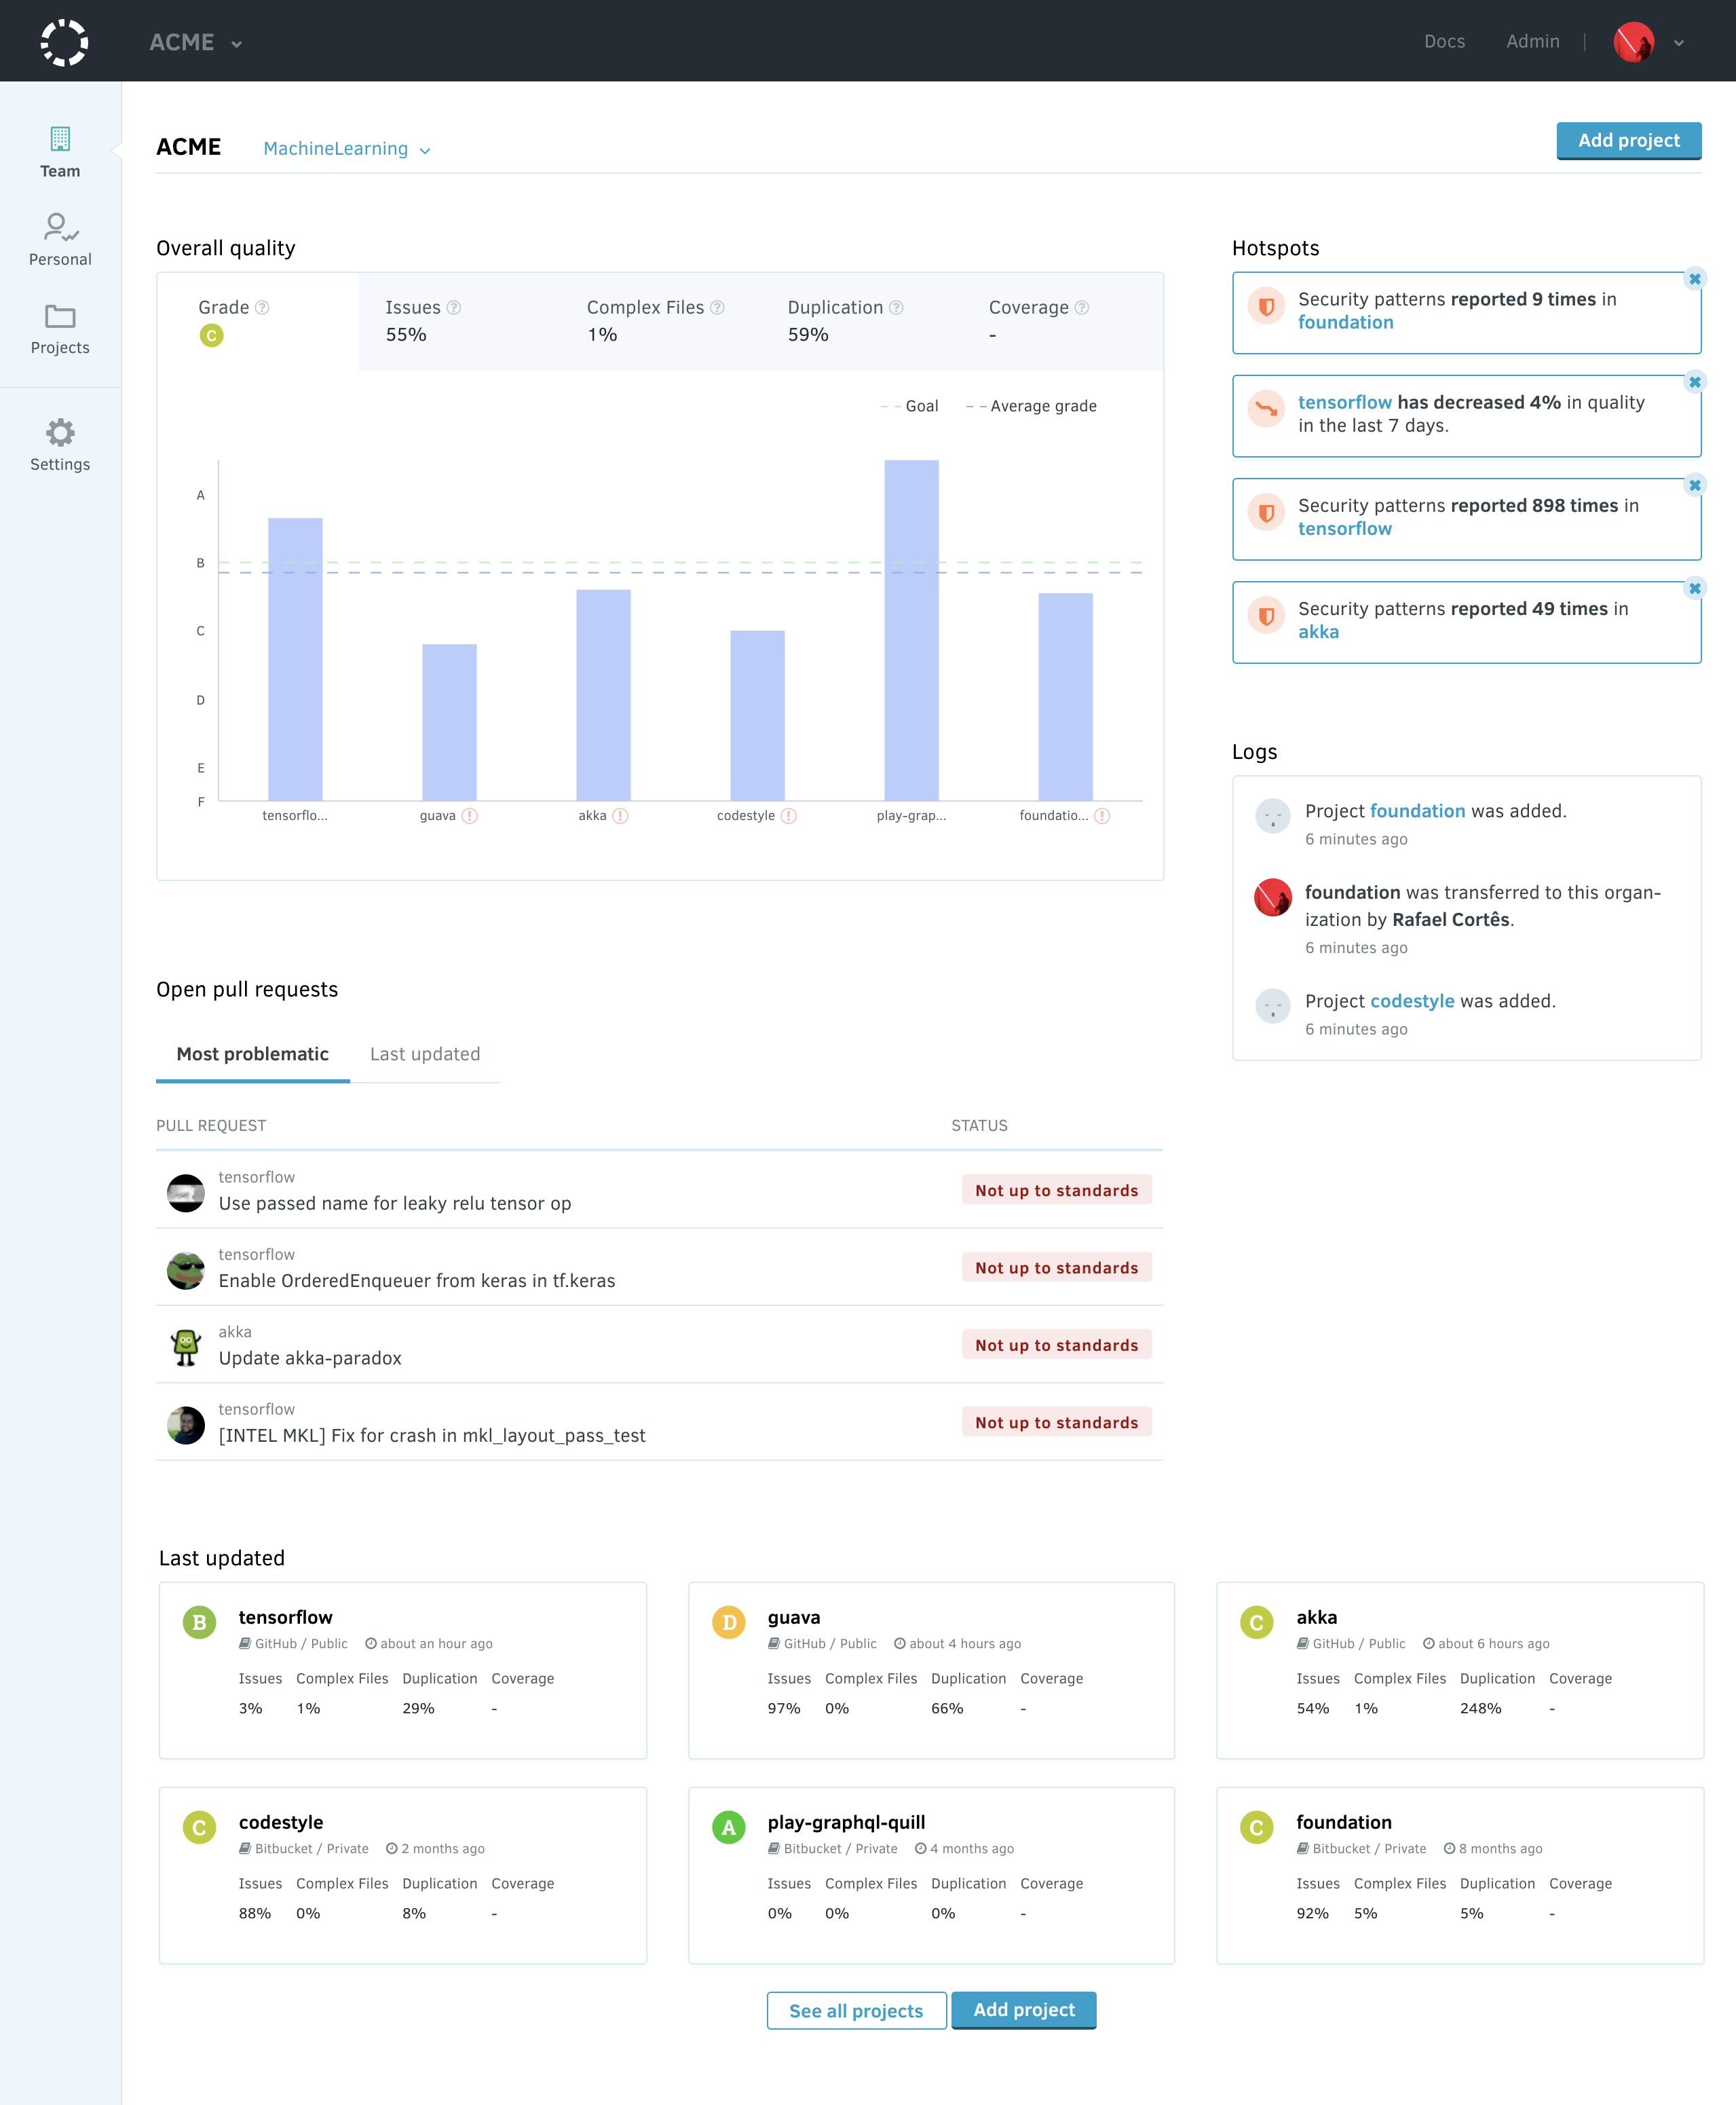
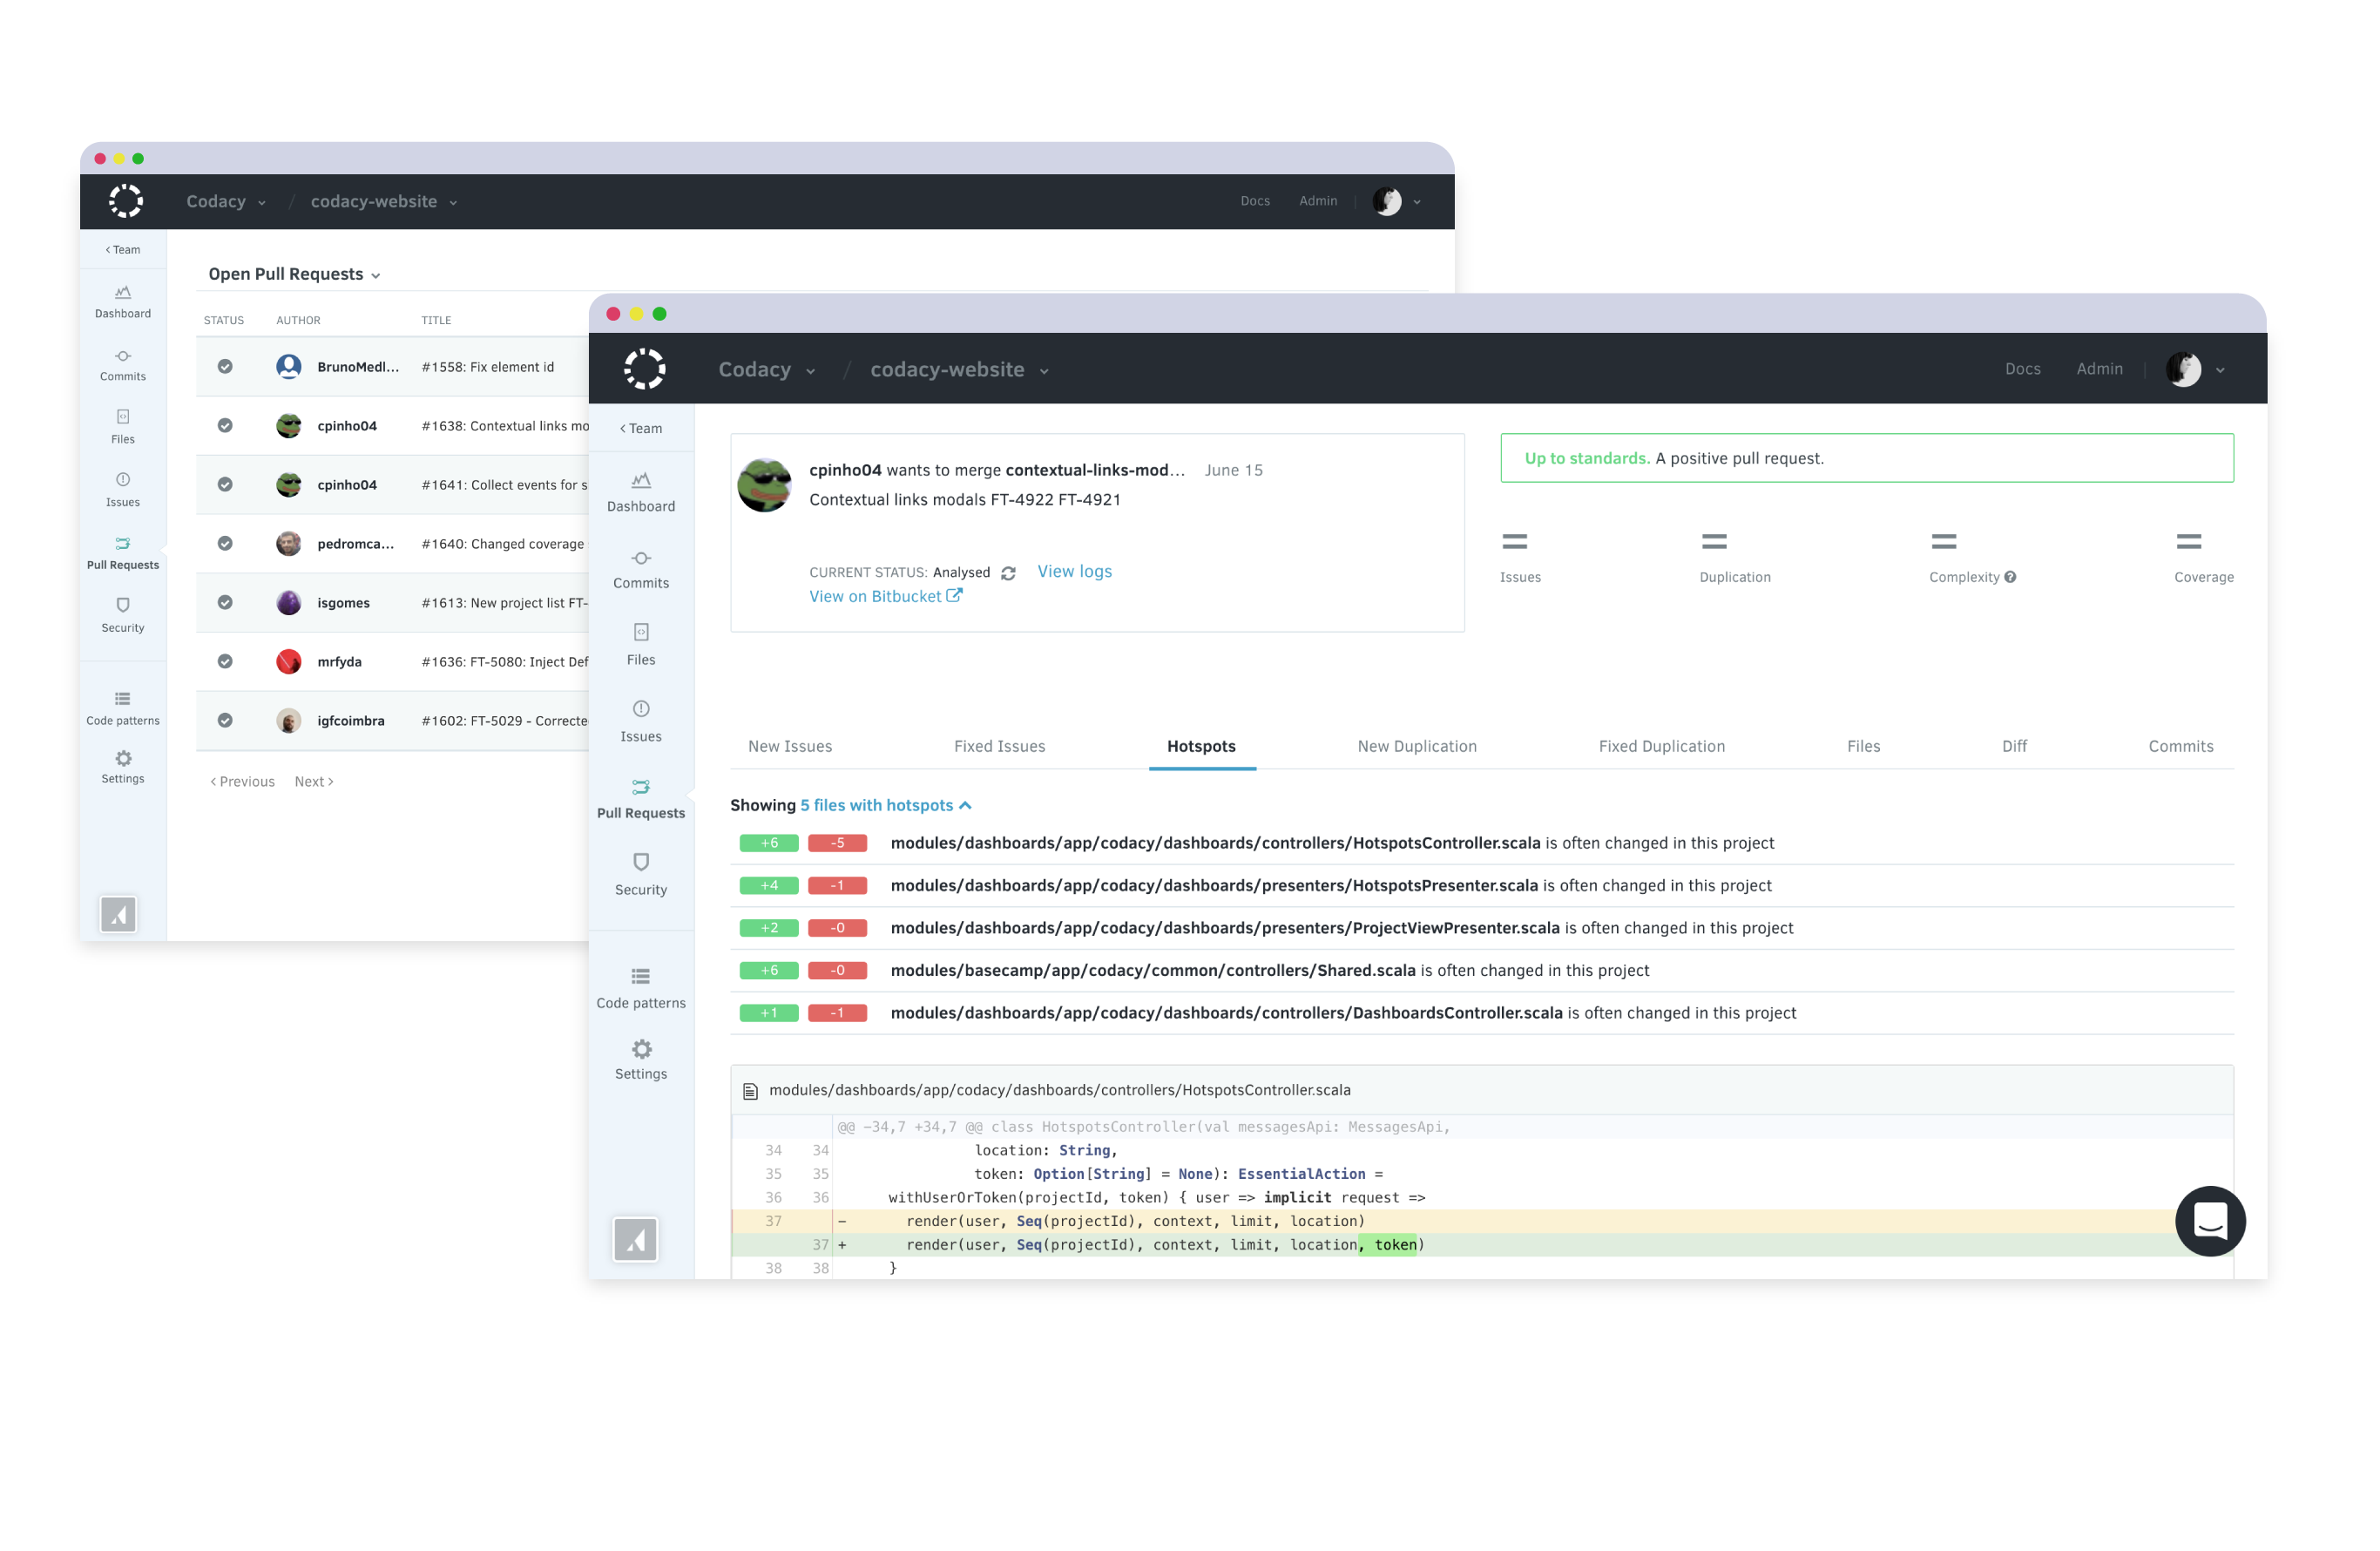
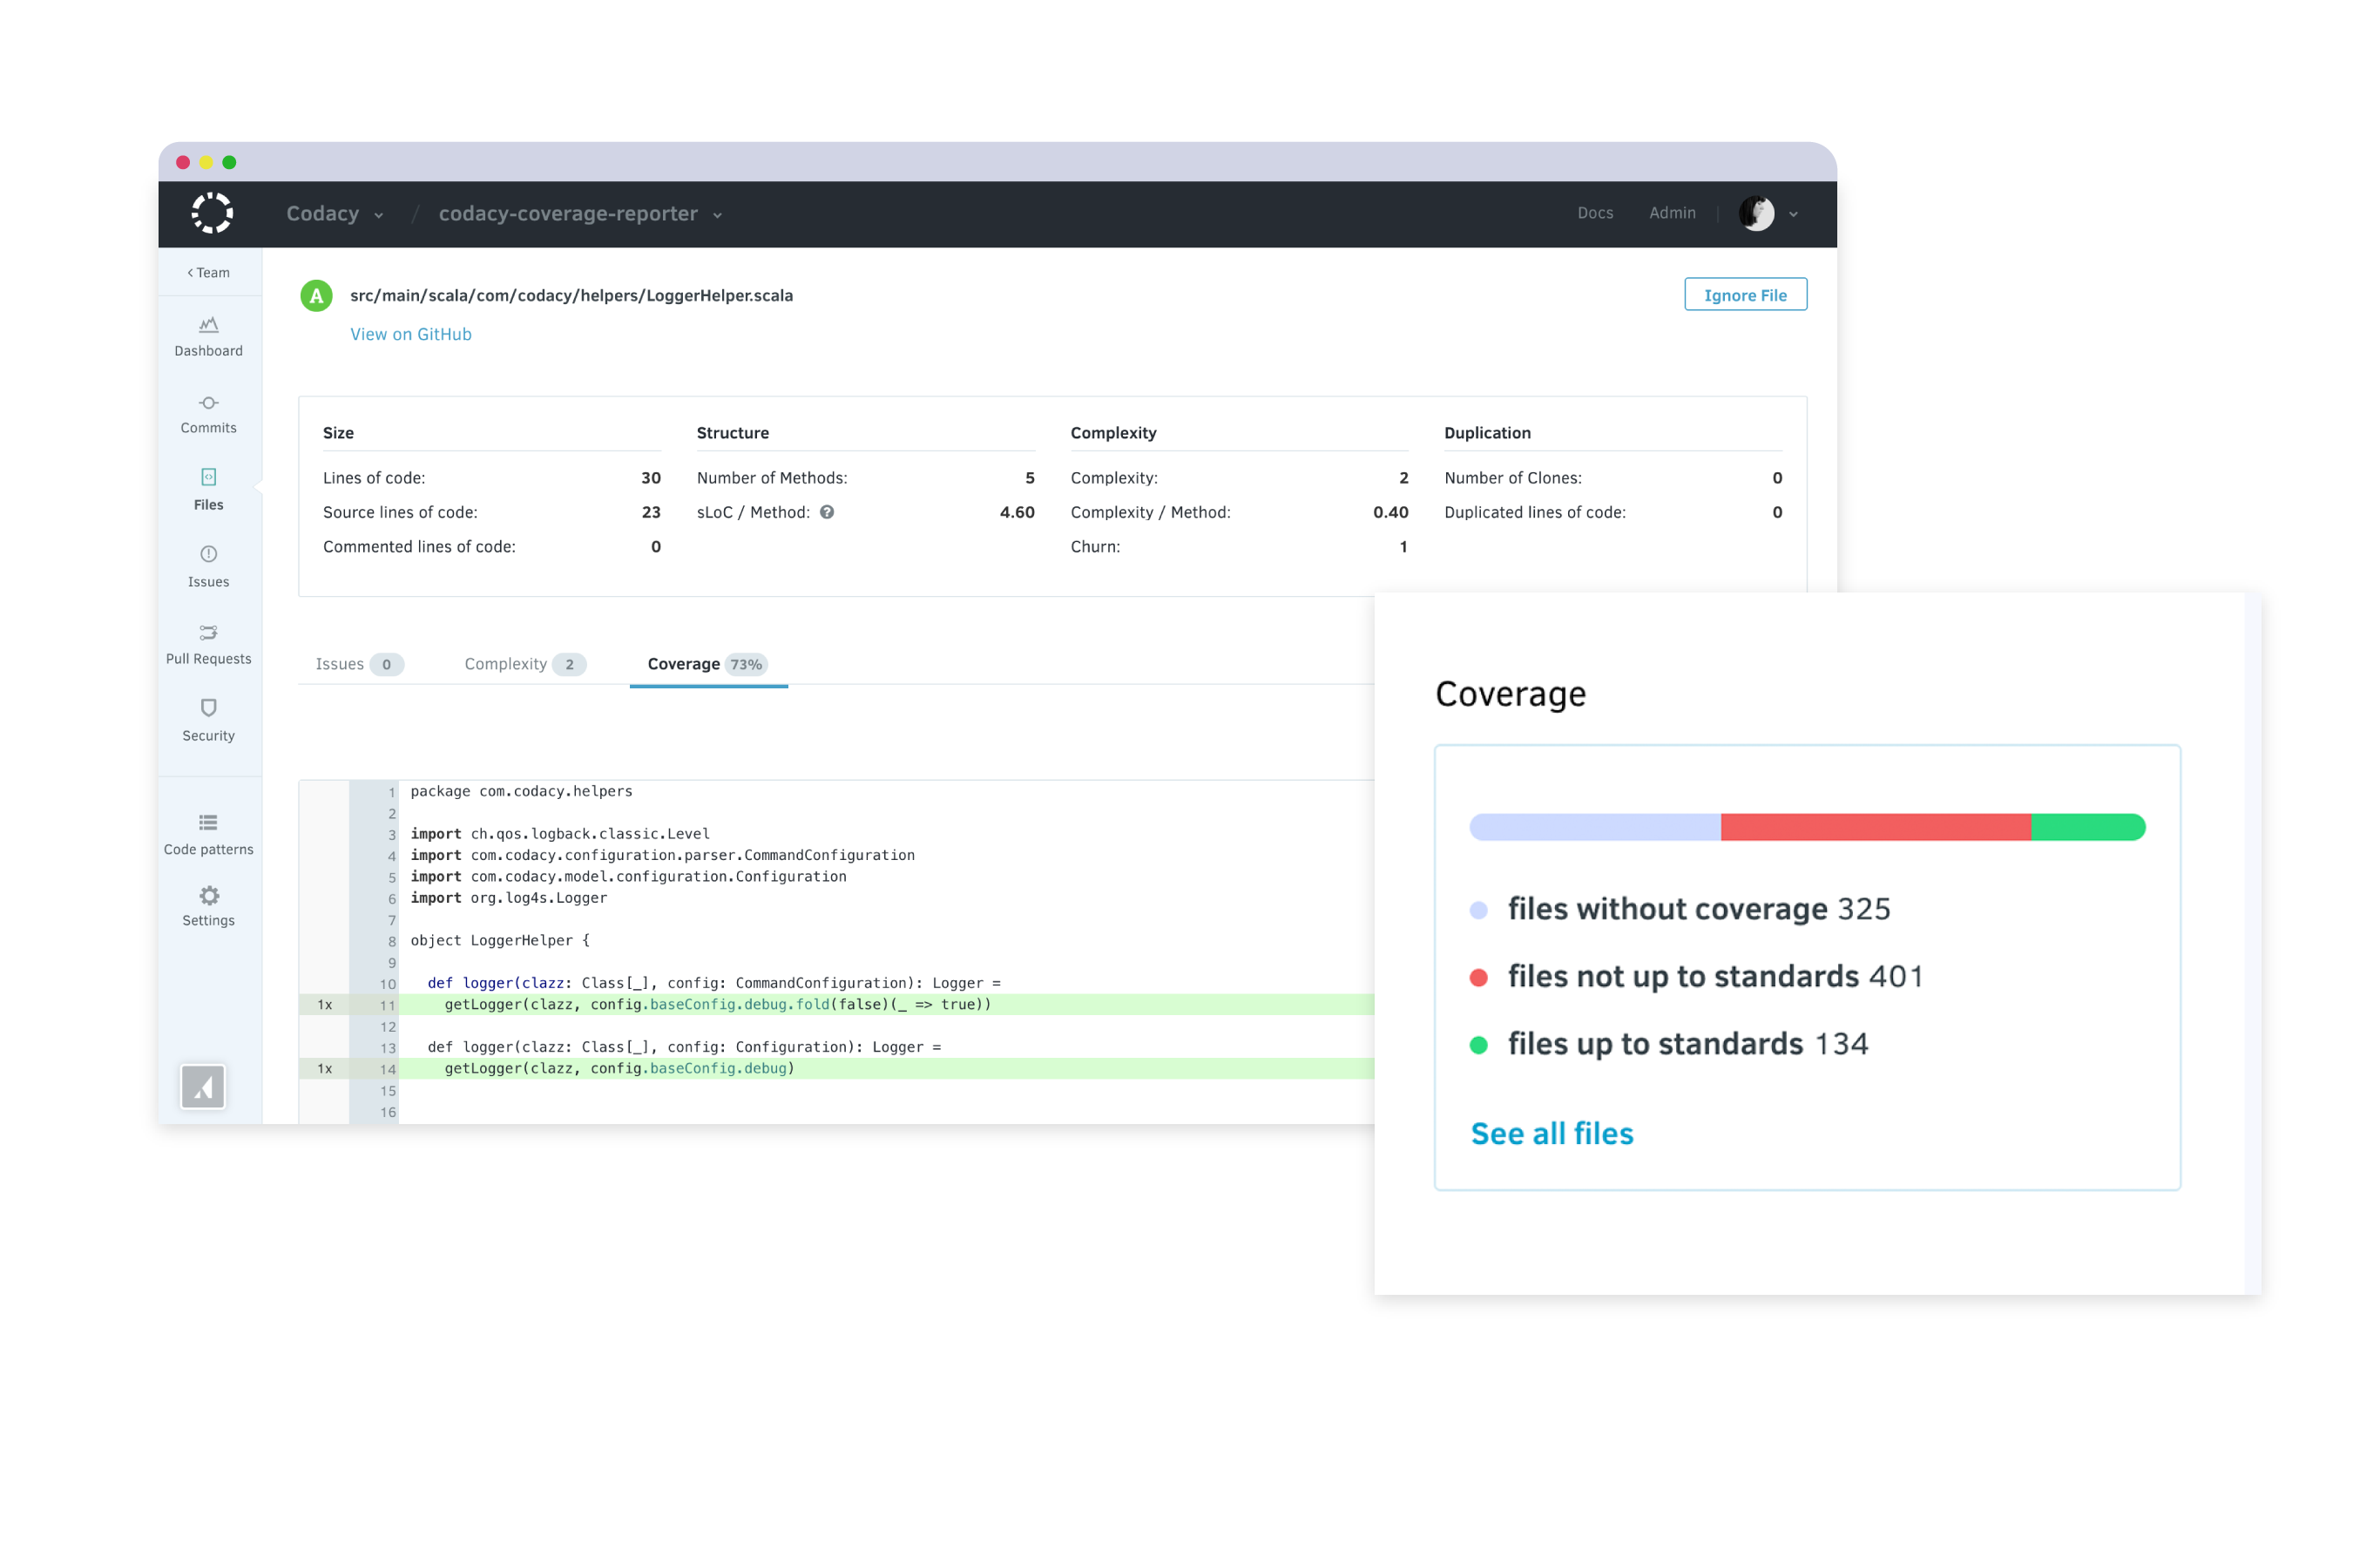
Codacy automates code reviews and monitors code quality on every commit and pull request reporting back the impact of every commit or pull request, issues concerning code style, best practices, security, and many others. It monitors changes in code coverage, code duplication and code complexity. Saving developers time in code reviews thus efficiently tackling technical debt. JavaScript, Java, Ruby, Scala, PHP, Python, CoffeeScript and CSS are currently supported. Codacy is static analysis…
$0
PortSwigger Burp Suite
Score9.2 out of 10
N/A
The Burp Suite, from UK-based alcohol-themed software company PortSwigger Web Security, is an application security and testing solution.
N/A
SonarQube
Score8.7 out of 10
N/A
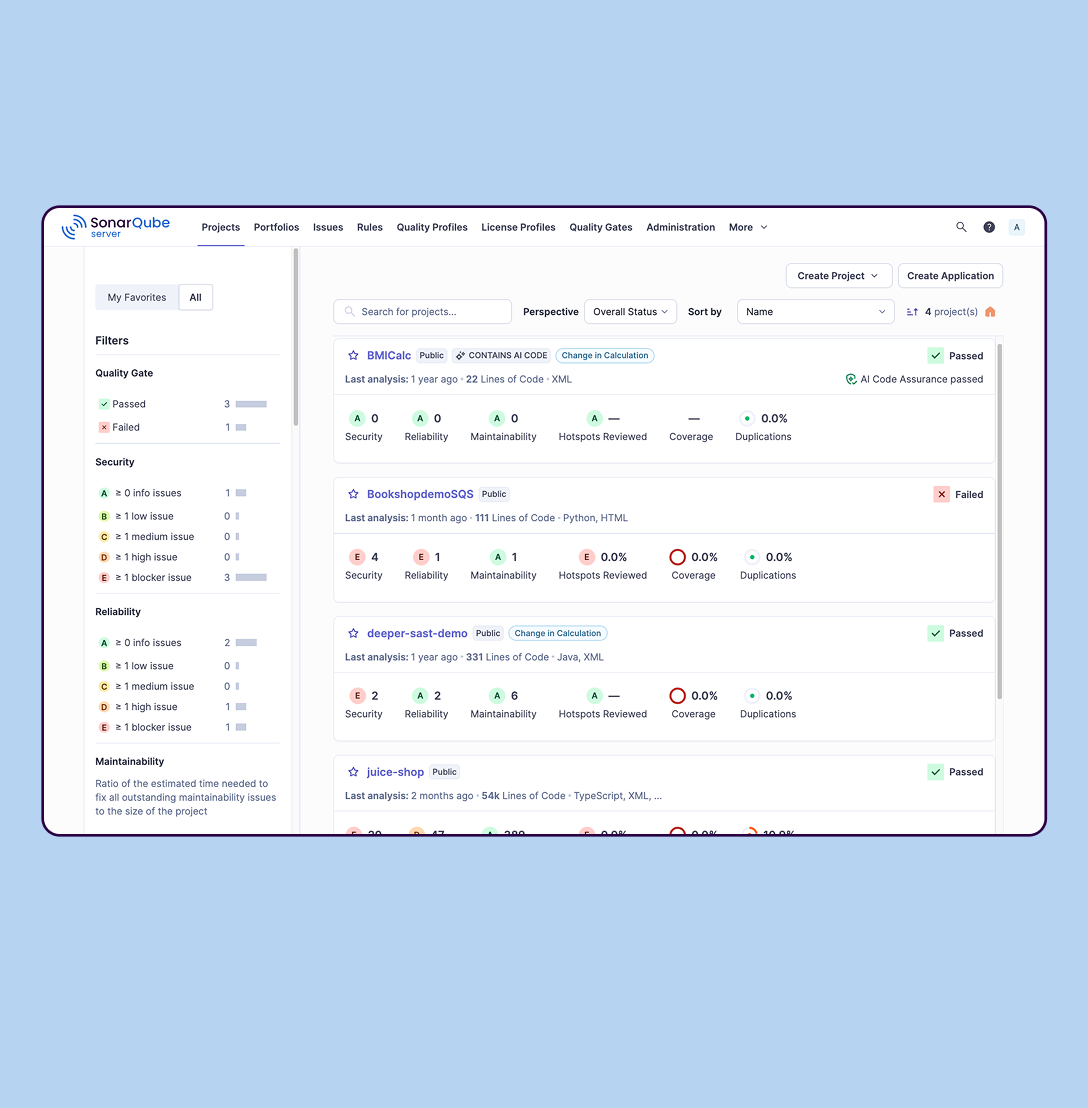
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
$34
per month Recommended for teams <50 developers
Pricing
Codacy
PortSwigger Burp Suite
SonarQube
Editions & Modules
Open Source
$0.00
Startup
$0.00
Pro
$15.00
user/mo
Enterprise
$40.00
user/mo
No answers on this topic
SonarQube Community Build
$0
(open source)
Self-managed: Developer
Starting at $720 annually
per year per installation
Self-managed: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Teams
Starting at $34 per month
per month per installation
Self-managed: Data Center
Contact sales for pricing
per year per installation
Offerings
Pricing Offerings
Codacy
PortSwigger Burp Suite
SonarQube
Free Trial
Yes
No
Yes
Free/Freemium Version
Yes
No
Yes
Premium Consulting/Integration Services
Yes
No
No
Entry-level Setup Fee
Optional
No setup fee
No setup fee
Additional Details
—
—
—
More Pricing Information
Community Pulse
Codacy
PortSwigger Burp Suite
SonarQube
Considered Multiple Products
Codacy
Verified User
Chose Codacy
Even though it is paid while SonarQube is free, we chose Codacy because it is simpler to configure and maintain the implemented rules. In addition, it offers support for the main programming languages on the market, ensuring that we can continue to use it if we want to use …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Freelancer in RPA in Information Technology at Self employed (Information Technology and Services, 11-50 employees)
Chose Codacy
Codacy provides a good support mechanism and has very intuitive UI. Even a newbie can understand the details of a code base. The best part is you don't have to manually update everything. Once you have connected the git repository, it will automatically rate the code and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose SonarQube
Some are still under consideration. Pricing is a big component. Some FOSS products have been considered is at par (at least for our needs) or catching up. Although the amazing support in the community weighs hard on the value. So, if it went away...so would some arguments …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I recommend it for companies that use several programming languages, as it supports several languages such as Java, Javascript, Python, among others. However, for companies that use only one programming language, there are specific tools for each language that can be more complete in this scenario. I do not recommend it for companies that only use open source software, in which case there are other tools available.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Burp Suite is a good general tool to test websites as long as your website is not too large or you have the time for it to complete. We have some websites that only about five to ten minutes for Burp Suite to complete an attack and a spider only takes about two minutes. Other websites have taken a few hours to complete. I have seen a tester actually run Burp Suite against one of our websites and it took all day to complete.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The interface is a big problem: No matter how many features a software provides you, if the features are not well presented, you will miss most of them when they are actually required. The presentation of the software should be improvised and made more presentable.
Tutorial videos for beginners: This software lacks a lot in tutorials. A beginner almost wastes most of the time in finding and understanding the features and the implementation of the same. The software vendor should work on providing more in-depth videos so that people can learn and understand the concepts.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The workflow between features like Proxy, Scanner, Intruder, and Repeater feels seamless, making it easy to intercept, manipulate, and analyze web traffic. Despite its advanced capabilities, the tool remains accessible and flexible, which significantly speeds up testing without overwhelming the user.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
BurpSuite does not have an amazing customer support. All the major help that you will find is from public forums and Google. Although you will find all the required information on Google, still at time professional support helps you solve the problem in much less time and make your operations go smoothly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Even though it is paid while SonarQube is free, we chose Codacy because it is simpler to configure and maintain the implemented rules. In addition, it offers support for the main programming languages on the market, ensuring that we can continue to use it if we want to use other languages in new products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Each tool is specific and are good for what they do. While Burp Suite can perform some level of the same functions, somehow security consultants prefer these tools as additional to the Burp Suite. Maybe due to open source and easy setup when compared to Burp Suite. But Burp Suite allows for one tool for many templates for each project.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)