F5 Distributed Cloud WAF leverages F5's Advanced WAF technology, delivering WAF-as-a-Service and combining signature- and behavior-based protection for web applications. It acts as an intermediate proxy to inspect application requests and responses to block and mitigate a broad spectrum of risks stemming from the OW ASP Top 10, persistent and coordinated threat campaigns, bots, and layer 7 DoS.
N/A
Microsoft Defender for Cloud
Score8.7 out of 10
N/A
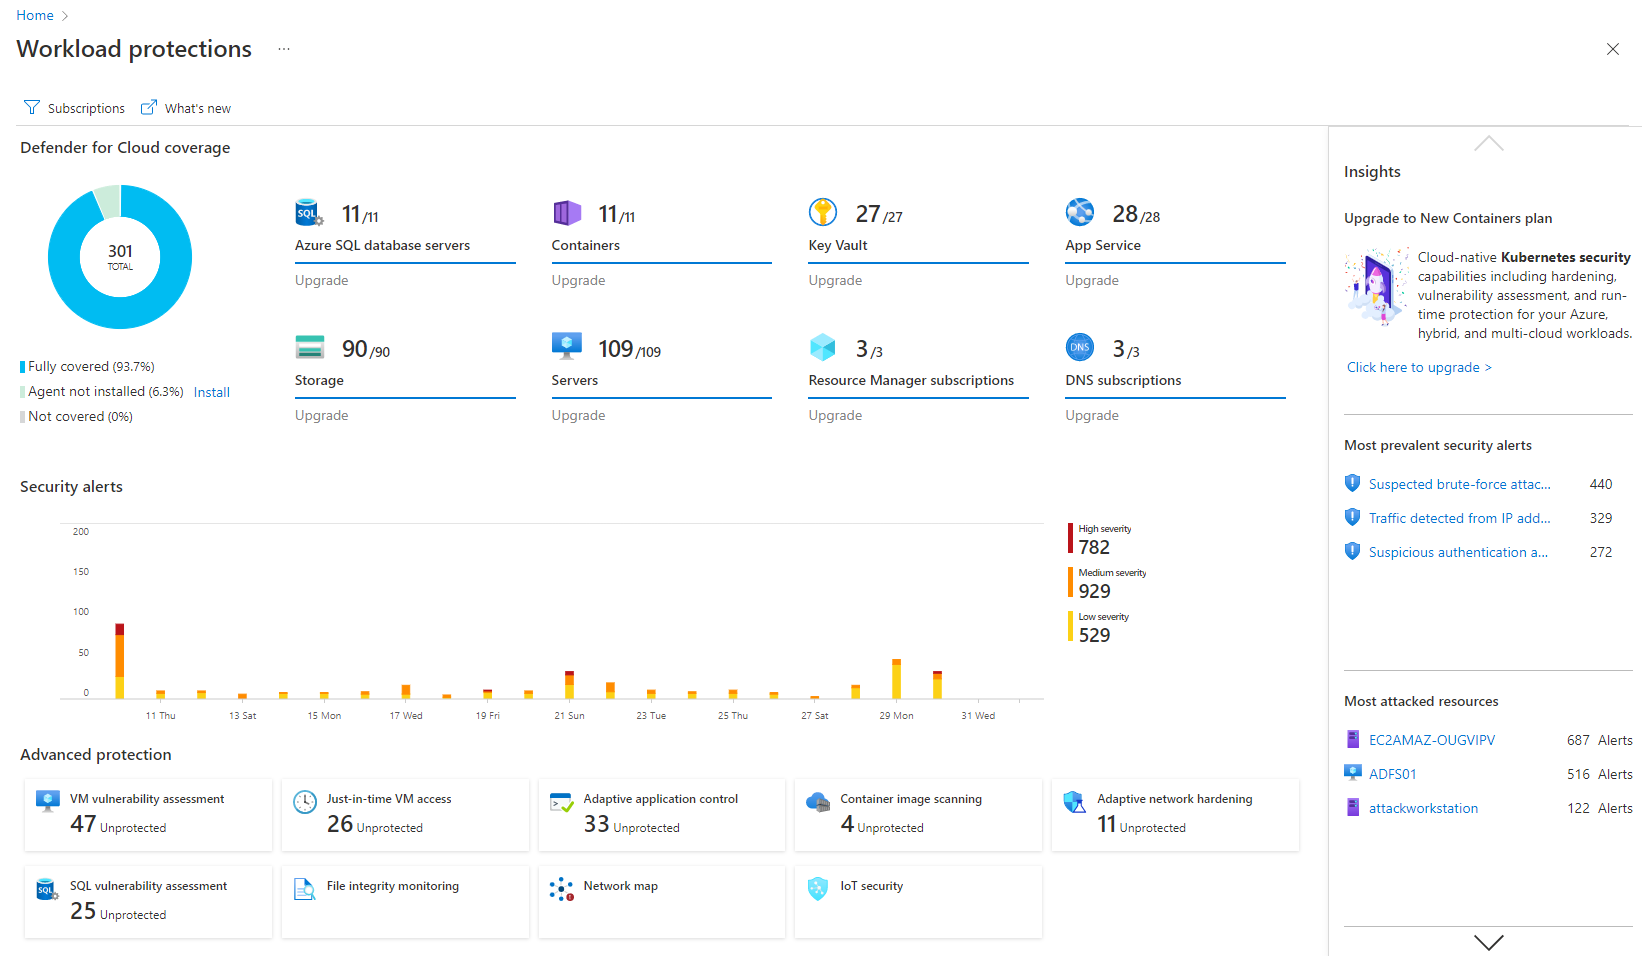
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
It provides fewer false positives and a more granular approach to eliminating them, allowing us to focus on threats. Also, with the need to secure both on-premise and cloud-based web applications, we can only use Azure on the cloud part, but we still need to cover on-premise …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is doing its job effectively, and its scalability is superb. So, if you have a mixed environment with cloud and on-premise systems to protect this product, provide a solution to the challenge. However, its management is more suited to DevOps teams rather than to the ones responsible for on-premise systems, making the management a bit more complex.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Layer seven attacks are becoming far more common. Traditionally it was always layered three, layer four, where you get an additional firewall, but with the application layer attacks become more frequent, more popular, et cetera. So having the web application firewall protecting us, and then with the recent Log4j, that's the most recent use case when it gave us that instant level of protection whilst we remediated the Log4j that we had that and the F5 Distributed Cloud WAF was protecting us.
I have a great relationship with the account manager, my account manager, and I think he drives the best price possible, um, for me, and I'm happy with that price.
F5 Distributed Cloud WAF is always innovating and evolving.
We run a very competitive proof value where we run numerous competitors against each other, and then we evaluate from that and then make the selection, and F5 Distributed Cloud WAF was the winner.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We gave it an 8 because it protects our web apps well and is reliable. The WAF is flexible and meets most of our needs. It could improve in user interface and make integrations easier, but overall, it’s a solid and effective security tool for us.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
I believe is a solution that was designed from the start to be simple and easy to use. Coming from Imperva, it simply eased the burden and complexity of managing and securing our apps on different environments (cloud and on-prem). It easy to scale and very quick to deploy (as a cloud waf should be), provide us with DevOps integrations, visibility and automatic insights from multiple events that guarantee peace of mind for us analysts and opp managers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The other one that I've used in the past, they're very similar and I haven't used it recently, so I can't do a side-by-side comparison today. But I can say that F5 does everything we want it to do consistent with what this other product did do and it's got enhanced features and of course we have a long history with F5 as a product set in general.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The biggest gain for us was speed. Before F5 Distributed Cloud WAF, onboarding a new app to our WAF stack meant manual rule tuning, traffic sampling and regression testing. Right now, we spin up a service, tag it with the right policy and its ready (production ready) within hours
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info