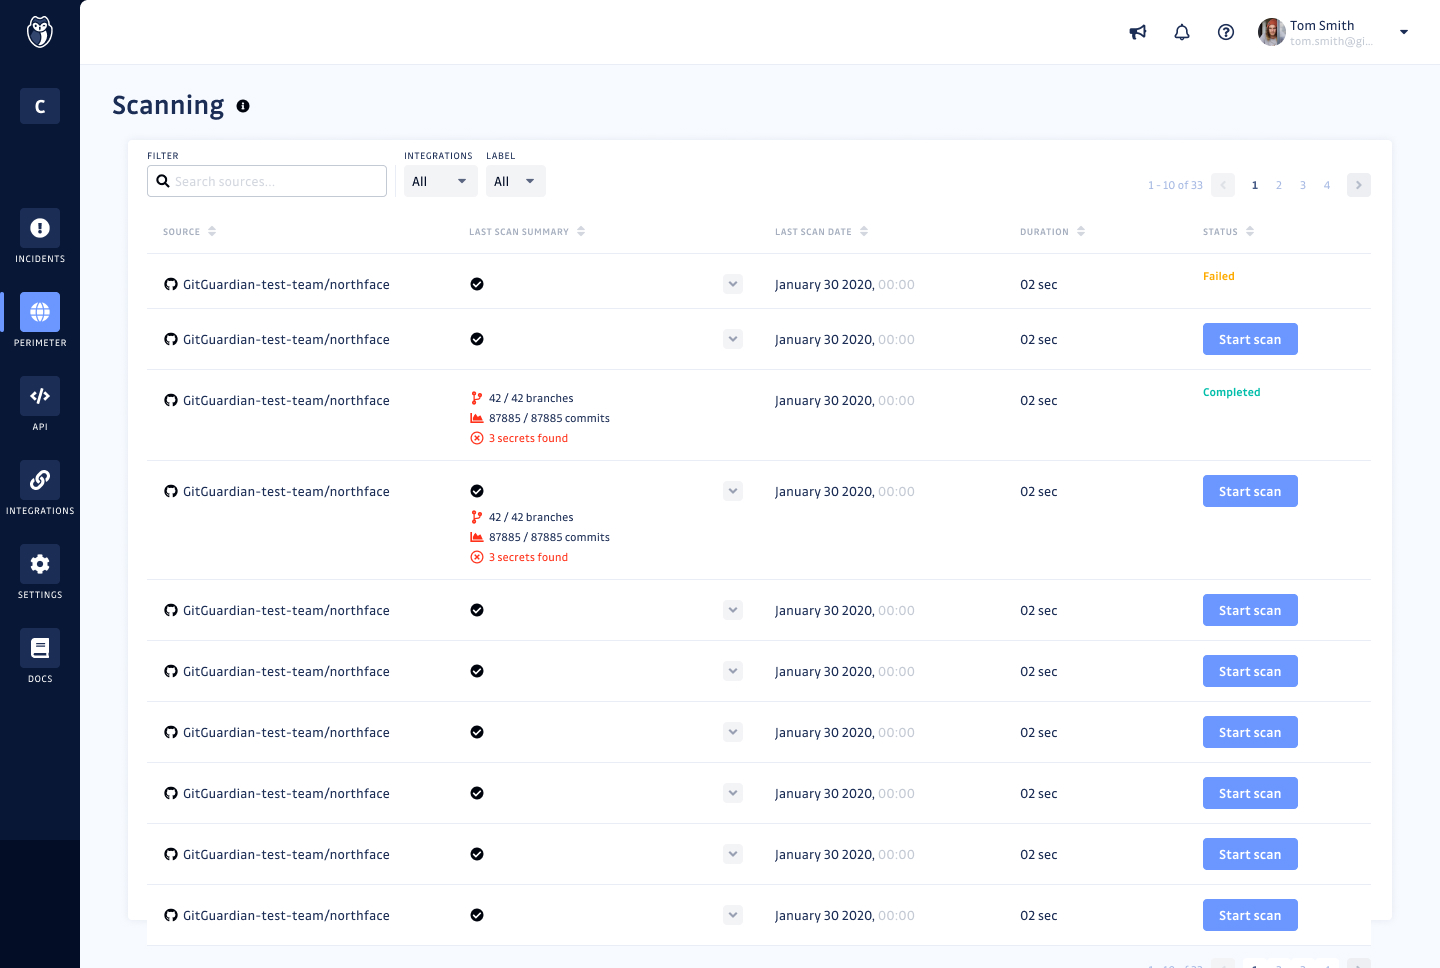
GitGuardian is an end-to-end NHI security platform designed to help organizations strengthen their Non-Human Identity (NHI) security posture and address compliance standards and regulations. As attackers increasingly target NHIs, such as service accounts, service principals, and applications, protecting and managing these critical assets has become paramount. NHIs rely on “secrets” like API keys and certificates for authentication, and their rapid proliferation has led to significant…
$0
(for individuals or up to 25 devs)
Trellix ePolicy Orchestrator
Score7 out of 10
N/A
Trellix ePolicy Orchestrator (formerly McAfee ePolicy Orchestrator) software centralizes and streamlines management of endpoint, network, data security, and compliance solutions.
I do think it'll absolutely fit everyone who codes integrates with another platform or services. We all forget that one credentials one in a while, and especially those who managed public repository, it is important to keep an eye on accidentally committed credentials. While I think you don't really needs it for personal project, it's a nice to have, you don't want to waie up to 50k USD of sudden surcharge on resources you don't use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
[McAfee ePolicy Orchestrator] seems to be better suited to large enterprise applications... I don't feel it really suits the or self-managed SMB market. The general joe is not going to understand how to wield this product to it's full potential. For those of us managing large networks, this is a very ideal product for managing multiple sites and users.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian monitors every public or private GitHub commit ( that have GitGuardian installed) and event in real-time for secrets and sensitive data. In a leak scenario it immediately notifies us.
It uses sophisticated pattern matching techniques to detect credentials that cannot be strictly defined with a distinctive pattern (like unprefixed credentials)
It covers several API providers, database connection strings, private keys, certificates, usernames and passwords etc
GitGuardian have high True Positive Rate of around 91% and reduces alert fatigue with smart occurrences regrouping
Static malware scans for known bad processes and files works well and can be schedules on endpoints easily
Preventing users from accessing USB drives and other peripherals is easily configured. We can also allow users to access to USB drives with user codes for the times they need it for business reasons.
ePO provides access into our MSME software so that we're not managing many different products from different locations.
In recent years the console has gotten much easier to navigate even though there is a ton of information to be accessed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved user interface: It would be beneficial to have a more intuitive and user-friendly interface for Internal Monitoring on GitGuardian. This would make it easier for users to quickly access the data they need and understand the results of their scans.
Automated alerts: It would be helpful to have automated alerts when certain conditions are met, such as when a scan reveals sensitive data or when a new repository is created. This would help users stay informed and take action in a timely manner.
More detailed reports: Currently, Internal Monitoring reports are limited in terms of the depth of information they provide. It would be useful to have more detailed reports that include additional metrics, such as the number of repositories scanned and the types of sensitive data found.
Faster scan times: Scan times can be slow at times, making it difficult to stay on top of changes in repositories quickly. It would be beneficial to have faster scan times so that users can take action quickly when needed.
It has a slow mechanism when adding custom threat feeds. For example, if McAfee didn't have a signature or detection about a new virus and we try to add it to our console it is like a really big process in adding that to our available signatures.
Whenever a scan is performed, the system CPU utilization goes up 100 percent.
Installation fails due to difference in timestamp when we try to shuffle between packages.
McAfee support is definitely GREAT! It is one of the best technical support on a business level. GOLD support is recommended to business. Their website is easy and quick to create a ticket. Their technical team usually responds right away with an email or call. Via call and web they provide a full and complete support until the issue is resolved. The best, most of the time they explain in detail what is the issue, the reason and how to resolve it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I've evaluated quite a few other tools, like git-secrets, Git-leaks, scan, and maybe a few more. They're all great but quite surprisingly none of them detected Github OAuth Secrets for us. A lot of the FOSS tools out there focus on much simpler, generic secrets, which is good in itself but with GitGuardian, it was dead simple from day one. I just connected our Github Account and set up the gg-shield cli and that was all.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have used Symantec Endpoint Encryption before. Symantec and EPO are both good in their own ways. EPO allows integration of other McAfee products. I have been using ePolicy Orchestrator for years. I have a lot of experience with the product. That is why I like it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian Internal Monitoring has had a positive impact on our overall business objectives. By providing visibility into our code repositories and alerting us to potential security risks, we have been able to identify and mitigate security issues before they become a problem. This has allowed us to focus more on developing our product and less on responding to security incidents. We have also seen an increase in customer confidence in our product as a result of using GitGuardian Internal Monitoring, which has led to increased customer loyalty and retention. Overall, the ROI of using GitGuardian Internal Monitoring has been very positive for our business.
We have seen an increase in the security of our codebase, as well as an improvement in the speed and accuracy of our code reviews. This has enabled us to quickly identify and address any potential security issues before they become a problem. Additionally, we have seen an increase in our ROI as a result of using GitGuardian Internal Monitoring, as it has allowed us to save time and money by preventing costly security breaches.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info