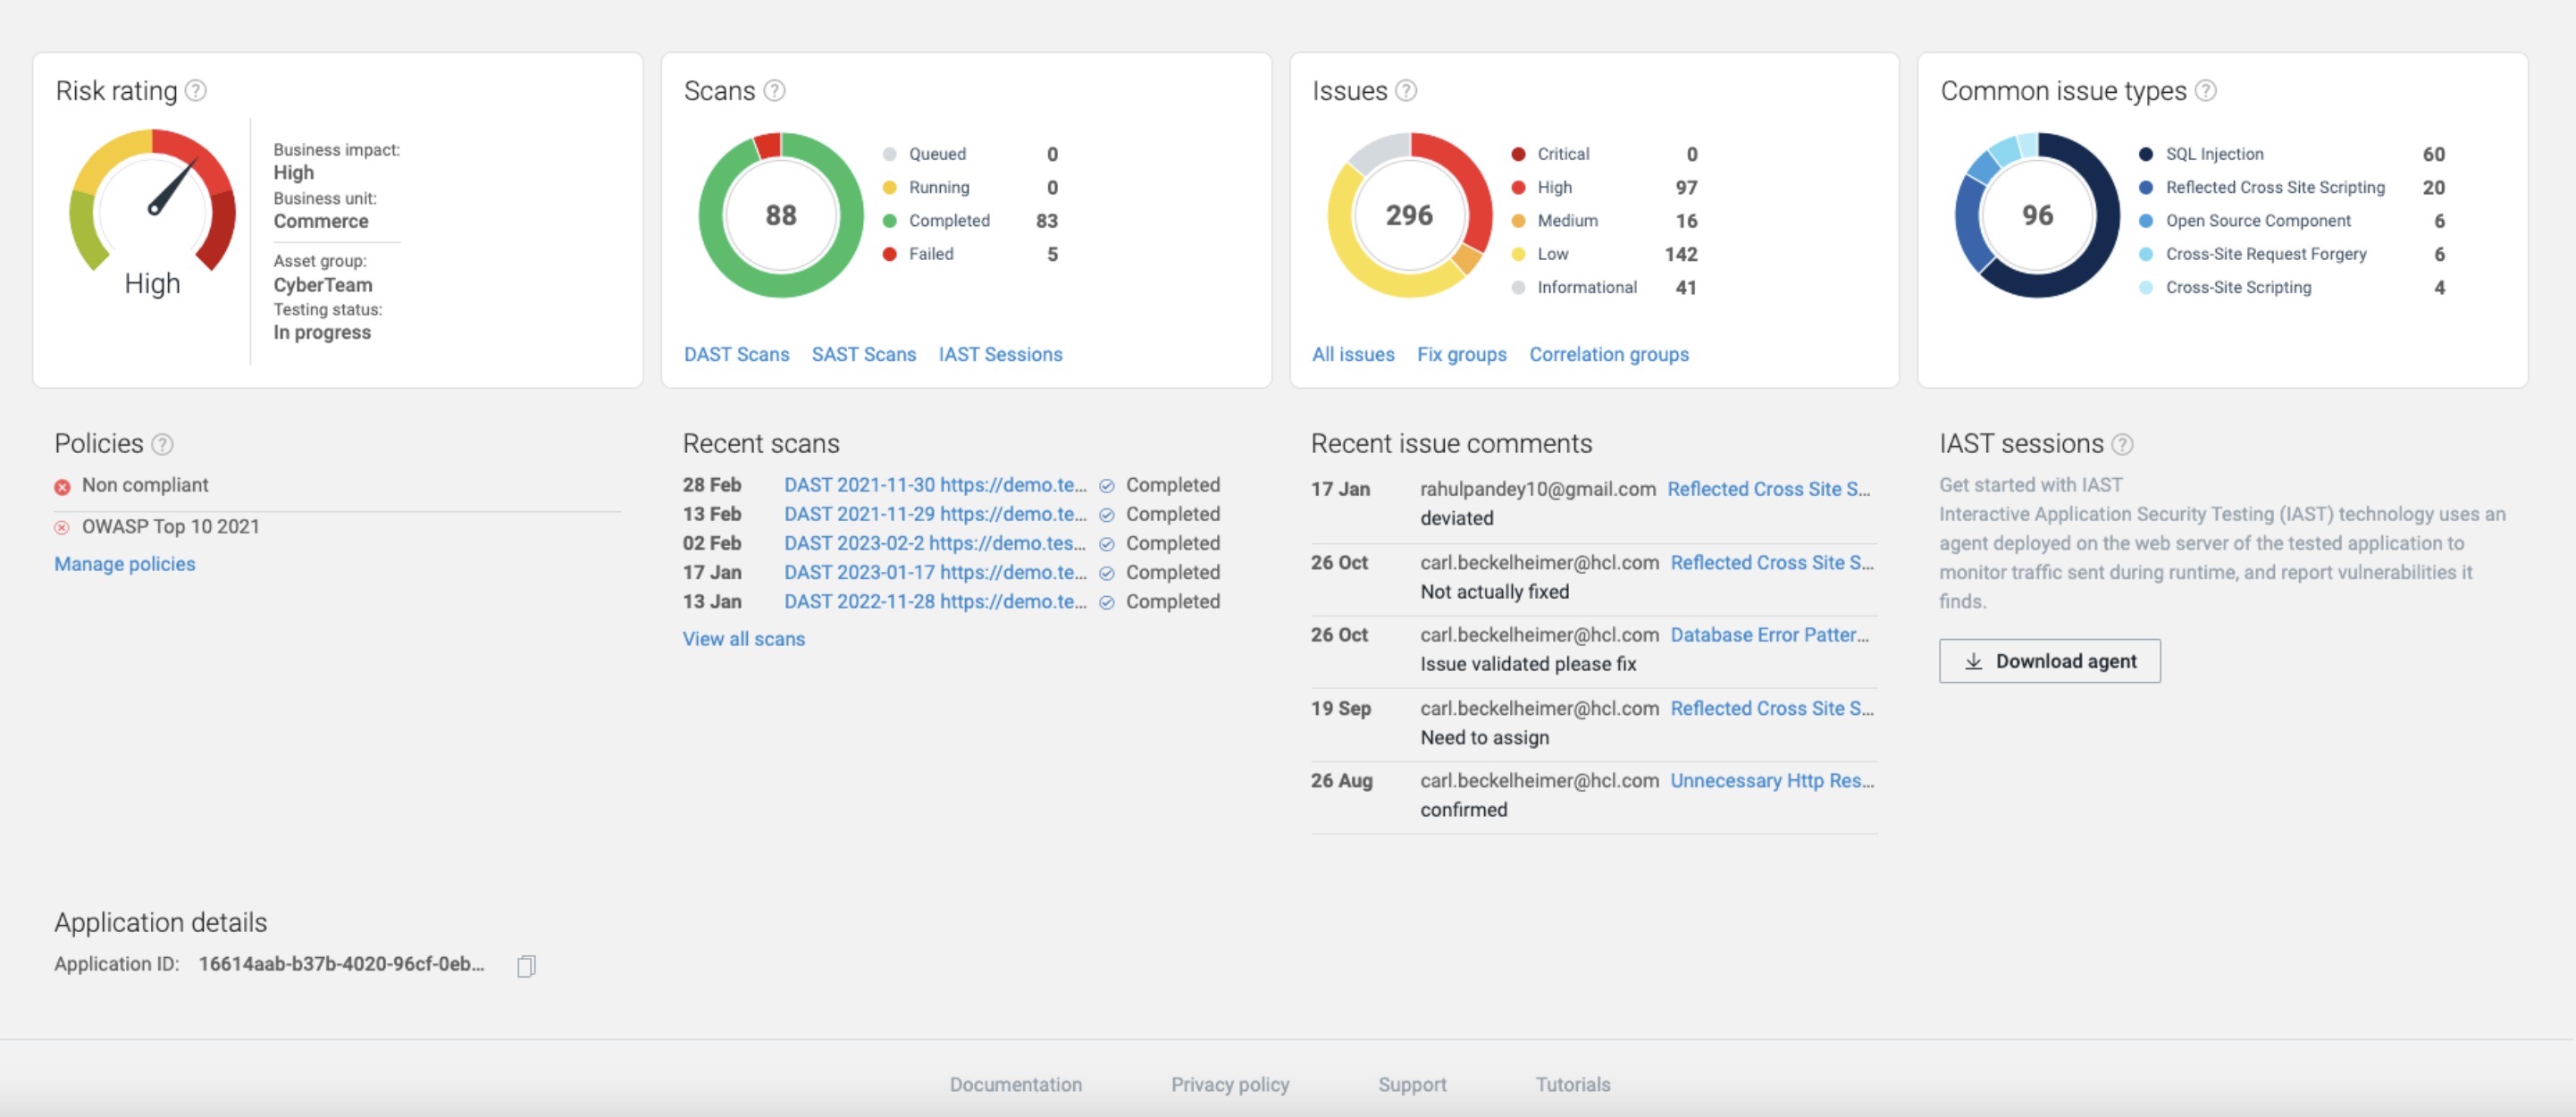
AppScan (formerly Rational AppScan) is an application security testing solution acquired by HCL Technologies from IBM in late 2018. Appscan supports both dynamic (DAST) and static (SAST) application security testing.
$29.99
one-time fee per scan (Choice of DAST, SAST, or SCA scans)
Trellix ePolicy Orchestrator
Score7 out of 10
N/A
Trellix ePolicy Orchestrator (formerly McAfee ePolicy Orchestrator) software centralizes and streamlines management of endpoint, network, data security, and compliance solutions.
N/A
Pricing
HCL AppScan
Trellix ePolicy Orchestrator
Editions & Modules
No answers on this topic
No answers on this topic
Offerings
Pricing Offerings
HCL AppScan
Trellix ePolicy Orchestrator
Free Trial
Yes
No
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
Pricing varies based on factors such as deployment model, application volume, users, and capabilities. A personalized quote is required based on the environment and its security requirements.
In HCL AppScan automation maintain a reasonable pace of review and remediation of flaws for our apps. HCL AppScan is a cloud-based enterprise mobile application security testing solution for Android and iOS applications developed using Java, .Net or Objective-C. So it covers all our area and It consists of three components: AppScan Source Edition for developing and testing apps internally, AppScan Standard Edition for testing internally or externally, and AppScan Enterprise Edition for large enterprises who need to secure their entire mobile application portfolio across the organization with multiple device types.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
[McAfee ePolicy Orchestrator] seems to be better suited to large enterprise applications... I don't feel it really suits the or self-managed SMB market. The general joe is not going to understand how to wield this product to it's full potential. For those of us managing large networks, this is a very ideal product for managing multiple sites and users.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AppScan works well in finding application vulnerabilities such as SQL injection, cross-site scripting and all of the OWASP top 10.
Flexible reporting allows us to generate executive reports for application owners as well as separate technical reports for developers and system engineers.
Technical reports include remediation information and cross reference CVSS scores
Because it maintains data on all repeated assessments it helps us to do trending and metrics on compliance
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Static malware scans for known bad processes and files works well and can be schedules on endpoints easily
Preventing users from accessing USB drives and other peripherals is easily configured. We can also allow users to access to USB drives with user codes for the times they need it for business reasons.
ePO provides access into our MSME software so that we're not managing many different products from different locations.
In recent years the console has gotten much easier to navigate even though there is a ton of information to be accessed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It has a slow mechanism when adding custom threat feeds. For example, if McAfee didn't have a signature or detection about a new virus and we try to add it to our console it is like a really big process in adding that to our available signatures.
Whenever a scan is performed, the system CPU utilization goes up 100 percent.
Installation fails due to difference in timestamp when we try to shuffle between packages.
McAfee support is definitely GREAT! It is one of the best technical support on a business level. GOLD support is recommended to business. Their website is easy and quick to create a ticket. Their technical team usually responds right away with an email or call. Via call and web they provide a full and complete support until the issue is resolved. The best, most of the time they explain in detail what is the issue, the reason and how to resolve it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Both solutions are decent, however, I had team members who had the experience working with HCL AppScan. Also, the product was priced nominally which suited our budget. Further, HCL AppScan's user community was bigger and many learning resources were freely available which helped junior peers learn quickly and eliminate any issues
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have used Symantec Endpoint Encryption before. Symantec and EPO are both good in their own ways. EPO allows integration of other McAfee products. I have been using ePolicy Orchestrator for years. I have a lot of experience with the product. That is why I like it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There are countless implementations to accomplish the same thing, and so many configurations are required.
Even if you test it finished and find no vulnerabilities, there is no point if you just get the error screen.
Until now, I was worried about vulnerabilities and security in software development, but I think it was good to find the vulnerability problem quickly with HCL AppScan.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info