TrustRadius: an HG Insights company

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Identity Rules

    N/AN/AIdentity Rules is a unified Identity Threat Detection and Response (ITDR) and Identity Visibility and Intelligence Platform (IVIP) developed for security teams at regulated enterprises. The platform combines real-time detection of identity-based threats with continuous visibility and intelligence across human and non-human identities, spanning Active Directory, Okta, Microsoft Entra ID, AWS IAM, Google Workspace, Oracle Database, and Linux environments. Key…N/A

    InsightIDR

    Score8.6 out of 10
    N/AIn addition to their incident response service, Rapid7 offers InsightIDR, a combined XDR and SIEM that provides user behavior and threat analytics.

    $5.89

    per month per asset

    Pricing
    Identity RulesInsightIDR
    Editions & Modules
    No answers on this topic
    InsightIDR Advanced
    $5.89
    per month per asset
    Offerings
    Pricing Offerings
    Identity RulesInsightIDR
    Free Trial
    NoYes
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional Details—*500 asset minimum. Billed annually. All amounts are shown in U.S. dollars. International prices vary.
    More Pricing Information
    Community Pulse
    Identity RulesInsightIDR
    Considered Both Products
    Identity Rules
    No answer on this topic
    Rapid7
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    100%
    Would buy again
    12 Answers
    Delivers good value for the price
    No answers on this topic
    91%
    Delivers good value for the price
    10 Answers
    Happy with the feature set
    No answers on this topic
    100%
    Happy with the feature set
    12 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    100%
    Lived up to sales and marketing promises
    12 Answers
    Implementation went as expected
    No answers on this topic
    100%
    Implementation went as expected
    12 Answers
    Best Alternatives
    Identity RulesInsightIDR
    Small Businesses
    No answers on this topic
    Microsoft Defender XDR
    Score8.7 out of 10
    Medium-sized Companies
    ManageEngine ADAudit Plus
    Score9 out of 10
    Microsoft Defender XDR
    Score8.7 out of 10
    Enterprises
    ManageEngine ADAudit Plus
    Score9 out of 10
    Palo Alto Networks Cortex XDR
    Score8.5 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    Identity RulesInsightIDR
    Likelihood to Recommend
    -
    (0 ratings)
    10.0
    (12 ratings)
    User Testimonials
    Identity RulesInsightIDR
    Likelihood to Recommend
    Identity Rules
    No answers on this topic
    Rapid7
    It has been brilliant for us in terms of understanding the behaviour affecting our endpoints and assets. We have full visibility of our alerts, which menas we can act on them immediately. We use a single pain of glass with dashboards that can be easily drilled down into to get further information. It has laso helped us eo create bespoke reports for senios Managmeent, while at the same time supports other teams like Network Mnagement and Operations.
    Incentivized
    Read full review
    Pros
    Identity Rules
    No answers on this topic
    Rapid7
    • Rapid7 InsightIDR does a very good job at keeping virus definitions up to date so that our threat intelligence is very up to date when knowing what to protect against.
    • It helps us by scanning all of our infrastructure components and highlights where improvements need to be made in security so we can be proactive with our security initiatives.
    • It has automated response mechanisms to triage and resolve any potentials risks allowing us to save time in the long run.
    Incentivized
    Read full review
    Cons
    Identity Rules
    No answers on this topic
    Rapid7
    • Sometimes Rapid7 InsightIDR will be too locked down and without knowing will block applications and processes needed for day to day operation.
    • System scans with Rapid7 InsightIDR can be very bandwidth-heavy on the network and system resources.
    • From a recent incident, we have seen more and more false positives from Rapid7 InsightIDR on areas that we know are secure.
    Incentivized
    Read full review
    Alternatives Considered
    Identity Rules
    No answers on this topic
    Rapid7
    The biggest advantage it has the lightweight agent and smooth and less traffic chaos in network during log collection. Cloud Security always require extra efforts but InsightIDR reduce that burden as it has highly anticipated agents to which knows what they need to do when they captured malicious traffic.log collection and threat intelligence is major part in and xdr and here it stand out along others in the market, I started my career as qualys administration but I like InsightIDR much now.
    Incentivized
    Read full review
    Return on Investment
    Identity Rules
    No answers on this topic
    Rapid7
    • Rapid7 InsightIDR has allowed us to be proactive in securing our systems as the vulnerability scans give us a lens at what we need to fortify when it comes to security.
    • In recent incidents its allowed us to save time and money as it mostly detects issues accurately and we are able to bring systems back quickly without too much downtime for the business.
    • With recent updates, we are confident that Rapid7 InsightIDR is a good solution for the long run as they are always making adjustments to their platform and improving it with every release.
    Incentivized
    Read full review
    ScreenShots

    Identity Rules Screenshots

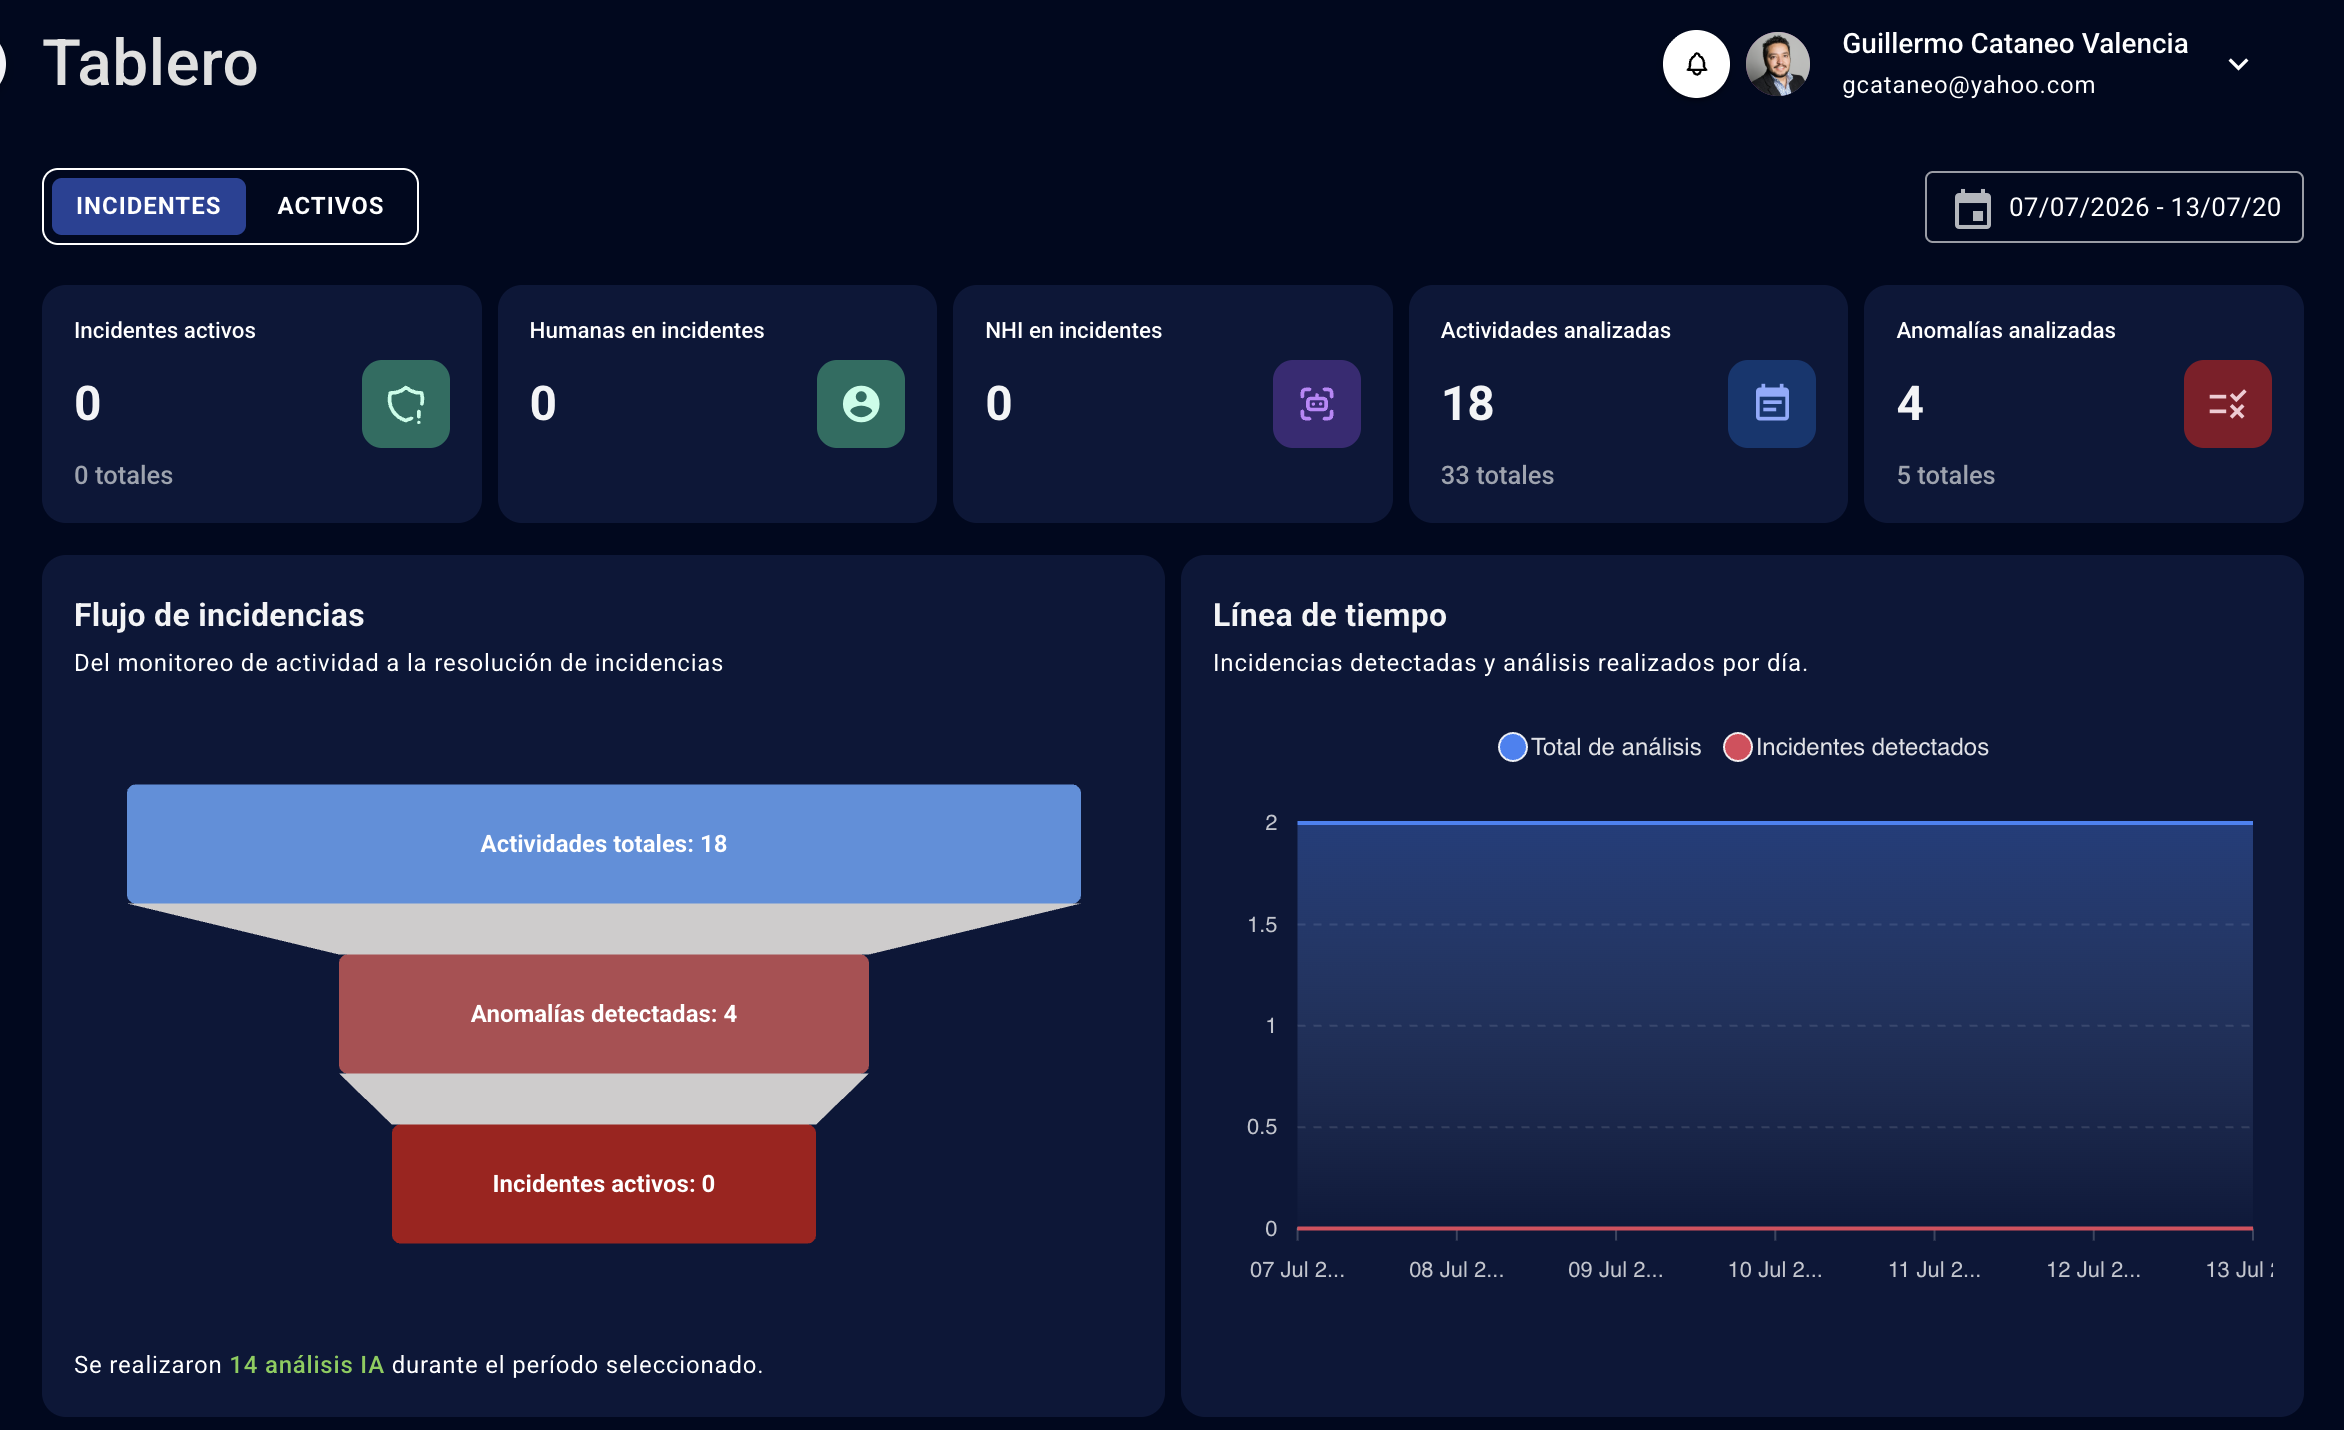
    Screenshot of Executive dashboard showing the identity activity funnel — from monitored activities (18) to anomalies detected (4) to active incidents (0) — for a selected date range. Adjacent timeline visualizes incident detection and total AI-driven  analysis events per day, with headline KPIs for active incidents, human vs. non-human identities involved, activities analyzed, and anomalies analyzed.Screenshot of Assets tab of the executive dashboard, delivering a unified inventory of 17 identities, 116 human accounts, 170 non-human identities (NHI), 599 entitlements, and 728 anomalies. Account risk distribution (Critical, High, Medium, Low) sits alongside behavioral anomaly indicators such as "NHI credential never expires" (169) and "NHI credential not rotated" (164), plus account state breakdown between active, locked, deleted, privileged, and shared accounts.Screenshot of Security incident management workspace where SOC and IAM teams triage identity threats across all connected systems. Each incident is displayed with source application (Google Workspace shown here), severity (Critical / High / Medium / Low), lifecycle state (New, In Triage, Closed), 
AI-calculated confidence score, and final verdict — including labels like Token Theft, Lateral Movement, Password Spraying, Legitimate Activity, Business Exception, and Insufficient Evidence.Screenshot of Detailed incident view for a high-severity case: "NHI account without owner and insecure credentials in Google Workspace". The AI Analysis tab maps the finding to MITRE ATT&CK tactic TA0006 (Credential Access) and technique T1556 (Modify Authentication Process) at 80% confidence, showing affected accounts, related activities, and correlated anomalies. An AI-generated Quality Assessment panel surfaces assumptions, evidence gaps, and cross-incident correlations so analysts can act with full context.Screenshot of Analytics view organizing every identity anomaly by MITRE ATT&CK tactic and technique. isplayed here: TA0006 (Credential Access) with 7 detections across 2 techniques, and TA0003 (Persistence) with 2 detections across 2 techniques. The right-hand panel drills into T1556 (Modify uthentication 
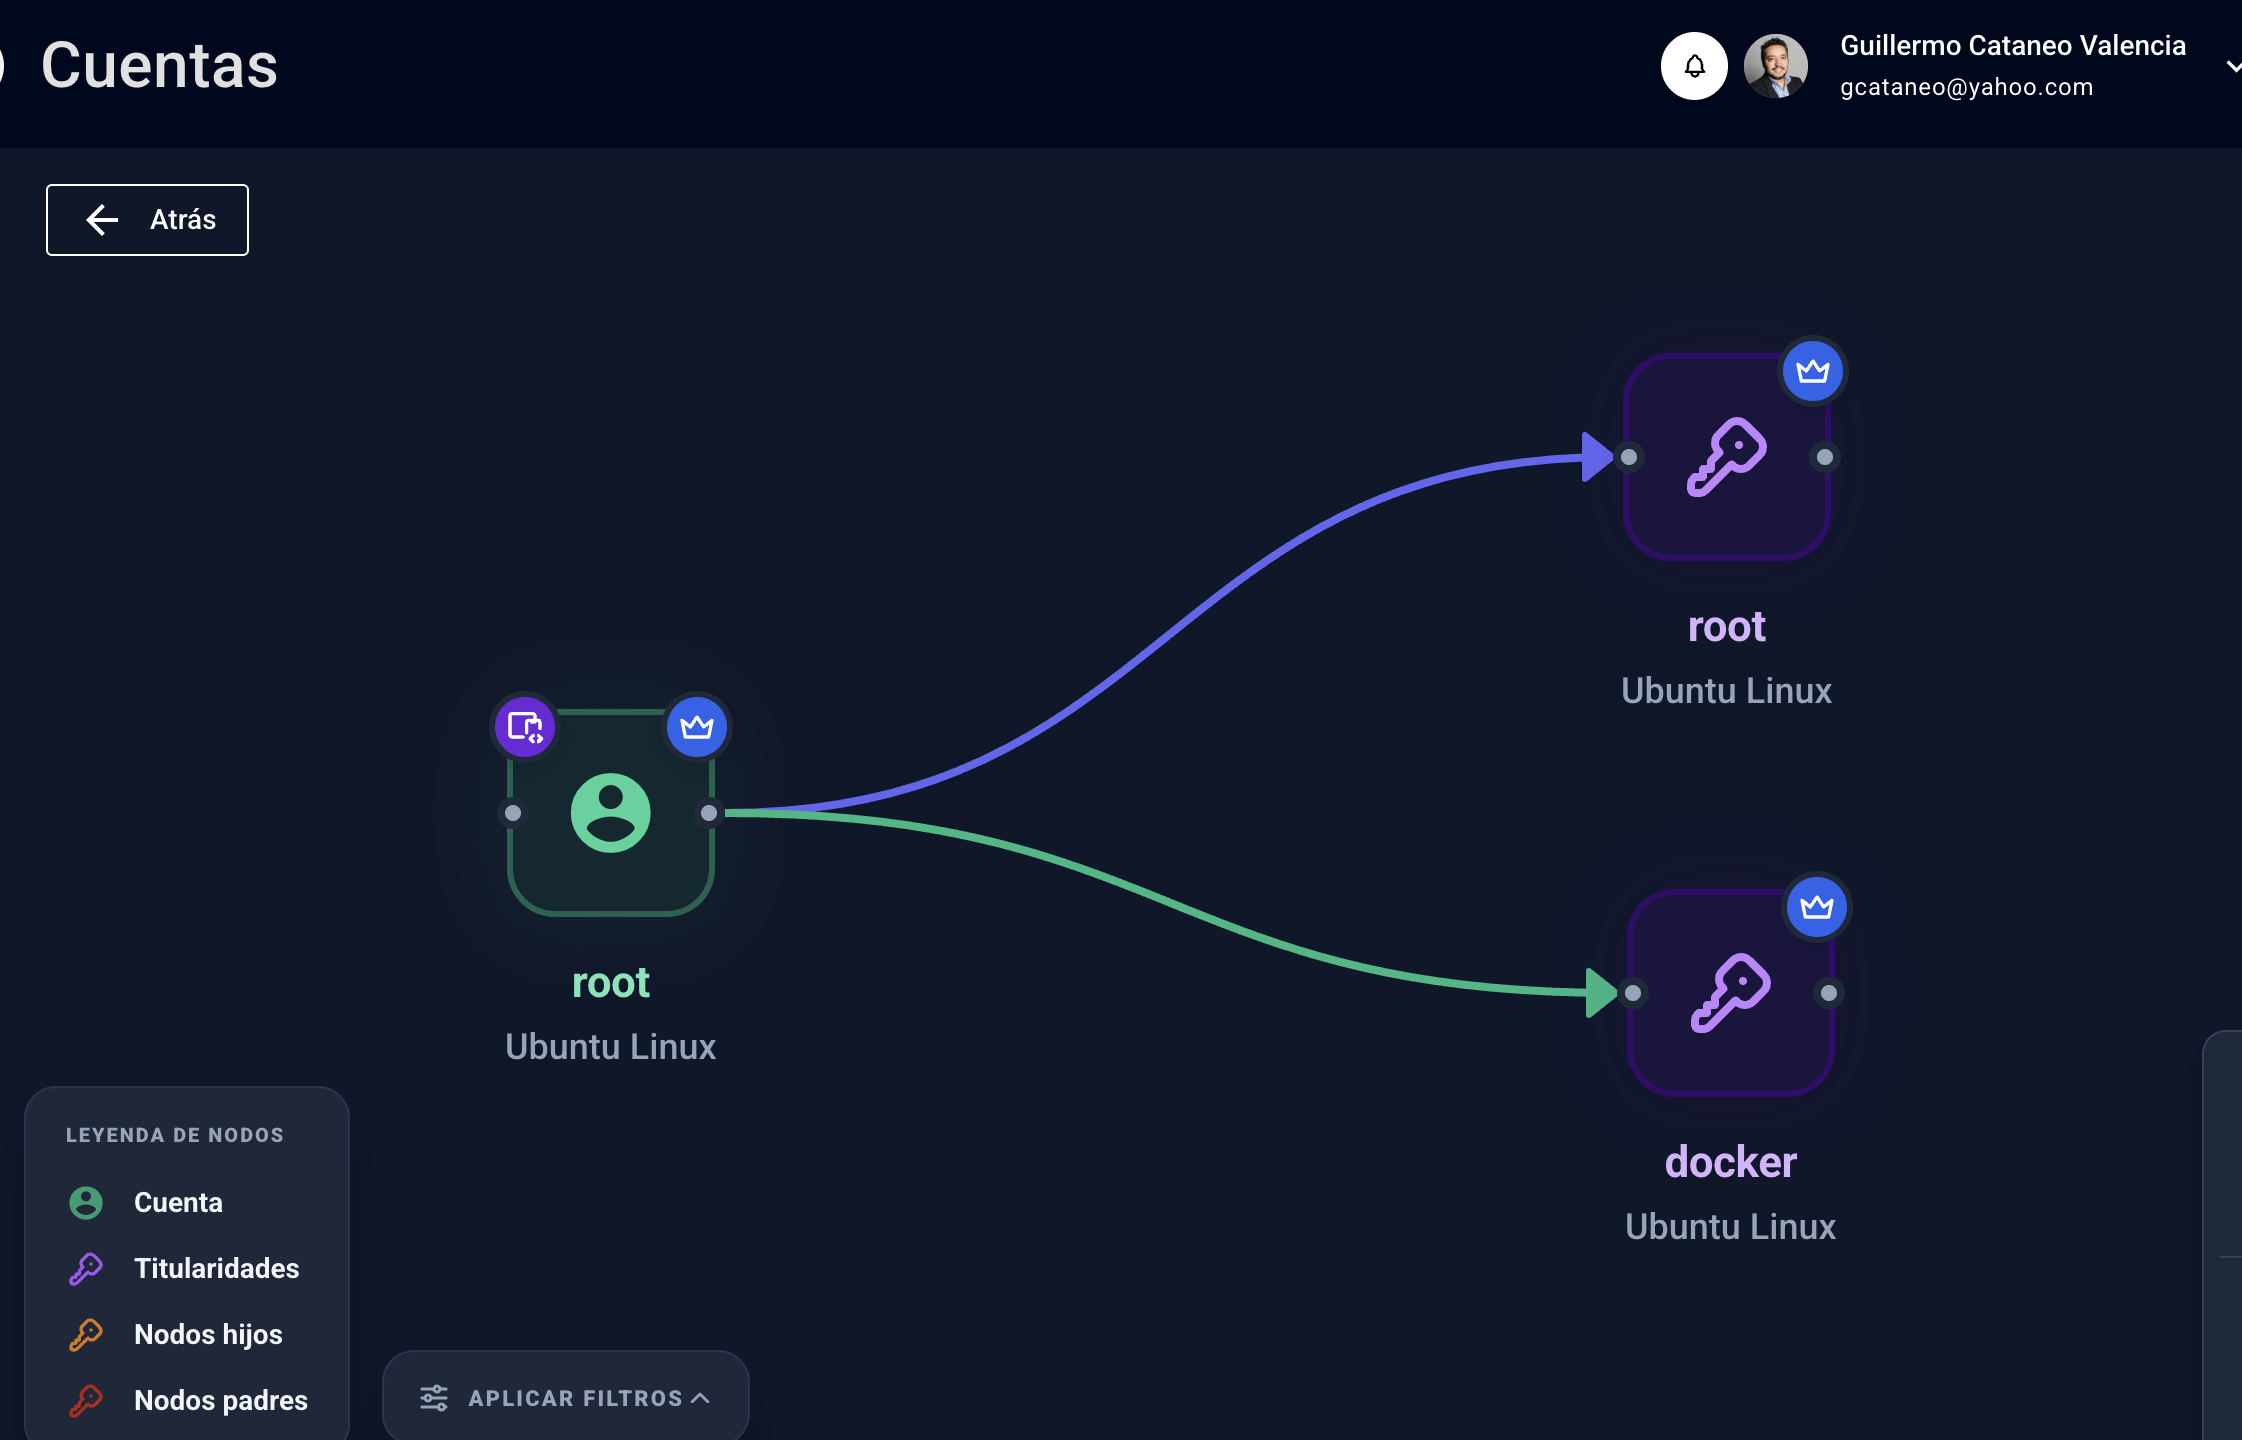
Process) showing each individual detection with application, stage, verdict (Legitimate Activity, Business Exception), severity, and affected accounts — giving SOC teams a native ATT&CK-aligned view of their identity attack surface.Screenshot of Interactive graph visualization of account relationships. Central node shows a Linux "root" account on Ubuntu, connected via directional edges to its two entitlements — "root" and "docker" privileged access on Ubuntu Linux. The legend explains node types (accounts, entitlements, child nodes, parent nodes), giving IAM and security teams a visual map of how privileges are structured across systems.