Sensagraph vs. Tenable Nessus

Overview
ProductRatingMost Used ByProduct SummaryStarting Price
Sensagraph
Score 0.0 out of 10
N/A
Sensagraph is an agentless external security scanning platform that shows you your web applications the way an attacker sees them: from the public internet, with nothing to install and no code to change. Point Sensagraph at a domain, verify ownership once, and it maps any app's real attack surface across five focused capabilities: Web Application Vulnerability Detection (SQL injection, XSS, CSRF, and the rest of the OWASP Top 10), Web Server Configuration Analysis,…
$19
per month
Tenable Nessus
Score 8.8 out of 10
N/A
Tenable headquartered in Columbia offers Nessus, a vulnerability scanning and security assessment solution used to analyze an entity's security posture, vulnerability testing, and provide configuration assessments.
$2,790
Pricing
SensagraphTenable Nessus
Editions & Modules
Scout
$19
per month
Sentinel
$49
per month
Ops
$119
per month
Scout
$190
per year
Sentinel
$490
per year
Ops
$1,190
per year
1 Year
$2,790.00
1 Year + Advanced Support
$3,190.00
2 Years
$5,440.00
2 Years + Advanced Support
$6,240.00
3 Years
$7,951.00
3 Years + Advanced Support
$9,151.00
Offerings
Pricing Offerings
SensagraphTenable Nessus
Free Trial
NoNo
Free/Freemium Version
YesNo
Premium Consulting/Integration Services
NoNo
Entry-level Setup FeeNo setup feeNo setup fee
Additional DetailsSensagraph is priced as a simple, self-serve subscription with no setup fees, no long procurement cycle, and no mandatory sales call to get started. A free plan includes 1 full external scan per month, so you can evaluate the product on your own domain before paying anything. Paid plans are built to scale with how much you scan and how many domains you monitor, which makes the product a good fit for a range of buyers: solo developers securing a single site, SaaS teams watching their production environment, and agencies managing many client domains from one account. There are no agents to license per host and no per-endpoint charges, so pricing stays predictable as your footprint grows. Every plan includes the same core scanning engine and the client-ready PDF report, so you are choosing based on scan volume and domain coverage, not being locked out of key security features at lower tiers.
More Pricing Information
Community Pulse
SensagraphTenable Nessus
Features
SensagraphTenable Nessus
Threat Intelligence
Comparison of Threat Intelligence features of Product A and Product B
Sensagraph
-
Ratings
Tenable Nessus
6.3
4 Ratings
25% below category average
Network Analytics00 Ratings1.02 Ratings
Threat Recognition00 Ratings7.14 Ratings
Vulnerability Classification00 Ratings9.53 Ratings
Automated Alerts and Reporting00 Ratings10.03 Ratings
Threat Analysis00 Ratings5.63 Ratings
Threat Intelligence Reporting00 Ratings5.13 Ratings
Automated Threat Identification00 Ratings5.63 Ratings
Vulnerability Management Tools
Comparison of Vulnerability Management Tools features of Product A and Product B
Sensagraph
-
Ratings
Tenable Nessus
7.5
4 Ratings
10% below category average
IT Asset Realization00 Ratings7.03 Ratings
Authentication00 Ratings7.63 Ratings
Configuration Monitoring00 Ratings8.14 Ratings
Web Scanning00 Ratings5.63 Ratings
Vulnerability Intelligence00 Ratings9.34 Ratings
Best Alternatives
SensagraphTenable Nessus
Small Businesses
Action1
Action1
Score 9.6 out of 10
Action1
Action1
Score 9.6 out of 10
Medium-sized Companies
Action1
Action1
Score 9.6 out of 10
Action1
Action1
Score 9.6 out of 10
Enterprises
CrowdStrike Falcon
CrowdStrike Falcon
Score 9.0 out of 10
CrowdStrike Falcon
CrowdStrike Falcon
Score 9.0 out of 10
All AlternativesView all alternativesView all alternatives
User Ratings
SensagraphTenable Nessus
Likelihood to Recommend
-
(0 ratings)
9.0
(9 ratings)
Likelihood to Renew
-
(0 ratings)
9.1
(1 ratings)
Usability
-
(0 ratings)
8.0
(5 ratings)
Support Rating
-
(0 ratings)
7.1
(4 ratings)
User Testimonials
SensagraphTenable Nessus
Likelihood to Recommend
Kaşgar Yazılım
No answers on this topic
Tenable
It is an excellent tool for scanning servers, workstations, and network devices to identify missing patches and misconfiguration; we regularly use it to confirm patch effectiveness after the update; it also helps us for preparing audits such as iso 27001, and regulatory requirements, it also helps us to identify open ports and services that violate security.
Read full review
Pros
Kaşgar Yazılım
No answers on this topic
Tenable
  • Nessus is best at performing vulnerability scans, in fact, it gives findings and moreover accurate findings of the assessments. It does not do penetration testing or exploit the vulnerabilities because it is concerned about scanning the systems/applications.
  • In fact, Nessus has multiple profiles/policies to perform different types of scans such as, scans oriented for PCI-DSS, malware scans, web application scans, bad shell shock detection scan to name a few.
  • Nessus has the ability to classify the vulnerabilities into risk-based categories from critical to even informational which I think is one of the things that separates Nessus from other vulnerability scanners.
Read full review
Cons
Kaşgar Yazılım
No answers on this topic
Tenable
  • The tool has lots of options for setting up before scanning any device, this methodology could be simplified further with default configuration for various devices predefined, anyhow we can use this technique by making use of policies.
  • For advanced users we cannot disable the plugins inside the plugin groups, we can enable the whole set of plugins at a time, for few hundreds its ok, but thousands of plugins are of waste of resource and time.
Read full review
Likelihood to Renew
Kaşgar Yazılım
No answers on this topic
Tenable
Nessus is best and easy to use application for Vulnerabilities finding and reporting, it has multiple platforms and wide scope covering almost all devices for security improvement so far, thus we are very likely to continue its services.
Read full review
Usability
Kaşgar Yazılım
No answers on this topic
Tenable
Tenable Nessus is a great product and provides a lot of value, but it is difficult to set up and use and the amount of data it generates can be overwhelming. It does help us prioritize based on the severity of the detection, however there are sometimes mitigating factors that we have implemented that Nessus does not account for, which causes lots of noise in the reports.
Read full review
Support Rating
Kaşgar Yazılım
No answers on this topic
Tenable
I haven't needed to contact support yet. But issues are easily solved with a quick internet search which means support and by extension, the larger community are involved and knowledgeable.
Read full review
Alternatives Considered
Kaşgar Yazılım
No answers on this topic
Tenable
Sometimes when we identify a vulnerability with Nessus that has an exploit, we made a proof of concept with Metasploit in order to show to the IT managers the importance of the software/hardware hardening.
Read full review
Return on Investment
Kaşgar Yazılım
No answers on this topic
Tenable
  • Nessus certainly has a positive impact while me while performing my job, either as security research, or performing vulnerability assessments for clients. It gives a lot of information about the system/application after performing scans. The number of false positives is also less compared to other vulnerability scanners.
  • The professional edition is very useful as policy templates available in this edition are very handy and useful even to perform compliance scan like PCI DSS scan.
  • Also, the ability to export the scan results into reports in formats like HTML, PDF is very useful which could be for performing system/application reviews.
Read full review
ScreenShots

Sensagraph Screenshots

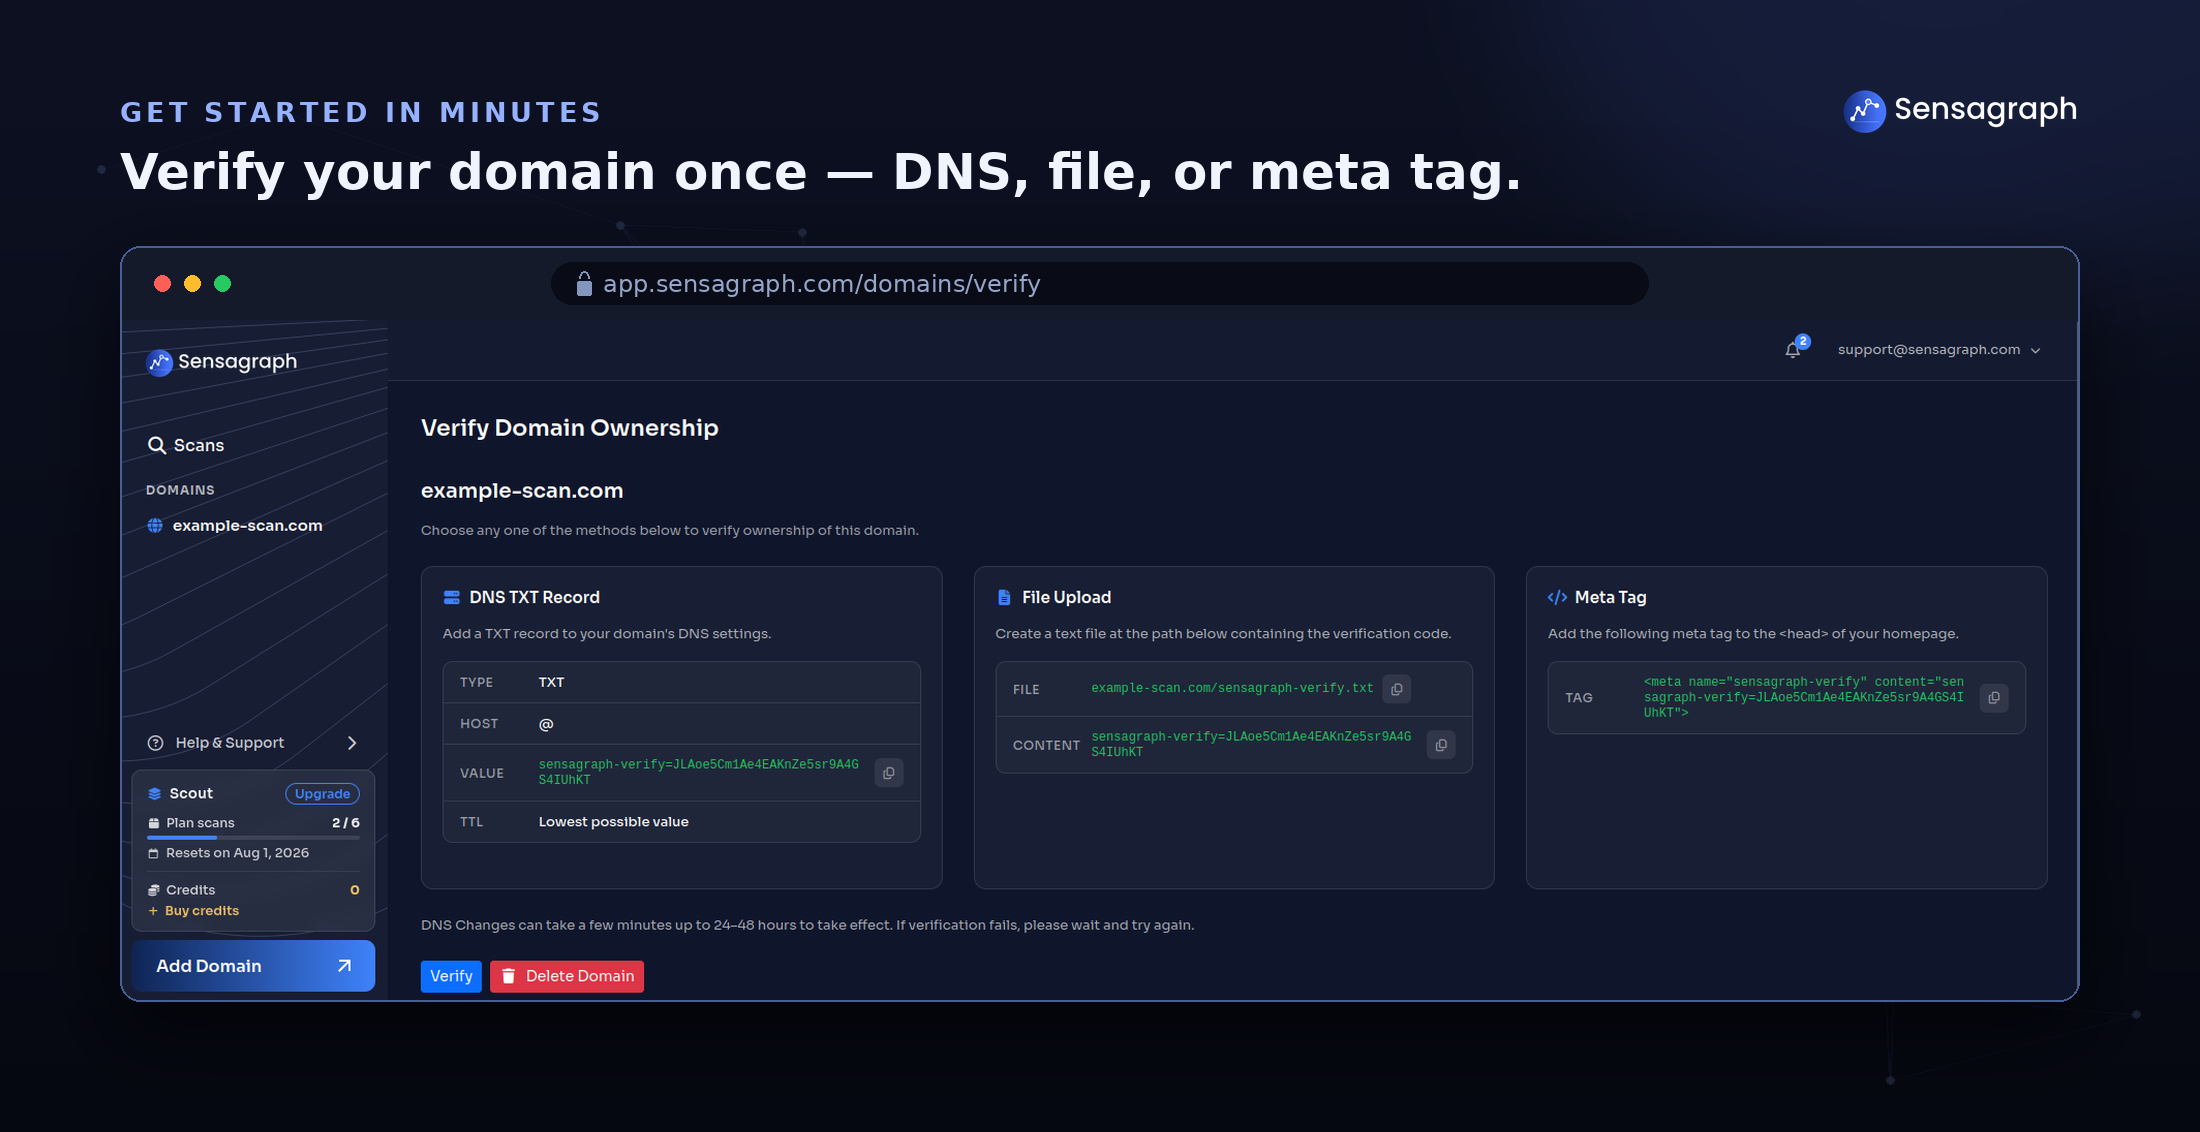
Screenshot of Scan Result ScreenScreenshot of Domain Verification Screen