Adlumin is a security operations command center that simplifies complexity and keeps organizations of all sizes secure. Its technology and integrations create a platform that obtains security telemetry from across an organization to provide greater insights into security alerts and streamline workflows.
N/A
AgileBlue
Score8.4 out of 10
N/A
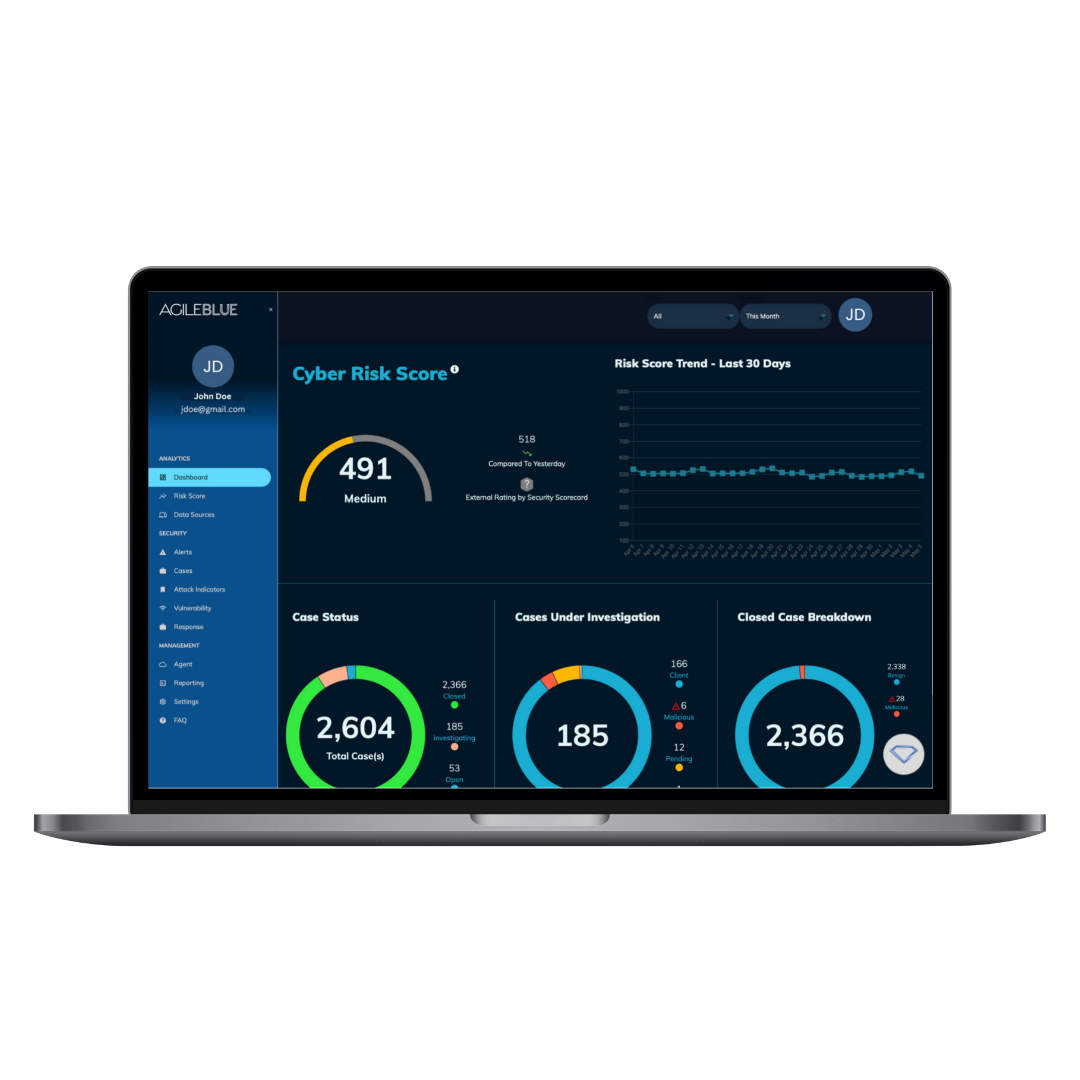
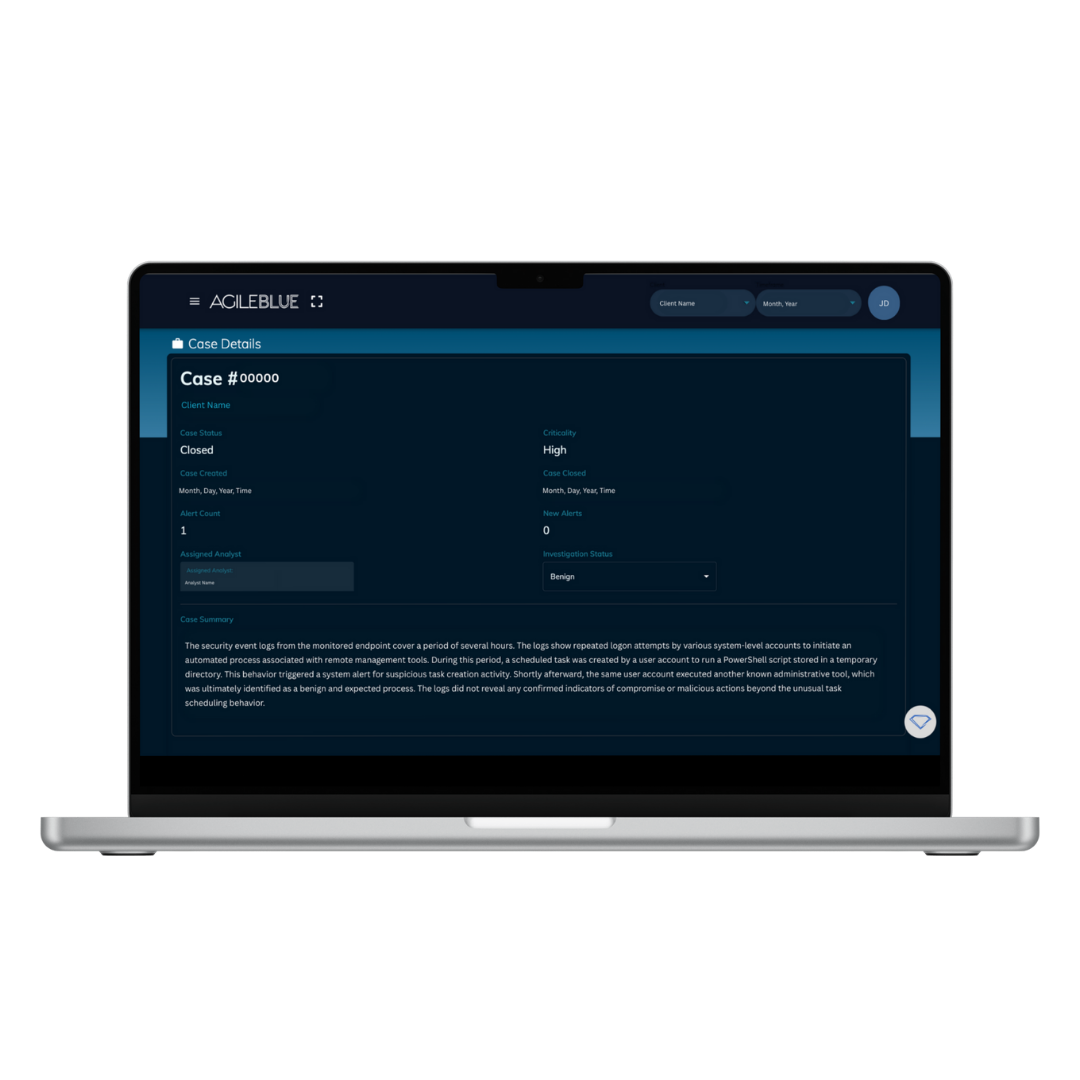
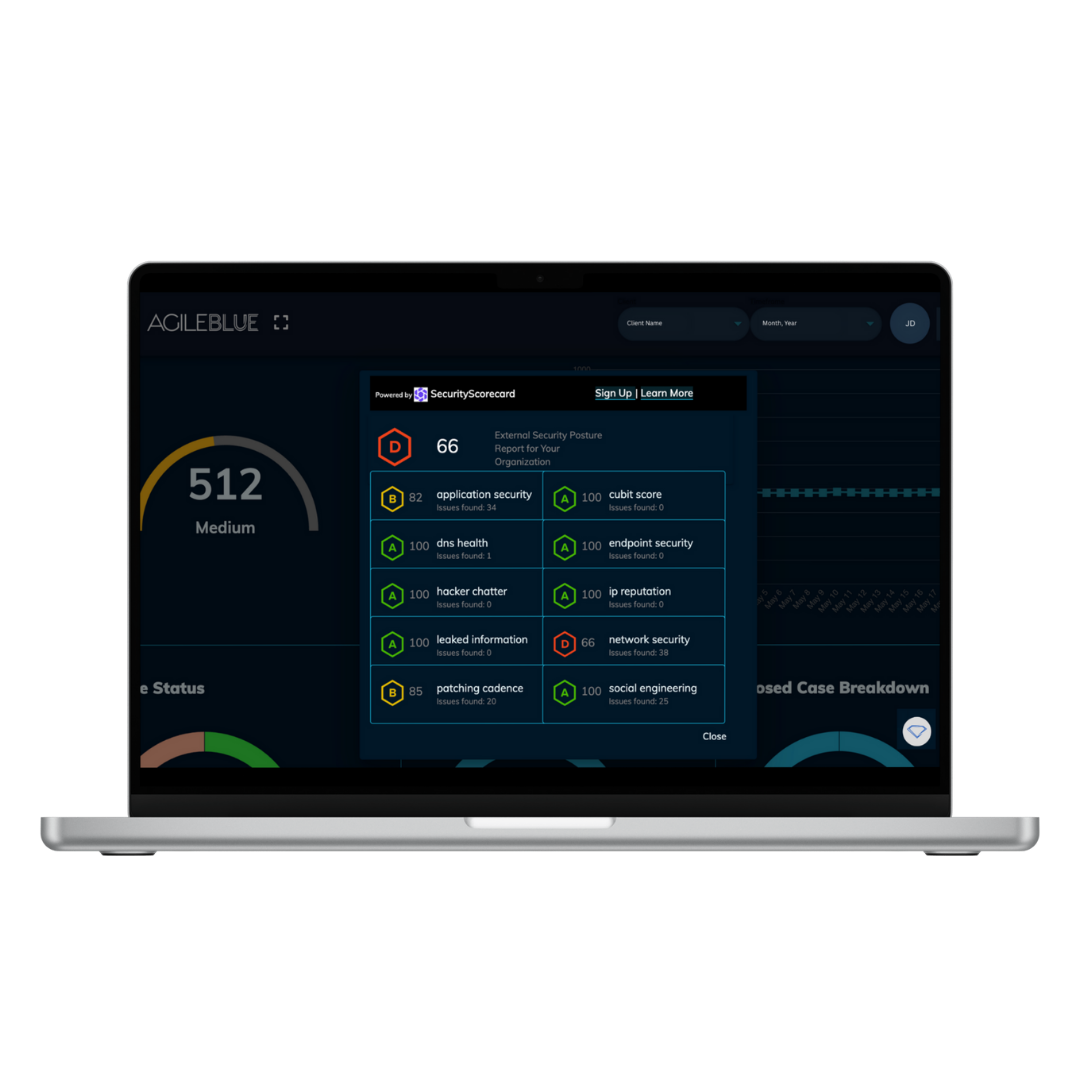
AgileBlue's SecOps platform autonomously detects, investigates, and responds to cyber threats across endpoints, cloud, and network. AgileBlue is offered for the mid market, and for these companies is designed to deliver all-in-one protection, integration, and a partnership so organizations can move from reactive defense to proactive resilience.
If you don't already have a system in place for anomoly detection, log monitoring, and alerting, you're doing your company a disservice. Whether Adlumin is the best choice for you depends on your budget and technology stack, but overall, Adlumin has been one of the best security purchases made by our company in the last few years, and has paid for itself by automatically preventing and protecting against specific attacks that were non-attacks due to Adlumin stopping them before they could start.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
AgileBlue provides good service with L1/L2 support, maintains a good service level with KPIs, and provides a Technical Account Manager to support day-to-day activities. AgileBlue can improve its Threat Intelligence process to better align with specific market requirements, source collection, scale reporting, and cover a larger attack surface.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
They are extremely quick identifying any potentially unusual activity
They make it easy for us to ensure that our employees can log in from other countries without triggering suspicious activity lock-outs when they travel.
Our quarterly meet-ups are a great way to keep my team up to date in the current cloud security scene, as well as to make sure we're doing everything we can to keep our users safe.
After an alert has been "Cleared" by internal IT, there should be no further action taken by the SOC team or the AI agent.
When there is an active internal incident or problem with Adlumin, there should be a notice in the incident or on the platform's active issues board about issues that may affect Adlumin agents. This would save people who have to respond a lot of time.
Have not been able to get one forwarder to function properly, despite documentation from a technician and the platform documentation. This is frustrating when a Windows collector option is available but doesn't work at all.
I have noticed some SentinelOne detections do not warrant responses or actions from the Adlumin team. These are usually repeated flags that do not require action, but some do, and some do not. I can't figure out what we reference specifically to determine a response from SOC or AI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A number of integrations were simple to set up and well documented, but a few things were difficult or undocumented yet. Some sections feel over-complicated and others feel way too vague during the setup process. Once the onboarding is finished though, the product is very simple, but there is a learning curve at the beginning.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We were able to get up and running in a day with very minimal onboarding. AgileBlue has great documentation as well as an onboarding team if you need it but in our experience we were able to get moving quickly. The support team and account managers are also very responsive and provide great response times.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
ArcticWolf has been a great product that we have used, but the ability that Adlumin has is extremely comparable for a fraction of the price. There are no hardware requirements with Adlumin, but it still has all of the abilities as ArcticWolf without the overheard. Again, the SOAR actions are a game changer when it comes to automation and immediate action.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
AgileBlue integrates as a partner to SentinelOne - allowing out MSSP to have insights into both platforms. Using AgileBlue as an escalation management tool allows false positive results to get handled quickly, low severity alerts to be dealt with before escalations, and high severity alerts to get forwarded to the appropriate members of higher-level triage teams
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We used to be with an MSP before I was hired, and the company spent over 20K per year for that service. With N-Able, we have reduced the cost by over half.
I spend minimal time now patching computers because this is all automated. I sometimes have to patch a couple of machines because I missed a patch, but it has saved me a great deal of time.
I save a great deal of time with Board Reports because they are automatically generated for me each month.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AgileBlue as drastically reduced the amount of time I had to spend monitoring the security aspect of our 365/Azure environment, freeing me up to spend a lot more time helping our users. That alone has made the switch worth it.
The reduction in accidental Microsoft account lockouts our users have had to endure is also a big win and definitely helps keep productivity up.