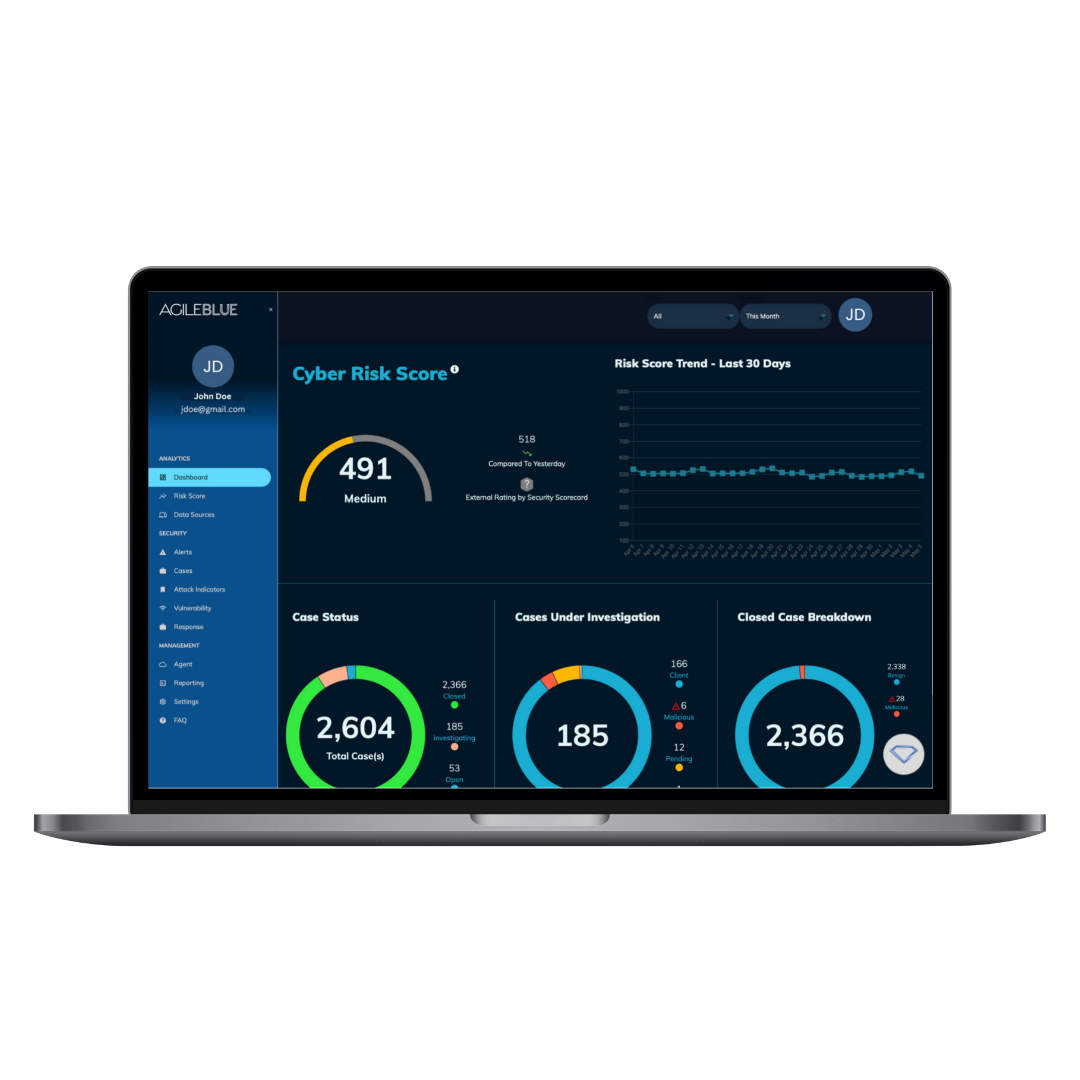
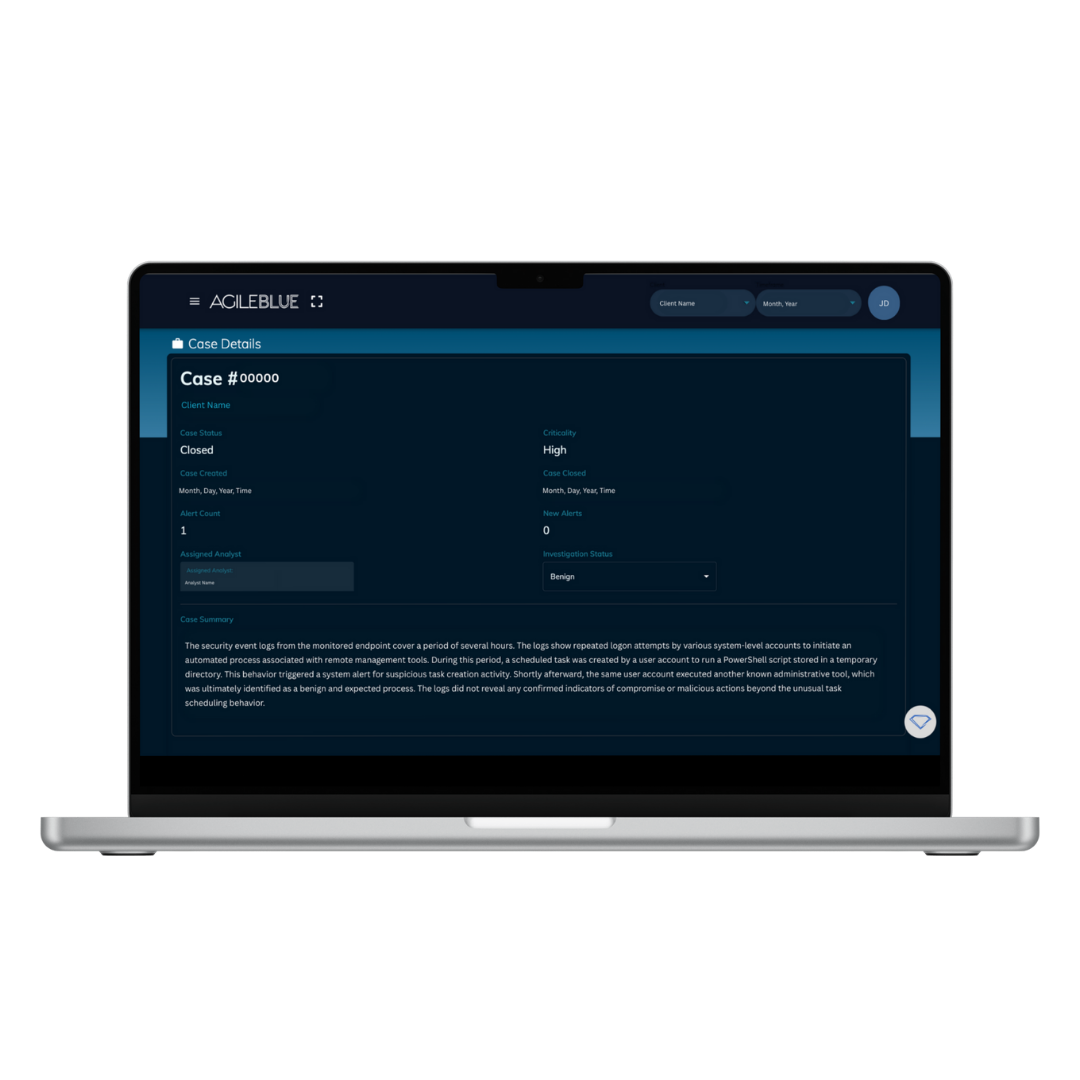
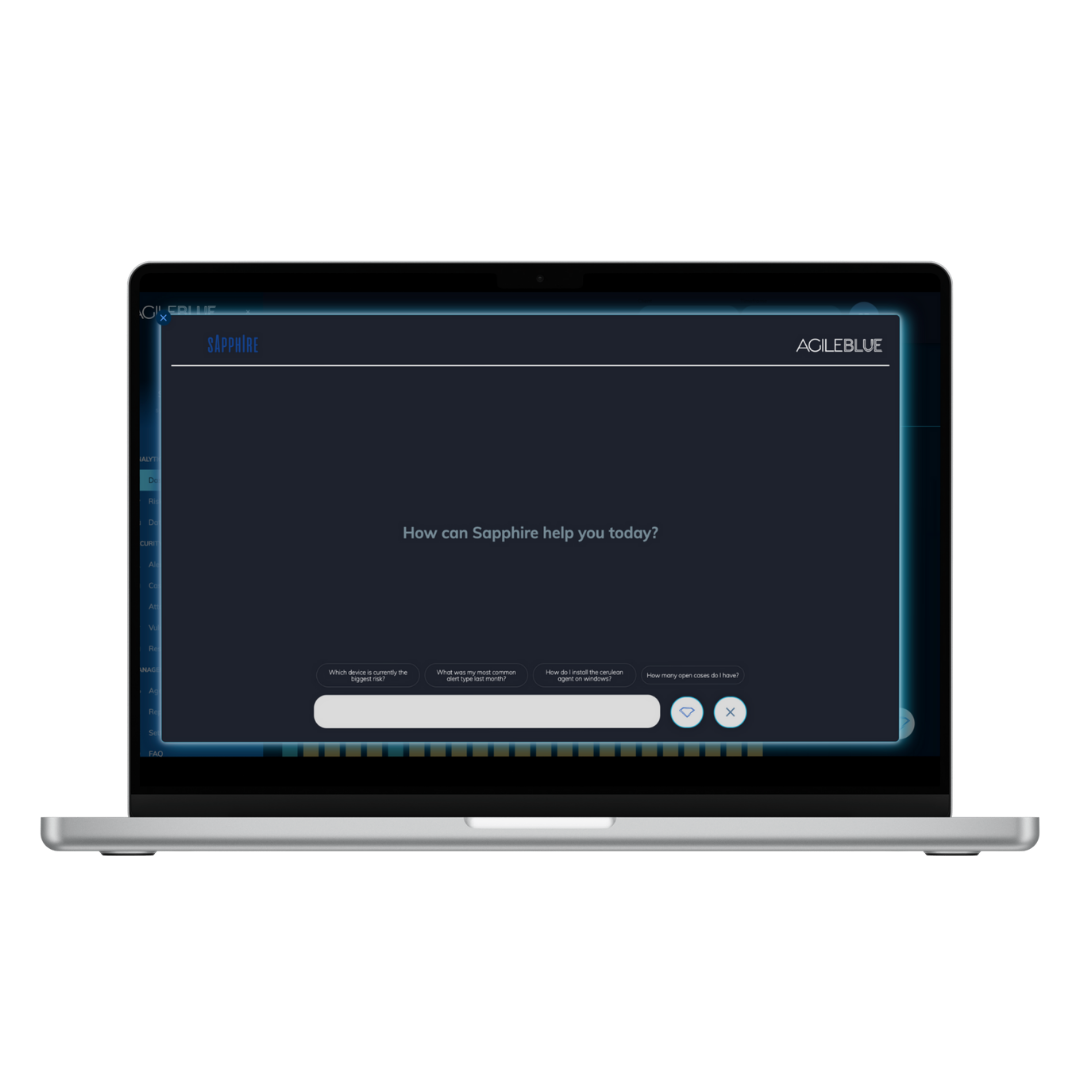
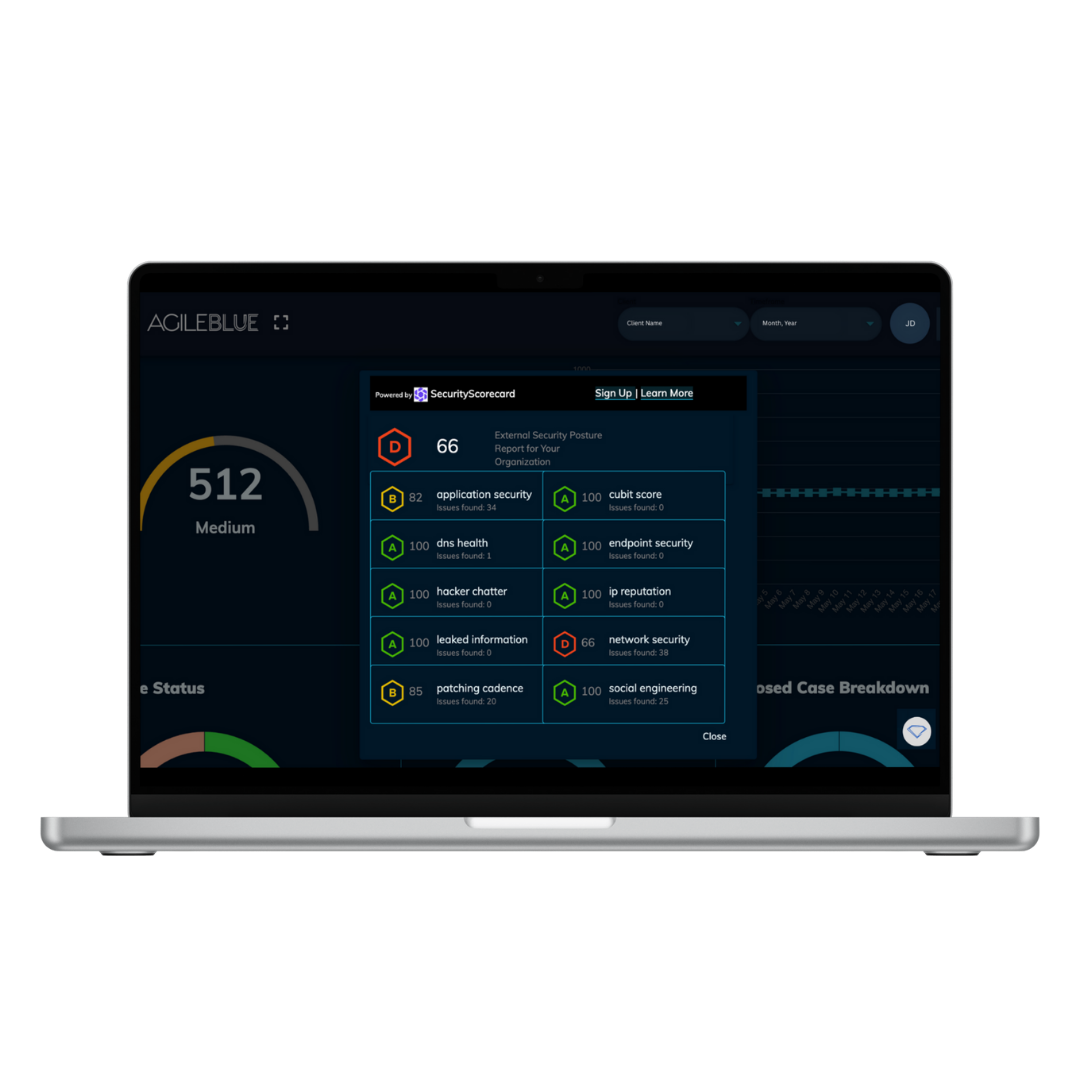
AgileBlue's SecOps platform autonomously detects, investigates, and responds to cyber threats across endpoints, cloud, and network. AgileBlue is offered for the mid market, and for these companies is designed to deliver all-in-one protection, integration, and a partnership so organizations can move from reactive defense to proactive resilience.
N/A
Alert Logic
Score9 out of 10
N/A
Alert Logic delivers managed detection and response (MDR) with comprehensive coverage for public clouds, SaaS, on-premises, and hybrid environments. Alert Logic is a LevelBlue solution since the January 2026 acquisition.
AgileBlue provides good service with L1/L2 support, maintains a good service level with KPIs, and provides a Technical Account Manager to support day-to-day activities. AgileBlue can improve its Threat Intelligence process to better align with specific market requirements, source collection, scale reporting, and cover a larger attack surface.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
This is pretty good AV product - lightweight, easy to install, and easy on system resources. It will take some getting used to on the end user side, it doesn't scan in a traditional way, and it does not have a taskbar icon so it hard to know if it's working or installed. My only complaint would be the false positives which I know every AV system has, but the problem with Barkly is that it alerts the users with a message (which they freak out about) and it alerts IT with an email. Again, not a major issue, but it can be annoying until it is overridden. The override process is super easy though, so its again, not a big deal.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
They are extremely quick identifying any potentially unusual activity
They make it easy for us to ensure that our employees can log in from other countries without triggering suspicious activity lock-outs when they travel.
Our quarterly meet-ups are a great way to keep my team up to date in the current cloud security scene, as well as to make sure we're doing everything we can to keep our users safe.
Customer Service. Usually, I'd put the technical details up front, and they're good with that too. But the service from pre-sales all the way through onboarding and continued account management is top tier. Our onboarding schedule got messed up, partly because of us, but that was rather minor. I always get prompt replies to any tickets, and they've even reached out to discuss my feature requests. When it comes to security, it's critical to have a responsive team, and they've got it.
Detection seems good. It's hard to quantify exactly, but it seems that they always detect the bad actors. And when we get an alert, they include a bunch of details so we know what kind of scan they're trying to do, how far they got, etc. You can't prevent everyone from doing a scan on your IP, but it gives you a really good idea of where your soft spots might be. And if you're getting those low-level alerts, it's a reminder that it's there and working if you have a major event too.
Very easy setup. This goes back to their customer support to some extent, as they walk you through all the steps required. But it's also about their technical solution, it's not so overly complex that it's fragile, nor does it take a great deal of time to deploy. And it's been zero effort to maintain since then.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
While most of the features are very easy to use, some of the rules are a little difficult to create if you are not in the platform all the time. However, the support team is always there to assist with things you may struggle with!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AgileBlue integrates as a partner to SentinelOne - allowing out MSSP to have insights into both platforms. Using AgileBlue as an escalation management tool allows false positive results to get handled quickly, low severity alerts to be dealt with before escalations, and high severity alerts to get forwarded to the appropriate members of higher-level triage teams
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I was using Alert Logic Insight for myself to improve my skills and ability to it. My organization was not happy using our previous website security program so I recommended for them to use this software. It has been more than 1 year and still, they are using this program without having any problem so far.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info