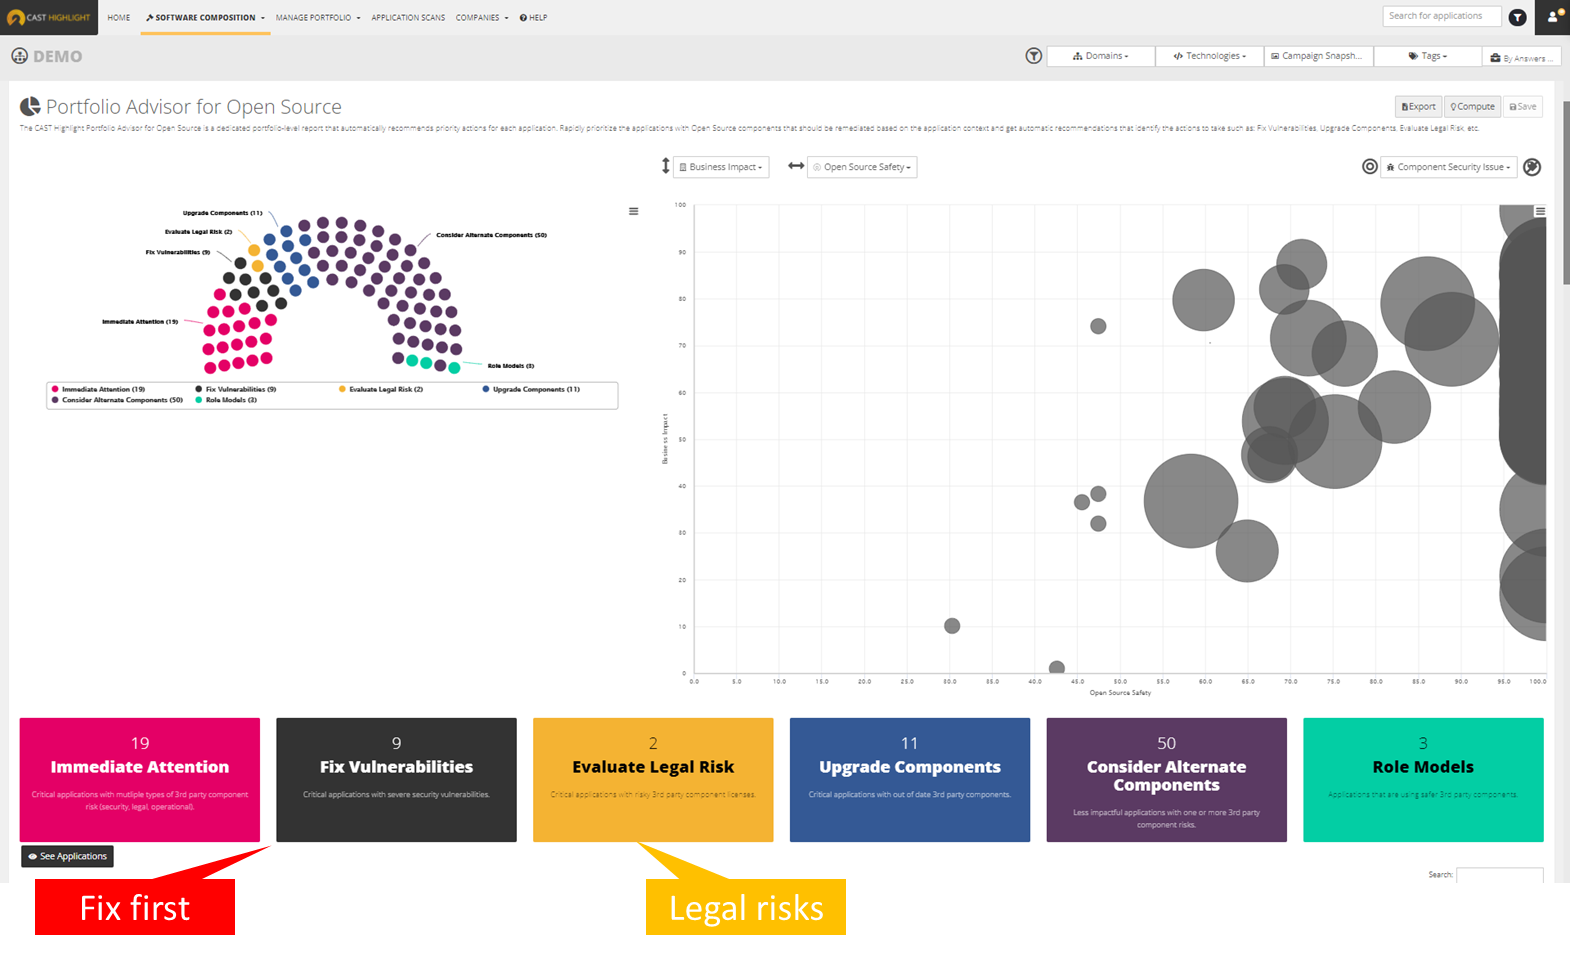
CAST headquartered in New York offers Highlight, an application portfolio management solution providing software component analysis , application security, application benchmarking, and technical due diligence.
$25,000
per year
Fortify by OpenText
Score9 out of 10
N/A
An AppSec solution formerly from Micro Focus, spanning SCA, SAST and DAST that supports the breadth and management of any application portfolio, used to secure code. Features API discovery and testing for any application, throughout the software lifecycle.
N/A
Snyk
Score8.6 out of 10
N/A
Snyk’s Developer Security Platform automatically integrates with a developer’s workflow and helps security teams to collaborate with their development teams. It boasts a developer-first approach that ensures organizations can secure all of the critical components of their applications from code to cloud, driving developer productivity, revenue growth, customer satisfaction, cost savings and an improved security posture. The vendor states Snyk is used by 1,200 customers worldwide today, including…
$0
Pricing
CAST Highlight
Fortify by OpenText
Snyk
Editions & Modules
Cloud
25k
Portfolio Size 25
SCA
$26k
Portfolio Size 25
Complete
33k
Portfolio Size 25
No answers on this topic
Free
$0
Team (Snyk Open Source or Snyk Container or Snyk Infrastructure as Code)
$23
per month per user
Business (Snyk Open Source or Snyk Container or Snyk Infrastructure as Code)
$42
per month per user
Team (Snyk Open Source + Snyk Container + Snyk Code + Snyk Infrastructure as Code)
$98
per month per user
Business (Snyk Open Source + Snyk Container + Snyk Code + Snyk Infrastructure as Code)
$178
per month per user
Enterprise
Contact Sales
Offerings
Pricing Offerings
CAST Highlight
Fortify by OpenText
Snyk
Free Trial
Yes
No
Yes
Free/Freemium Version
No
No
Yes
Premium Consulting/Integration Services
Yes
No
No
Entry-level Setup Fee
Optional
No setup fee
No setup fee
Additional Details
Annual Pricing by Size of Application Portfolio
—
Pricing is dependent on the number of developers selected, the number of products selected, and the payment term selected. Please visit the Snyk plans page for an interactive pricing calculator.
I think CAST is a great tool to give insight into your applications. The tool can be met with resistance from team members as the tool is going to expose defects that should be addressed. Out of the box, it may need some tailoring to focus on certain areas so that you are not overwhelmed with defects the first time you scan your code. But ultimately, you will want to eliminate all defects in the code and have all violations turned on.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is best suited for runtime application security scanning and very useful for automation. You can seemlessly integrate with pipeline for dynamic scans. Cloud based apps can also be scanned for vulnerabilities, cross site scripting attacks. Basically all OWASP TOP 10. It is less appropriate to use if you have serverless architecture
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Scenarios Where Snyk Is Well-Suited CI/CD Pipeline Integration (Node.js, Python, etc.) Container Security Open Source License Compliance Infrastructure as Code (IaC) SecurityScenarios Where Snyk May Be Less Appropriate Scanning Proprietary or Custom Code for Unknown Vulnerabilities Complex Monorepos with Custom Build Tools Organizations Requiring Custom Security Rules Advanced Security Teams Needing Correlation and Deep Triage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The tool itself has many capabilities but using them operationally within the platform on a day to day basis for managing vulnerabilities is not a good experience.
Our company was in desparate need of a tool to help us manage vulnerabilities so we could achieve a SOC 2 assurance report without findings.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Since every firm needs to perform static code analysis on their applications, I believe Micro Focus Fortify WebInspect would work well for them (they also offer dynamic scanning, although I haven't used it myself). Different static analysis tools scan code in different ways, and Micro Focus Fortify WebInspect asks you to submit a complete build of the application along with debugging files. Depending on how your company builds its apps, this requirement may be simple or challenging.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a cloud-based platform which can provide us a very useful and unique features like Application Assessment, Scans, Vulnerability Test, Comprehensive Reporting, Monitoring, etc. Fortify by Open Text is also outstanding in various parameters for the support and integration and it is highly adaptable in various DevOps Program where you need secure app testing with all given features.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Developer-Centric Design - Snyk integrates directly into IDEs (like VS Code and IntelliJ), CI/CD pipelines, GitHub/GitLab, and container registries. Clear, Actionable Vulnerability report issues are categorized by severity.
Reports include fix recommendations, pull request suggestions, and links to remediation advice.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
These other tools only do a part of what CAST does. CAST gives a comprehensive view into the code looking at all aspects, code quality, security, maintainability, vulnerability, privacy, reuse, etc. These other tools only focus on one or two dimensions.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Fortify Application Defender is a little more timely and upfront with a lot of their information on cyber security. we like what they provide and how they communicate with our users. I think they have a good understanding and practice in their field. they seem best suited for us and the best fit.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Unfortunately, neither cover all of the use cases that we would like so we need to use both but they are both excellent tools as part of our vulnerability management. We find that Snyk helps us better with improving our MTTR of identified vulnerabilities when compared to inspector but that may be more based on how we have implemented both tools
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe once we had the tool working for our code base, we immediately saw positive ROI.
We spent some time getting to where our code code be scanned efficiently but some of that was trying to do things ourselves instead of fully utilizing Cast Professional Services. I highly recommend to do an engagement with CAST to have them help setup the tool in your environment or to run it in the cloud for you.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info