Check Point Harmony SASE, based on Perimeter 81 which was acquired by Check Point in late 2023, is designed to simplify secure network, cloud and application access for the modern and distributed workforce.
$10
per month per user
SonarQube
Score8.7 out of 10
N/A
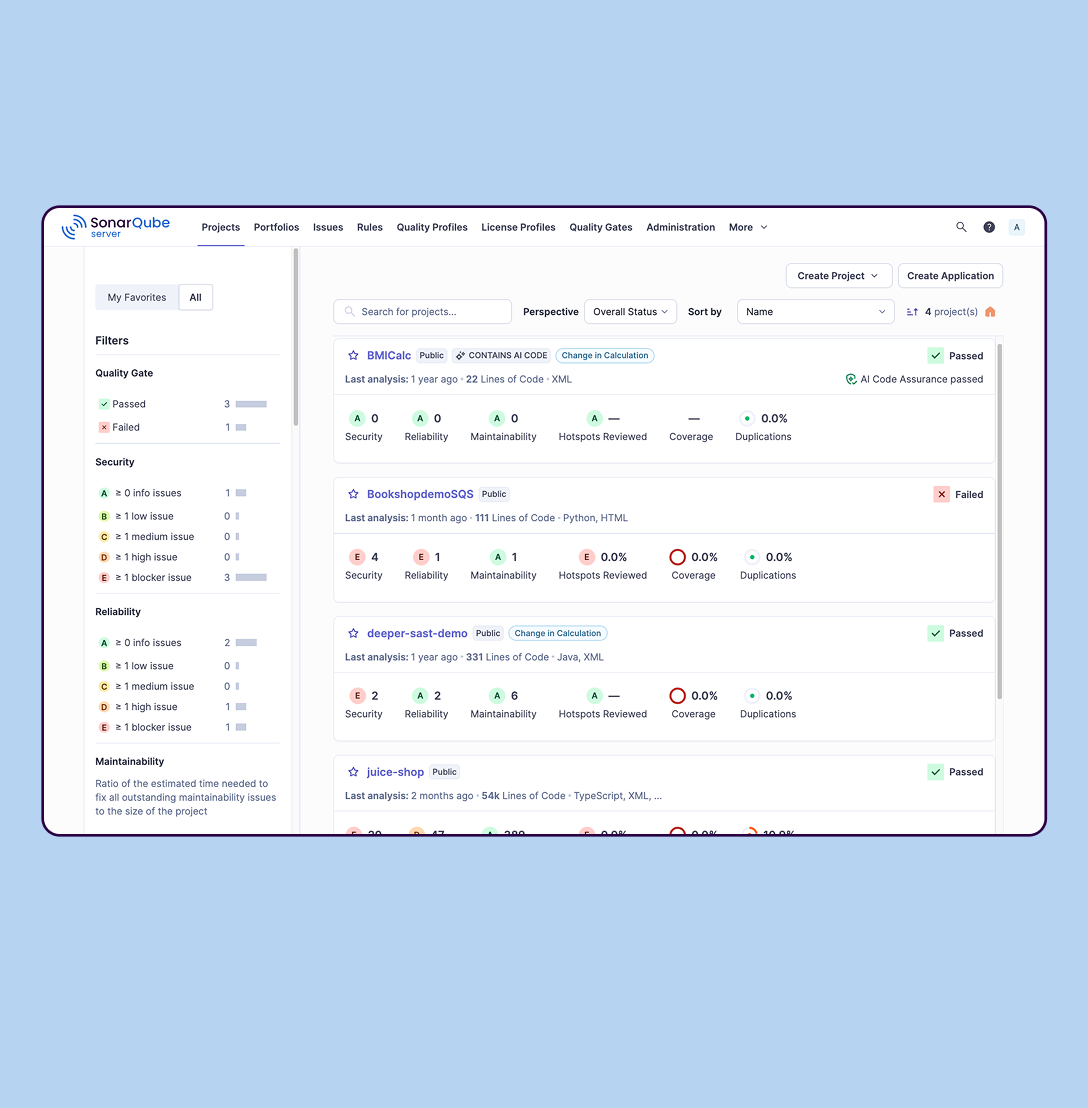
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
$34
per month Recommended for teams <50 developers
Pricing
Harmony SASE
SonarQube
Editions & Modules
Essentials
$10
per month per user
Premium
$15
per month per user
Premium Plus
$20
per month per user
Enterprise
Custom
SonarQube Community Build
$0
(open source)
Self-managed: Developer
Starting at $720 annually
per year per installation
Self-managed: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Teams
Starting at $34 per month
per month per installation
Self-managed: Data Center
Contact sales for pricing
per year per installation
Offerings
Pricing Offerings
Harmony SASE
SonarQube
Free Trial
No
Yes
Free/Freemium Version
No
Yes
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
+$50 per month per gateway. Discounts available for annual pricing.
We have found that when thoughtfully implemented, Check Point Harmony SASE can be well suited for almost any customer. Smaller customers may not need all the functions of SASE, but they all need a reliable VPN solution when traveling. The platform can be configured for individual tenants, allowing the solution to scale with the client as they grow. As the customer grows, they are already familiar with the agent, so scaling up has less user pushback.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
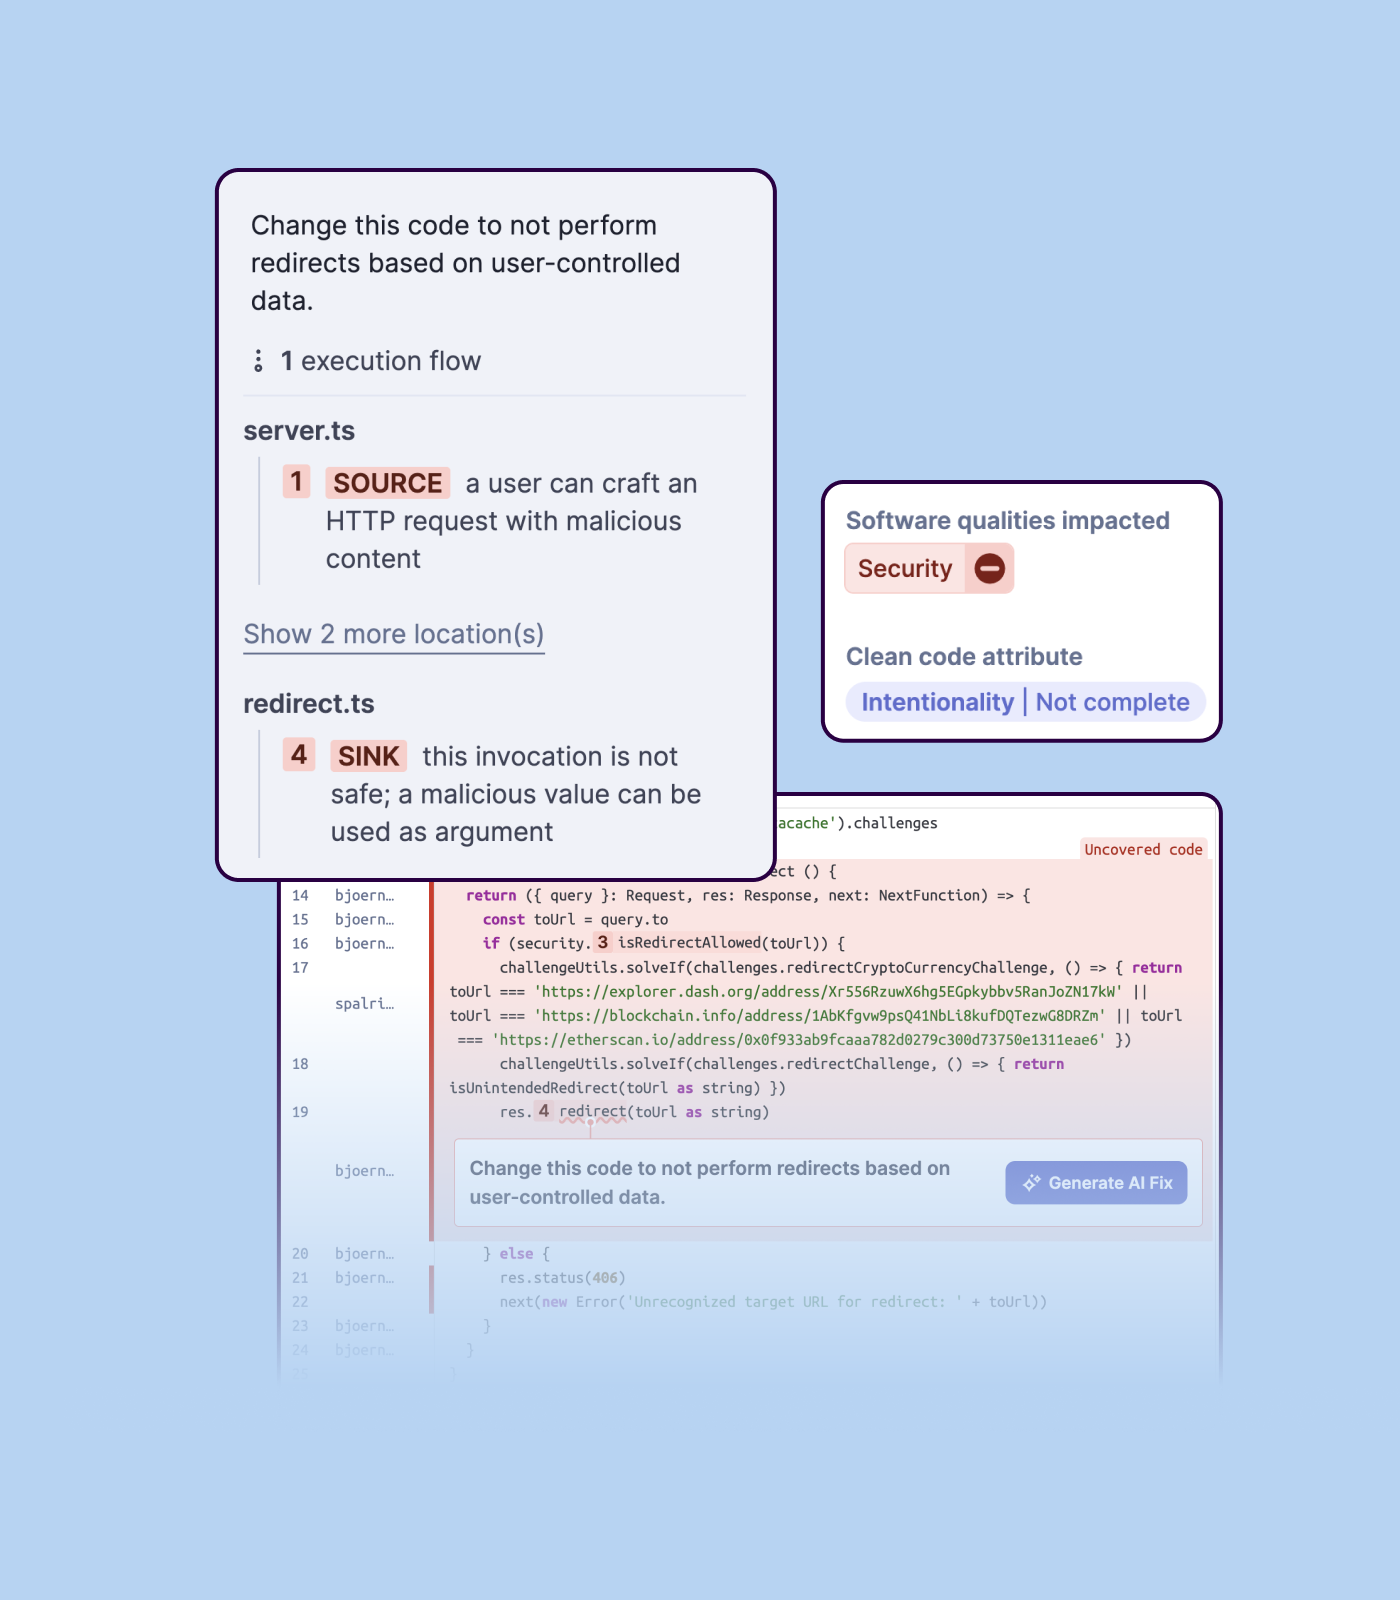
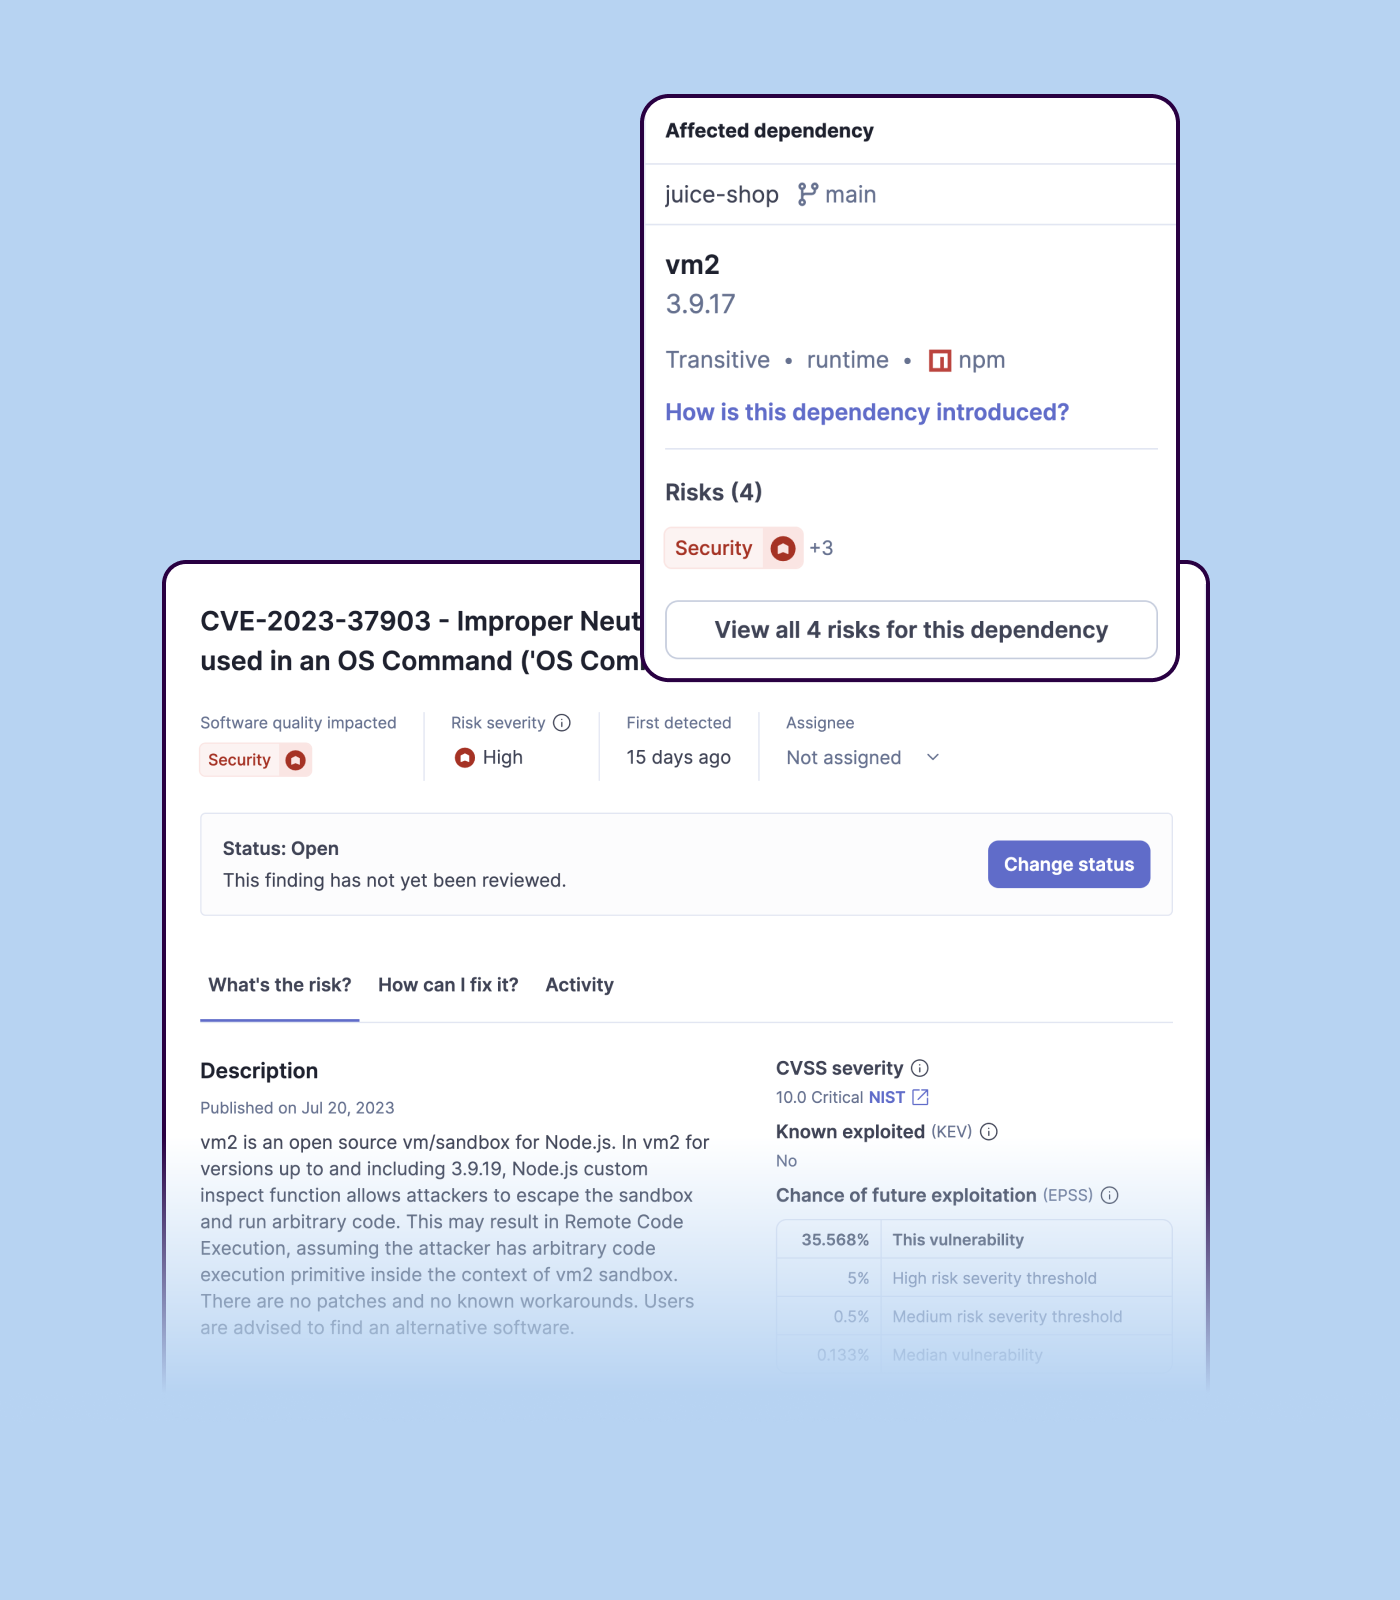
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Harmony SASE can use some improvement in reporting. While general reports are available in the dashboard, it lacks additional details and flexibility to capture insights on user adoption, bandwidth utilization, etc.
The app lacks visibility into failures, errors, and network diagnostics, which would allow IT and network professionals to conduct their own investigation and troubleshooting. While their support has a good grasp of this, having these capabilities will allow organizations to take action on their own rather than waiting for support during issues and outages.
Expanding the platform's global presence, like adding gateways in different countries, is not a use case for us right now. They have a presence in most geographic locations we need, but I can imagine bigger companies needing other locations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Overall, the product is easy to use, reliable, and can be automated to minimize user input. Occasionally, an agent update will clear the workspace and sign the user out. When this occurs, a member of our helpdesk team is needed to assist the user in signing back in. This is our biggest reason for giving it a 9 out of 10.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
In the beginning, it was a bit rough getting it to work and getting any kind of quality support from customer service. But recently they really improved their service and customer service. I believe they raise 100M in new funding which provides them the resources to make a better product with better tools and a better help desk.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One of the biggest benefits of switching to Check Point Harmony SASE was the pricing model. Our previous VPN solution is usage-based and billed on the amount of network traffic, while Harmony SASE has a per-user license.
We also benefited from simplified network architecture. Check Point Harmony SASE takes care of everything; we just need to select a location. Previously, we had to design and architect our VPN infrastructure, a task that required technical expertise.
Our organization leverages Harmony SASE's VPN solution allows us to meet our client-specific requirements. It enables remote work and removes the requirement for a physical office.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)