Check Point Software Technologies provides threat intelligence via the Check Point ThreatCloud.
N/A
IntSights Cyber Intelligence, from Rapid7
Score7.7 out of 10
Enterprise companies (1,001+ employees)
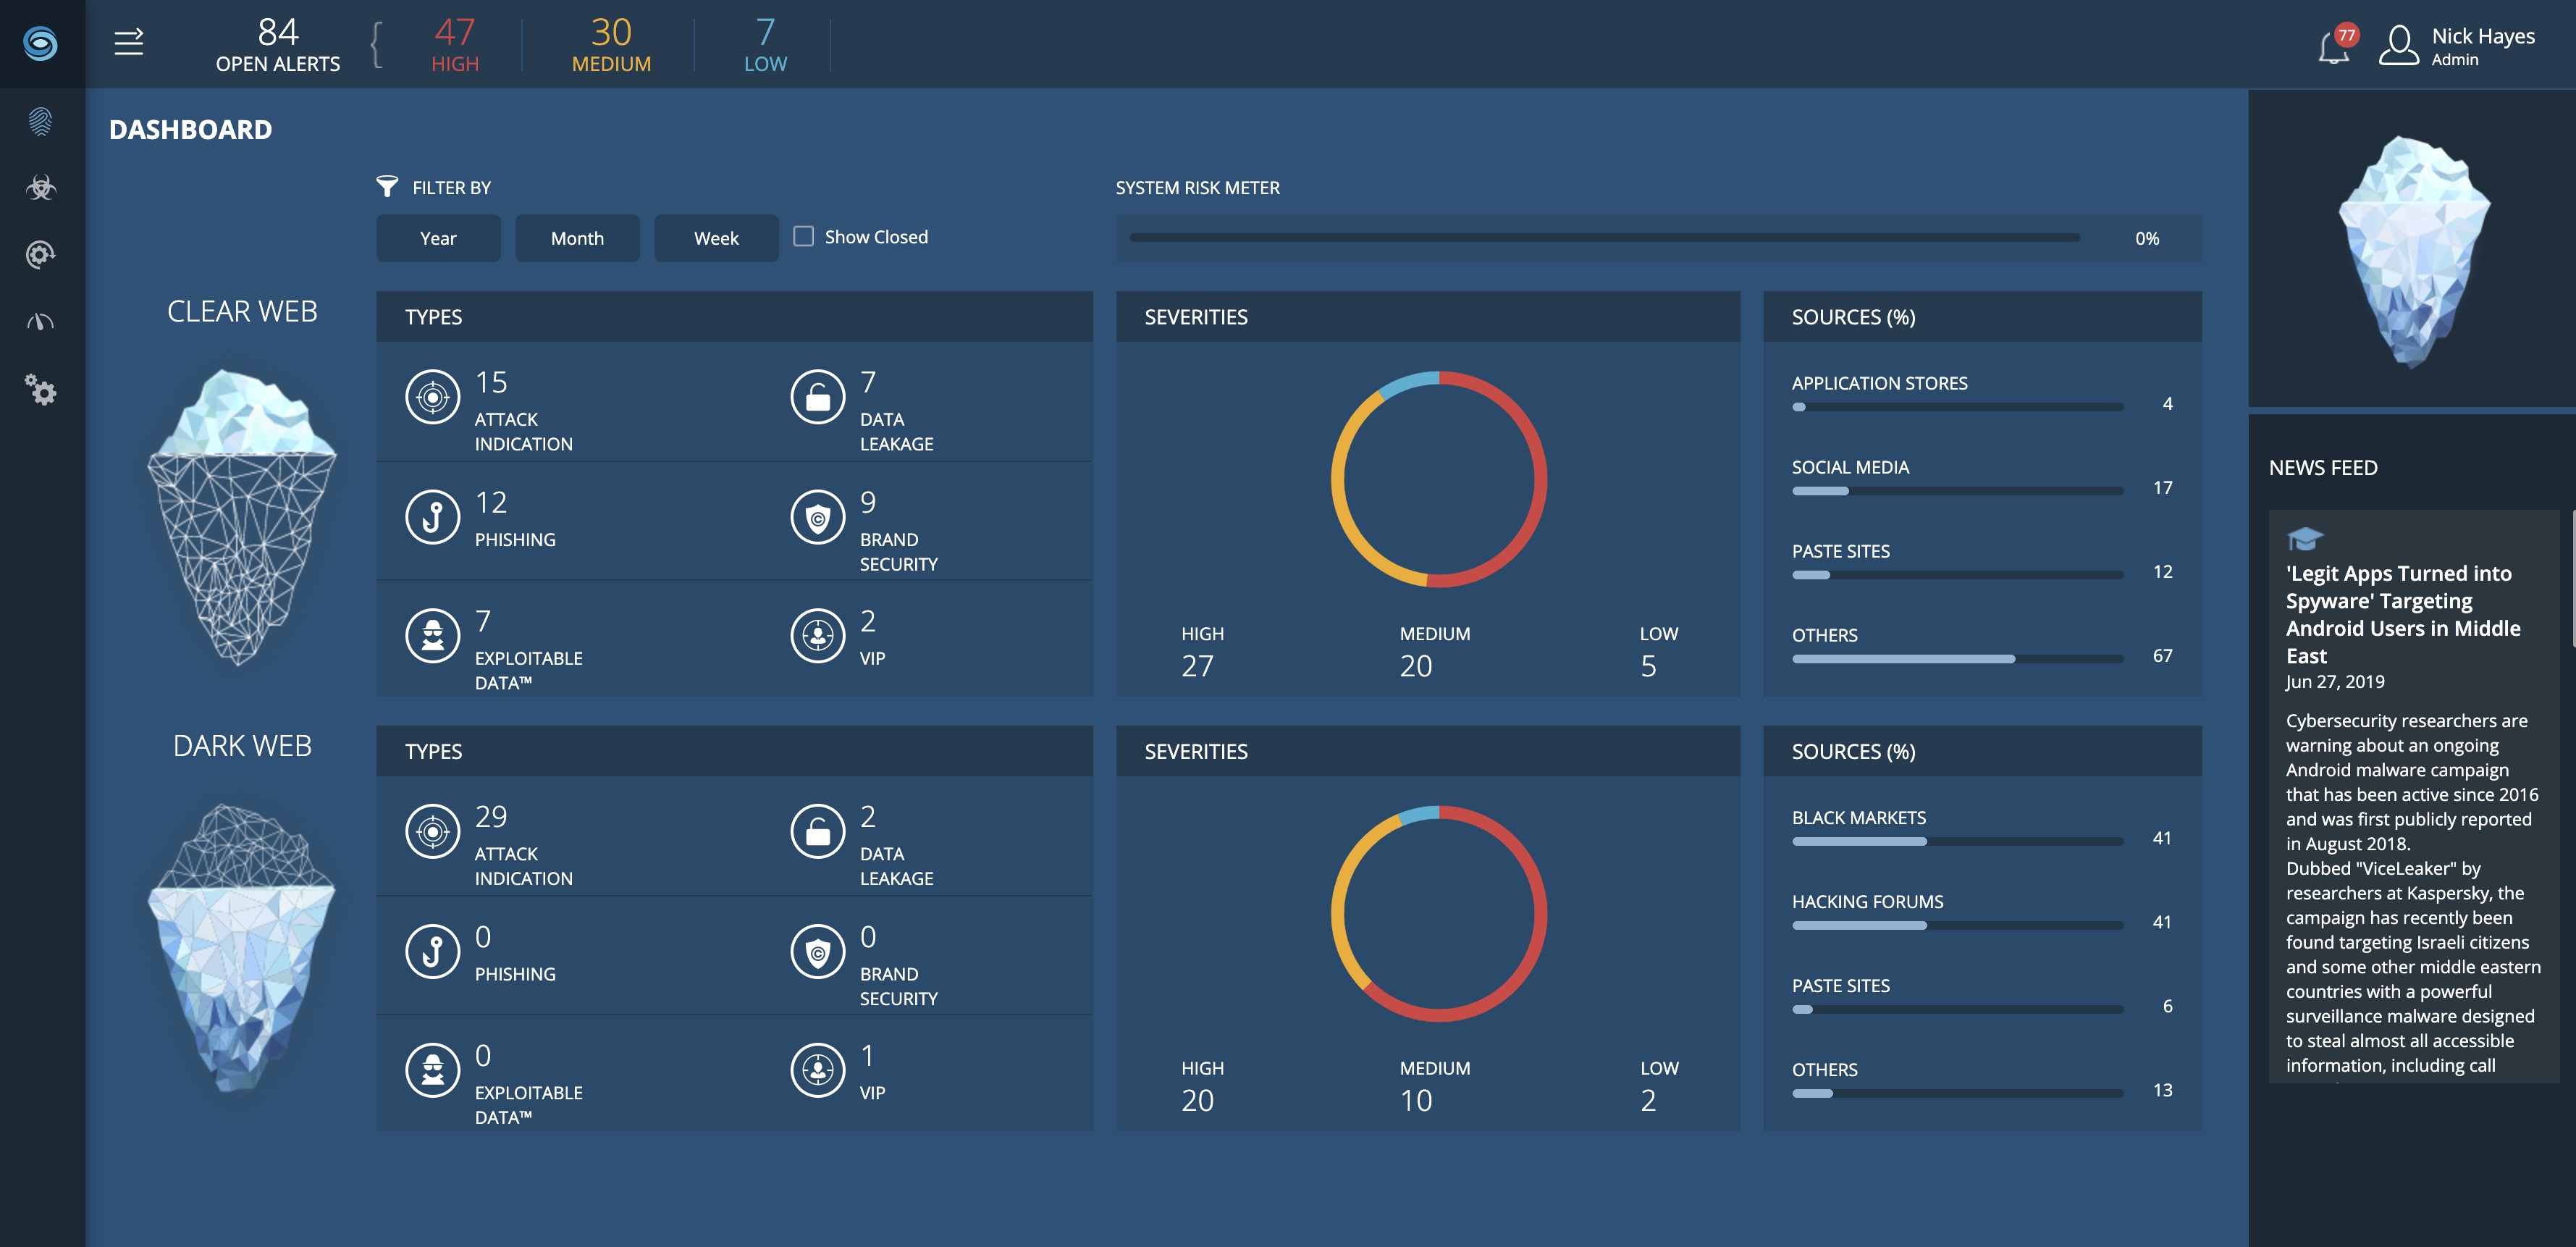
IntSights is an all-in-one external threat intelligence and protection platform, purpose-built to neutralize threats outside the wire. According to the vendor, it is the only solution of its kind. IntSights solution suite's goal is to equip cybersecurity teams worldwide to more effectively detect, assess, and mitigate threats externally from the source, well-before before they reach the perimeter. IntSights four core offerings are: Threat Command™ Threat Intelligence…
If you have the Check Point environment and want to utilize the Checkpoint environment, you should use the [Check Point] ThreatCloud. Without [Check Point] ThreatCloud, there’s no way to stop the 0days or APTs. However, [Check Point] ThreatCloud relies on the Checkpoint infrastructure to be used and integrated. If you have other firewall and/or endpoint vendors, [Check Point] ThreatCloud is not the best service to be used. Checkpoint also offers 24x7 threat cloud-managed security services to [...] organizations. Threat cloud-managed security services leverage the threat cloud decreasing the detection time and false-positive rates via increasing protection rates.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It has been a brilliant tool and we have harnessed it for so many applications - Threat intelligence, Risk Analysis, Automation, Endpoint protection, Vulnerability Management, Application Security, Protecting all our Cloud Applications. We love the fact that we only have to see those threats that are meaningful to us. We don't need clutter and endless dashboards with information that just gets in the way and makes things complicated. By having this full, crisp, easily discernible visibility, our decision-making is enhanced and we can see clearly what's happening in real time. We also love the fact that if a dashboard isn't proving to be productive, then we can go ahead and scrap it, and create another one. The tailor made/bespoke aspect of the Application is the thing that really sets it apart. By having all our dashboards aligned, our teams are all working from the same page and it means we are safe in the knowledge that our systems and applications are being monitored in the most effective and efficient ways. There haven't been any real scenarios where it has been ineffective. - perhaps just In-depth Risk Vulnerability Analytics are a bit lacking. However, I'm probably just picking hairs there.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As Checkpoint next generation firewalls were already implemented in the network, ThreatCloud was easy to implement and had better features and reputation than competitors
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IntSights Cyber Intelligence, from Rapid7 was by far the clear winner, in terms of seamless integration with our exisitng systems, deployment, cleaner User Interface, ease of operation, better for monitoring Indicators of compromise and dark web information, having more features etc.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
High score rates [are] seen on breach systems after deploying systems integrated with [Check Point] ThreatCloud
Catch rates are very high compared to other vendors
One missing thing is the detection for localized URLs and IPs
Purchasing within the 3-year perspective is cheap compared to other solutions; ROI is generally six months
[Check Point] ThreatCloud eliminates the need [for] other additional services that may need to be deployed like dedicated IPS, Dedicated Sandbox, DNS solution, etc.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info