Checkmarx, an Israeli headquartered company with US offices, provides a suite of application security software delivered via the Checkmarx Software Security Platform. Individual modules and capabilities include Checkmarx Static Application Security Testing, Checkmarx Software Composition Analysis, Checkmarx Interactive Application Security Testing (CxIAST)
N/A
Fortify by OpenText
Score9 out of 10
N/A
An AppSec solution formerly from Micro Focus, spanning SCA, SAST and DAST that supports the breadth and management of any application portfolio, used to secure code. Features API discovery and testing for any application, throughout the software lifecycle.
N/A
SonarQube
Score8.7 out of 10
N/A
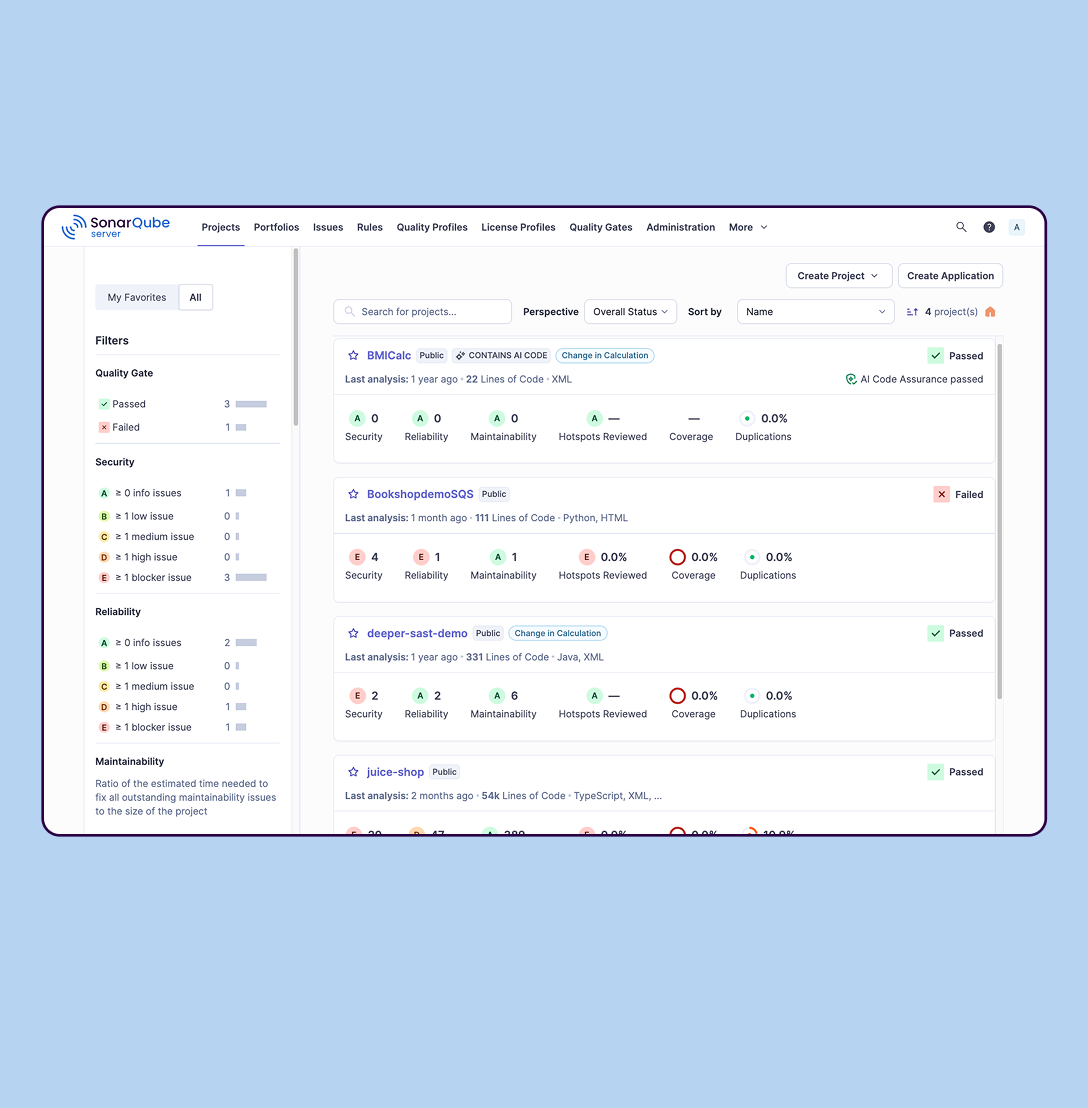
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
$34
per month Recommended for teams <50 developers
Pricing
Checkmarx
Fortify by OpenText
SonarQube
Editions & Modules
No answers on this topic
No answers on this topic
SonarQube Community Build
$0
(open source)
Self-managed: Developer
Starting at $720 annually
per year per installation
Self-managed: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Teams
Starting at $34 per month
per month per installation
Self-managed: Data Center
Contact sales for pricing
per year per installation
Offerings
Pricing Offerings
Checkmarx
Fortify by OpenText
SonarQube
Free Trial
No
No
Yes
Free/Freemium Version
No
No
Yes
Premium Consulting/Integration Services
No
No
No
Entry-level Setup Fee
No setup fee
No setup fee
No setup fee
Additional Details
—
—
—
More Pricing Information
Community Pulse
Checkmarx
Fortify by OpenText
SonarQube
Considered Multiple Products
Checkmarx
No answer on this topic
OpenText
Verified User
Chose Fortify by OpenText
Veracode is the product I've used that is most similar to Fortify WebInspect. They both do a good job at reporting code vulnerabilities and both allow for good automation.
SonarQube can be a free tool, but does a much better job at finding bugs that aren't necessarily …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Fortify by OpenText
Micro Focus Fortify WebInspect is better when it comes to speed, integration and detection capabilities as compared to Insight Appsec. What I loved the most is the broad coverage of vulnerabilities it identified as against Insight Appsec. Apart from detection capabilities the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarSource Sarl
Verified User
Chose SonarQube
Getting SonarQube instead of the other tools we tested was an easy choice. Snyk was way too much limited to only Docker images and dependency analysis at that time. And Checkmarx was very hard to adapt to our needs : configuring custom quality gates was way too much of a …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose SonarQube
Some are still under consideration. Pricing is a big component. Some FOSS products have been considered is at par (at least for our needs) or catching up. Although the amazing support in the community weighs hard on the value. So, if it went away...so would some arguments …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
If you are going with SAST process or want to improve overall security posture then go for it like integrating it with post deployment steps. If you are more concerned about proactive controls better choose other options such as pee-commit hooks and CI security. Also choose other tools for DAST and API scans.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is best suited for runtime application security scanning and very useful for automation. You can seemlessly integrate with pipeline for dynamic scans. Cloud based apps can also be scanned for vulnerabilities, cross site scripting attacks. Basically all OWASP TOP 10. It is less appropriate to use if you have serverless architecture
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
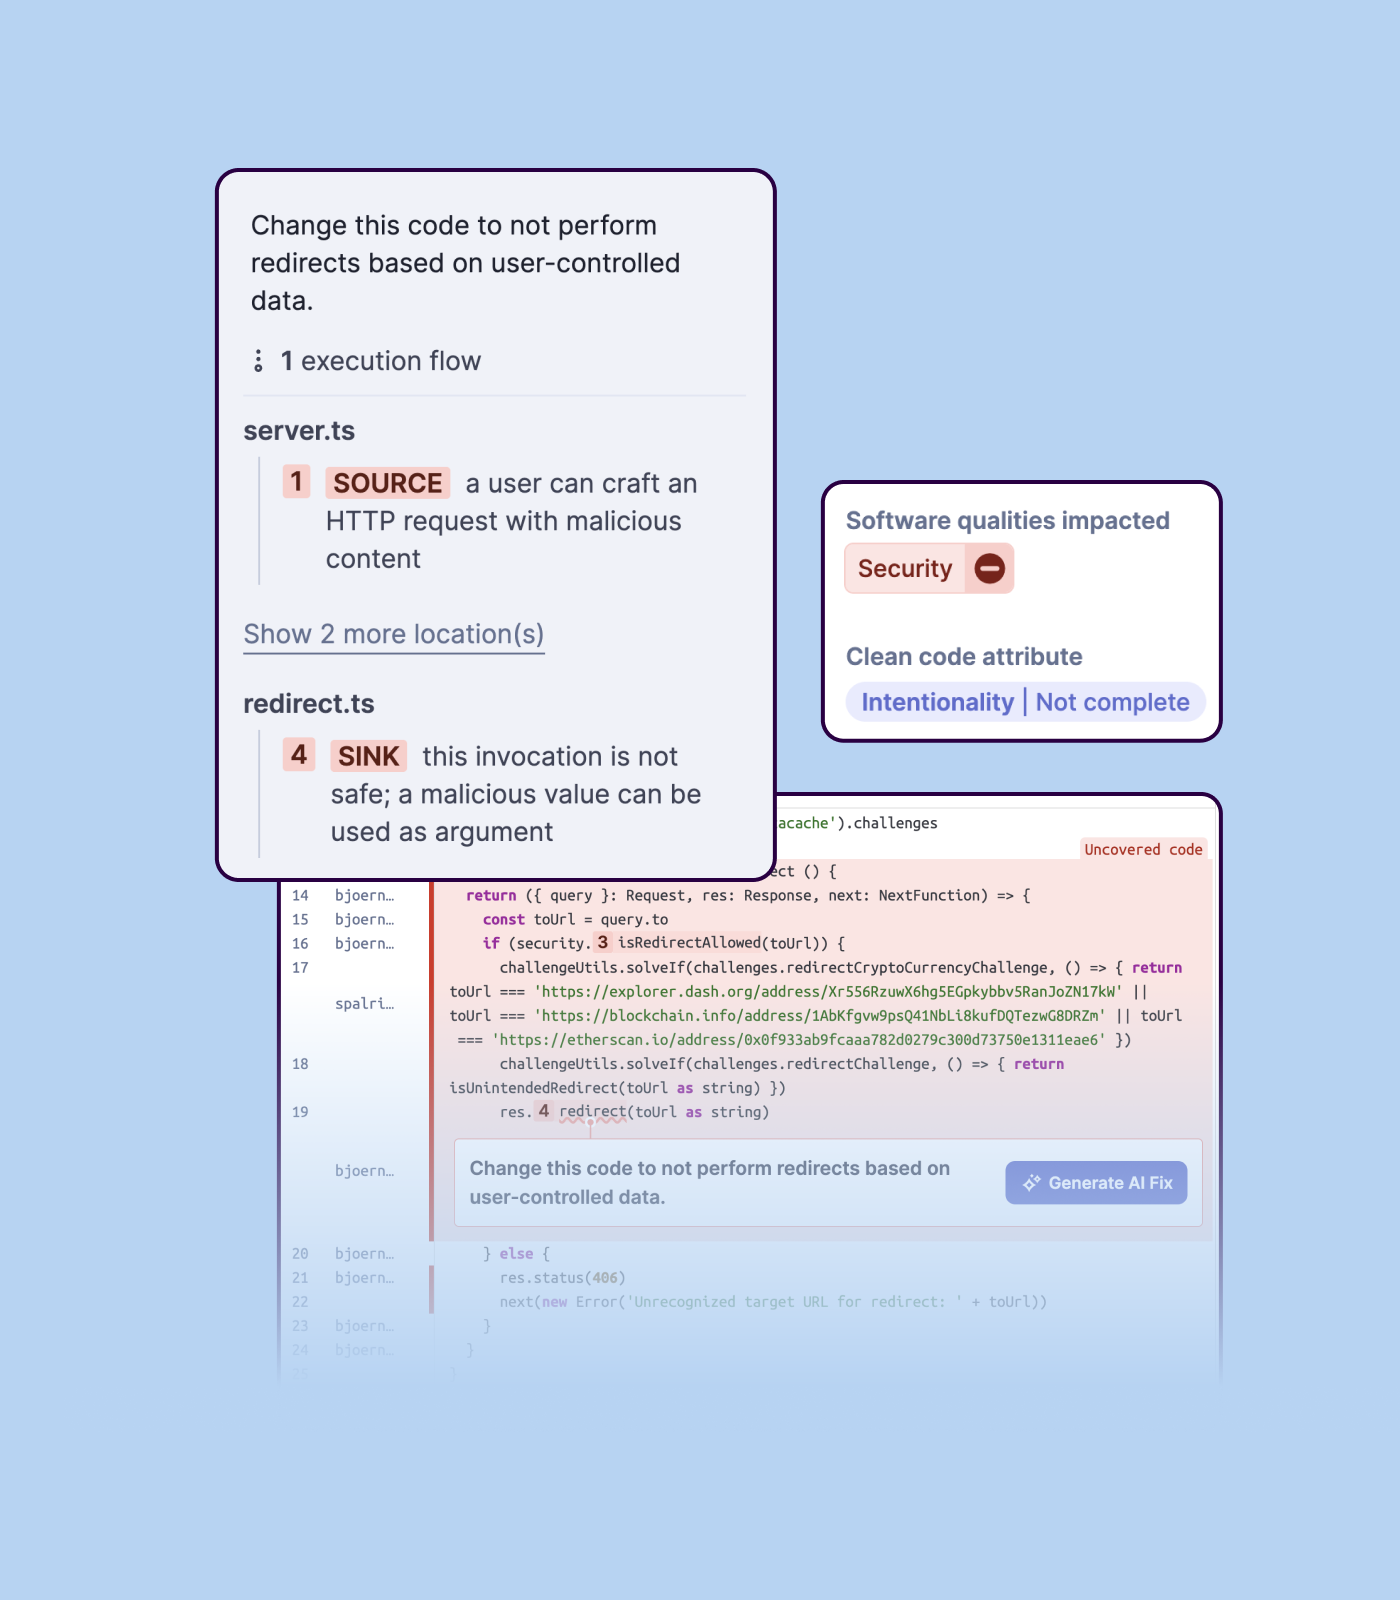
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Since every firm needs to perform static code analysis on their applications, I believe Micro Focus Fortify WebInspect would work well for them (they also offer dynamic scanning, although I haven't used it myself). Different static analysis tools scan code in different ways, and Micro Focus Fortify WebInspect asks you to submit a complete build of the application along with debugging files. Depending on how your company builds its apps, this requirement may be simple or challenging.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Their API based customizations which I leveraged to create an ASPM package, which is developer friendly and can extend above the dashboard features, other ones are UI which is great and feels clutter free. Menu and navigation is also good so as support. Only drawback is sometimes scan takes longer which I feel so can be reduced
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a cloud-based platform which can provide us a very useful and unique features like Application Assessment, Scans, Vulnerability Test, Comprehensive Reporting, Monitoring, etc. Fortify by Open Text is also outstanding in various parameters for the support and integration and it is highly adaptable in various DevOps Program where you need secure app testing with all given features.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Checkmarx is easier to integrate with development tools and gives quick feedback during coding, which is helpful for developers. Veracode is more focused on scanning and reporting for compliance, but it’s more complex to set up. We chose Checkmarx because it fits better into our development process, offering faster scans and more useful suggestions for fixing problems
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Fortify Application Defender is a little more timely and upfront with a lot of their information on cyber security. we like what they provide and how they communicate with our users. I think they have a good understanding and practice in their field. they seem best suited for us and the best fit.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)