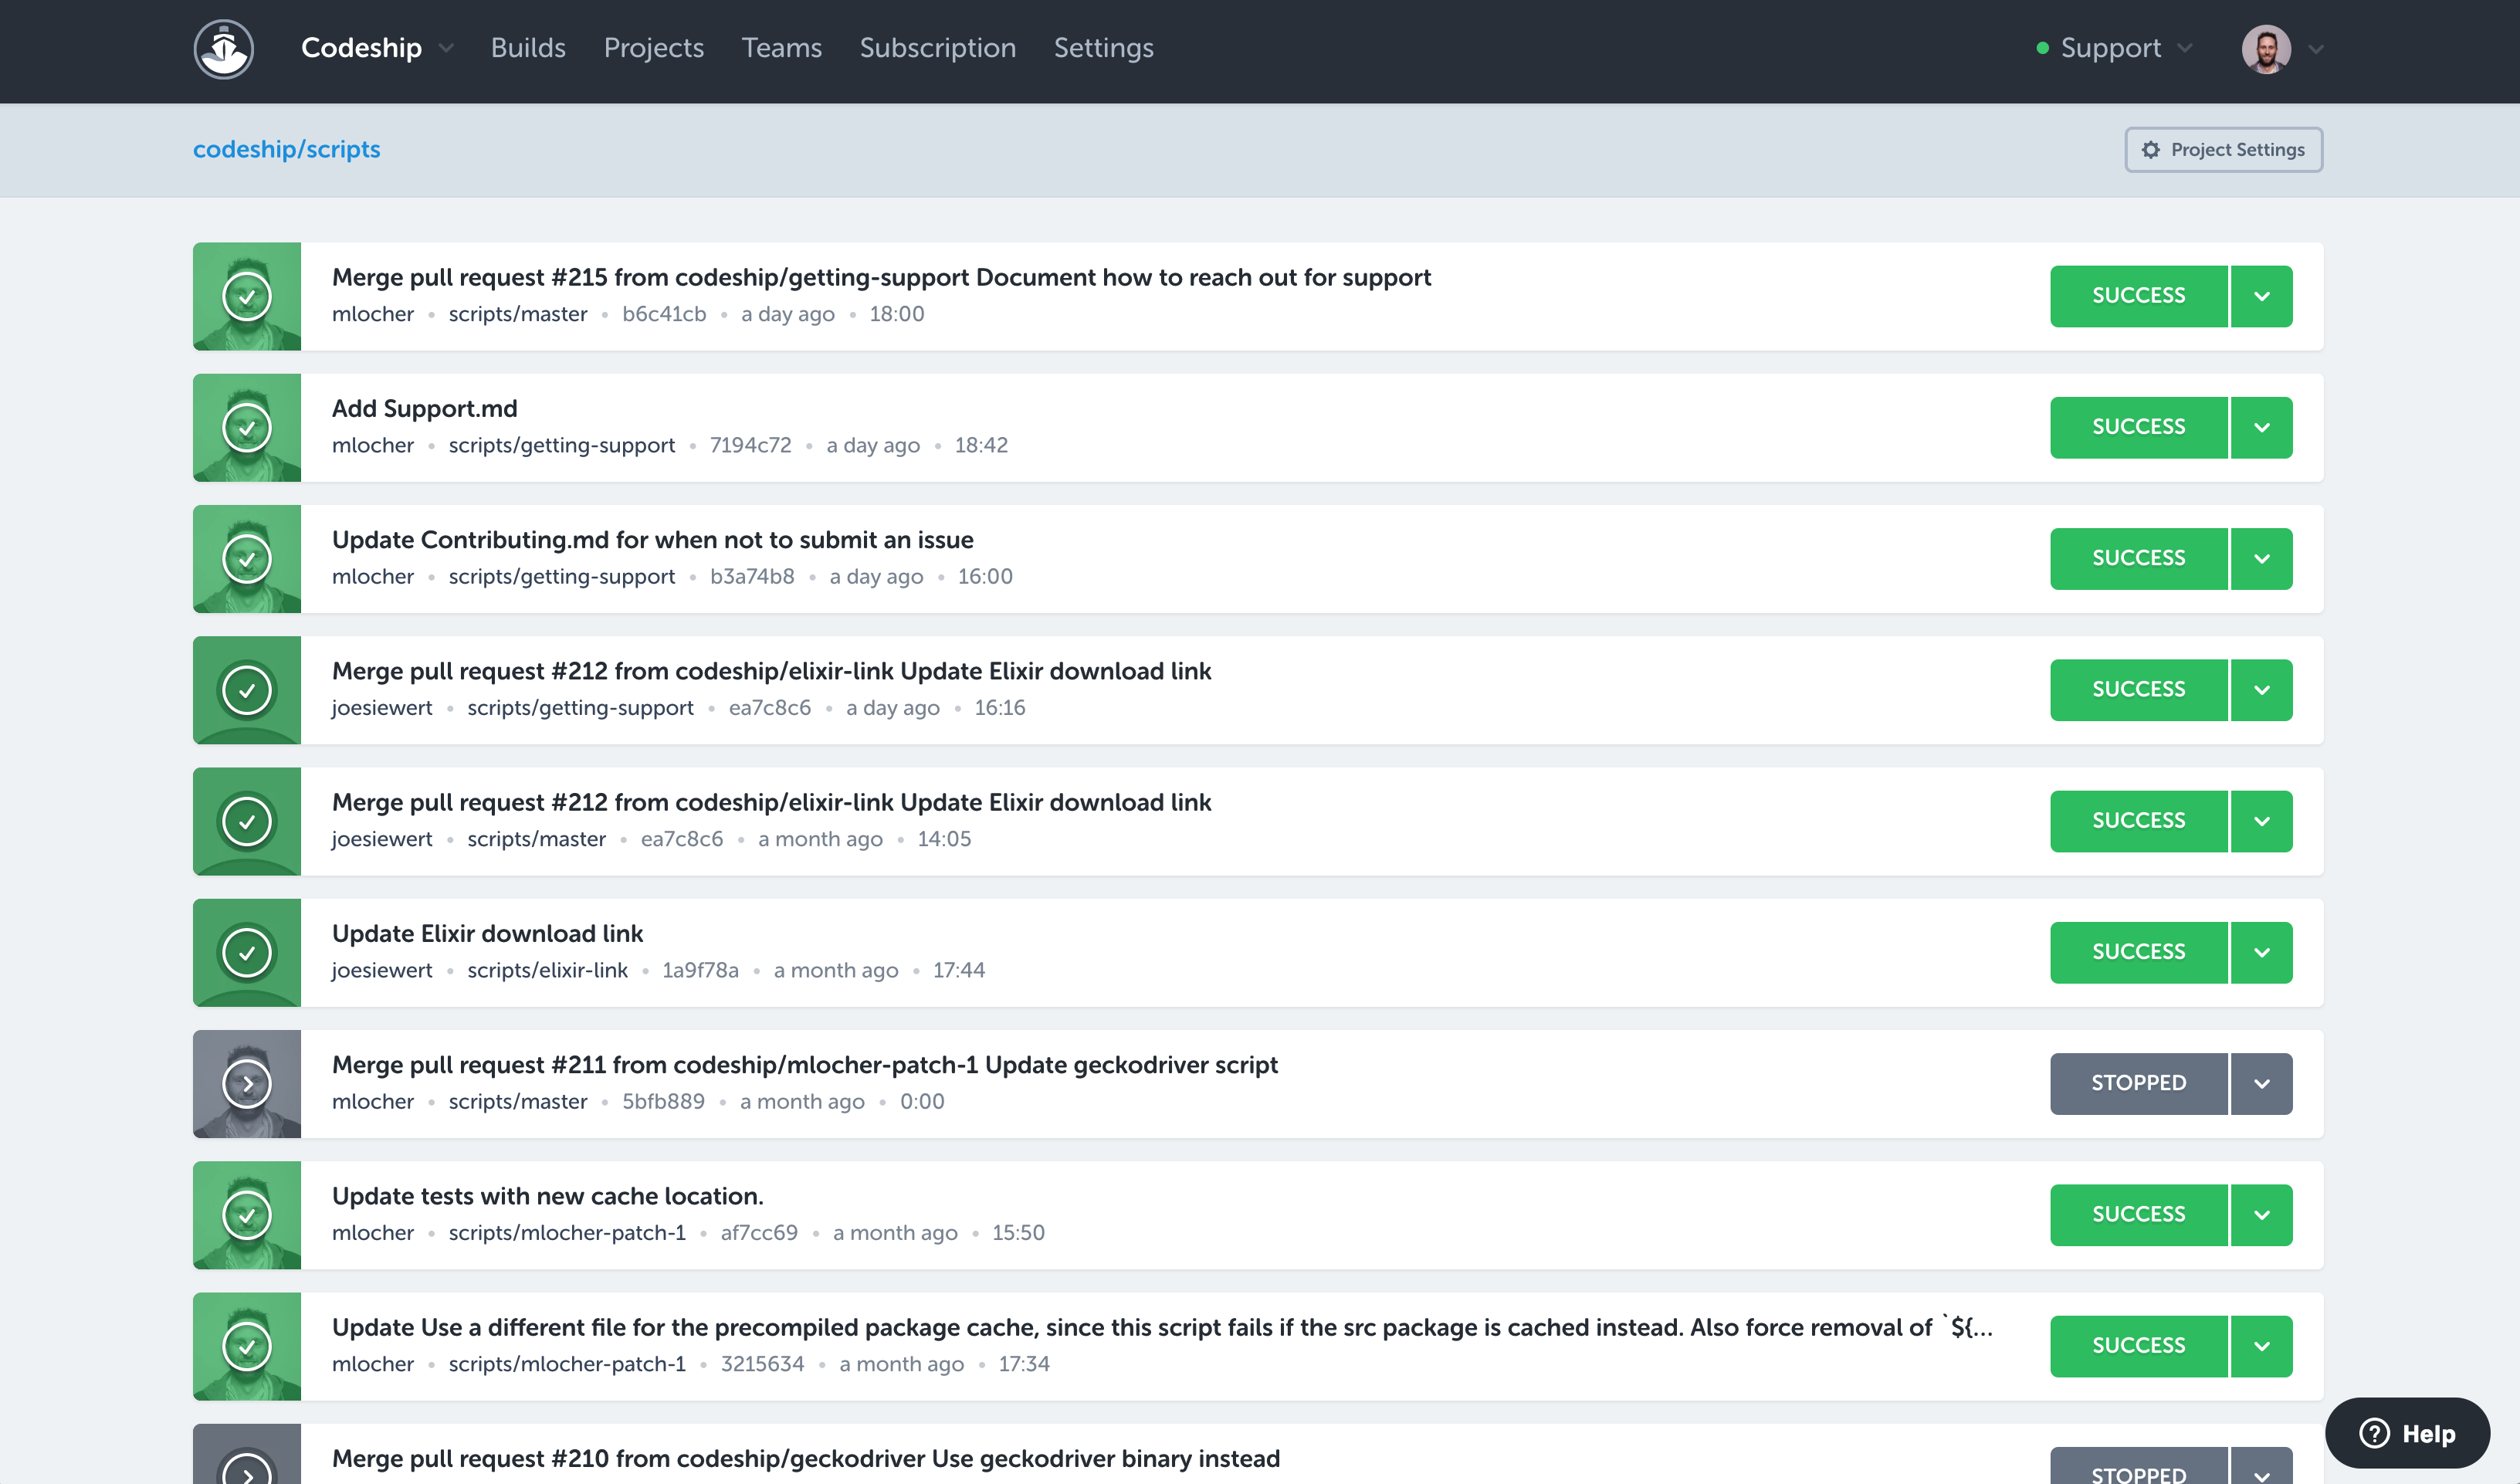
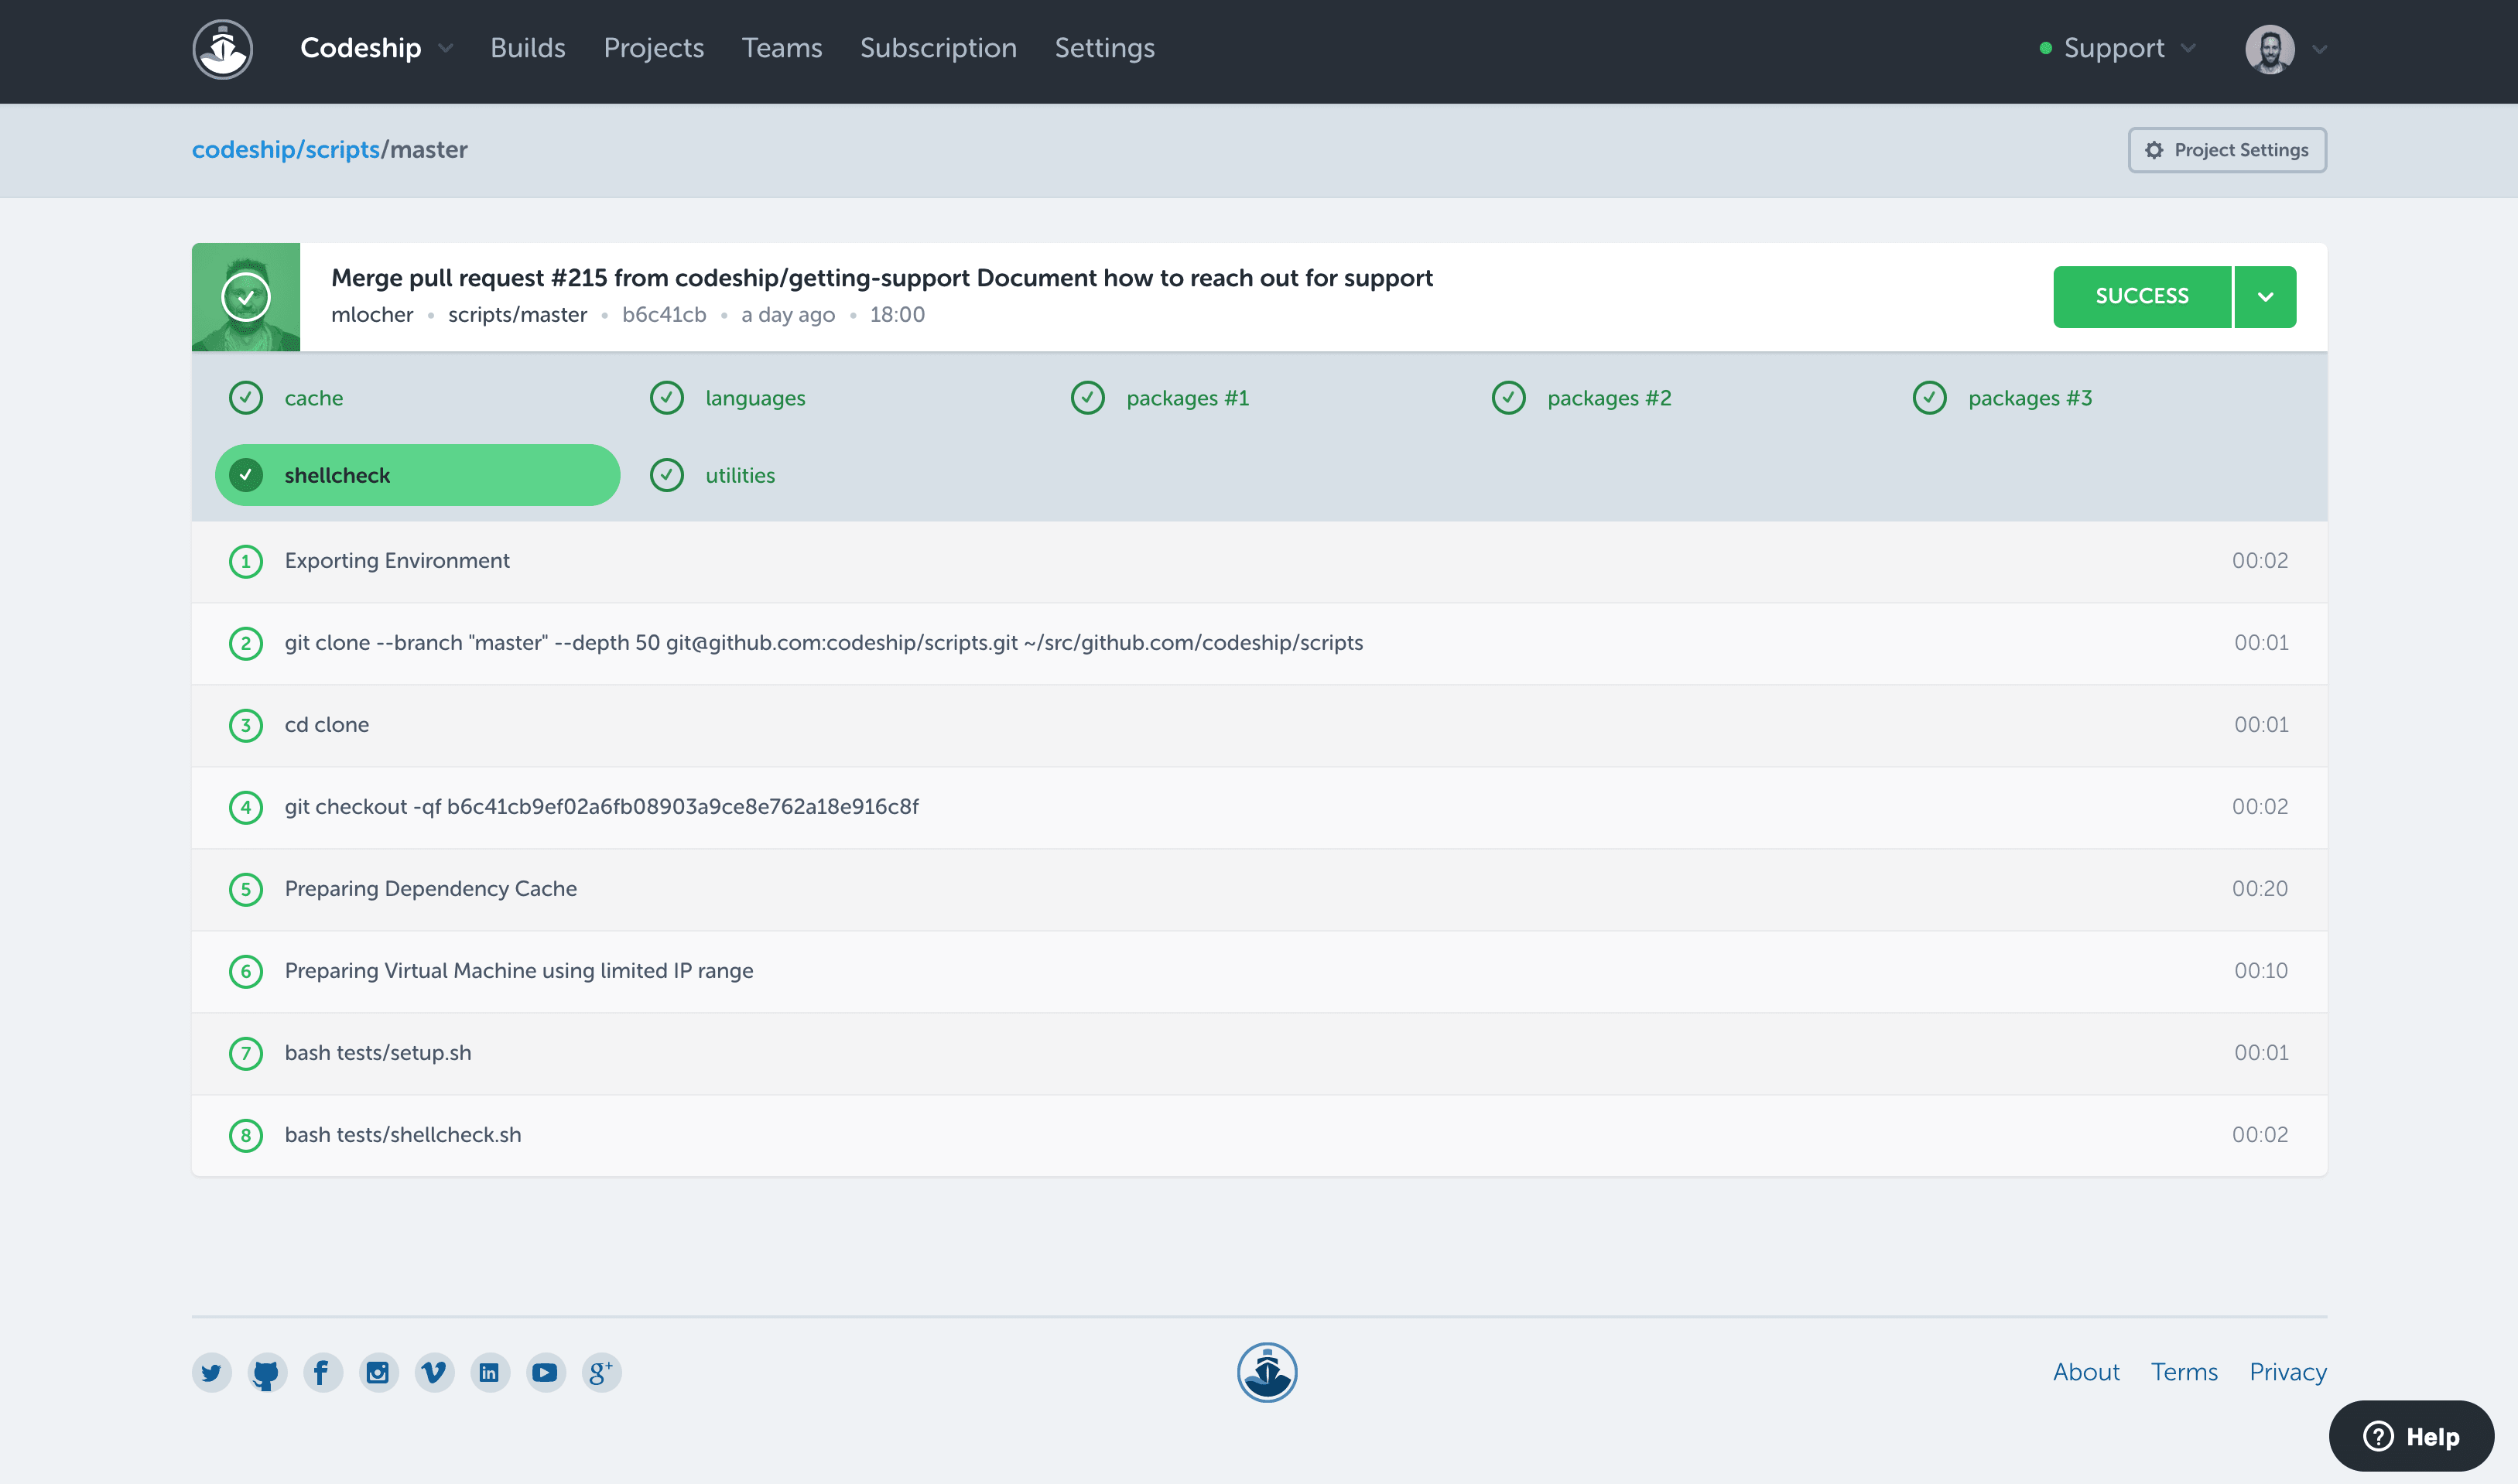
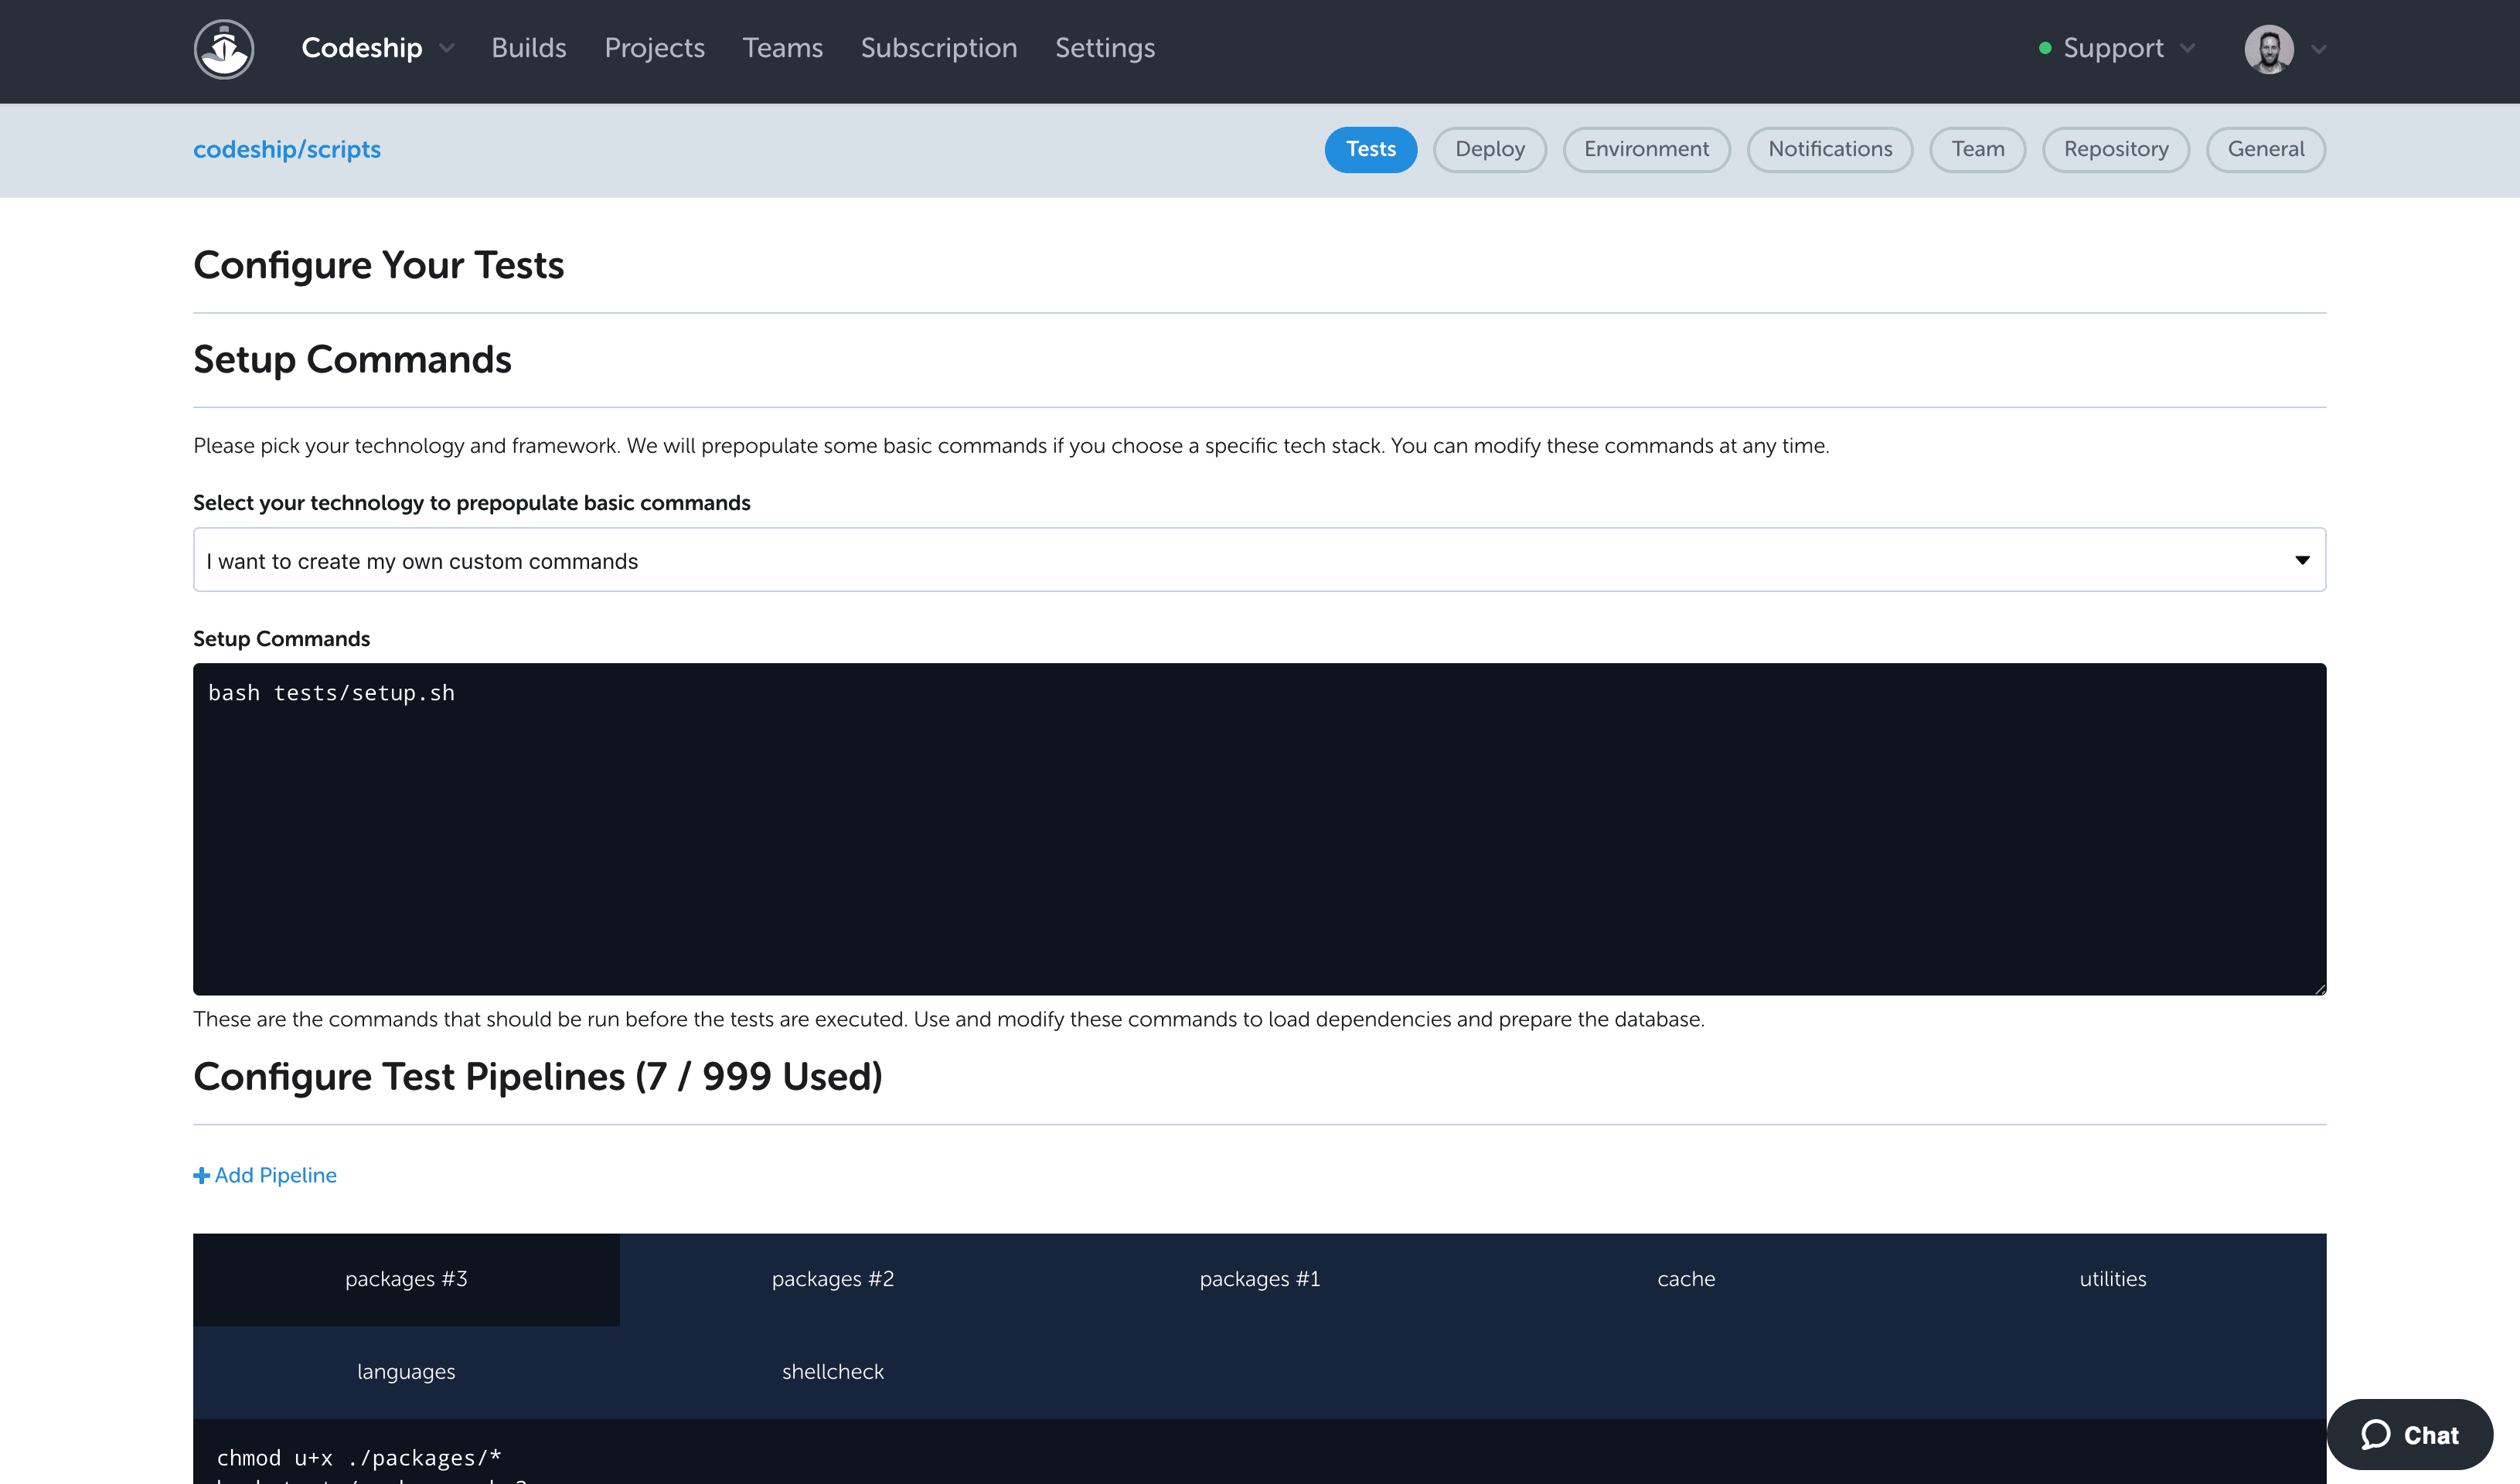
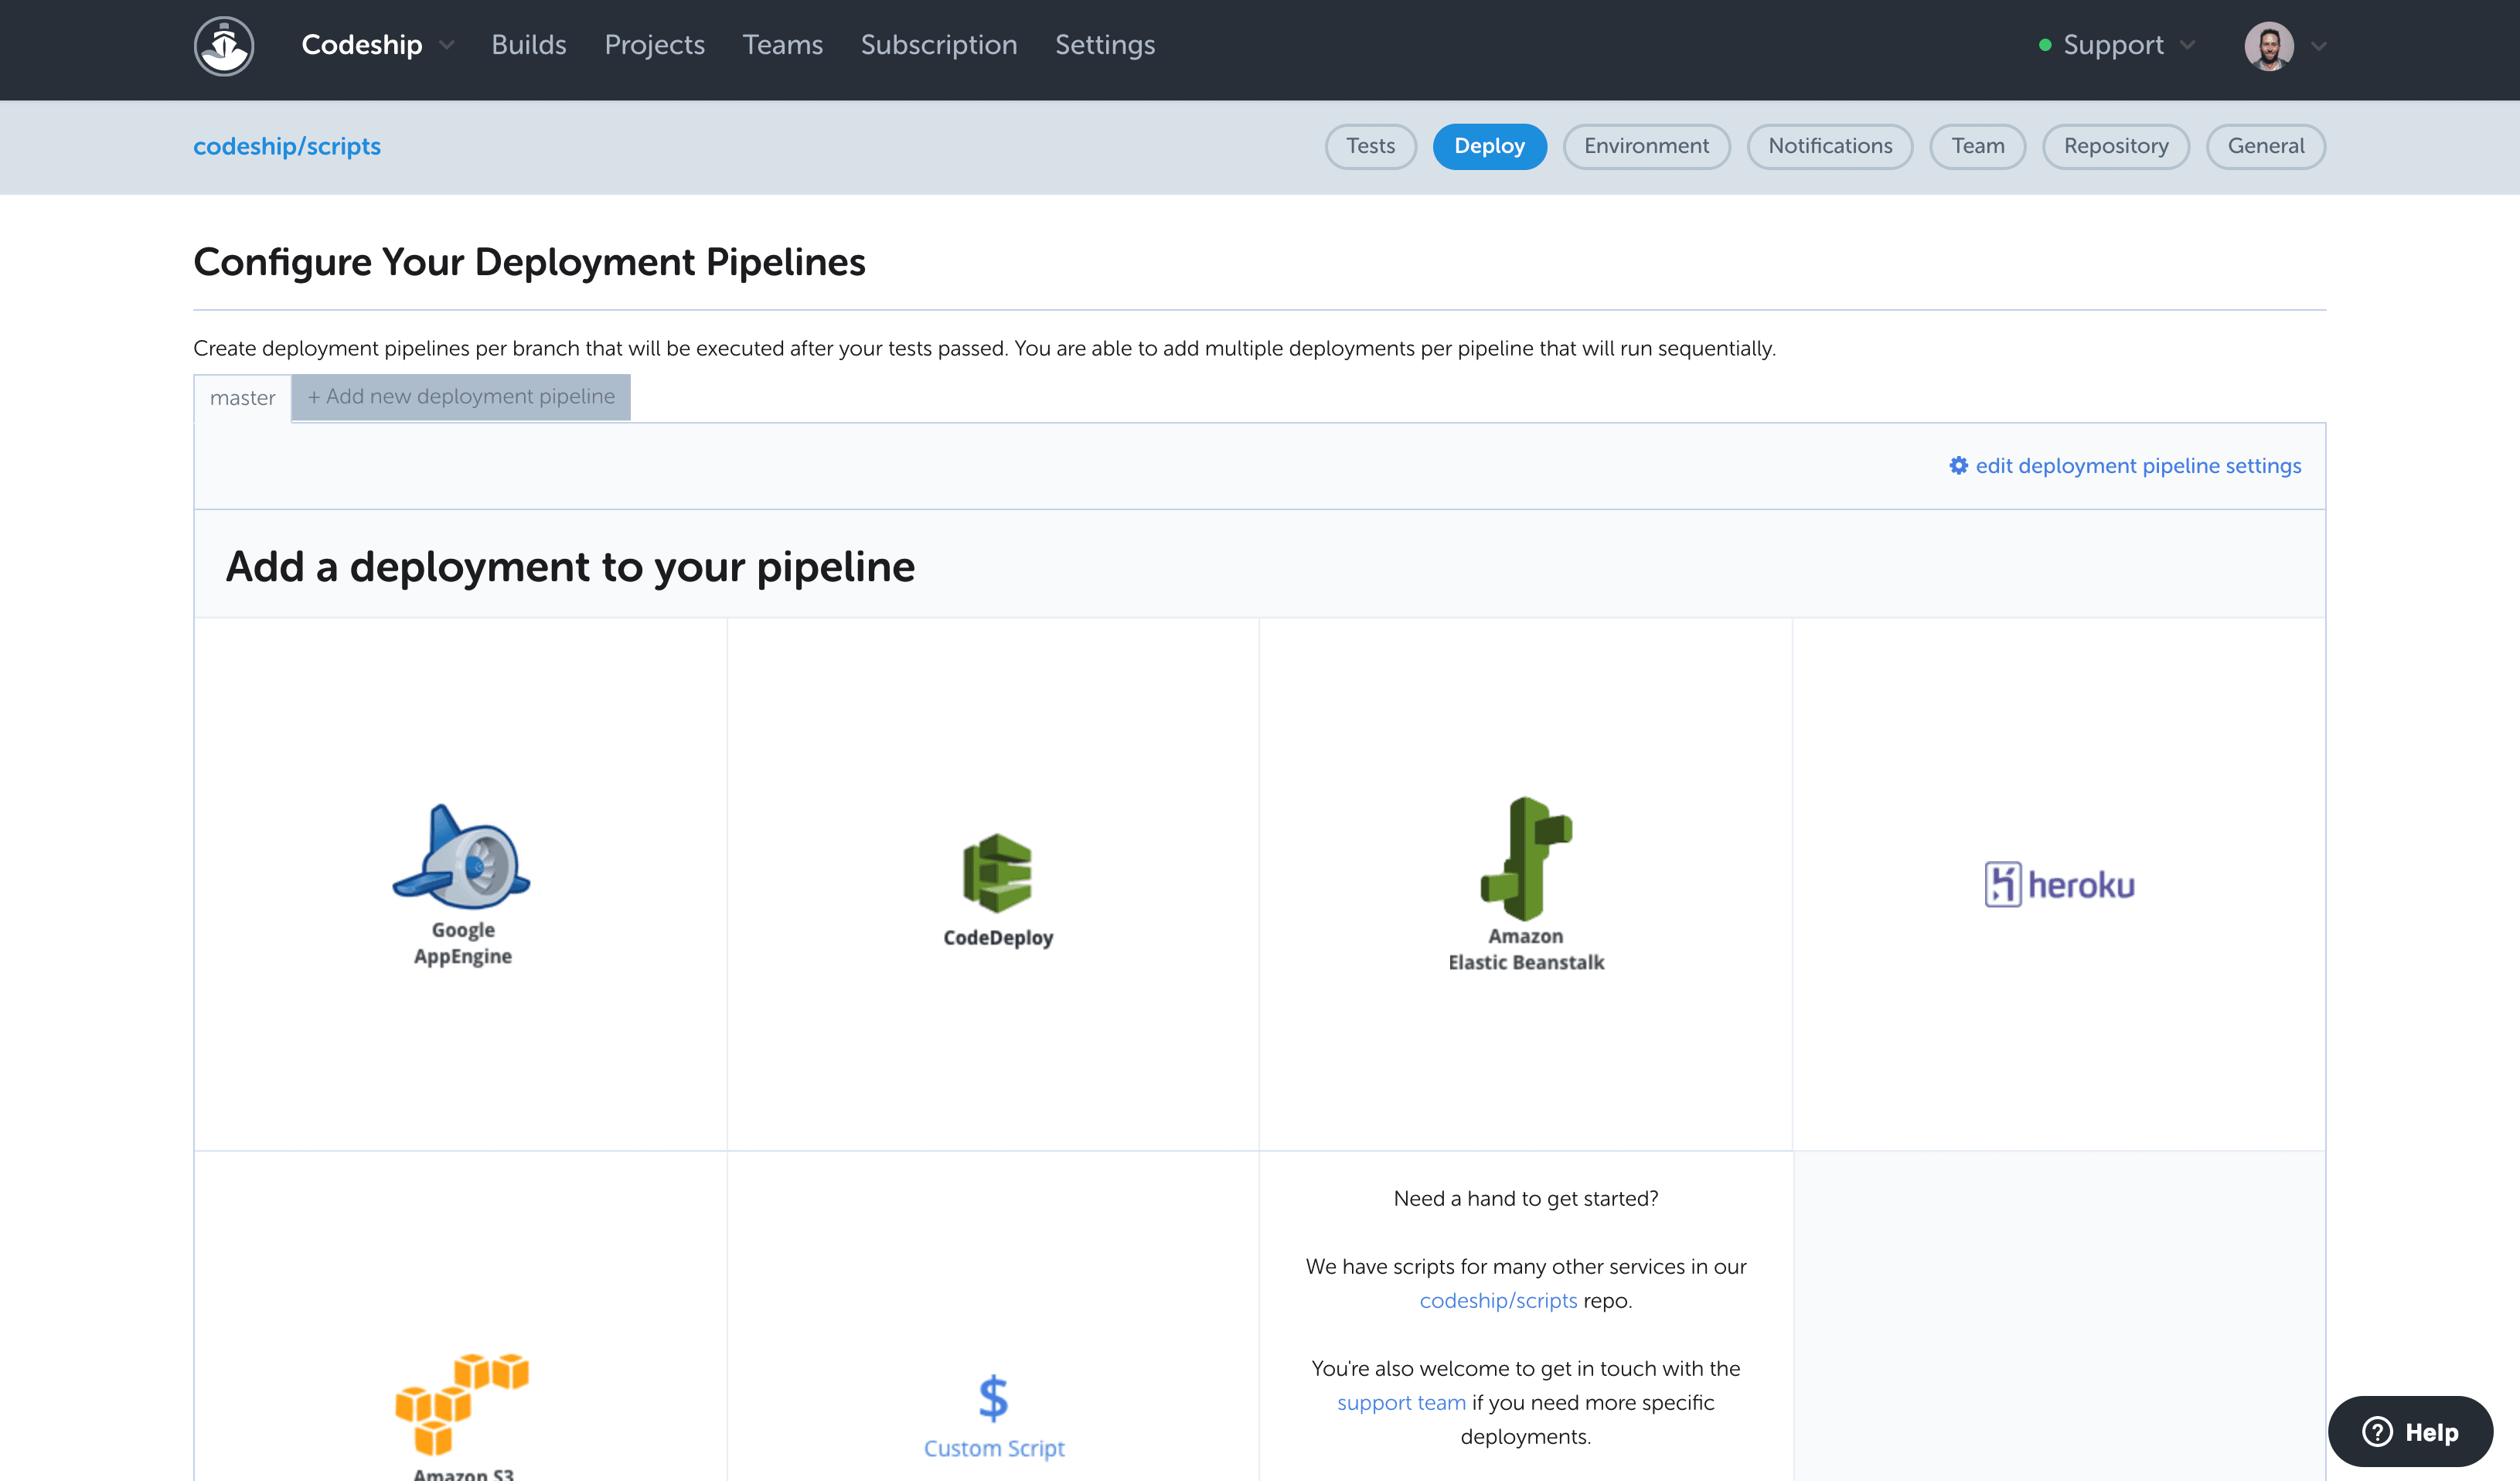
Codeship from CloudBees is a build automation platform from the Austrian company of the same name.
N/A
Snyk
Score8.6 out of 10
N/A
Snyk’s Developer Security Platform automatically integrates with a developer’s workflow and helps security teams to collaborate with their development teams. It boasts a developer-first approach that ensures organizations can secure all of the critical components of their applications from code to cloud, driving developer productivity, revenue growth, customer satisfaction, cost savings and an improved security posture. The vendor states Snyk is used by 1,200 customers worldwide today, including…
$0
Pricing
CloudBees Codeship
Snyk
Editions & Modules
No answers on this topic
Free
$0
Team (Snyk Open Source or Snyk Container or Snyk Infrastructure as Code)
$23
per month per user
Business (Snyk Open Source or Snyk Container or Snyk Infrastructure as Code)
$42
per month per user
Team (Snyk Open Source + Snyk Container + Snyk Code + Snyk Infrastructure as Code)
$98
per month per user
Business (Snyk Open Source + Snyk Container + Snyk Code + Snyk Infrastructure as Code)
$178
per month per user
Enterprise
Contact Sales
Offerings
Pricing Offerings
CloudBees Codeship
Snyk
Free Trial
Yes
Yes
Free/Freemium Version
Yes
Yes
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
Pricing is dependent on the number of developers selected, the number of products selected, and the payment term selected. Please visit the Snyk plans page for an interactive pricing calculator.
Codeship is extremely well suited for projects that are version controlled on public hosting such as Github or Bitbucket, and for situations where you need to pick up code from these systems and deploy it to different cloud environments. For example, we had two projects for the same client that were hosted on Github and needed to be deployed to AWS and Heroku. The native CI/CD tools of these cloud environments could not provide a holistic solution to deploy to both environments the way Codeship did.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Scenarios Where Snyk Is Well-Suited CI/CD Pipeline Integration (Node.js, Python, etc.) Container Security Open Source License Compliance Infrastructure as Code (IaC) SecurityScenarios Where Snyk May Be Less Appropriate Scanning Proprietary or Custom Code for Unknown Vulnerabilities Complex Monorepos with Custom Build Tools Organizations Requiring Custom Security Rules Advanced Security Teams Needing Correlation and Deep Triage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Codeship provides a set of tools for quickly creating and building our deployment artifacts and push them to the designated servers.
Codeship's hooks allows our developers to simply push tags from our git repositories to initiate a deployment of code to a server. No one outside of the devops team needs any expertise to get our code packages delivered.
Codeship allows us to tie in behat and unit tests easily to prevent delivery of buggy code.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I would like to see a little bit more than the green/red status. If there are tests, it would be good to see how many have failed on a red build.
To improve build times (and reduce feedback times), it would be good to see how long build, tests, and deployment take over time. An overview like that could very easily point to potential areas of improvement. I think Codeship users do not want to bother with the build process, but, if there is anything to improve and increase productivity it's very unlikely that users wouldn't want to do this.
The tool itself has many capabilities but using them operationally within the platform on a day to day basis for managing vulnerabilities is not a good experience.
Our company was in desparate need of a tool to help us manage vulnerabilities so we could achieve a SOC 2 assurance report without findings.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Developer-Centric Design - Snyk integrates directly into IDEs (like VS Code and IntelliJ), CI/CD pipelines, GitHub/GitLab, and container registries. Clear, Actionable Vulnerability report issues are categorized by severity.
Reports include fix recommendations, pull request suggestions, and links to remediation advice.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Our company uses Jenkins for all internal deployment processes for one very important reason - it's hosted internally. But Codeship is great for personal use - it has intuitive UI, easy setup and tons of integrations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Unfortunately, neither cover all of the use cases that we would like so we need to use both but they are both excellent tools as part of our vulnerability management. We find that Snyk helps us better with improving our MTTR of identified vulnerabilities when compared to inspector but that may be more based on how we have implemented both tools
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Having the code tested thoroughly. While it's obviously a part of the job that still requires the developer to sit down and to actually have some decent and thorough tests implemented, by using codeship we were able to guarantee 100% that our code was being tested each and every time it got commited and pushed onto our repositories. Leading to a faster, shorter and sure implementation iterative cycle.
Fewer 'man in the middle' processes which required more steps and people involved just to get the code shipped onto our deployment servers.
Almost inexistent learning curve. Codeship is simple to use and very intuitive. Nobody in our development department had a hard time figuring out how to have it properly configured for each new project created there.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info