TrustRadius: an HG Insights company

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Eureka DevSecOps

    N/A
    Small Businesses (1-50 employees)
    Eureka supports application vulnerability management for teams that need more than raw scanner output. It helps organize findings, show status, connect work to owners, track remediation activity, and preserve the history reviewers and security leaders need to understand what changed over time. It is useful for teams dealing with scanner fatigue, backlog noise, and unclear prioritization. Eureka is an AppSec evidence layer for software teams facing customer reviews, SOC 2 preparation, or…

    $150

    per month includes up to five seats

    SonarQube

    Score8.5 out of 10
    N/ASonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.

    $34

    per month Recommended for teams <50 developers

    Pricing
    Eureka DevSecOpsSonarQube
    Editions & Modules
    Team
    $150
    per month
    Enterprise
    Custom
    SonarQube Community Build
    $0
    (open source)
    Self-managed: Developer
    Starting at $720 annually
    per year per installation
    Self-managed: Enterprise
    Contact sales for pricing
    per year per installation
    Cloud-based: Enterprise
    Contact sales for pricing
    per year per installation
    Cloud-based: Teams
    Starting at $34 per month
    per month per installation
    Self-managed: Data Center
    Contact sales for pricing
    per year per installation
    Offerings
    Pricing Offerings
    Eureka DevSecOpsSonarQube
    Free Trial
    YesYes
    Free/Freemium Version
    NoYes
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional DetailsSeats are counted as contributing users connected to scanned repositories, not total employees. Enterprise pricing includes usage-based credits that scale with repository coverage, scan volume, advanced integrations, custom workflows, and evidence exports — specific credit prices are not publicly listed. Eligible open-source projects can apply for free access. A discount is available for annual billing.—
    More Pricing Information
    Community Pulse
    Eureka DevSecOpsSonarQube
    Considered Both Products
    Eureka DevSecops
    No answer on this topic
    SonarSource Sarl
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    100%
    Would buy again
    32 Answers
    Delivers good value for the price
    No answers on this topic
    100%
    Delivers good value for the price
    29 Answers
    Happy with the feature set
    No answers on this topic
    100%
    Happy with the feature set
    32 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    95%
    Lived up to sales and marketing promises
    18 Answers
    Implementation went as expected
    No answers on this topic
    100%
    Implementation went as expected
    27 Answers
    Best Alternatives
    Eureka DevSecOpsSonarQube
    Small Businesses
    GitLab
    Score8.9 out of 10
    No answers on this topic
    Medium-sized Companies
    GitLab
    Score8.9 out of 10
    No answers on this topic
    Enterprises
    GitLab
    Score8.9 out of 10
    No answers on this topic
    All AlternativesView all alternativesView all alternatives
    User Ratings
    Eureka DevSecOpsSonarQube
    Likelihood to Recommend
    -
    (0 ratings)
    8.9
    (35 ratings)
    Usability
    -
    (0 ratings)
    9.1
    (2 ratings)
    Support Rating
    -
    (0 ratings)
    9.0
    (1 ratings)
    User Testimonials
    Eureka DevSecOpsSonarQube
    Likelihood to Recommend
    Eureka DevSecops
    No answers on this topic
    SonarSource Sarl
    SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
    Incentivized
    Read full review
    Pros
    Eureka DevSecops
    No answers on this topic
    SonarSource Sarl
    • Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
    • Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
    • Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
    • Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
    • Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
    • Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
    Incentivized
    Read full review
    Cons
    Eureka DevSecops
    No answers on this topic
    SonarSource Sarl
    • Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
    • Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
    • When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
    Incentivized
    Read full review
    Usability
    Eureka DevSecops
    No answers on this topic
    SonarSource Sarl
    It can improve in some user experience and usability parts, like the code view and the way we assign issues it's a bit hidden and not highlighted
    Incentivized
    Read full review
    Support Rating
    Eureka DevSecops
    No answers on this topic
    SonarSource Sarl
    We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
    Incentivized
    Read full review
    Alternatives Considered
    Eureka DevSecops
    No answers on this topic
    SonarSource Sarl
    SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
    Incentivized
    Read full review
    Return on Investment
    Eureka DevSecops
    No answers on this topic
    SonarSource Sarl
    • Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
    • Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)
    Read full review
    ScreenShots

    Eureka DevSecOps Screenshots

    Screenshot of which findings combine into an attack scenario, scored so you know what to fix first.Screenshot of An attack scenario that shows the steps an attacker could chain together and the findings involved.Screenshot of a vulnerability finding and the OWASP ASVS reference displayed in its details.Screenshot of Press Autofix to start an AI agent that writes a fix for a GitHub repository.Screenshot of a finding. Every finding comes with the affected code and how to fix it.

    SonarQube Screenshots

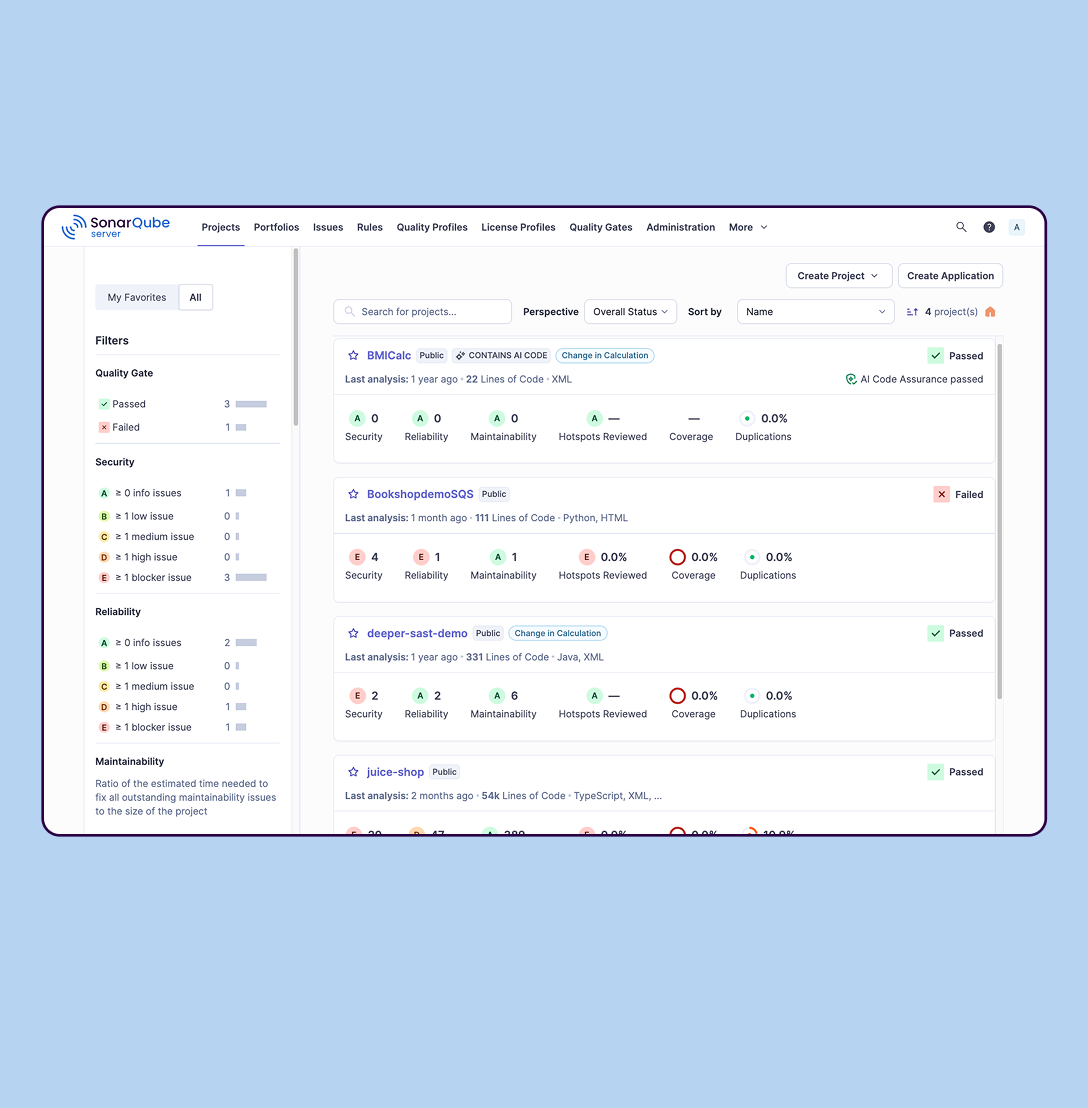
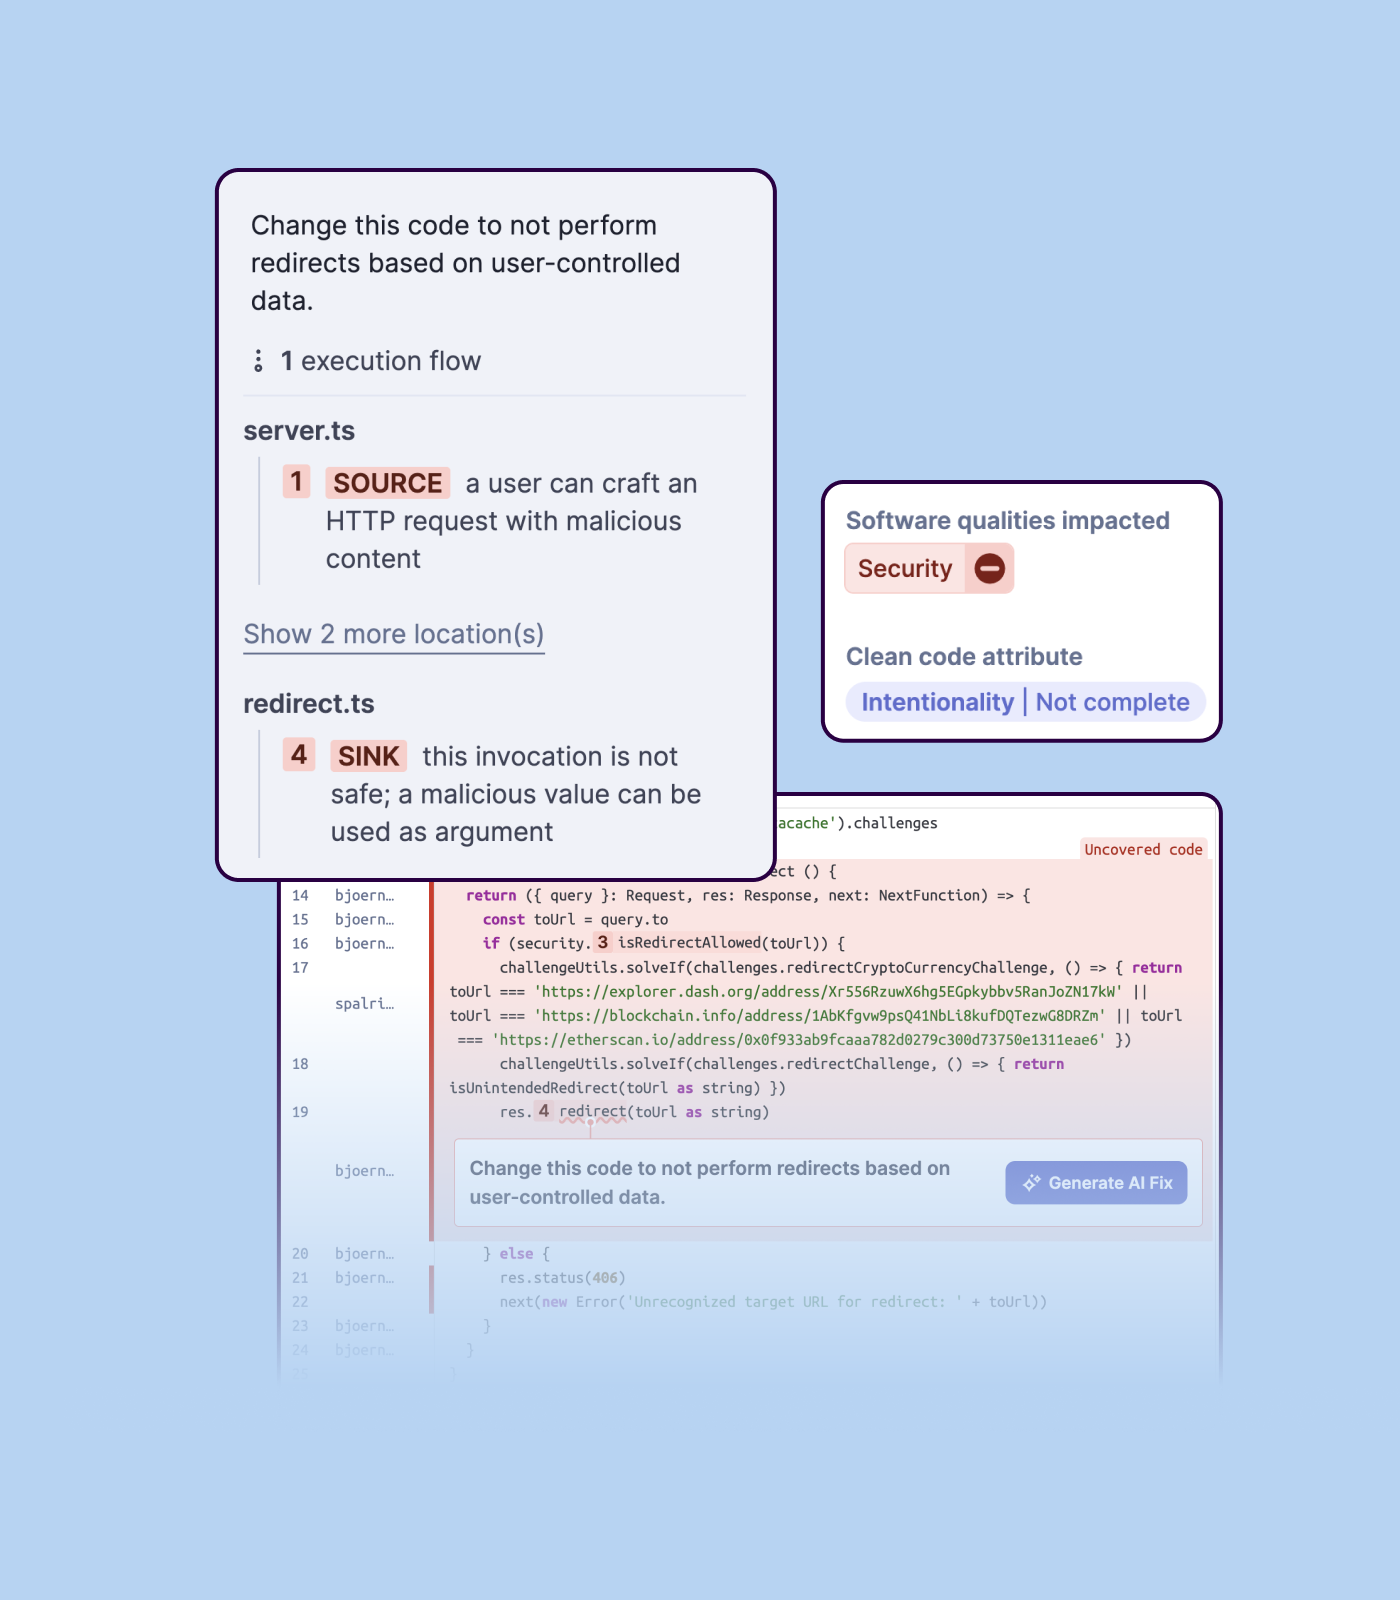
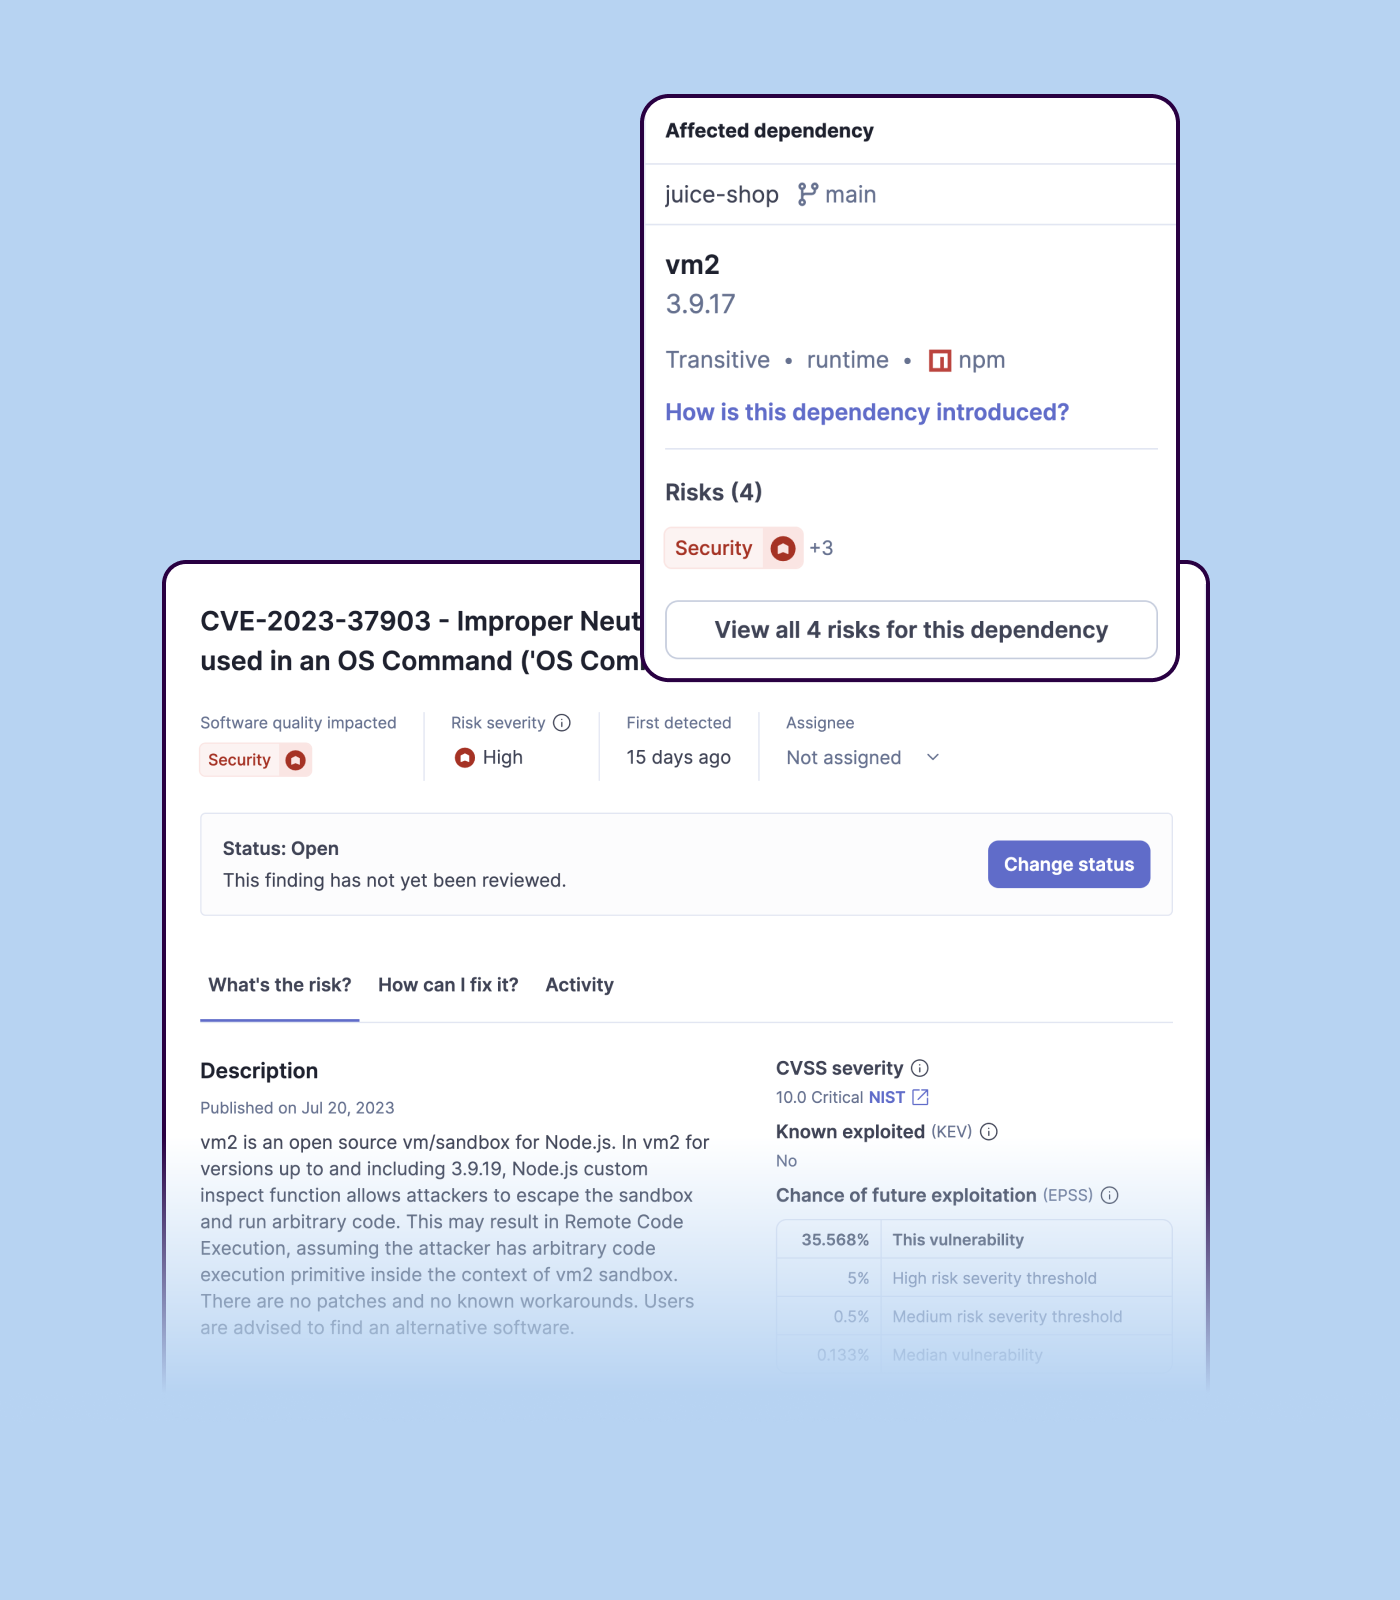
    Screenshot of Projects.Screenshot of Static Application Security Testing.Screenshot of Software Composition Analysis.