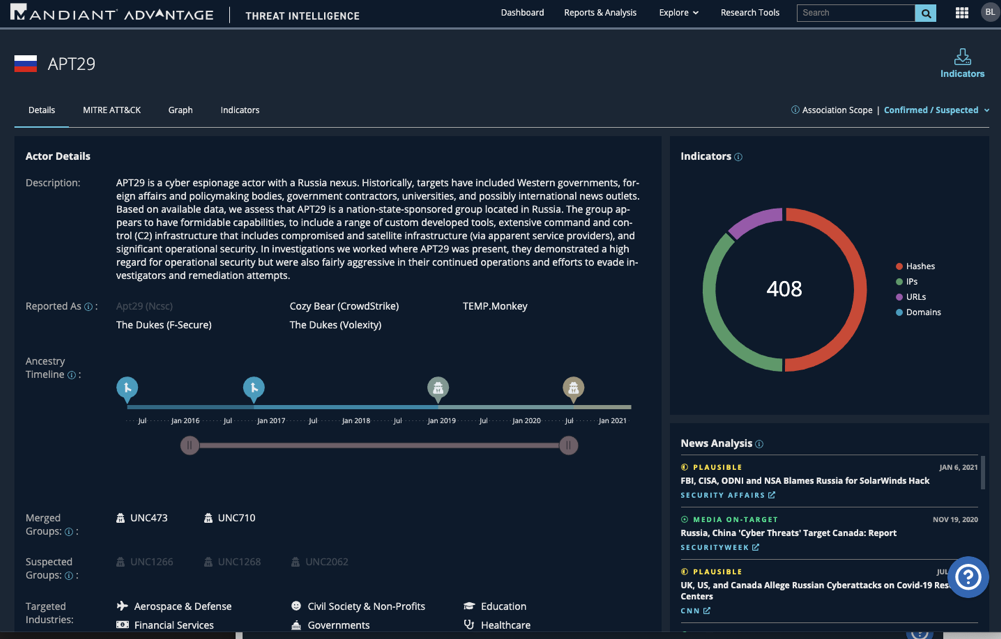
Google Threat Intelligence, based on the expertise and service of Mandiant, aims to accelerate security and risk decision making – operational as well as strategic – and to enable security teams to focus on threats that matter to them.
N/A
Pricing
Google Threat Intelligence (Mandiant)
Editions & Modules
No answers on this topic
Offerings
Pricing Offerings
Google Threat Intelligence (Mandiant)
Free Trial
Yes
Free/Freemium Version
Yes
Premium Consulting/Integration Services
Yes
Entry-level Setup Fee
Optional
Additional Details
Priced by company size
More Pricing Information
Community Pulse
Google Threat Intelligence (Mandiant)
Considered Both Products
Google
Verified User
Chose Google Threat Intelligence (Mandiant)
There are multiple SaaS based players offering Threat Intel. But Mandiant TI has the following features which makes it one of the best among the competitors: 1.It understands recent actor, malware or vulnerability trends making it very easy for the analysts to do the research 2.Th…
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Global Enterprise Architect in Information Technology at Kyndryl (Information Technology & Services, 10,001+ employees)
Chose Google Threat Intelligence (Mandiant)
Broadcom, though it has similar functionality, is a bit expensive in terms of licensing and the feature set available for integration into the existing environment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Google Threat Intelligence (Mandiant)
The Mandiant Advantage Threat intelligence can evaluate and find the holes in the existing security countermeasures, giving the option to detect vulnerabilities and threats in advance. We can do device health checks periodically, making it possible to identify the weaknesses …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Google Threat Intelligence (Mandiant)
The interface and clearly the analysis provided was much better as compared to other tools. Also, it is more integrable and provided real updates, the logs are also detailed and clear to navigate to the issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Network Security Engineer in Information Technology at Hitachi Systems Micro Clinic (Computer & Network Security, 5001-10,000 employees)
Chose Google Threat Intelligence (Mandiant)
It gives more ways to analyze threats and options to fixed it. This device gives more visibility on vulnerability detection and its analysis. It provides detailed reports to have more information of all malwares which help us to increase overall security of our current …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Senior Security Engineer in Information Technology at NCRIC (Government Administration, 51-200 employees)
Chose Google Threat Intelligence (Mandiant)
I feel that Mandiant Advantage Threat Intelligence is a reputable company with a history of excellent incident response that is well known in the APT space.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
IT Department in Human Resources at It Trailblazers (Computer Software, 501-1000 employees)
Chose Google Threat Intelligence (Mandiant)
I am glad we chose Mandiant Advantage Threat Intelligence for two reasons: They have a very responsive customer support team available 24 hours a day, seven days a week and the dashboard UX is easy to use and attractive.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Google Threat Intelligence (Mandiant)
Recorded Future and ThreatQuotient are in the same ballpark when it comes to price. Mandiant Advantage Threat Intelligence had, at the time of use, the best tracking of unclassified threat actors and the best methodology for assessing the overlap between campaigns and actors. …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Google Threat Intelligence (Mandiant)
For this comparison, I use Intel471, another intelligence platform that I also use on a daily basis. Although it has its differences, the main objective is to provide intelligence to the analyst. Although it is true that Mandiant Advantage Threat Intelligence has higher waiting …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Google Threat Intelligence (Mandiant)
Mandiant Advantage Threat Intelligence offers a wide range of detections that BlueVoyant Digital Risk Protection doesn't cover in my opinion. The software brings a different level of detail that the competitors didn't.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Google Threat Intelligence (Mandiant)
Mandiant provides timely expert analysis for each vulnerability in the vulnerability intelligence feed. Most other solutions are just aggregators of vulnerability data that they synthesize into a feed but don't provide their own expert analysis.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
CSO (Chief Security Officer) in Information Technology at Paya (Financial Services, 201-500 employees)
Chose Google Threat Intelligence (Mandiant)
If you want threat intel coming into your EDR, Email gateway, and IPS, this is the most cost-effective solution. The others can only pump into your SIEM and rely on monitoring and detection. The former goes into active defense, aka active blocking.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Usually SOC leverages Intel from mutiple sources. The scenarios are: 1.Suitable: In large scale SOC where more than 5000 devices are being monitored and the tech stack is wide, Mandiant will play an excellent role in that scenario. 2.Not Suitable: In small scale SOCs wherein limited devices belonging to the same tech stack is being used then the analysts can rely on OSINT and it is not useful to buy the solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Mandiant Advantage Threat Intelligence has a very usable platform, with well-differentiated sections for the analyst, as well as the possibility of cross-searching to obtain the desired results. All this is presented with an interface that is easy on the eye and not very messy, which increases productivity and the speed with which work is done.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It gives more ways to analyze threats and options to fixed it. This device gives more visibility on vulnerability detection and its analysis. It provides detailed reports to have more information of all malwares which help us to increase overall security of our current organization
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info