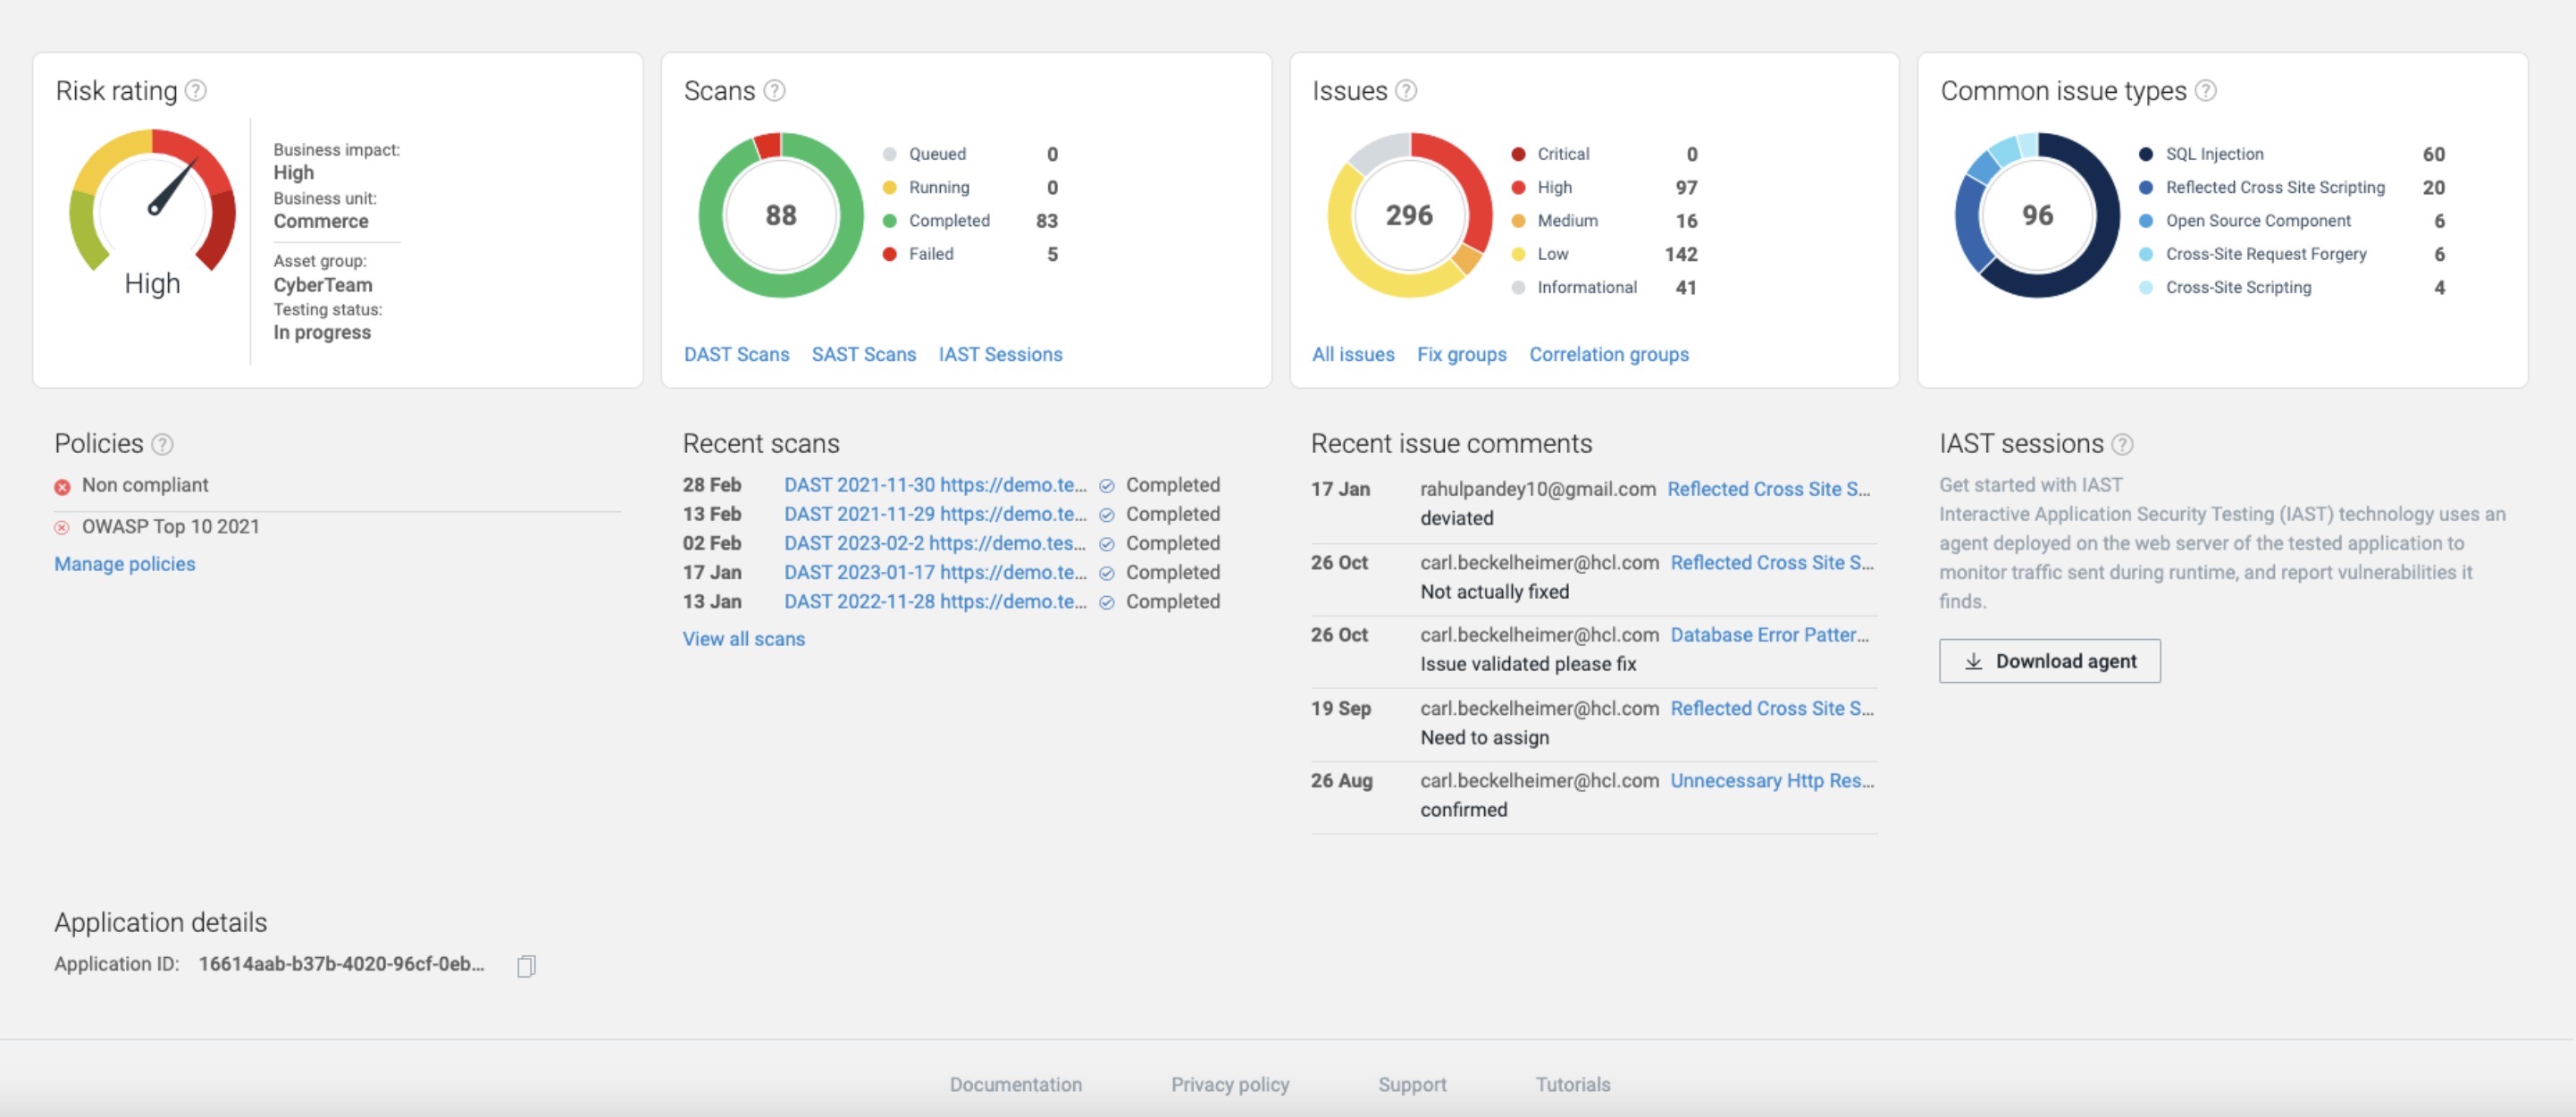
AppScan (formerly Rational AppScan) is an application security testing solution acquired by HCL Technologies from IBM in late 2018. Appscan supports both dynamic (DAST) and static (SAST) application security testing.
$29.99
one-time fee per scan (Choice of DAST, SAST, or SCA scans)
Fortify by OpenText
Score9 out of 10
N/A
An AppSec solution formerly from Micro Focus, spanning SCA, SAST and DAST that supports the breadth and management of any application portfolio, used to secure code. Features API discovery and testing for any application, throughout the software lifecycle.
N/A
SonarQube for IDE
Score8.1 out of 10
N/A
SonarQube for IDE is a free IDE plugin that helps developers by detecting and highlighting issues in their code in real time. Like a spell checker, SonarLint detects Bugs, code smells, and Security Vulnerabilities as code is written, and offers guidance.
$0
Pricing
HCL AppScan
Fortify by OpenText
SonarQube for IDE
Editions & Modules
No answers on this topic
No answers on this topic
No answers on this topic
Offerings
Pricing Offerings
HCL AppScan
Fortify by OpenText
SonarQube for IDE
Free Trial
Yes
No
Yes
Free/Freemium Version
No
No
Yes
Premium Consulting/Integration Services
No
No
No
Entry-level Setup Fee
No setup fee
No setup fee
No setup fee
Additional Details
Pricing varies based on factors such as deployment model, application volume, users, and capabilities. A personalized quote is required based on the environment and its security requirements.
—
—
More Pricing Information
Community Pulse
HCL AppScan
Fortify by OpenText
SonarQube for IDE
Considered Multiple Products
HCLSoftware
No answer on this topic
OpenText
Verified User
Chose Fortify by OpenText
Micro Focus Fortify WebInspect is better when it comes to speed, integration and detection capabilities as compared to Insight Appsec. What I loved the most is the broad coverage of vulnerabilities it identified as against Insight Appsec. Apart from detection capabilities the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
In HCL AppScan automation maintain a reasonable pace of review and remediation of flaws for our apps. HCL AppScan is a cloud-based enterprise mobile application security testing solution for Android and iOS applications developed using Java, .Net or Objective-C. So it covers all our area and It consists of three components: AppScan Source Edition for developing and testing apps internally, AppScan Standard Edition for testing internally or externally, and AppScan Enterprise Edition for large enterprises who need to secure their entire mobile application portfolio across the organization with multiple device types.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is best suited for runtime application security scanning and very useful for automation. You can seemlessly integrate with pipeline for dynamic scans. Cloud based apps can also be scanned for vulnerabilities, cross site scripting attacks. Basically all OWASP TOP 10. It is less appropriate to use if you have serverless architecture
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AppScan works well in finding application vulnerabilities such as SQL injection, cross-site scripting and all of the OWASP top 10.
Flexible reporting allows us to generate executive reports for application owners as well as separate technical reports for developers and system engineers.
Technical reports include remediation information and cross reference CVSS scores
Because it maintains data on all repeated assessments it helps us to do trending and metrics on compliance
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarLint highlights all the issues in our codes and also displays the severity of each issue.
SonarLint also provides suggestions for how to fix those code issues which are highlighted.
SonarLint starts the processing of the file as soon as it is opened and highlights all the issues which it found.
When we fix the issue, we don't even need to create a new build or generate fresh code quality report, as soon as we save the file with the changes, it does the processing again and shows the result if the issue is fixed or not.
SonarLint saves a lot of time and effort by saving us from doing fresh build every time and generating new code quality report every time, thus increasing the efficiency and output which is in return beneficial for the client.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Since every firm needs to perform static code analysis on their applications, I believe Micro Focus Fortify WebInspect would work well for them (they also offer dynamic scanning, although I haven't used it myself). Different static analysis tools scan code in different ways, and Micro Focus Fortify WebInspect asks you to submit a complete build of the application along with debugging files. Depending on how your company builds its apps, this requirement may be simple or challenging.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a cloud-based platform which can provide us a very useful and unique features like Application Assessment, Scans, Vulnerability Test, Comprehensive Reporting, Monitoring, etc. Fortify by Open Text is also outstanding in various parameters for the support and integration and it is highly adaptable in various DevOps Program where you need secure app testing with all given features.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Both solutions are decent, however, I had team members who had the experience working with HCL AppScan. Also, the product was priced nominally which suited our budget. Further, HCL AppScan's user community was bigger and many learning resources were freely available which helped junior peers learn quickly and eliminate any issues
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Fortify Application Defender is a little more timely and upfront with a lot of their information on cyber security. we like what they provide and how they communicate with our users. I think they have a good understanding and practice in their field. they seem best suited for us and the best fit.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There are countless implementations to accomplish the same thing, and so many configurations are required.
Even if you test it finished and find no vulnerabilities, there is no point if you just get the error screen.
Until now, I was worried about vulnerabilities and security in software development, but I think it was good to find the vulnerability problem quickly with HCL AppScan.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarLint helps in achieving all the business requirements in a more efficient way.
It reduces the manual and redundant work which we would have to do else every time if we did not use SonarLint.
SonarLint helps in maintaining code quality, and thus also highlights the loopholes for the cyber attacks and phishing attacks.
SonarLint makes work easy and helps the developer to invest less time in manual work thereby increasing their capacity to deliver the maximum output to the client.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info