IBM Terraform (formerly Hashicorp Terraform) is a cloud infrastructure automation tool used to create, change, and improve production infrastructure, and it allows infrastructure to be expressed as code. It is available Open Source, and via Cloud and Self-Hosted editions.
$0
Microsoft Defender for Cloud
Score8.7 out of 10
N/A
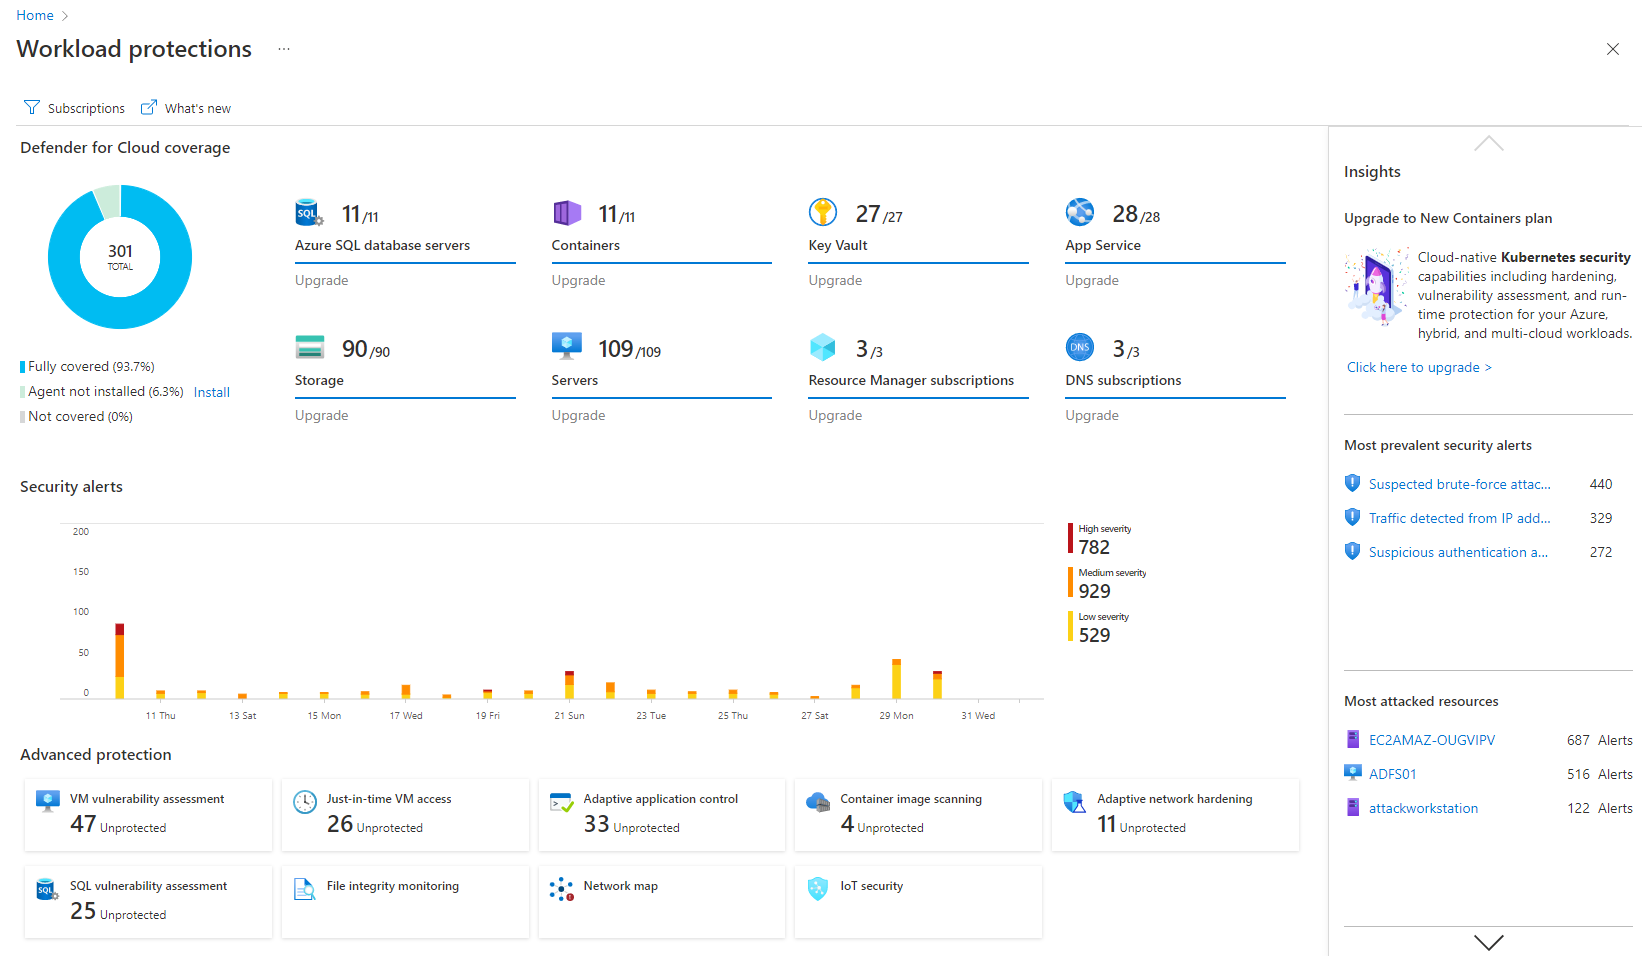
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
Anything that needs to be repeated en masse. Terraform is great at taking a template and have it be repeated across your estate. You can dynamically change the assets they're generating depending on certain variables. Which means though templated assets will all be similar, they're allowed to have unique properties about them. For example flattening JSON into tabular data and ensuring the flattening code is unique to the file's schema.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The language itself is a bit unusual and this makes it hard for new users to get onboarded into the codebase. While it's improving with later releases, basic concepts like "map an array of options into a set of configurations" or "apply this logic if a variable is specified" are possible but unnecessarily cumbersome.
The 'Terraform Plan' operation could be substantially more sophisticated. There are many situations where a Terraform file could never work but successfully passes the 'plan' phase only to fail during the 'apply' phase.
Environment migrations could be smoother. Renaming/refactoring files is a challenge because of the need to use 'Terraform mv' commands, etc.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
The syntax itself is pretty straightforward. The documentation is well-maintained & easy to follow. Most cloud providers, even smaller ones, maintain official provider libraries, making discovery & learning a breeze. Some, like GCP, even provide high-level libraries on top of their own more primitive provider, making building complex infra much more manageable. The language itself is cloud-agnostic, so you can literally manage resources from multiple providers in a single Terraform repo.
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Terraform's performance is quite amazing when it comes to deployment of resources in AWS. Of course, the deployment times depend on various parameters like the number of resources to deploy and different regions to deploy. Terraform cannot control that. The only minor drawback probably shows up when a terraform job is terminated mid way. Then in many cases, time-consuming manual cleanup is required.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have yet to have an opportunity to reach out directly to HashiCorp for support on Terraform. However, I have spent a great deal of time considering their documentation as I use the tool. This opinion is based solely on that. I find the Terraform documentation to have great breadth but lacking in depth in many areas. I appreciate that all of the tool's resources have an entry in the docs but often the examples are lacking. Often, the examples provided are very basic and prompt additional exploration. Also, the links in the documentation often link back to the same page where one might expect to be linked to a different source with additional information.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Terraform is the solid leader in the space. It allows you to do more then just provisioning within a pre-existing servers. It is more extensible and has more providers available than it competitors. It is also open source and more adopted by the community then some of the other solutions that are available in the market place.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
we are able to deploy our infrastructure in a couple of ours in an automated and repeatable way, before this could take weeks if the work was done manually and was a lot of error prone.
having the state file, you can see a diff of what things have changed manually out side of Terraform which is a huge plus
if state file gets corrupted, it is very hard to debug or restore it without an impact or spending hours ..
writing big scale code can be very challenging and hard to be efficient so it's usable by the whole team
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info