TrustRadius: an HG Insights company

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Logmanager

    N/AN/ALogmanager is a log management platform enhanced with SIEM capabilities that helps IT professionals to contain cyberthreats, ensure legal compliance, and streamline troubleshooting. By transforming diverse logs, events, metrics, and traces into actionable insights, it helps security and operations teams respond swiftly to any incident. Logmanager delivers a unified approach to modern observability and security, helping customers…

    $0.09

    per month GB

    Splunk Cloud Platform

    Score8 out of 10
    N/ASplunk Cloud Platform is a data platform service thats help users search, analyze, visualize and act on data. The service can go live in as little as two days, and with an IT backend managed by Splunk experts.N/A
    Pricing
    LogmanagerSplunk Cloud Platform
    Editions & Modules
    Logmanager Free
    $0
    Logmanager Scale
    $0.09
    per month GB
    Logmanager Max
    Custom
    per month GB
    No answers on this topic
    Offerings
    Pricing Offerings
    LogmanagerSplunk Cloud Platform
    Free Trial
    YesNo
    Free/Freemium Version
    YesNo
    Premium Consulting/Integration Services
    YesNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional DetailsAll packages include full log management and SIEM functionality, ensuring that customers in any tier can fully benefit from Logmanager, and does not impose limitations on the number of users. Pay only for the log data stored each month. No limits on daily data volume. Available for VMware, Hyper-V, and Proxmox. The Logmanager Free Plan supports up to 100 GB of storage.—
    More Pricing Information
    Community Pulse
    LogmanagerSplunk Cloud Platform
    Considered Both Products
    Logmanager
    No answer on this topic
    Cisco
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    100%
    Would buy again
    15 Answers
    Delivers good value for the price
    No answers on this topic
    92%
    Delivers good value for the price
    11 Answers
    Happy with the feature set
    No answers on this topic
    100%
    Happy with the feature set
    15 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    91%
    Lived up to sales and marketing promises
    10 Answers
    Implementation went as expected
    No answers on this topic
    100%
    Implementation went as expected
    13 Answers
    Features
    LogmanagerSplunk Cloud Platform
    Security Information and Event Management (SIEM)
    Comparison of Security Information and Event Management (SIEM) features of Logmanager and Splunk Cloud Platform
    Feature
    Logmanager
    -
    Ratings
    Splunk Cloud Platform
    8.2
    20 Ratings
    3% above category average
    Centralized event and log data collection00 Ratings9.019 Ratings
    Correlation00 Ratings8.419 Ratings
    Event and log normalization/management00 Ratings9.220 Ratings
    Deployment flexibility00 Ratings7.220 Ratings
    Integration with Identity and Access Management Tools00 Ratings7.718 Ratings
    Custom dashboards and workspaces00 Ratings8.920 Ratings
    Host and network-based intrusion detection00 Ratings8.117 Ratings
    Data integration/API management00 Ratings7.310 Ratings
    Behavioral analytics and baselining00 Ratings7.28 Ratings
    Rules-based and algorithmic detection thresholds00 Ratings8.210 Ratings
    Response orchestration and automation00 Ratings7.38 Ratings
    Reporting and compliance management00 Ratings8.810 Ratings
    Incident indexing/searching00 Ratings8.711 Ratings
    Best Alternatives
    LogmanagerSplunk Cloud Platform
    Small Businesses
    SolarWinds Papertrail
    Score8.9 out of 10
    No answers on this topic
    Medium-sized Companies
    SolarWinds Kiwi Syslog Server
    Score8.1 out of 10
    IBM Security QRadar SIEM
    Score8.9 out of 10
    Enterprises
    SolarWinds Loggly
    Score7.7 out of 10
    SolarWinds Security Event Manager (SEM)
    Score8.1 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    LogmanagerSplunk Cloud Platform
    Likelihood to Recommend
    -
    (0 ratings)
    8.8
    (21 ratings)
    Likelihood to Renew
    -
    (0 ratings)
    9.1
    (1 ratings)
    Usability
    -
    (0 ratings)
    8.3
    (7 ratings)
    Support Rating
    -
    (0 ratings)
    7.2
    (4 ratings)
    User Testimonials
    LogmanagerSplunk Cloud Platform
    Likelihood to Recommend
    Logmanager
    No answers on this topic
    Cisco
    Splunk is excellent when all your data is in one location. Its ability to correlate all that data is intuitive (once the hurdle of learning the query language is overcome). It is also easy to standardize the presentation of information to the company. When data is siloed/standalone, other systems can be cheaper and faster to implement.
    Incentivized
    Read full review
    Pros
    Logmanager
    No answers on this topic
    Cisco
    • This SIEM consolidates multiple data points and offers several features and benefits, creating custom dashboards and managing alert workflows.
    • Splunk Cloud provides a simple way to have a central monitoring and security solution. Though it does not have a huge learning curve, you should spend some time learning the basics.
    • Splunk Cloud enables me to create and schedule statistical reports on network use for Management.
    Incentivized
    Read full review
    Cons
    Logmanager
    No answers on this topic
    Cisco
    • The SPL programming language that the queries are built in is not very intuitive.
    • There should be a better repository of pre-built queries for what I would think of as common Active Directory usage monitoring.
    • I would like to see more free training/familiarization information made available.
    Incentivized
    Read full review
    Likelihood to Renew
    Logmanager
    No answers on this topic
    Cisco
    Ease of use and have all the features we need
    Incentivized
    Read full review
    Usability
    Logmanager
    No answers on this topic
    Cisco
    Splunk AI Assistant for SPL is good tool, as I said, it is really useful for educational purpose, taking in its hands small and simple tasks (ex:small query dashboard,...), but it's not a ten because the contextual memory for complex issues/dashboarding/reports etc can be limited, and can sometime suggets none optimized query which are not always checked by teammates and can cause issue on the long term.
    Incentivized
    Read full review
    Support Rating
    Logmanager
    No answers on this topic
    Cisco
    Splunk Cloud support is sorely lacking unfortunately. The portal where you submit tickets is not very good and is lacking polish. Tickets are left for days without any updates and when chased it is only sometimes you get a reply back. I get the feeling the support team are very understaffed and have far too much going on. From what I know, Splunk is aware of this and seem to be trying to remedy it.
    Incentivized
    Read full review
    Alternatives Considered
    Logmanager
    No answers on this topic
    Cisco
    Vs elastic: - SPL's statistical functions superior to KQL for complex correlations - Better enterprise support, less operational overhead - Splunk Cloud Platform's detection engineering more mature vs Sentinel: - SPL more powerful than KQL for custom analytics - Better cross-platform visibility (non-Azure environments) vs Datadog - SPL enables deeper forensic Investigations - Superior compliance/audit capabilities
    Incentivized
    Read full review
    Return on Investment
    Logmanager
    No answers on this topic
    Cisco
    • End-end visibility across your departmental silos
    • Strengthen the overall global monitoring posture
    • Move from Reactive to Proactive Monitoring
    • Highly secure environment at your finger-tips
    • Takes you away from managing infrastructure/administration, allows saving time & money. Reduce the overall TCO (Total Cost of Ownership)
    Incentivized
    Read full review
    ScreenShots

    Logmanager Screenshots

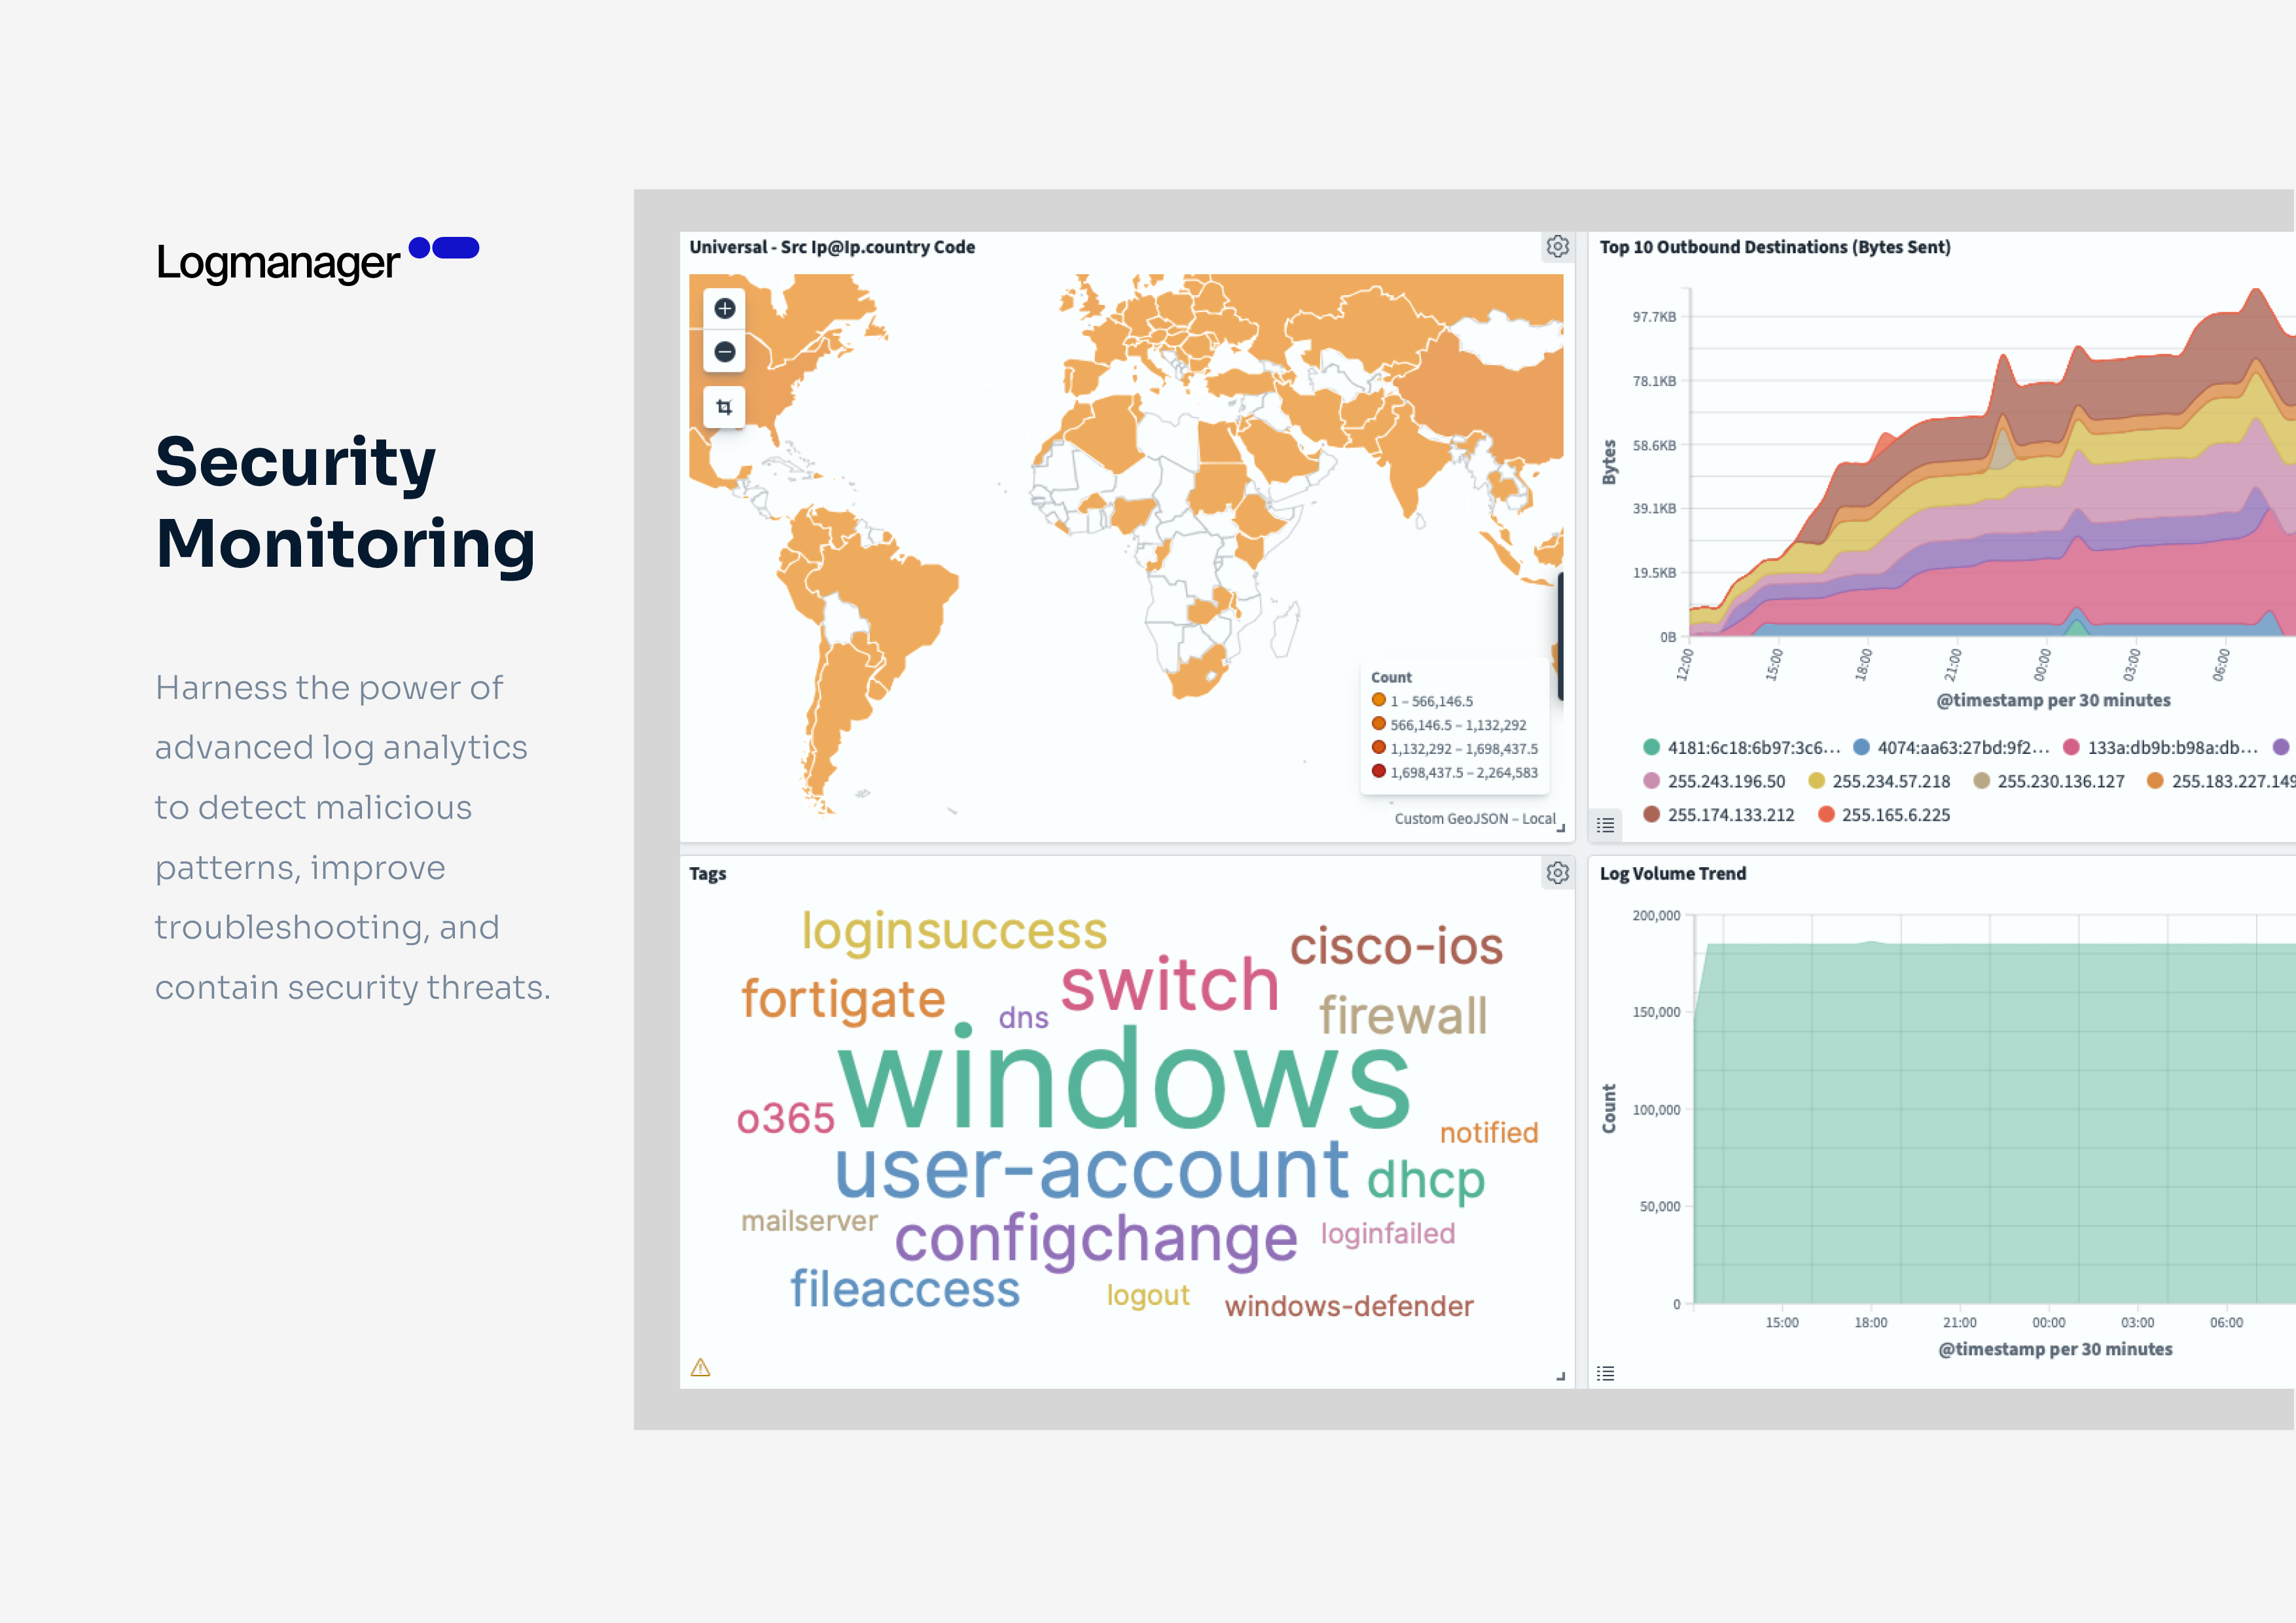
    Screenshot of The dashboard. Logmanager features 140+ built-in parsers for technologies like firewalls, networking devices, and EDR. It also features connectors for Windows, SQL, Microsoft 365, and Linux, with support for formats such as CEF, LEEF, and JSON. Through consistent log normalization, all data is presented in a unified visualization pane as shown, to give operators the information they need at a glance.Screenshot of How Logmanager ensures secure, long-term retention of log data for forensic analysis and compliance. It helps meet cybersecurity regulations like GDPR and NIS2, industry standards such as HIPAA, and frameworks like ISO 27001.Screenshot of Where to query and filter log files by host, device, or any other tag with natural query language. Specific security events can be analyzed, or patterns in context through log enrichment.Screenshot of The advanced log analytics that help detect malicious patterns, improve troubleshooting, and contain security threats.Screenshot of An out-of-the-box reporting template. Reports can be generated based on dashboard templates.Screenshot of Some of the dozens of predefined dashboards available. These offer insights into log data trends, system performance, security events, and compliance status.