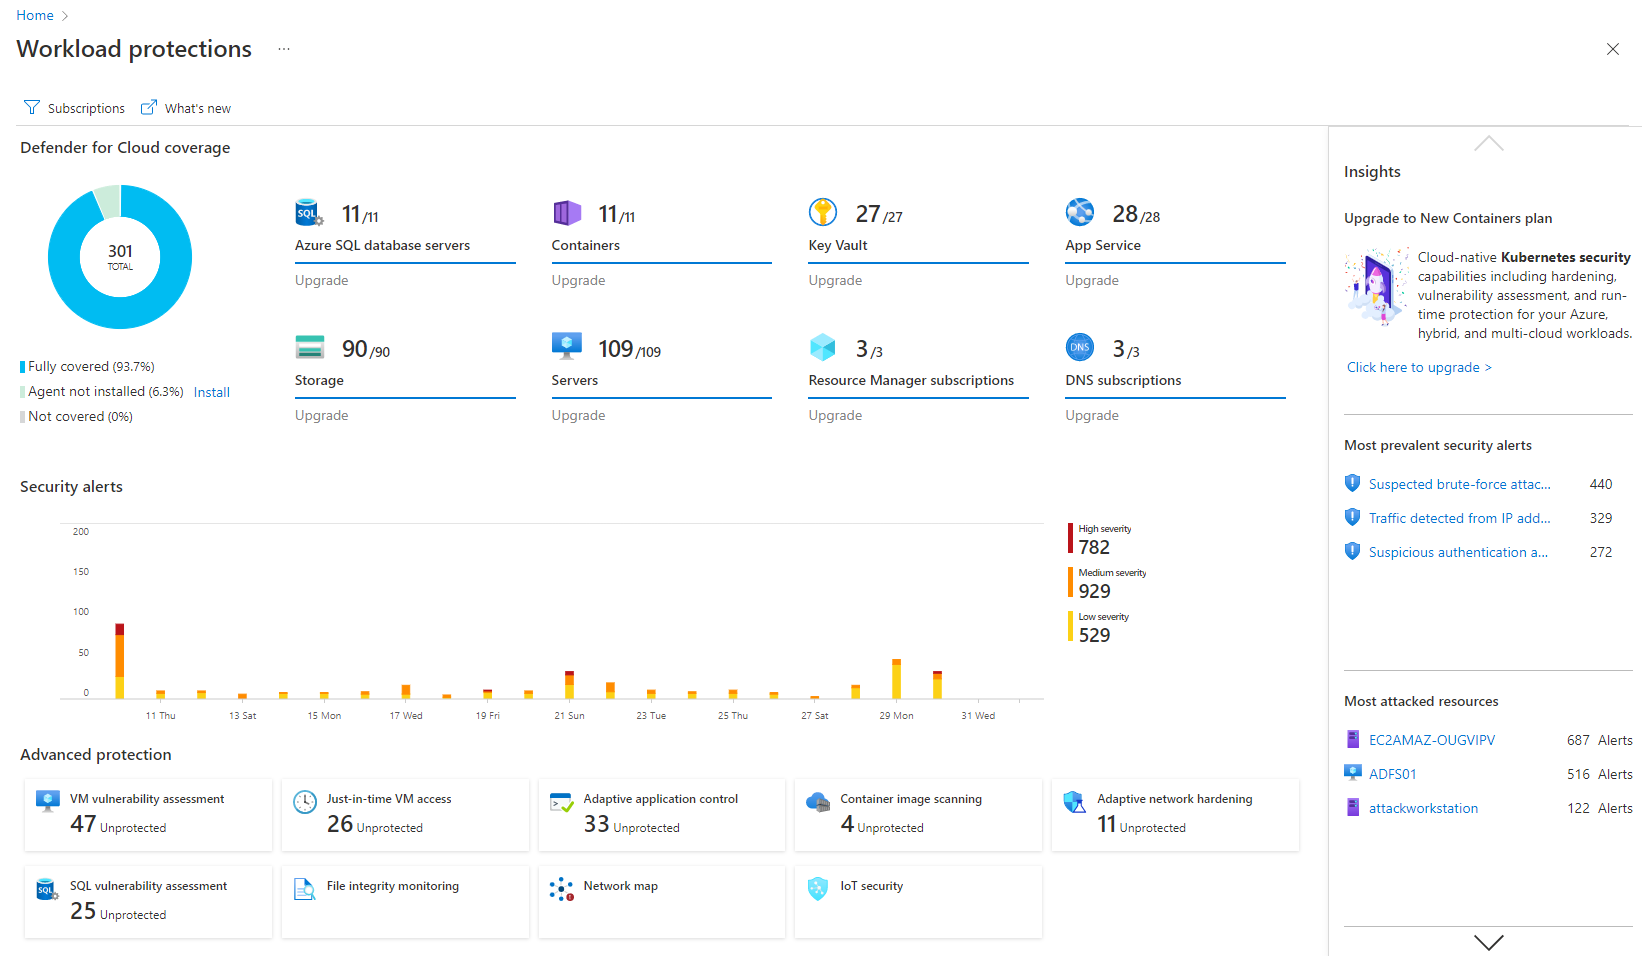
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
N/A
Microsoft Defender for Cloud Apps
Score7.8 out of 10
N/A
Microsoft Defender for Cloud Apps (formerly Microsoft Cloud App Security) is a multimode cloud access security broker.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Cloud Apps is well suited when working with other Microsoft Applications. For example, if you are working with Microsoft Office 365 it works very well when implementing CASB features. It works when implementing monitoring or blocks on Sanctioned applications however customizing the message to users is not that great.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The integration to Microsoft Entra ID is seamless, which allows Conditional Access to redirect the session to Microsoft Defender for Cloud App for it to take actions (Block or Monitor).
Tracker users' activity is very good when troubleshooting or running an investigate.
Detecting risky users through tight integration with Microsoft Entra ID is a very good feature.
Detecting mass downloads and blocking the download of files from non-manage company devices is a very good feature as well.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It takes some time to scan and apply the policies when there is some sensitive information.
After it applies the policies, it works, but there is a delay.
It doesn't provide any way to scan Microsoft Teams when an external exchange of images is happening. You can always do the filtering on the documents during the chat, but if there is an image, then some kind of OCR capability is required to detect it. At present, there is no way [Microsoft Cloud App Security] can go and detect those kinds of images and alert us
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The interface is pretty simple and easy to use; however, you will need to do a lot of investigative research on your own to get comfortable with it. Originally, many of the Microsoft security tools had their own seperate consoles. Overtime, they have blended into one interface which is the ideal state. In some cases it is clear Microsoft had to pick which console a certain feature or setting was going to reside in and this leads to some confusion. For example, DLP is managed through Defender for Cloud Apps but you will also need to jump into Purview. For things like reverse proxy on your M365 tenant, you will need to go into Azure and setup conditional access rules. Not a big problem and I can understand why the settings are located where they are but for someone just starting out with Defender for Cloud Apps, it will take some time to figure out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have not utilized actual support but the Sales and Product teams have been super helpful in moving our implementation forward and showing us the best practices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
More flexible and more features with easy integration with cloud services like Microsoft Azure and other cloud services. Overall both gives similar features but we prefer Microsoft cloud app security due to its high threat detection rate. mostly we have been able to stop the threat in very very less time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cloud App Security saves us thousands of dollars finding and rectifying apps security issues
Identity Security Posture helps the organization identity stay in shape, saving thousands of dollars on security consultations
The cost of suffering a breach cannot be quantified, CAS helps minimize the chances of the attackers succeeding, with excellent historical logging for most operations
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info