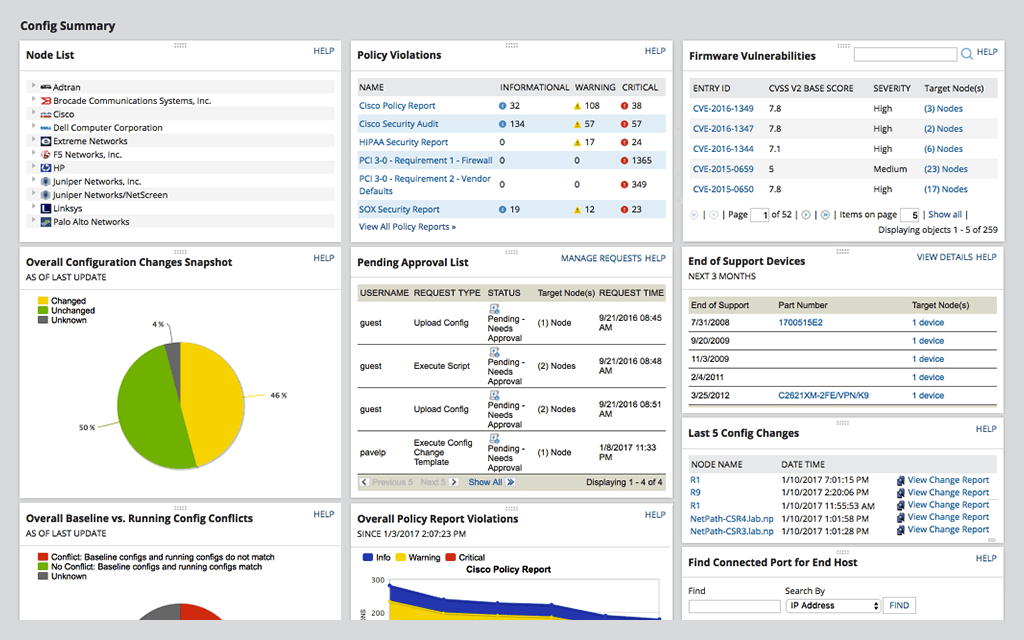
SolarWinds Network Configuration Manager is network diagnostics and troubleshooting technology, from Austin-based SolarWinds.
N/A
Tenable Nessus
Score8.8 out of 10
N/A
Tenable headquartered in Columbia offers Nessus, a vulnerability scanning and security assessment solution used to analyze an entity's security posture, vulnerability testing, and provide configuration assessments.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Network Configuration Manager is well suited for backing up configurations of all your devices. It also has a great comparison tool for seeing only the differences in config. Another great feature is it's ability to push a script to any number of devices. This is very handy for pushing changes to one, 10 or multiple devices. There are also some great reports that you can run against the devices in inventory
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is an excellent tool for scanning servers, workstations, and network devices to identify missing patches and misconfiguration; we regularly use it to confirm patch effectiveness after the update; it also helps us for preparing audits such as iso 27001, and regulatory requirements, it also helps us to identify open ports and services that violate security.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Nessus is best at performing vulnerability scans, in fact, it gives findings and moreover accurate findings of the assessments. It does not do penetration testing or exploit the vulnerabilities because it is concerned about scanning the systems/applications.
In fact, Nessus has multiple profiles/policies to perform different types of scans such as, scans oriented for PCI-DSS, malware scans, web application scans, bad shell shock detection scan to name a few.
Nessus has the ability to classify the vulnerabilities into risk-based categories from critical to even informational which I think is one of the things that separates Nessus from other vulnerability scanners.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For our use case, it does everything great and some of the features we underutilize but I would like to be able to set a configuration baseline when initially adding a node instead of after the configuration is pulled but it's not a particularly big deal to let it pull the configuration then set it as the baseline.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The tool has lots of options for setting up before scanning any device, this methodology could be simplified further with default configuration for various devices predefined, anyhow we can use this technique by making use of policies.
For advanced users we cannot disable the plugins inside the plugin groups, we can enable the whole set of plugins at a time, for few hundreds its ok, but thousands of plugins are of waste of resource and time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Medium complexity to set up in the beginning if using any non-standard devices or configurations, else fairly easy (e.g. Cisco Nexus or IOS-based devices). Reports are fairly straightforward to set up. Updates to the platform are fairly straightforward and don't take a major effort. Easy to add or remove devices.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Nessus is best and easy to use application for Vulnerabilities finding and reporting, it has multiple platforms and wide scope covering almost all devices for security improvement so far, thus we are very likely to continue its services.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The user interface is lacking. It is difficult to navigate at times and things can be done multiple ways. Quite often I am confused by how their notification structure works. It is not very intuitive. They do offer a free Academy. They also offer a community of other technical folks. I have enjoyed both.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Tenable Nessus is a great product and provides a lot of value, but it is difficult to set up and use and the amount of data it generates can be overwhelming. It does help us prioritize based on the severity of the detection, however there are sometimes mitigating factors that we have implemented that Nessus does not account for, which causes lots of noise in the reports.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
To be fair, I have not had to involve Support in a number of years, but when I did, I was greeted with enthusiastic engineers who wanted to understand and solve the issue. It was a fairly complex scenario and I have discovered in my most recent implementation that engineering included that option as a standard now.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I haven't needed to contact support yet. But issues are easily solved with a quick internet search which means support and by extension, the larger community are involved and knowledgeable.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Solarwinds has actually produced new training since I last used it that is available on their site at any time. Their previous training was more than enough to get us started but now there is significantly more content. Since I'm comfortable with the Orion platform and the products we use I haven't checked the new training out yet but we have new staff go through portions of that training and they always come away with an understanding of the platform and ready to use it
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
it was a fairly easy implementation and everything was pretty straightforward. only challenge we had was getting all the snmp communities updated on the networking equipment
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
At the time SolarWinds was the biggest player in the space and their whole portfolio was very comprehensive. As time progressed and newer technologies came about (i.e. SDWAN) their products couldn't keep up with the consumer demands and changing market. Security became such a big focus that once Solarwinds got hacked we had to remove all their products from our environment
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Sometimes when we identify a vulnerability with Nessus that has an exploit, we made a proof of concept with Metasploit in order to show to the IT managers the importance of the software/hardware hardening.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Saves 100s of hours a year in man hours over manual configuration.
Saved easily 50k in lost revenue when a switch rebooted with months old unsaved configuration. NCM let us quickly restore a snapshot of the running config from the previous day.
Saves us several man hours per week of config auditing by reducing all changes to a summary email.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Nessus certainly has a positive impact while me while performing my job, either as security research, or performing vulnerability assessments for clients. It gives a lot of information about the system/application after performing scans. The number of false positives is also less compared to other vulnerability scanners.
The professional edition is very useful as policy templates available in this edition are very handy and useful even to perform compliance scan like PCI DSS scan.
Also, the ability to export the scan results into reports in formats like HTML, PDF is very useful which could be for performing system/application reviews.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info