
Microsoft Sentinel vs. Trellix Helix
Microsoft Sentinel vs. Trellix Helix
| Product | Rating | Most Used By | Product Summary | Starting Price |
|---|---|---|---|---|
 Microsoft Sentinel | N/A | Microsoft Sentinel (formerly Azure Sentinel) is designed as a birds-eye view across the enterprise. It is presented as a security information and event management (SIEM) solution for proactive threat detection, investigation, and response. | $2.46 per GB ingested | |
 Trellix Helix | Enterprise companies (1,001+ employees) | Trellix Helix (formerly FireEye Helix) is a SIEM solution providing a non-malware threat detection solution. | $0 Events per second |
| Microsoft Sentinel | Trellix Helix | |||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| Editions & Modules |
|
| ||||||||||||||
| Offerings |
| |||||||||||||||
| Entry-level Setup Fee | No setup fee | Optional | ||||||||||||||
| Additional Details | — | — | ||||||||||||||
| More Pricing Information | ||||||||||||||||
| Microsoft Sentinel | Trellix Helix |
|---|
| Microsoft Sentinel | Trellix Helix | ||||||||||||||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| Security Information and Event Management (SIEM) |
|
| Microsoft Sentinel | Trellix Helix | |
|---|---|---|
| Small Businesses |  LevelBlue USM Anywhere Score 8.3 out of 10 | LevelBlue USM Anywhere Score 8.3 out of 10 |
| Medium-sized Companies |  Sumo Logic Score 8.9 out of 10 | Sumo Logic Score 8.9 out of 10 |
| Enterprises | Sumo Logic Score 8.9 out of 10 | Sumo Logic Score 8.9 out of 10 |
| All Alternatives | View all alternatives | View all alternatives |
| Microsoft Sentinel | Trellix Helix | |
|---|---|---|
| Likelihood to Recommend | 8.5 (74 ratings) | 9.8 (3 ratings) |
| Likelihood to Renew | 6.5 (2 ratings) | - (0 ratings) |
| Usability | 8.2 (27 ratings) | - (0 ratings) |
| Support Rating | 8.0 (3 ratings) | 9.0 (1 ratings) |
| Ease of integration | - (0 ratings) | 9.8 (3 ratings) |
| Professional Services | 5.0 (1 ratings) | - (0 ratings) |
| Microsoft Sentinel | Trellix Helix | |
|---|---|---|
| Likelihood to Recommend | Microsoft
 Andrew Stowell Data Engineer |  Trellix (Musarubra US LLC)
 Shirleen Muraya Branch Manager |
| Pros | Microsoft
| Trellix (Musarubra US LLC)
|
| Cons | Microsoft
| Trellix (Musarubra US LLC)
|
| Likelihood to Renew | Microsoft
| Trellix (Musarubra US LLC) No answers on this topic |
| Usability | Microsoft
| Trellix (Musarubra US LLC) No answers on this topic |
| Support Rating | Microsoft
 Flavio Pereira Analista de sistemas | Trellix (Musarubra US LLC)
|
| Alternatives Considered | Microsoft
| Trellix (Musarubra US LLC)
Shirleen Muraya Branch Manager |
| Professional Services | Microsoft
| Trellix (Musarubra US LLC) No answers on this topic |
| Return on Investment | Microsoft
| Trellix (Musarubra US LLC)
Shirleen Muraya Branch Manager |
| ScreenShots | Microsoft Sentinel Screenshots   | Trellix Helix Screenshots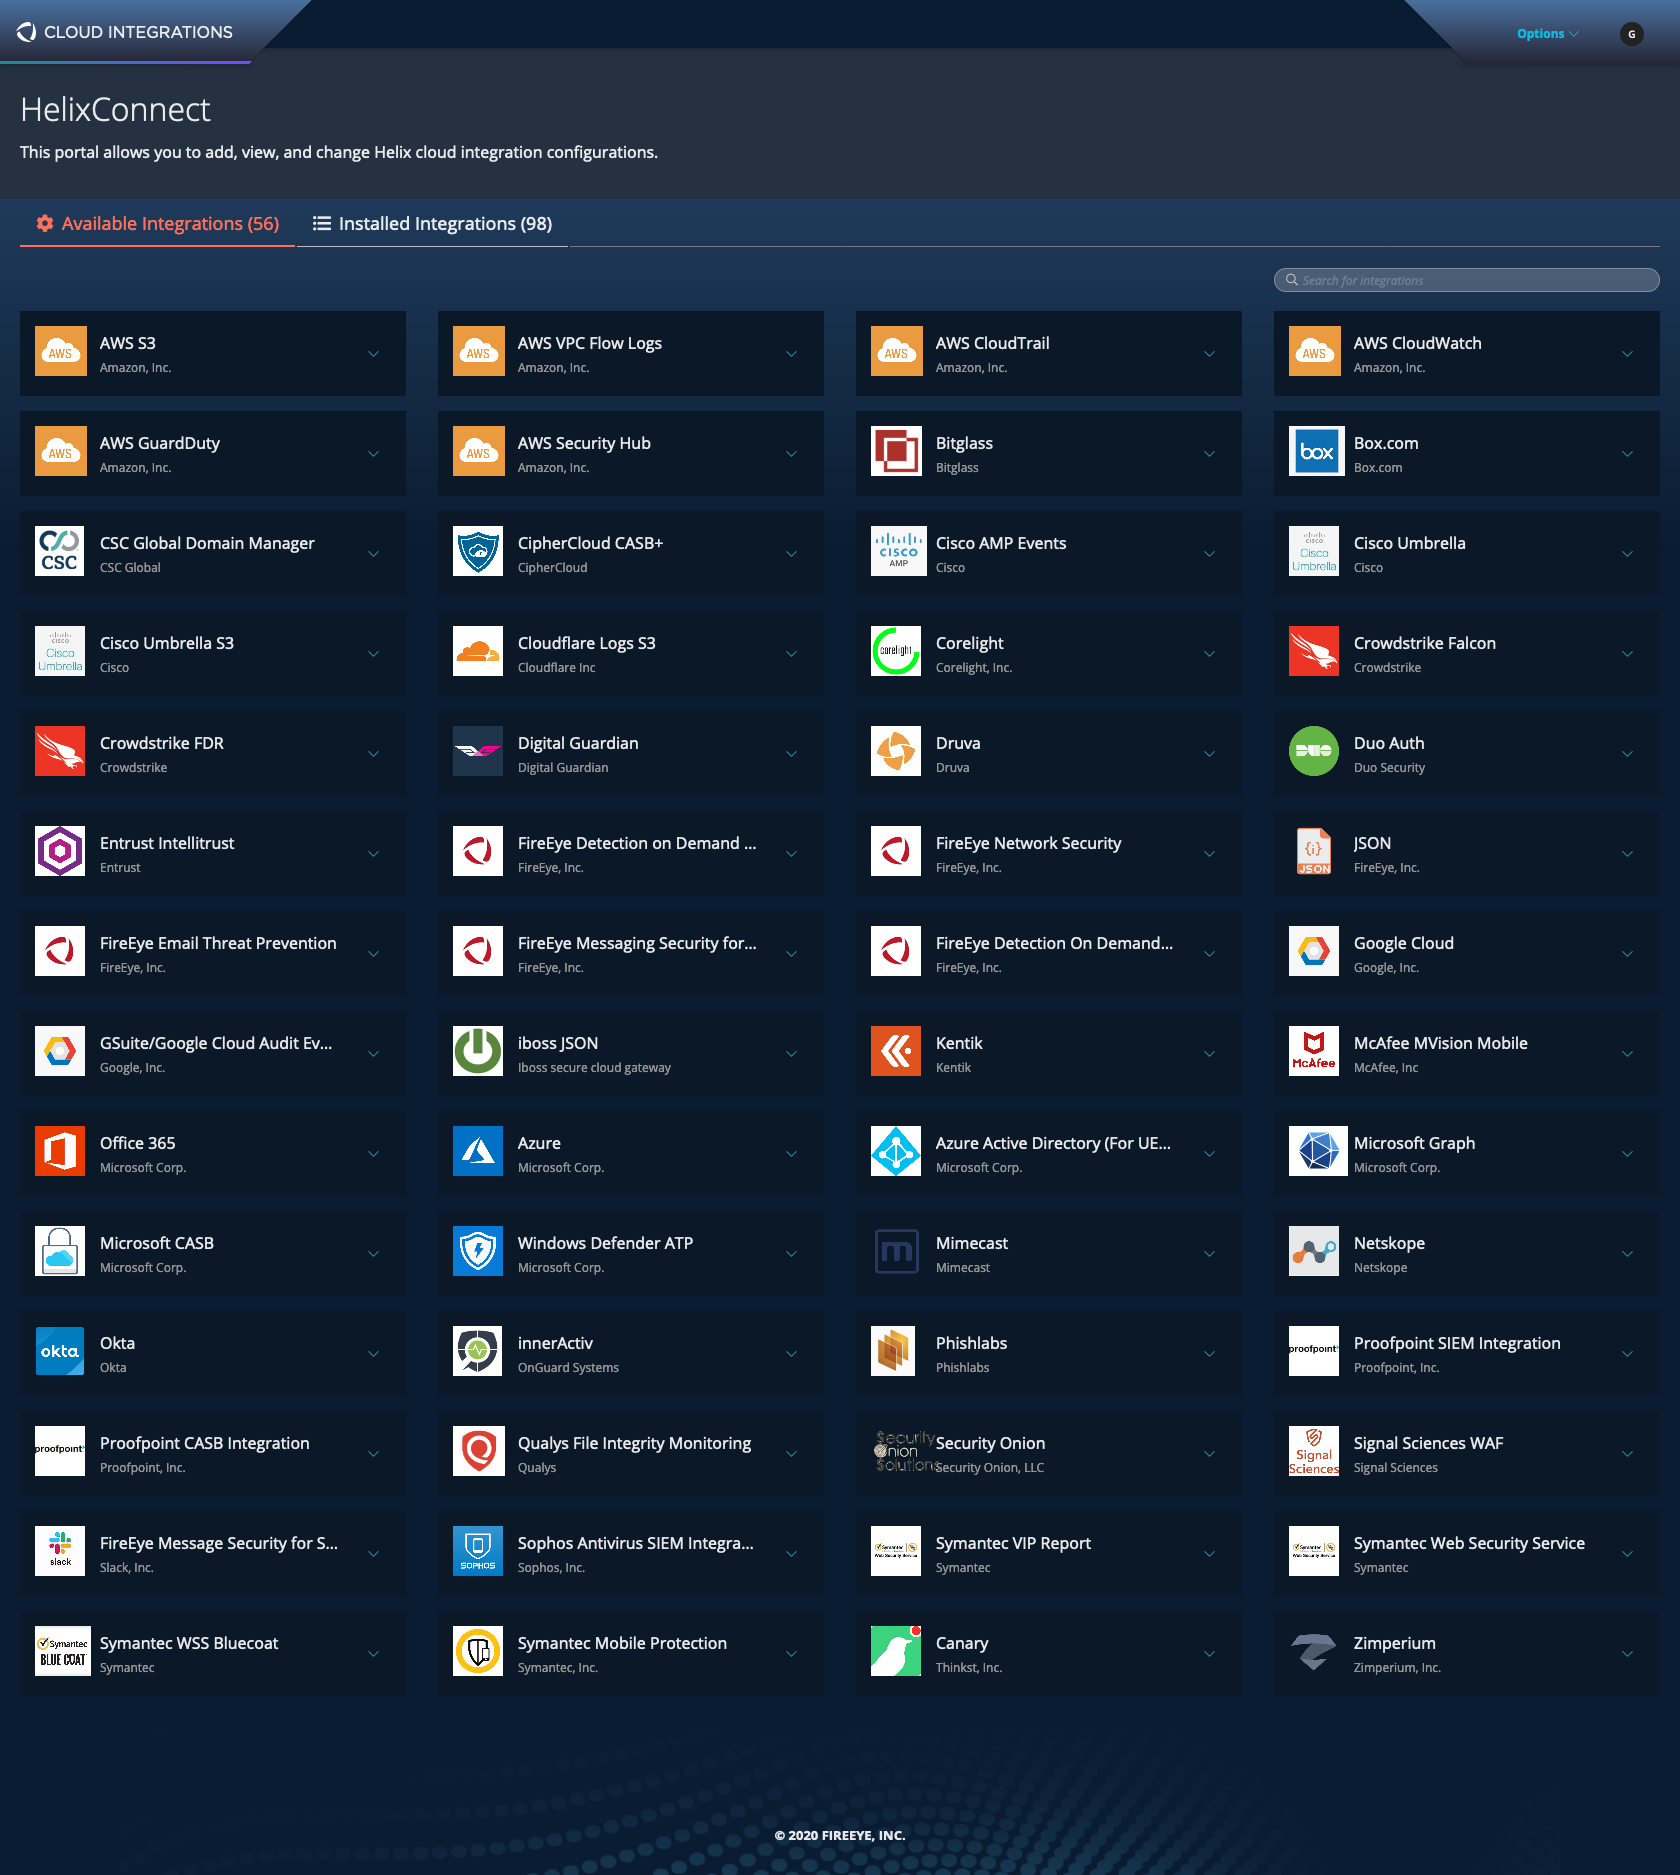  |