TrustRadius: an HG Insights company

AgileBlue

Score8.2 out of 10

22 Reviews and Ratings

What is AgileBlue?

AgileBlue's SecOps platform autonomously detects, investigates, and responds to cyber threats across endpoints, cloud, and network. AgileBlue is offered for the mid market, and for these companies is designed to deliver all-in-one protection, integration, and a partnership so organizations can move from reactive defense to proactive resilience.

Media

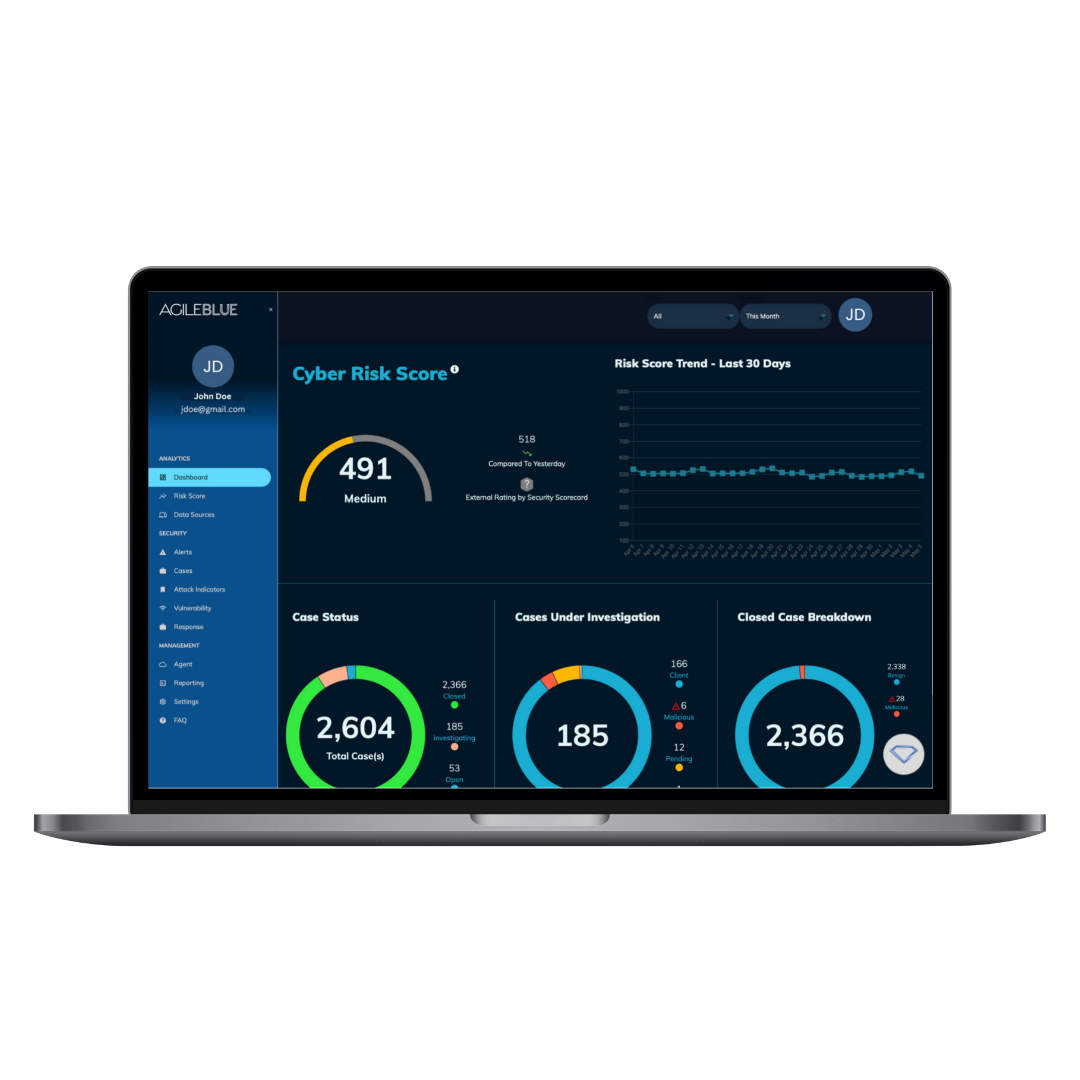
Screenshot of the AgileBlue main dashboard
Screenshot of AgileBlue alert types
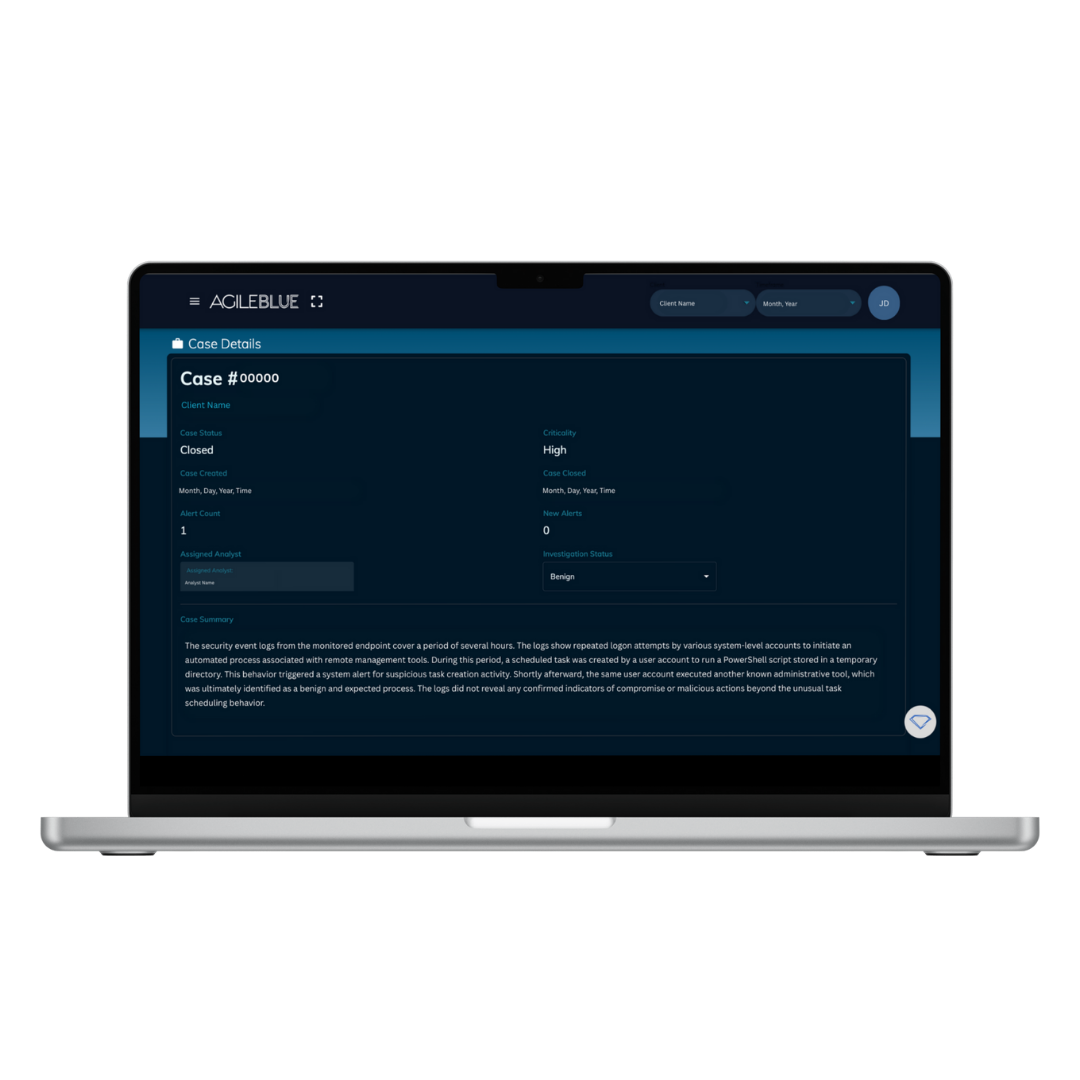
Screenshot of AgileBlue AI case summary
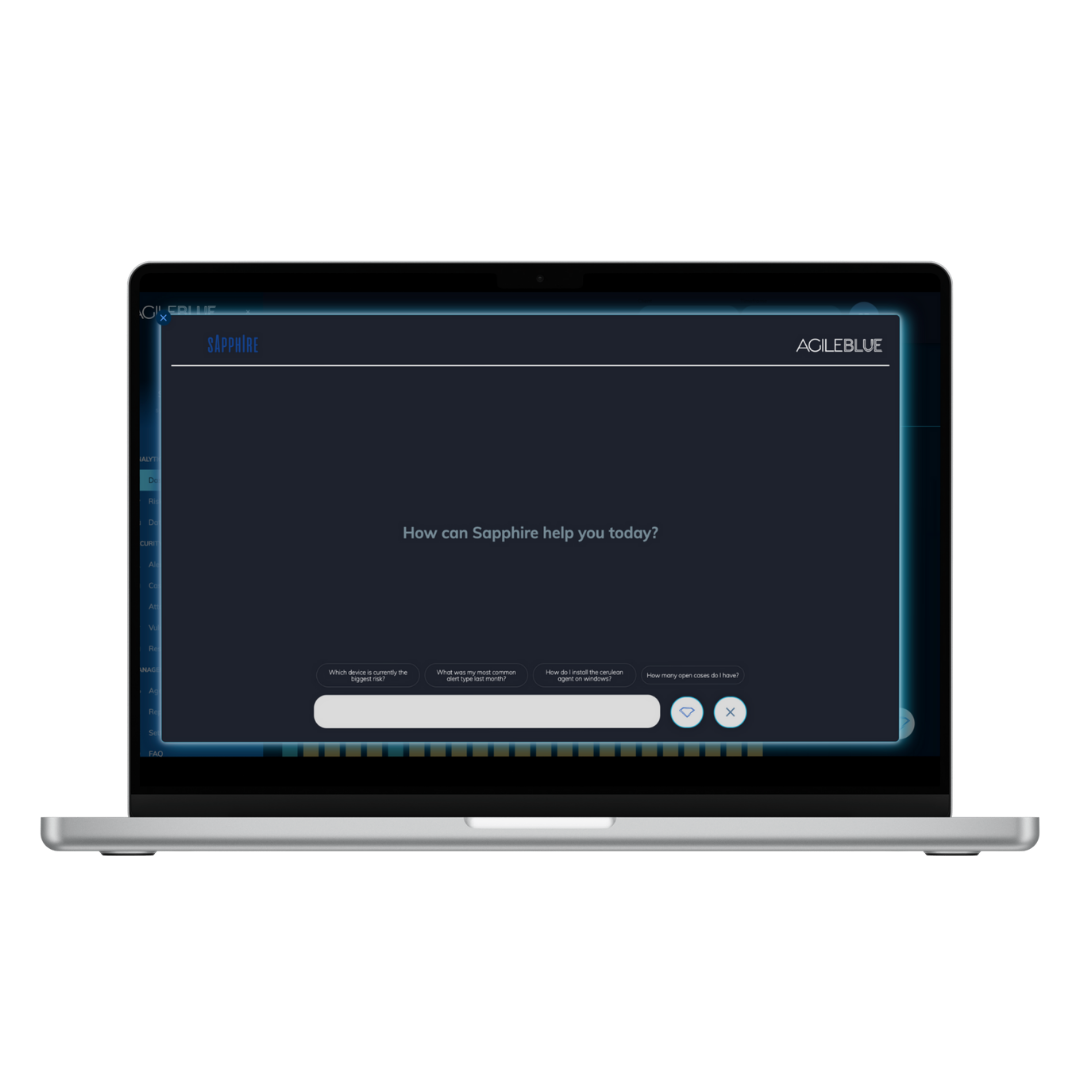
Screenshot of Sapphire AI SOC analyst
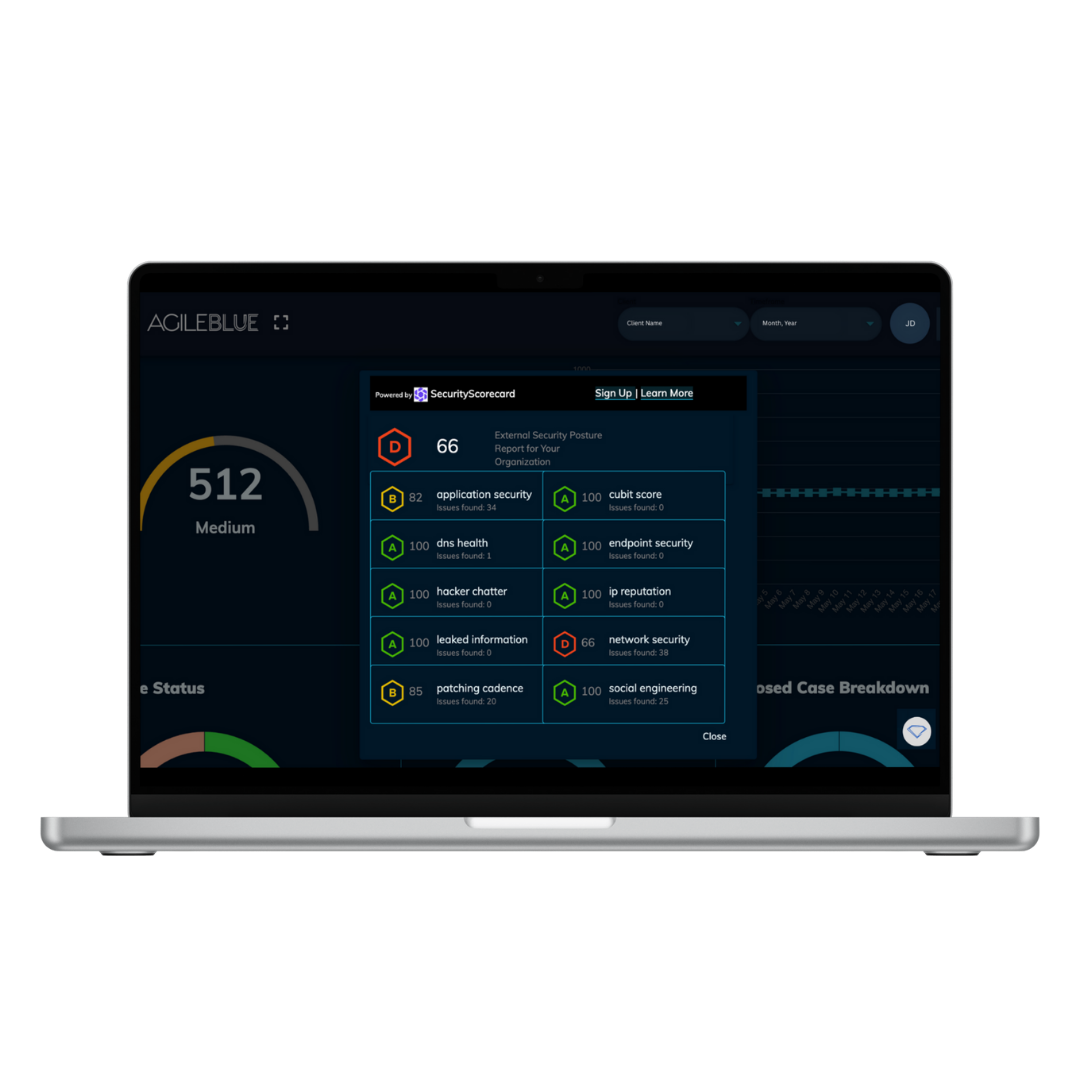
Screenshot of AgileBlue internal risk scoring

1 / 5

Screenshot of the AgileBlue main dashboard

Pros

  • Rapid threat identification and response speed
  • Proactive communication and regular updates (monthly/quarterly)
  • Straightforward security incident management and system configuration

Cons

  • Agent stability issues, particularly with syslog integration
  • UI/UX refinements needed, including web interface and expanded scanning capabilities
  • Overly technical communication and inconsistent account manager check-ins

AgileBlue Supports Small IT Teams

Use Cases and Deployment Scope

We are a small company with limited IT staff. AgileBlue is a single source solution that provides end point security and 10,000 foot overview of your corporate security. We have had a couple issues with processes being identified as malicious but with the help of support - we have whitelisted those. So initial setup you want to be cautious installing the agents.

The Nodeware part of the solution is very helpful for managing OS Updates and seeing vulnerabilities on your network. As well as the AI notifications of employee activities.

Overall, for a small IT team this has been a solid solution for us.

Pros

  • End point management
  • OS/Application Updates and Vulnerabilities
  • Notifications of possible IT related issues

Cons

  • Ability for IT to easily turn on/off blocking of apps/installations
  • Better OS Update integration - reporting - current status
  • Pricing - accurate license counts

Return on Investment

  • Peace of mind
  • Awareness of Employee Actions / Risks
  • High Level Review of OS Updates

Usability

Other Software Used

Veeam Data Platform

Great Product

Use Cases and Deployment Scope

We use AgileBlue as a SIEM tonotify us of any actions that are taking place in our network. A few examples would be account creation, installing or uninstalling applications, or any other potential malicious activity.

Pros

  • Notifying us of potentially harmful events
  • The ease in which to respond to cases
  • Monthly meetings to update us on new features, etc.

Cons

  • Response Time
  • N/A
  • N/A

Return on Investment

  • It has made our network more secure
  • Gives us better insight into events that could potentially impact our network

Usability

Other Software Used

Notepad++, OneNote

AgileBlue MSSP Review.

Use Cases and Deployment Scope

AgileBlue provides Managed Security Services, including L1 and L2 SOC, Threat Intelligence, Email Security, Vulnerability Management, and Security Engineering. It covers all security operations, integration with the company's L3 support, ingestion of SIEM logs, and includes additional services such as EDR licenses. The AgileBlue SOC engine runs on a proprietary AI platform that creates cases from logs and telemetry ingested by our platforms and provides periodic reports and KPIs.

Pros

  • Agentic SOC for L1 and L2 detection and case analysis.
  • EDR support included with their endpoint monitoring.
  • SIEM support with ingestion of multiple sources.

Cons

  • Vulnerability Management support.
  • Threat Intelligence process to cover specific markets.
  • Playbooks to automate incident responses.

Return on Investment

  • Positive: great support and TAM, less hassle with L1/L2 analysis, improved KPIs.
  • Negative: focus efforts on the Threat Intelligence process, which requires an additional tool to maintain adequate coverage.

Usability

Other Software Used

Google Threat Intelligence (Mandiant)

AgileBlue is the best XDR platform I have ever utilized

Use Cases and Deployment Scope

AgileBlue helps to keep our network, endpoints and all devices secure and security patches up to date. It detects malicious activity and alerts us to anomalies that are found in our network. It has been an invaluable addition to our suite of tools and the best XDR tool we have utilized to date.

Pros

  • AgileBlue is constantly monitoring our environment for cybersecurity threats and responds to those threats with a combination of AI and human security analysts.
  • AgileBlue combines SIEM, SOAR XDR, Vulnerability management and M365 monitoring in one single tool.
  • Onboarding was done particularly well. Having utilized several services in the past, the transition to AgileBlue was handled in white-glove fashion.

Cons

  • AgileBlue could have more user friendly options for AI management in our environment.

Return on Investment

  • The transition from SecureWorks to AgileBlue provided us a significant cost-savings and gave us a broader feature set.

Usability

Alternatives Considered

Secureworks Managed Security Services, Bitdefender Managed Detection and Response (MDR), Arctic Wolf Managed Detection and Response, Microsoft Defender XDR and Microsoft Defender Vulnerability Management

Other Software Used

NinjaOne, Lansweeper, SurePoint Legal Management System (LMS)

An Agile SaaS leaving you not so Blue

Use Cases and Deployment Scope

AgileBlue helps our organization monitor and address gaps in our existing security stack. We have AgileBlue connected to all of our SaaS applications that control identity, security, and logging which allows our IT team to focus on other tasks and projects instead of micro-managing these platforms. In addition to that, we utilize the vulnerability scanning aspect of the platform to help inform patch management decisions; saving both time and attention for our team.

Pros

  • Machine level monitoring
  • Fast response and triage
  • Stack connections and integrations

Cons

  • Self-service integration managment
  • More detailed agent management or features
  • Backup POCs or a published escalation chain for critical events

Return on Investment

  • Allowing our IT staff more time to focus on user needs
  • Integrate well with our existing SECaaS providers for gap coverage and escalation

Usability

Alternatives Considered

SentinelOne Singularity

Other Software Used

SentinelOne Singularity, Cisco Duo, Cisco Umbrella, Cisco Meraki MX