

Diras
What is Diras?
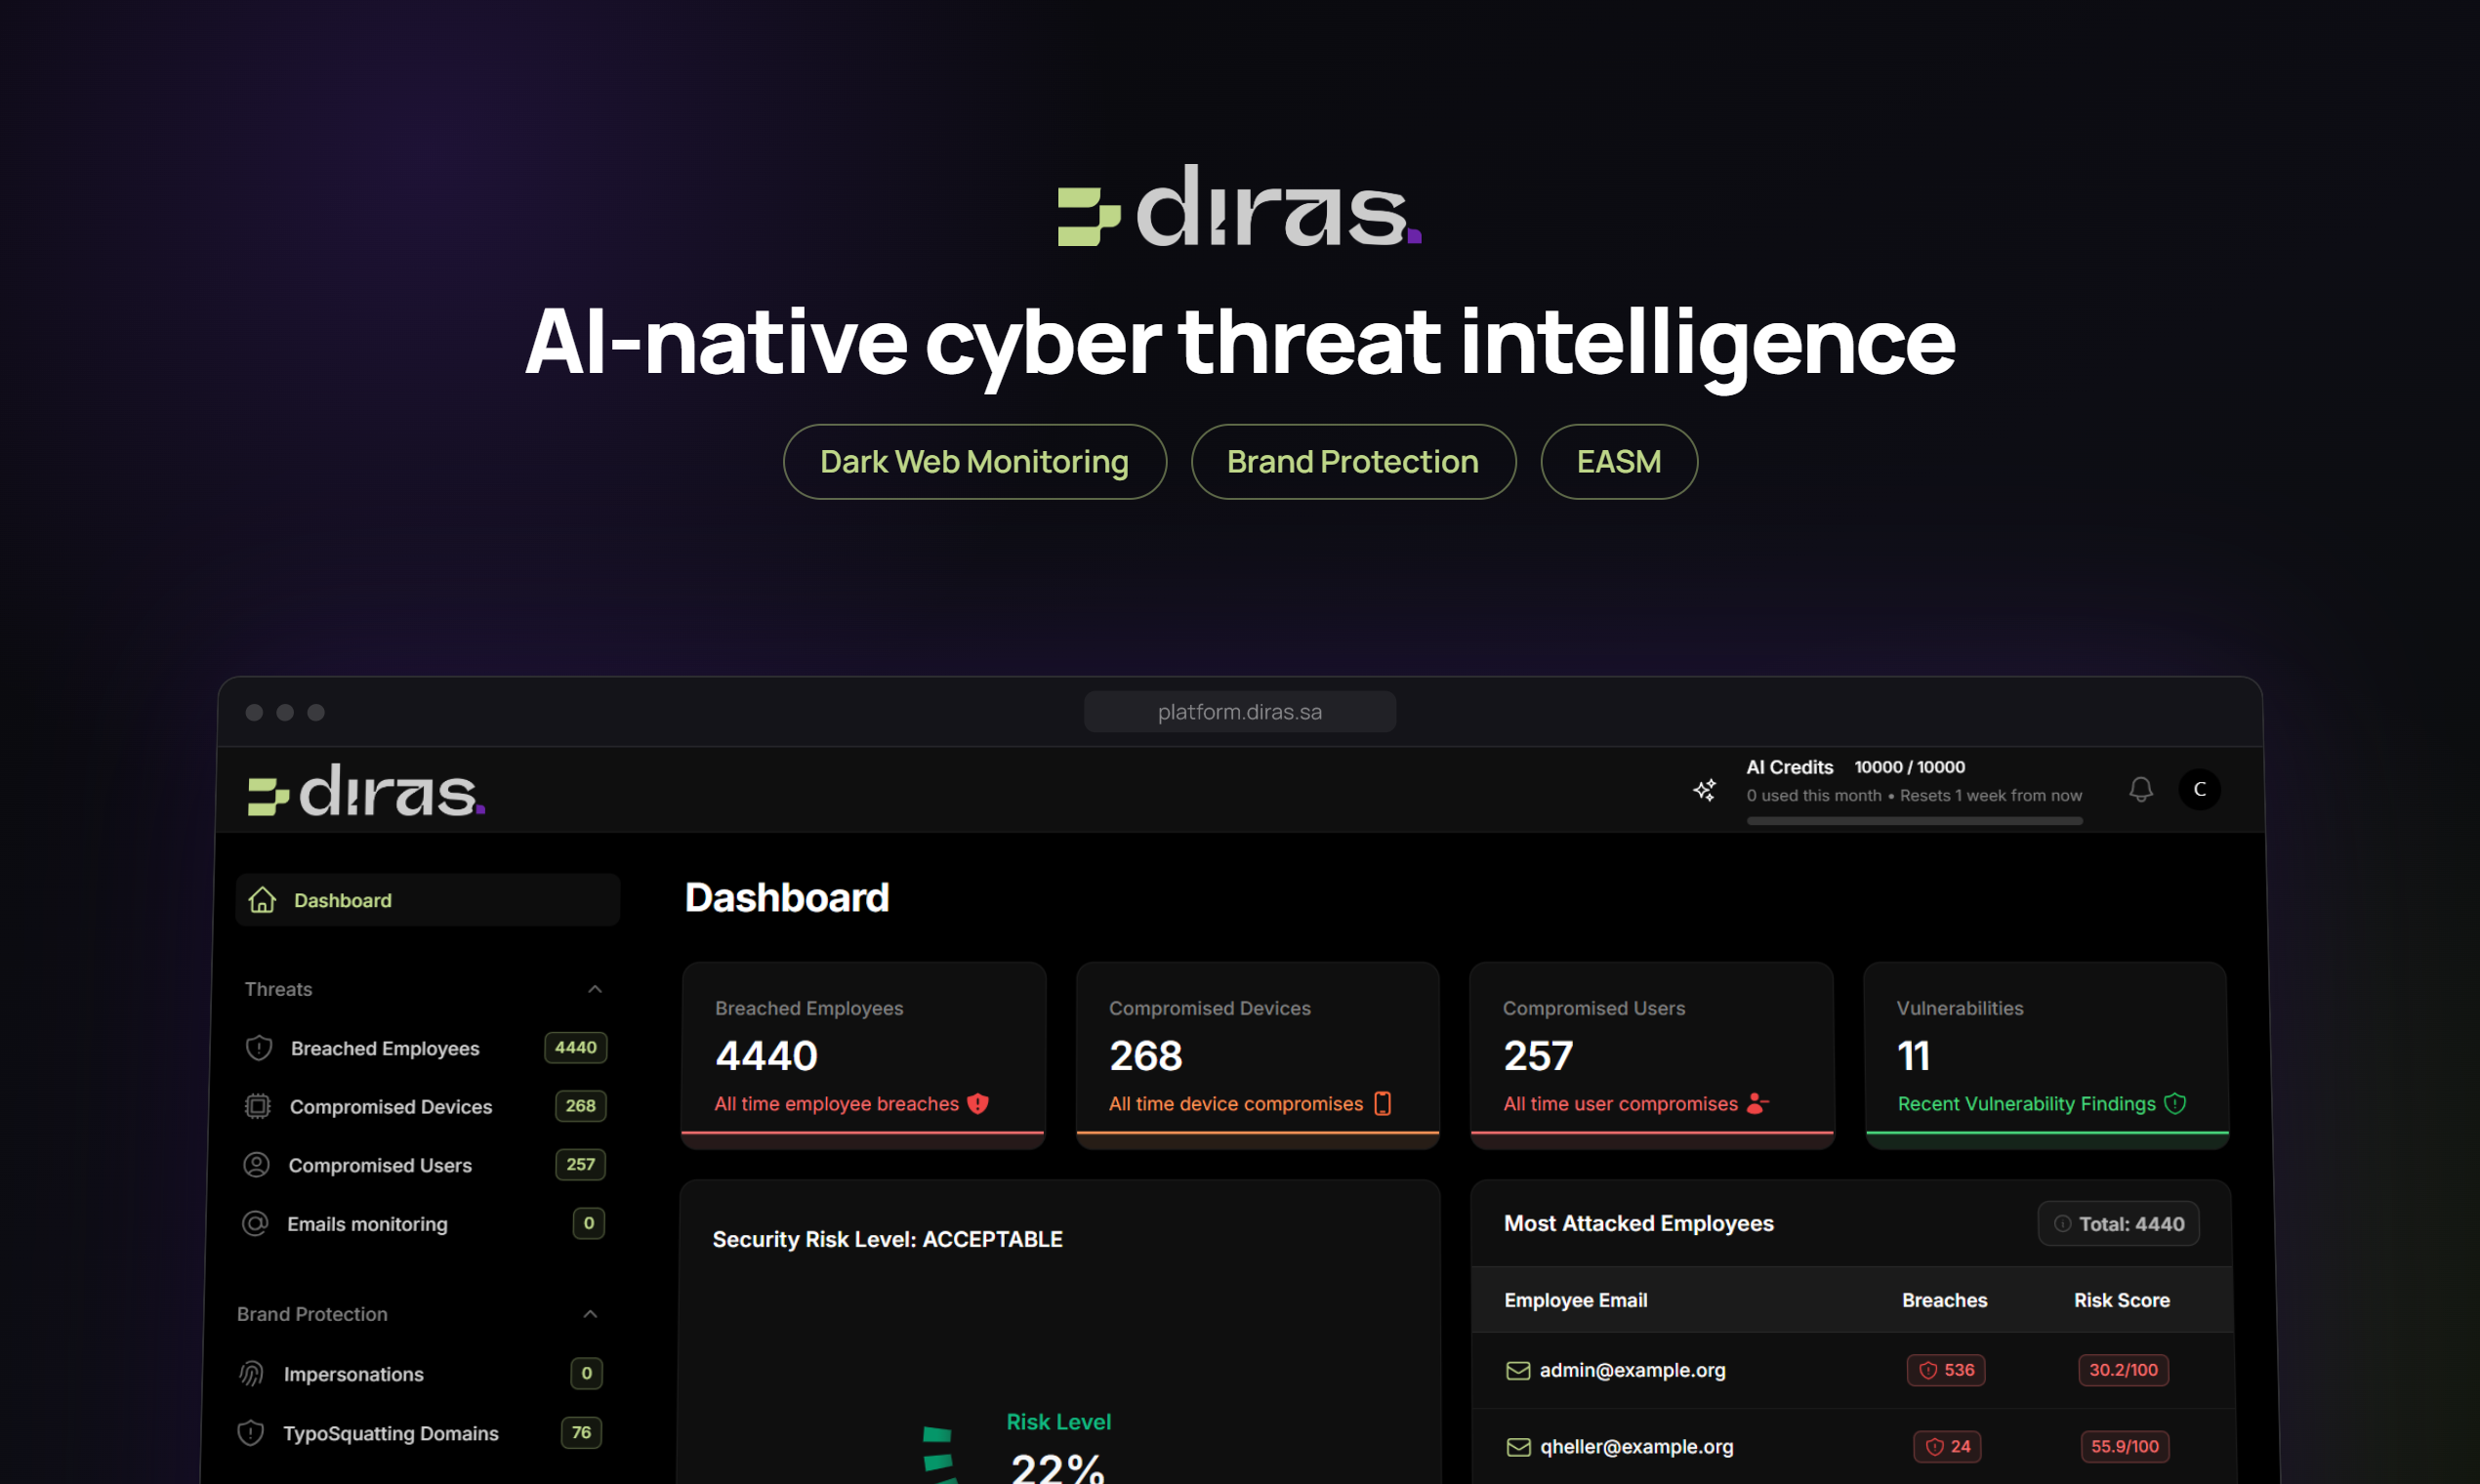
Diras is a Threat Intelligence platform that helps security teams identify exposed credentials, brand impersonation, and risks affecting internet-facing assets. It combines dark web monitoring, brand protection, and external attack surface management in a shared dashboard; available capabilities vary by plan.
Dark web monitoring checks breach dumps, infostealer logs, paste sites, forums, and underground markets for exposed employee or customer credentials, compromised devices, and company data. Alerts include contextual risk information, while sensitive password values remain masked.
Brand protection detects typosquatting domains and social media accounts impersonating an organization or its executives. A managed takedown workflow allows Diras analysts to collect evidence, submit removal requests, and track cases through completion.
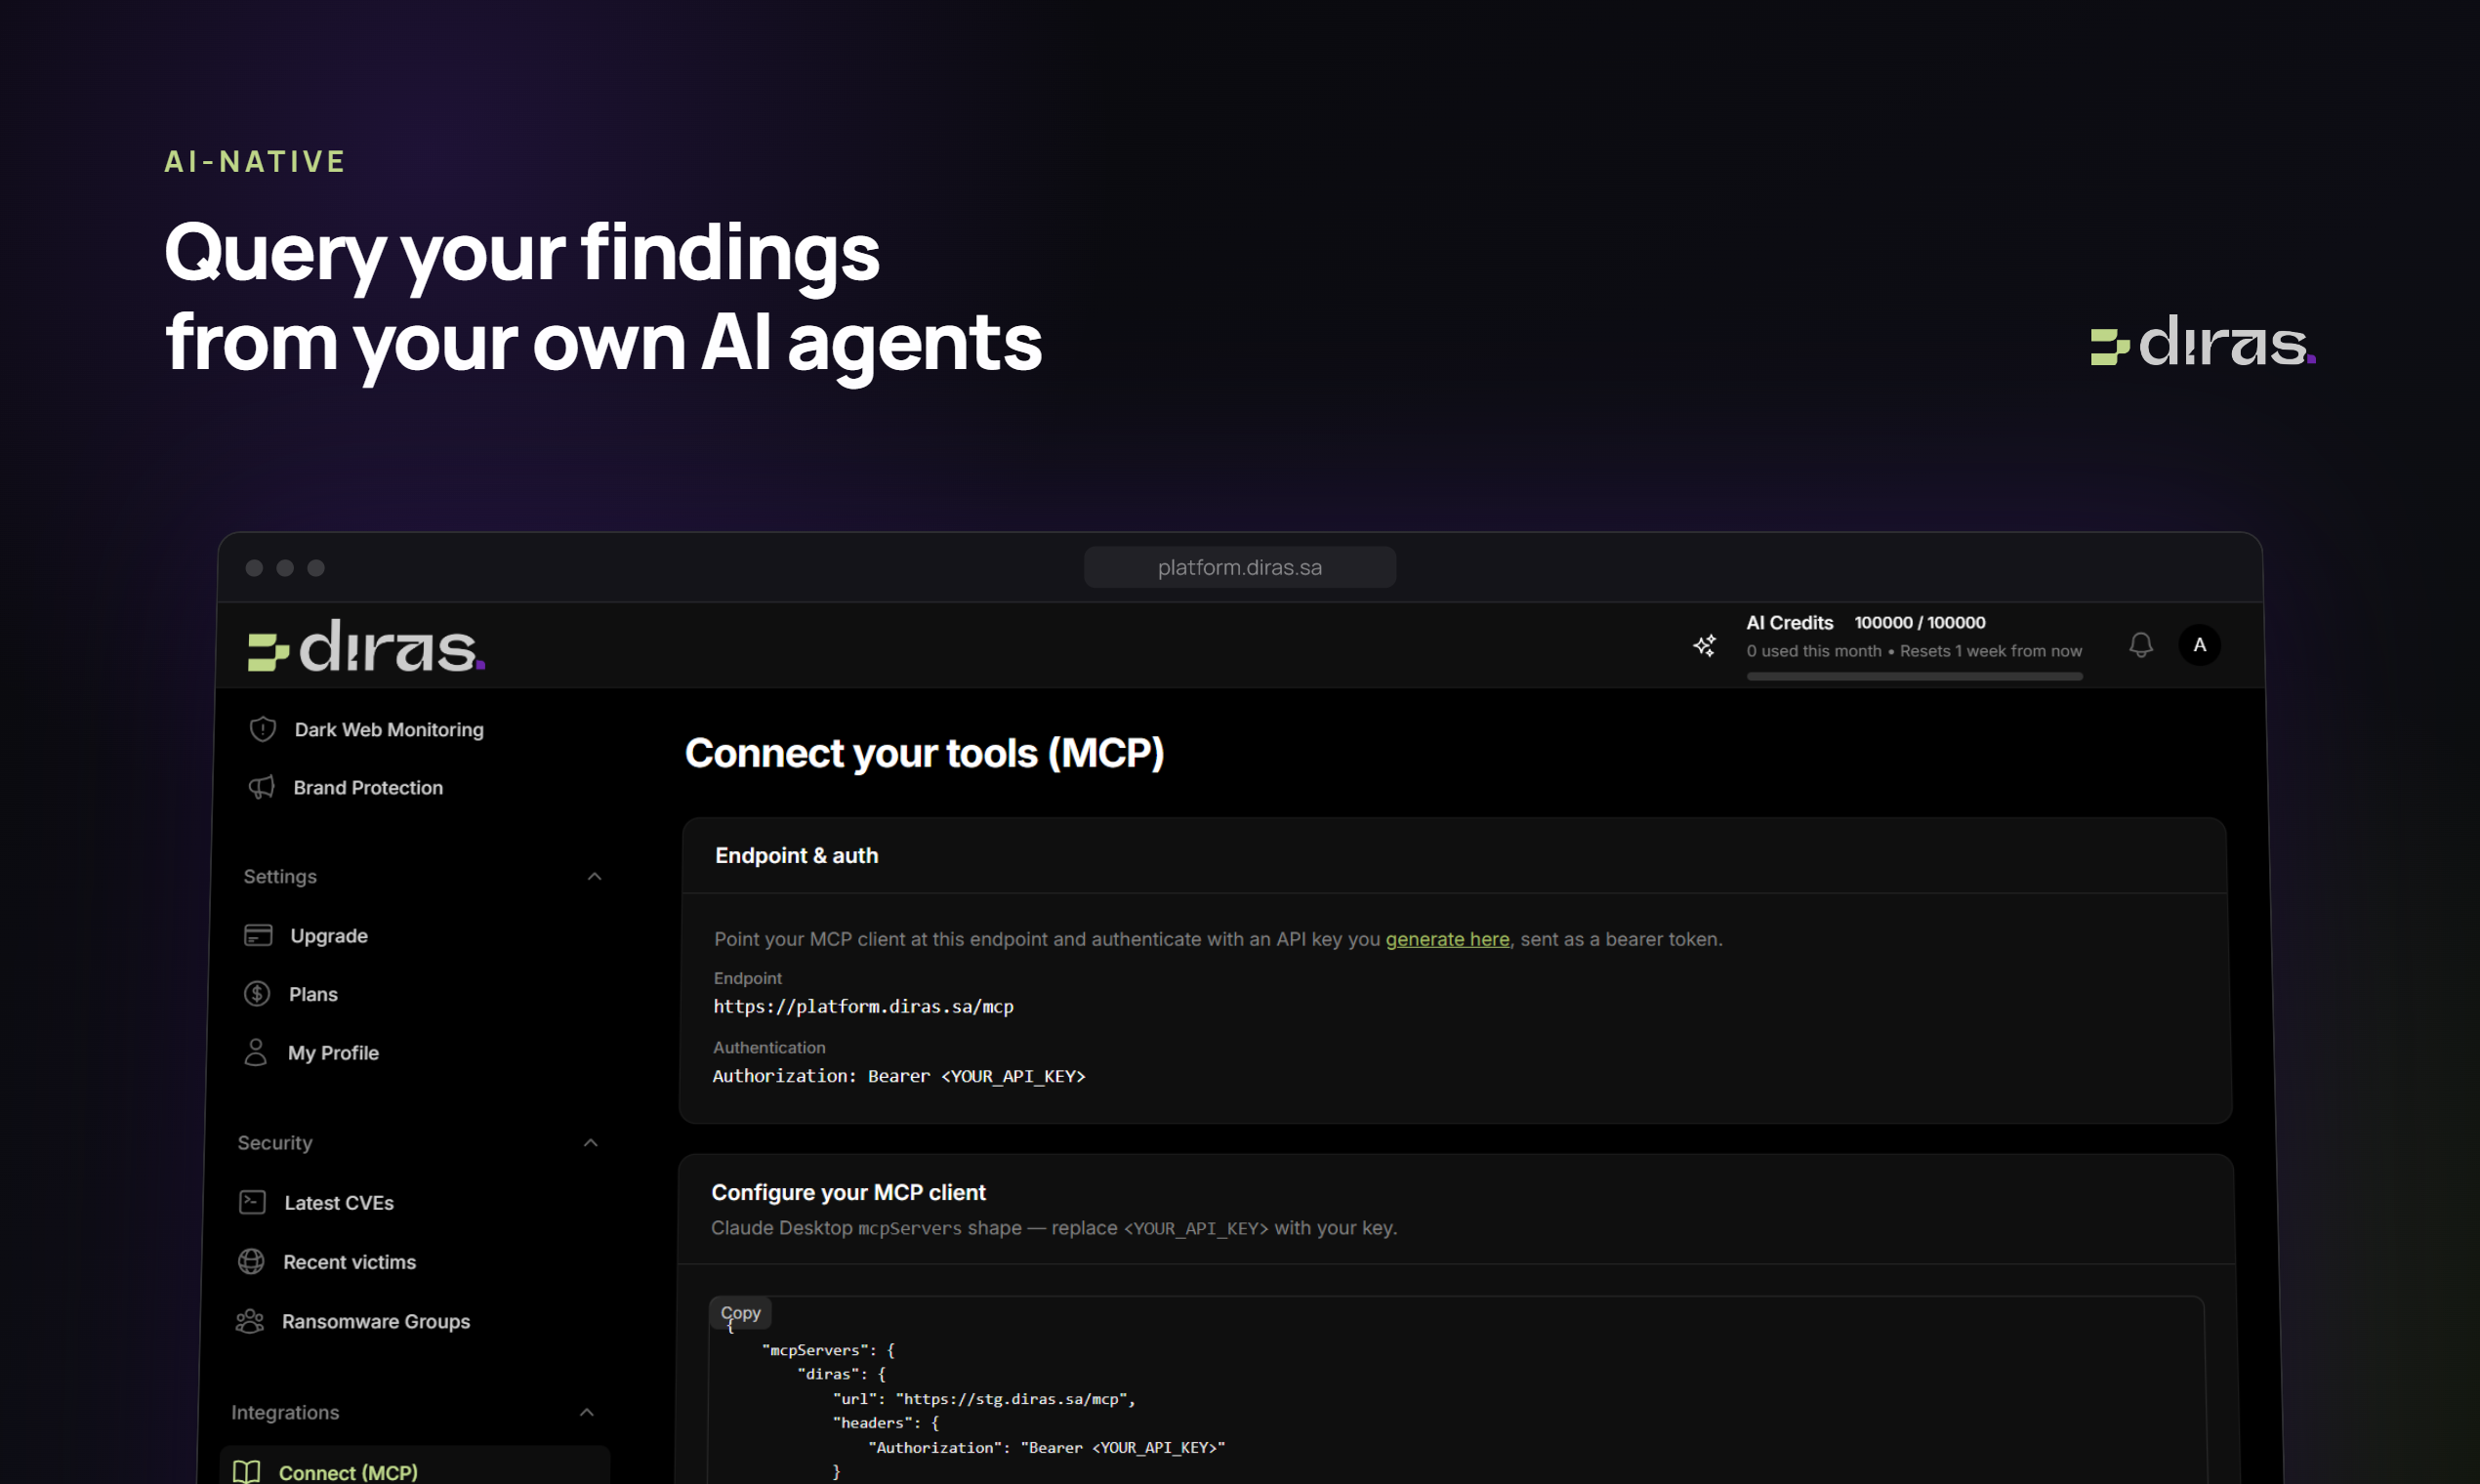
External attack surface management maintains an inventory of domains, subdomains, IP addresses, exposed services, and certificates. Its Vulnerability Management capabilities classify findings by severity and provide remediation guidance. Diras also offers risk scoring, signal correlation, alert prioritization, and a Model Context Protocol server for querying threat data from compatible AI clients.
Diras was developed and is hosted in Saudi Arabia, offers Arabic and English interfaces, and states that it is designed to align with Saudi Arabia’s Personal Data Protection Law and National Cybersecurity Authority requirements. Organizations can use a free exposure check to search known breach and dark-web sources without creating an account.
Categories & Use Cases
Media


1 / 5