

TurboPentest
What is TurboPentest?
TurboPentest is a self-serve, agentic AI penetration-testing platform from IntegSec, an offensive-security firm. A user buys a pentest online, proves ownership of the target, and autonomous AI agents run the engagement start to finish, with no sales call, no scoping meeting, and no human in the loop. A full report arrives in a few hours rather than the 2 to 4 weeks typical of manual pentesting. Email sign-in unlocks a live demo pentest with no credit card required.
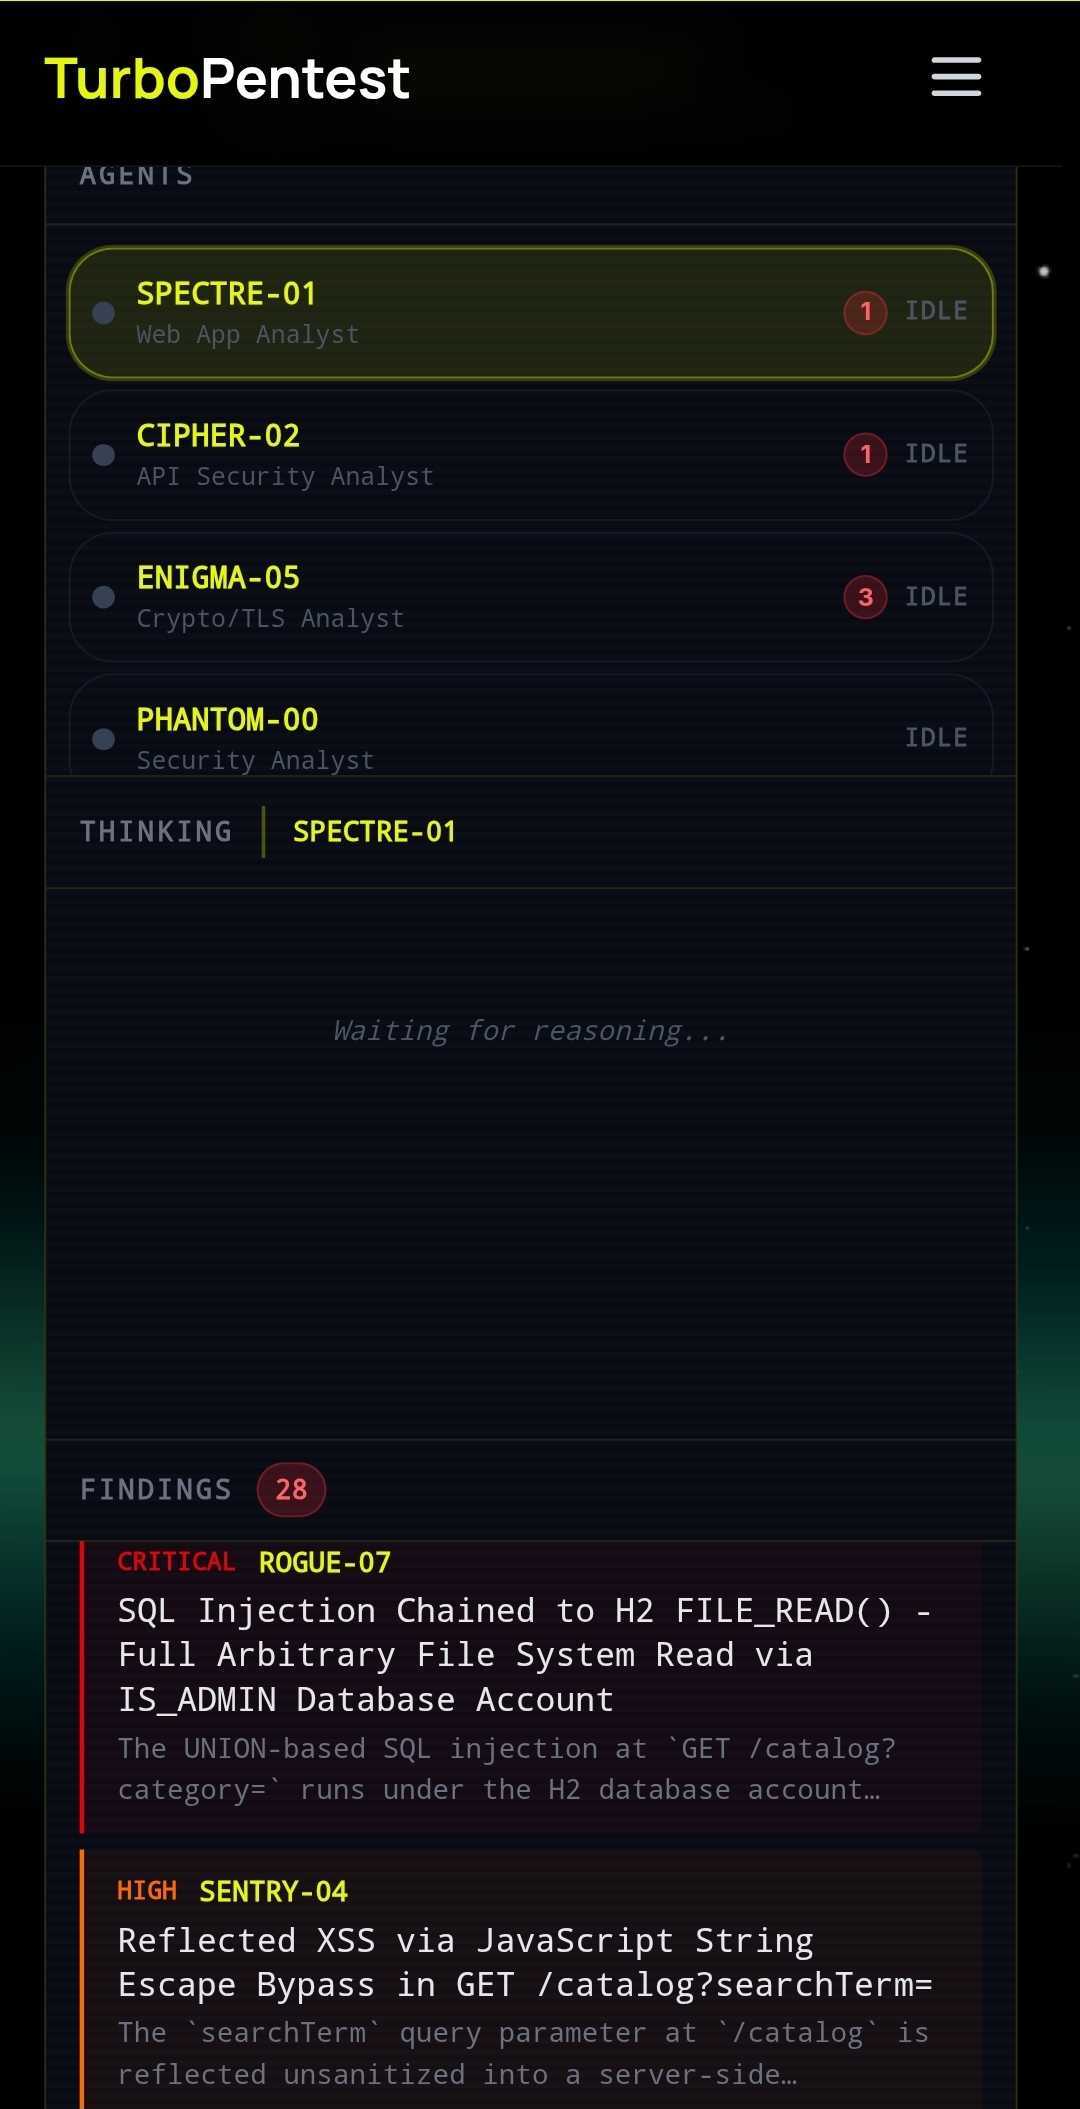
Testing engine and coverage Each run orchestrates 14 professional SAST and DAST tools under Paladin, an AI orchestrator that validates every candidate finding with reproducible proof and classifies source-code findings to OWASP ASVS (and mobile findings to MASVS) and conducts a full pentest against the target. Coverage spans network, web application, API, subdomain discovery, SSL/TLS, and external attack surface in a single run, aligned to frameworks including PTES, NIST SP 800-115, the OWASP Testing Guides, and MITRE ATT&CK.
White-box source-code analysis Connecting a GitHub repository (read-only) adds white-box testing at no additional cost: Opengrep SAST running a 325-rule pack across JavaScript/TypeScript, Python, Java, Go, PHP, Ruby, and C# (each rule mapped to CWE, OWASP, and ASVS and shipped with true-positive and true-negative unit tests), plus secret scanning and software-composition analysis included.
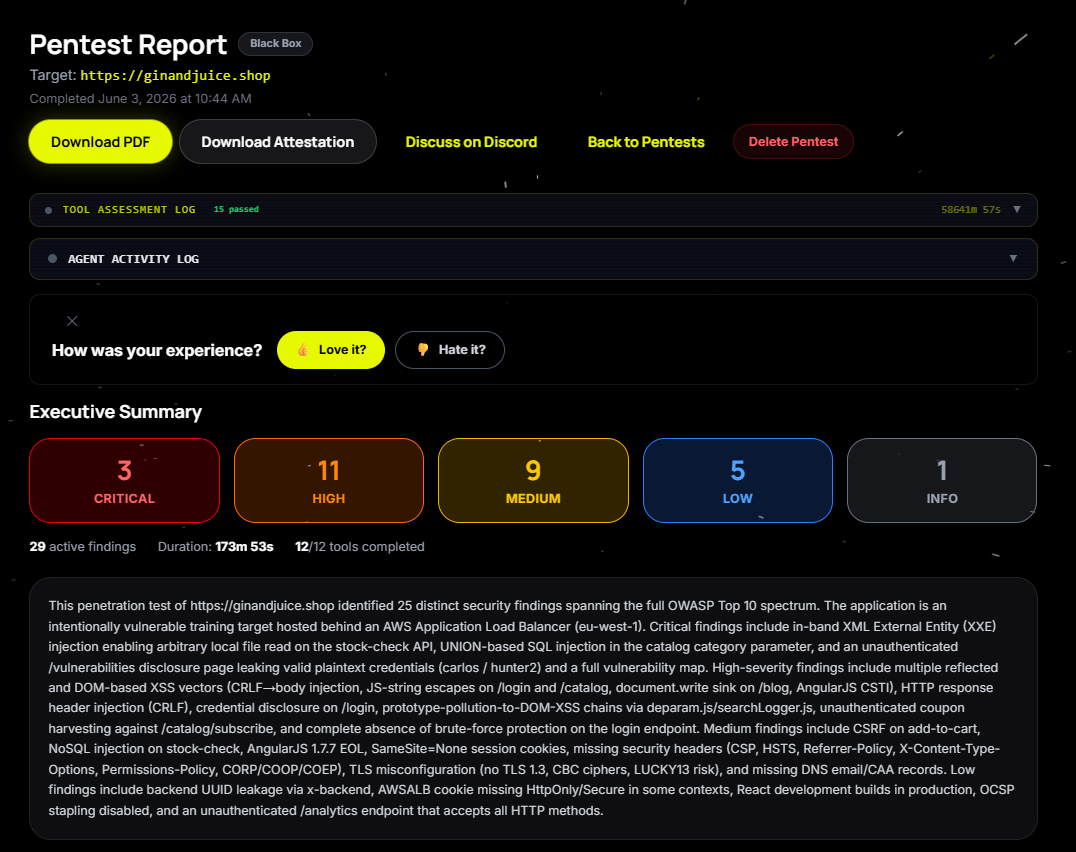
Deliverables Every pentest produces a PDF report (executive summary, findings with proof-of-concept, and remediation guidance), a signed third-party attestation letter suitable for SOC 2, ISO 27001, and HIPAA vendor questionnaires, an attack-surface map, a STRIDE threat model, retest commands to confirm each fix, and ready-to-paste "Fix with AI" prompts for tools such as Cursor and Claude Code.
Differentiators
Testing engine and coverage Each run orchestrates 14 professional SAST and DAST tools under Paladin, an AI orchestrator that validates every candidate finding with reproducible proof and classifies source-code findings to OWASP ASVS (and mobile findings to MASVS) and conducts a full pentest against the target. Coverage spans network, web application, API, subdomain discovery, SSL/TLS, and external attack surface in a single run, aligned to frameworks including PTES, NIST SP 800-115, the OWASP Testing Guides, and MITRE ATT&CK.
White-box source-code analysis Connecting a GitHub repository (read-only) adds white-box testing at no additional cost: Opengrep SAST running a 325-rule pack across JavaScript/TypeScript, Python, Java, Go, PHP, Ruby, and C# (each rule mapped to CWE, OWASP, and ASVS and shipped with true-positive and true-negative unit tests), plus secret scanning and software-composition analysis included.
Deliverables Every pentest produces a PDF report (executive summary, findings with proof-of-concept, and remediation guidance), a signed third-party attestation letter suitable for SOC 2, ISO 27001, and HIPAA vendor questionnaires, an attack-surface map, a STRIDE threat model, retest commands to confirm each fix, and ready-to-paste "Fix with AI" prompts for tools such as Cursor and Claude Code.
Differentiators
Categories & Use Cases
Media




1 / 12
Screenshot of Summary of finding & executive summary