TrustRadius: an HG Insights company

Anomali ThreatStream vs. Google Threat Intelligence (Mandiant)

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Anomali ThreatStream

    Score6.4 out of 10
    N/AA solution to operationalize actionable data and insights to secure any organization. Anomali ThreatStream provides curated access to the a global repository of threat intelligence, delivering enrichment, contextualization, and detection of known and emerging threats.N/A

    Google Threat Intelligence (Mandiant)

    Score10 out of 10
    Enterprise companies (1,001+ employees)
    Google Threat Intelligence, based on the expertise and service of Mandiant, aims to accelerate security and risk decision making – operational as well as strategic – and to enable security teams to focus on threats that matter to them.N/A
    Pricing
    Anomali ThreatStreamGoogle Threat Intelligence (Mandiant)
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    Anomali ThreatStreamGoogle Threat Intelligence (Mandiant)
    Free Trial
    NoYes
    Free/Freemium Version
    NoYes
    Premium Consulting/Integration Services
    NoYes
    Entry-level Setup FeeNo setup feeOptional
    Additional DetailsPriced by company size
    More Pricing Information
    Community Pulse
    Anomali ThreatStreamGoogle Threat Intelligence (Mandiant)
    Considered Both Products
    Anomali
    No answer on this topic
    Google
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    100%
    Would buy again
    17 Answers
    Delivers good value for the price
    No answers on this topic
    100%
    Delivers good value for the price
    14 Answers
    Happy with the feature set
    No answers on this topic
    100%
    Happy with the feature set
    17 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    80%
    Lived up to sales and marketing promises
    8 Answers
    Implementation went as expected
    No answers on this topic
    100%
    Implementation went as expected
    14 Answers
    Features
    Anomali ThreatStreamGoogle Threat Intelligence (Mandiant)
    Endpoint Security
    Comparison of Endpoint Security features of Anomali ThreatStream and Google Threat Intelligence (Mandiant)
    Feature
    Anomali ThreatStream
    -
    Ratings
    Google Threat Intelligence (Mandiant)
    7.2
    6 Ratings
    0% below category average
    Infection Remediation00 Ratings7.26 Ratings
    Threat Intelligence
    Comparison of Threat Intelligence features of Anomali ThreatStream and Google Threat Intelligence (Mandiant)
    Feature
    Anomali ThreatStream
    -
    Ratings
    Google Threat Intelligence (Mandiant)
    7.8
    10 Ratings
    8% above category average
    Network Analytics00 Ratings7.79 Ratings
    Threat Recognition00 Ratings7.89 Ratings
    Vulnerability Classification00 Ratings7.510 Ratings
    Automated Alerts and Reporting00 Ratings8.09 Ratings
    Threat Analysis00 Ratings7.510 Ratings
    Threat Intelligence Reporting00 Ratings8.210 Ratings
    Automated Threat Identification00 Ratings7.99 Ratings
    User Ratings
    Anomali ThreatStreamGoogle Threat Intelligence (Mandiant)
    Likelihood to Recommend
    8.9
    (2 ratings)
    7.8
    (18 ratings)
    Usability
    -
    (0 ratings)
    7.6
    (18 ratings)
    User Testimonials
    Anomali ThreatStreamGoogle Threat Intelligence (Mandiant)
    Likelihood to Recommend
    Anomali
    Anomali ThreatStream is excellent in scenarios where we deliver Managed Security Services to customers. It offers exhaustive volumes of information in the form of threat bulletins, IOCs, Threat Actor profiling, and details related to campaigns in the wild which can be used to a great extent by MSSPs. For an enterprise SOC, I believe it is a little less suited purely because of the pricing aspect as it is slightly towards the expensive side of the spectrum.
    Incentivized
    Read full review
    Google
    Usually SOC leverages Intel from mutiple sources. The scenarios are: 1.Suitable: In large scale SOC where more than 5000 devices are being monitored and the tech stack is wide, Mandiant will play an excellent role in that scenario. 2.Not Suitable: In small scale SOCs wherein limited devices belonging to the same tech stack is being used then the analysts can rely on OSINT and it is not useful to buy the solution.
    Incentivized
    Read full review
    Pros
    Anomali
    • Indicators of Compromise
    • Signatures
    • Community Sharing
    Incentivized
    Read full review
    Google
    • accelerated threat response feature, prioritizing threats according to requirement.
    • Optimization of the threat intelligence , and can be integrated with 3rd party tools.
    • Features like - Breach ,Adversary, Machine and Operational Intelligence.
    • Mandiant dynamic host and the malware views along with indicators.
    Incentivized
    Read full review
    Cons
    Anomali
    • The user interface, perhaps there is some room for improvement although it is good already.
    • Confidence assigning process for IOCs needs to be more robust and transparent.
    • While integration with SIEM solutions is a cakewalk, there is definitely added value if SIGMA rule conversion and YARA rule creation are provided from the platform.
    Incentivized
    Read full review
    Google
    • Paywalls exist throughout the data set and can halt an investigation without the right model
    • Some data was incomplete or broken up between pay tiers
    • Navigation through the data lacked a definitive trail or breadcrumbs to retrace steps during investigations
    Incentivized
    Read full review
    Usability
    Anomali
    No answers on this topic
    Google
    Mandiant Advantage Threat Intelligence has a very usable platform, with well-differentiated sections for the analyst, as well as the possibility of cross-searching to obtain the desired results. All this is presented with an interface that is easy on the eye and not very messy, which increases productivity and the speed with which work is done.
    Incentivized
    Read full review
    Alternatives Considered
    Anomali
    Many of the products that can be used to be ingested into a security event management software can be cumbersome with threat streamThere are many opportunities to continue fine-tuning the environment and providing great context in regards to threat research. When compared to other products threat stream stands out from usability and features.
    Incentivized
    Read full review
    Google
    It gives more ways to analyze threats and options to fixed it. This device gives more visibility on vulnerability detection and its analysis. It provides detailed reports to have more information of all malwares which help us to increase overall security of our current organization
    Incentivized
    Read full review
    Return on Investment
    Anomali
    • We have seen a positive ROI as the security monitoring is taken to the next level when it is augmented with threat intel data that Anomali provides.
    • Our customers are very satisfied with the periodic threat reports that we send, which are created using Anomali ThreatStream.
    • The overall business objectives are met as Threat Intel is one of the most important pillars when it comes to providing security services, and we use Anomali ThreatStream extensively for that.
    Incentivized
    Read full review
    Google
    • Improved incident response time
    • Specific investigations that have reduced the attack surface
    • Technical reports on threats not controlled by the bank's local team
    Incentivized
    Read full review
    ScreenShots

    Google Threat Intelligence (Mandiant) Screenshots
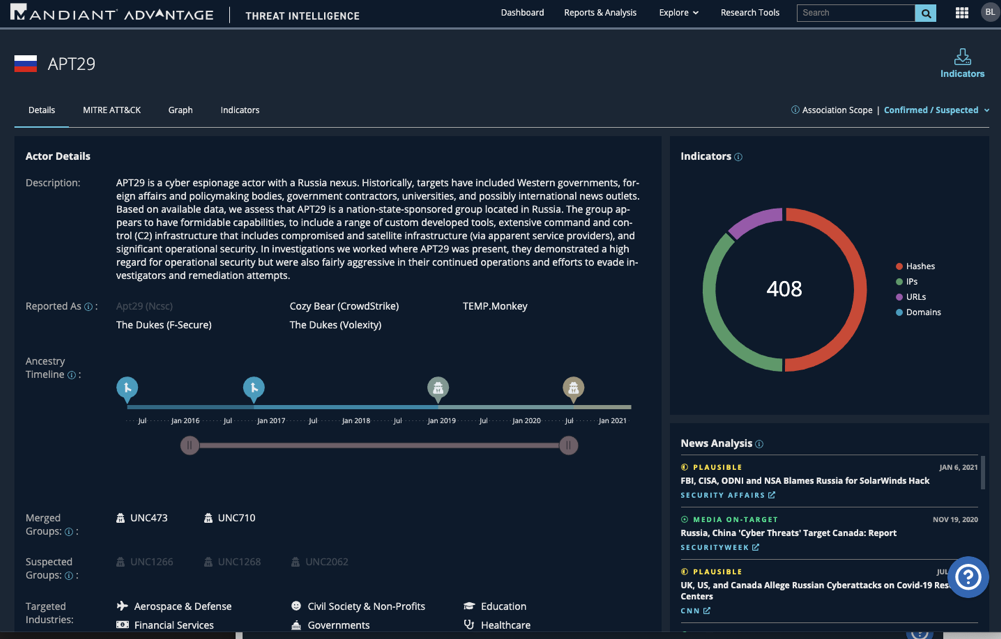
    Screenshot of Mandiant Advantage DashboardScreenshot of Mandiant Advantage Actor DetailsScreenshot of Mandiant Advantage Actor Graph
