TrustRadius: an HG Insights company

Arctic Wolf Managed Detection and Response vs. Mandiant Managed Defense

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Arctic Wolf Managed Detection and Response

    Score9.1 out of 10
    N/AArctic Wolf Networks in Sunnyvale provides scalable managed cybersecurity protection for IT-constrained companies, to keep their critical data, networks, web-based applications, and devices safe. Working as an extension of an internal team, Arctic Wolf security experts deliver 24x7 cloud-based monitoring, risk management, threat detection, and response services that protect companies from ever-evolving methods of cyber attack.N/A

    Mandiant Managed Defense

    Score6.8 out of 10
    Enterprise companies (1,001+ employees)
    Mandiant Managed Defense provides 24/7 threat detection, investigation, and response (TDIR) with access to frontline experts who monitor the client's security technology. It has been offered through Google Cloud since the late 2022 acquisition of Mandiant, by Google.N/A
    Pricing
    Arctic Wolf Managed Detection and ResponseMandiant Managed Defense
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    Arctic Wolf Managed Detection and ResponseMandiant Managed Defense
    Free Trial
    NoNo
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional Details
    More Pricing Information
    Community Pulse
    Arctic Wolf Managed Detection and ResponseMandiant Managed Defense
    Considered Both Products
    Arctic Wolf Networks
    No answer on this topic
    Google
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    100%
    Would buy again
    6 Answers
    Delivers good value for the price
    No answers on this topic
    100%
    Delivers good value for the price
    6 Answers
    Happy with the feature set
    No answers on this topic
    100%
    Happy with the feature set
    6 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    No answers on this topic
    Implementation went as expected
    No answers on this topic
    No answers on this topic
    User Ratings
    Arctic Wolf Managed Detection and ResponseMandiant Managed Defense
    Likelihood to Recommend
    7.0
    (3 ratings)
    7.0
    (6 ratings)
    Usability
    8.0
    (1 ratings)
    -
    (0 ratings)
    Support Rating
    -
    (0 ratings)
    7.3
    (6 ratings)
    User Testimonials
    Arctic Wolf Managed Detection and ResponseMandiant Managed Defense
    Likelihood to Recommend
    Arctic Wolf Networks
    [Artic Wolf SOC-as-a-Service is] great if you don't have a large team nor the time to look at all the systems in your network. They monitor 24x7x365 taking that burden away from a reduced IT team.
    Incentivized
    Read full review
    Google
    Rapid identification & Neutralization : The Madiant Rapid Response team will get work right away often within hours to identify and eject the adversary . Others Vendor takes days. Post Incidents Threat Summary: Mandiant provide formal summary of its investigation, detailing the actions it took & discovery it made as well as recommending long term guidance on how to mitigate the recurrence of similar threats in future . Also provide ongoing detection & response.
    Incentivized
    Read full review
    Pros
    Arctic Wolf Networks
    • Monitoring 365 logins
    • Monitoring Windows processes
    • Active Directory monitoring
    Incentivized
    Read full review
    Google
    • Excellent across all major tenant of incident response (detection, containment, eradication, etc.)
    • Has a strong backend support system to perform advanced incident response activities (reverse malware engineering, etc.)
    • Very scalable - no matter how small or large the incident, Managed Defense can tackle it, or escalate to Mandiant IR if the incident is complex and/or large enough.
    Read full review
    Cons
    Arctic Wolf Networks
    • Too many independent dashboards to look at (they are working on consolidating)
    Incentivized
    Read full review
    Google
    • Due to split from FireEye Mandiant no longer can provide its own End Point Protection as part of MDR for customers that want to transition after incident is complete .
    • Single remediation response with no-ongoing monitoring
    Incentivized
    Read full review
    Usability
    Arctic Wolf Networks
    Their portal is easy to use and they raise important incidents to us via email or phone. They have been good with us customizing the way we want to get important information. Sometimes there is a delay between when we have resolved and issue and it is updated on the portal.
    Incentivized
    Read full review
    Google
    No answers on this topic
    Support Rating
    Arctic Wolf Networks
    No answers on this topic
    Google
    We are a quiet shop with few incidents, however, MD's response to questions and access to our assigned MD consultant is excellent.
    Incentivized
    Read full review
    Alternatives Considered
    Arctic Wolf Networks
    The biggest issue with Crowdstrike was their sales staff - they were not very responsive. AWN does frequent check-ins with us, which helps communication. We have not had any issues with the service creating downtime. Whereas Crowdstrike had an issue in July 2024 that created many problems. This combined with the sales issues made it easy for us to go back to AWN.
    Incentivized
    Read full review
    Google
    Honestly, Mandiant seems to be the best all around. Even with being a smaller business, it’s help tremendously and keeps us feeling safe and protected
    Incentivized
    Read full review
    Return on Investment
    Arctic Wolf Networks
    • Stopped unauthorized 365 access on user account
    • Pointed out malicious file activity on end point
    • Alert sent when a domain admin account was enabled
    Incentivized
    Read full review
    Google
    • IT/SOC time saved by monitoring alerts
    • Improved time to remediation due to 24/7 eyes on glass
    • Hopefully less impact from security incidents due to early detection and containment
    Incentivized
    Read full review
    ScreenShots

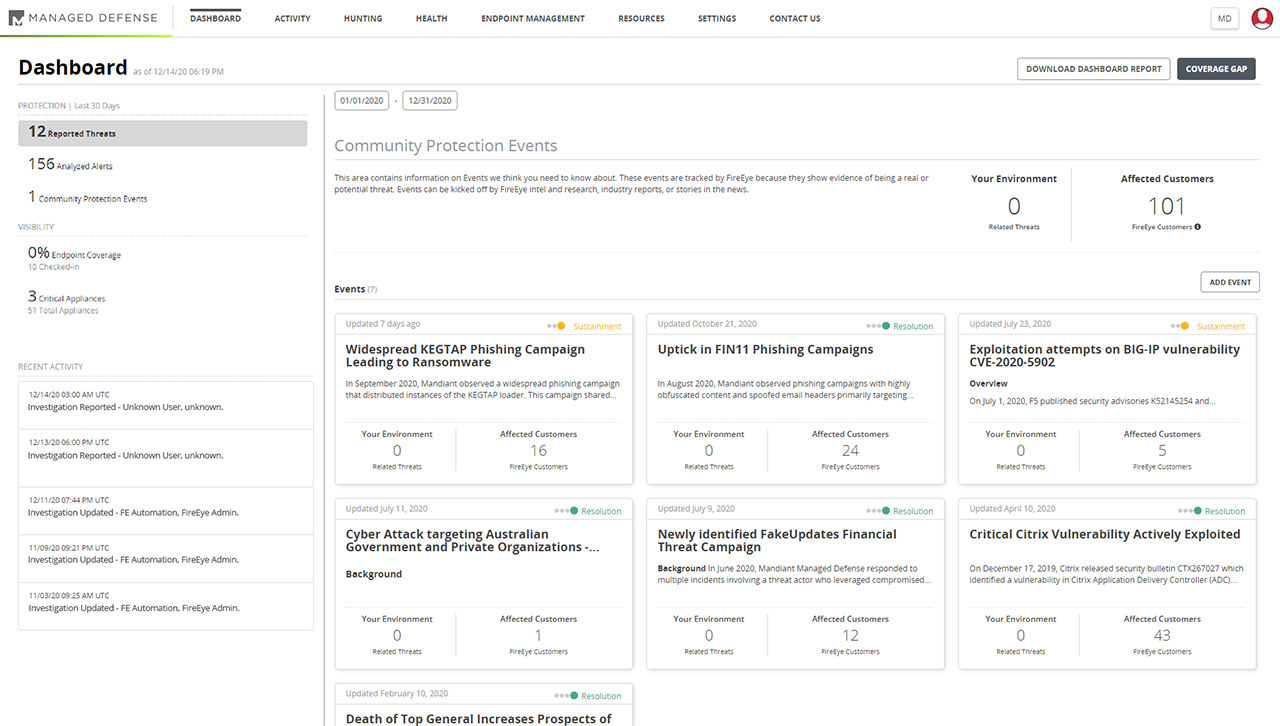
    Mandiant Managed Defense Screenshots

    Screenshot of Managed Defense DashboardScreenshot of Community Protection Events DashboardScreenshot of Threat Hunting Details