TrustRadius: an HG Insights company

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    AWS CloudTrail

    Score8.8 out of 10
    N/AAWS CloudTrail is a service that enables governance, compliance, operational auditing, and risk auditing of an AWS account. With CloudTrail, users can log, continuously monitor, and retain account activity related to actions across AWS infrastructure. CloudTrail provides event history of AWS account activity, including actions taken through the AWS Management Console, AWS SDKs, command line tools, and other AWS services. This event history simplifies security analysis, resource change tracking,…N/A

    Microsoft Defender for Endpoint

    Score8.8 out of 10
    N/AMicrosoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.

    $2.50

    per user/per month

    Pricing
    AWS CloudTrailMicrosoft Defender for Endpoint
    Editions & Modules
    No answers on this topic
    Academic
    $2.50
    per user/per month
    Standalone
    $5.20
    per user/per month
    Offerings
    Pricing Offerings
    AWS CloudTrailMicrosoft Defender for Endpoint
    Free Trial
    YesYes
    Free/Freemium Version
    YesNo
    Premium Consulting/Integration Services
    YesNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional DetailsYou can view, filter, and download the most recent 90 days of your account activity for all management events in supported AWS services free of charge. You can set up a trail that delivers a single copy of management events in each region free of charge. Once a CloudTrail trail is set up, Amazon S3 charges apply based on your usage. You will be charged for any data events or additional copies of management events recorded in that region. In addition, you can choose CloudTrail Insights by enabling Insights events in your trails. CloudTrail Insights analyzes write management events, and you are charged based on the number of events that are analyzed in that region.—
    More Pricing Information
    Community Pulse
    AWS CloudTrailMicrosoft Defender for Endpoint
    Considered Both Products
    Amazon AWS
    No answer on this topic
    Microsoft
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    96%
    Would buy again
    157 Answers
    Delivers good value for the price
    No answers on this topic
    99%
    Delivers good value for the price
    146 Answers
    Happy with the feature set
    No answers on this topic
    95%
    Happy with the feature set
    155 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    97%
    Lived up to sales and marketing promises
    130 Answers
    Implementation went as expected
    No answers on this topic
    95%
    Implementation went as expected
    140 Answers
    Features
    AWS CloudTrailMicrosoft Defender for Endpoint
    Endpoint Security
    Comparison of Endpoint Security features of AWS CloudTrail and Microsoft Defender for Endpoint
    Feature
    AWS CloudTrail
    -
    Ratings
    Microsoft Defender for Endpoint
    8.7
    79 Ratings
    2% above category average
    Anti-Exploit Technology00 Ratings9.075 Ratings
    Endpoint Detection and Response (EDR)00 Ratings9.179 Ratings
    Centralized Management00 Ratings8.679 Ratings
    Hybrid Deployment Support00 Ratings7.110 Ratings
    Infection Remediation00 Ratings9.077 Ratings
    Vulnerability Management00 Ratings8.774 Ratings
    Malware Detection00 Ratings9.278 Ratings
    Best Alternatives
    AWS CloudTrailMicrosoft Defender for Endpoint
    Small Businesses
    Armor
    Score6 out of 10
    SentinelOne Singularity
    Score9 out of 10
    Medium-sized Companies
    Trend Micro Deep Security
    Score8.3 out of 10
    BlackBerry Protect (CylancePROTECT)
    Score9.1 out of 10
    Enterprises
    Wiz
    Score9.4 out of 10
    ESET PROTECT
    Score8.8 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    AWS CloudTrailMicrosoft Defender for Endpoint
    Likelihood to Recommend
    8.0
    (4 ratings)
    8.9
    (169 ratings)
    Likelihood to Renew
    -
    (0 ratings)
    8.4
    (10 ratings)
    Usability
    -
    (0 ratings)
    8.6
    (40 ratings)
    Availability
    -
    (0 ratings)
    9.1
    (1 ratings)
    Performance
    -
    (0 ratings)
    9.1
    (1 ratings)
    Support Rating
    -
    (0 ratings)
    9.0
    (7 ratings)
    Implementation Rating
    -
    (0 ratings)
    7.3
    (1 ratings)
    Configurability
    -
    (0 ratings)
    8.2
    (1 ratings)
    Product Scalability
    -
    (0 ratings)
    9.1
    (1 ratings)
    User Testimonials
    AWS CloudTrailMicrosoft Defender for Endpoint
    Likelihood to Recommend
    Amazon AWS
    It is necessary to enable [AWS] Cloudtrail when using AWS in a production environment, otherwise you will not have any idea what is happening within your accounts. Third party monitoring applications will all require [AWS] CloudTrail to be enabled as well. I would not recommend it solely as a monitoring tool, to get the most out of it you must send the logs elsewhere. Either to Cloudwatch logs or a third party product.
    Incentivized
    Read full review
    Microsoft
    If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
    Incentivized
    Read full review
    Pros
    Amazon AWS
    • API Log
    • User activity tracking
    • Real-time alerts
    Incentivized
    Read full review
    Microsoft
    • The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
    Incentivized
    Read full review
    Cons
    Amazon AWS
    • [In my experience] Cost can easily get out of control with multiple trails on full logging
    • Logs can be difficult to decipher
    Incentivized
    Read full review
    Microsoft
    • I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
    Incentivized
    Read full review
    Likelihood to Renew
    Amazon AWS
    No answers on this topic
    Microsoft
    Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
    Incentivized
    Read full review
    Usability
    Amazon AWS
    No answers on this topic
    Microsoft
    Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
    Incentivized
    Read full review
    Reliability and Availability
    Amazon AWS
    No answers on this topic
    Microsoft
    Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
    Incentivized
    Read full review
    Performance
    Amazon AWS
    No answers on this topic
    Microsoft
    Microsoft Defender for Endpoint is easy on memory and resources on clients.
    Incentivized
    Read full review
    Support Rating
    Amazon AWS
    No answers on this topic
    Microsoft
    The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
    Incentivized
    Read full review
    Implementation Rating
    Amazon AWS
    No answers on this topic
    Microsoft
    Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
    Incentivized
    Read full review
    Alternatives Considered
    Amazon AWS
    I think in the end, CloudTrail has more features and you can dive deeper inside the logs so it depends on your usage and what you expect in the end to make the right choice, I would say that both tools are really useful and bring a lot of benefits to I.T. companies.
    Incentivized
    Read full review
    Microsoft
    Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
    Incentivized
    Read full review
    Scalability
    Amazon AWS
    No answers on this topic
    Microsoft
    Microsoft Defender for Endpoint is easily scaled from small orgs to giant enterprises.
    Incentivized
    Read full review
    Return on Investment
    Amazon AWS
    • Allows us to investigate any strange api actions
    • Increases security
    • Audit trail of changes made in AWS
    Incentivized
    Read full review
    Microsoft
    • I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
    Incentivized
    Read full review
    ScreenShots

    AWS CloudTrail Screenshots

    Screenshot of CloudTrail Insights: Identify and respond to unusual operational activity
•Unexpected spikes in resource provisioning
•Bursts of IAM management actions
•Gaps in periodic maintenance activity
•Automatic analysis of API calls and usage patterns
•Alerts when unusual activity is detected

    Microsoft Defender for Endpoint Screenshots
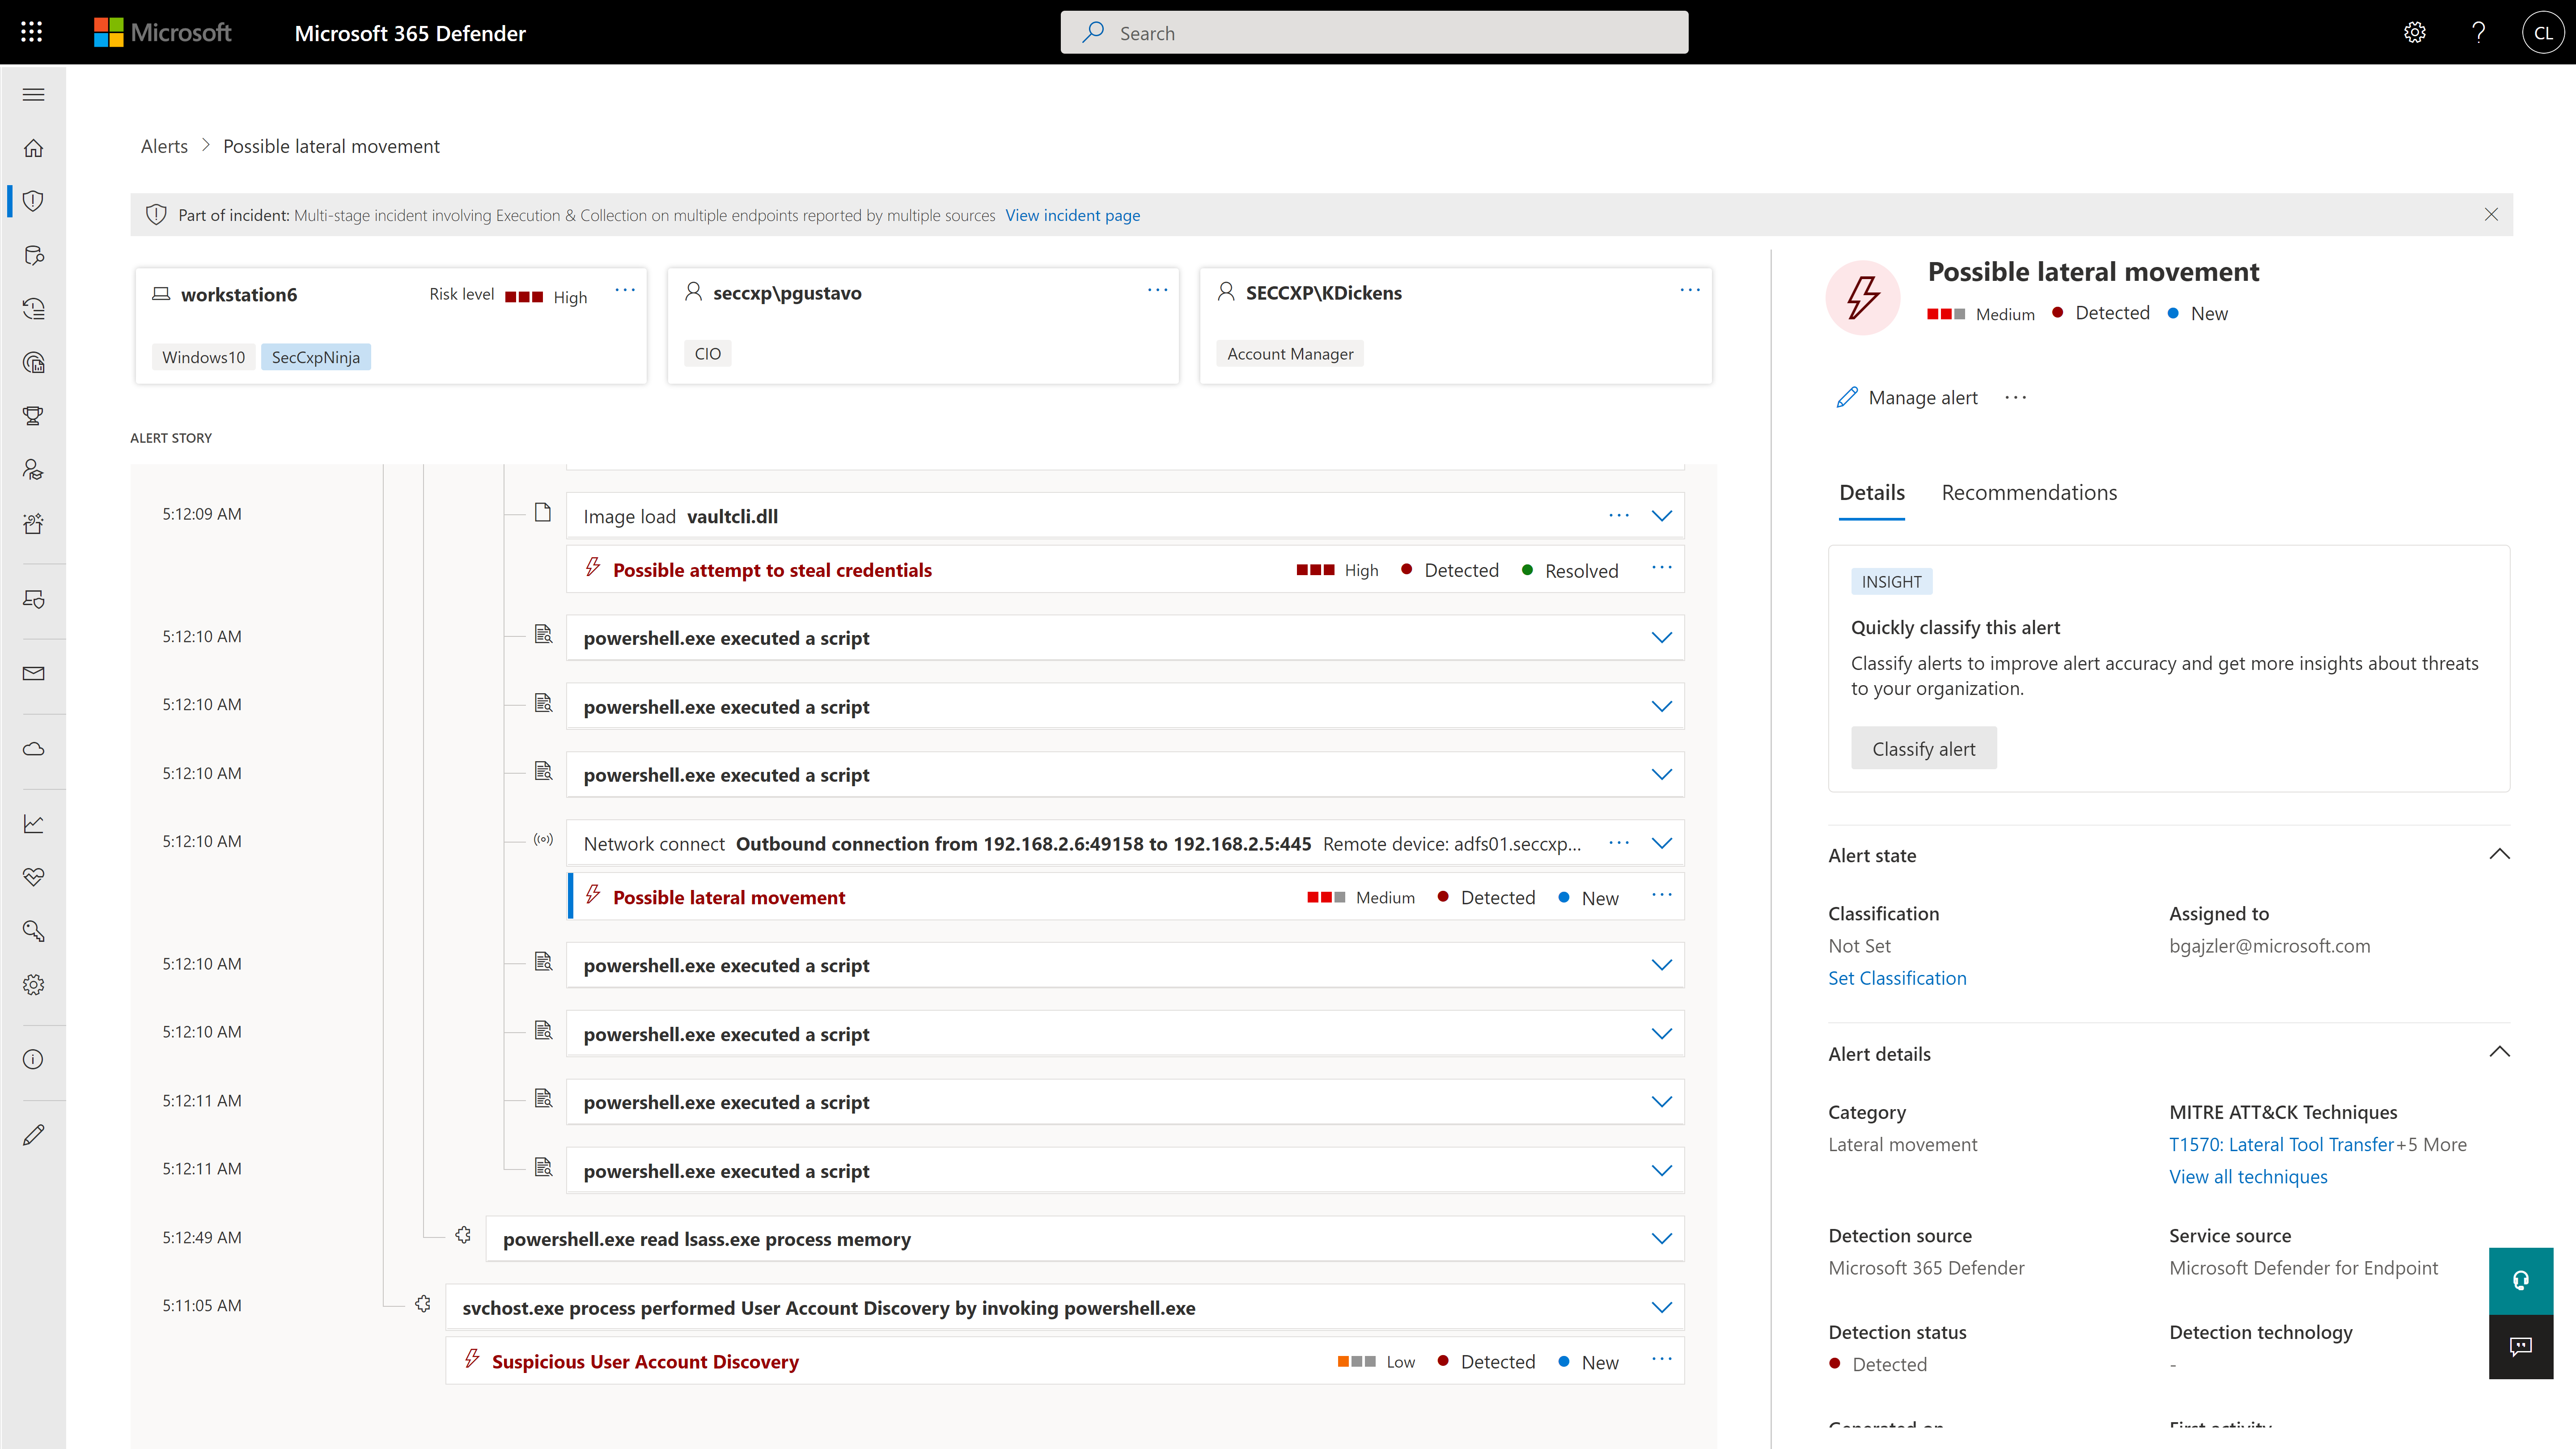
    Screenshot of blocked activitiesScreenshot of Detects & respondsScreenshot of discovers vulnerabilityScreenshot of Eliminates blind spotsScreenshot of Risk management