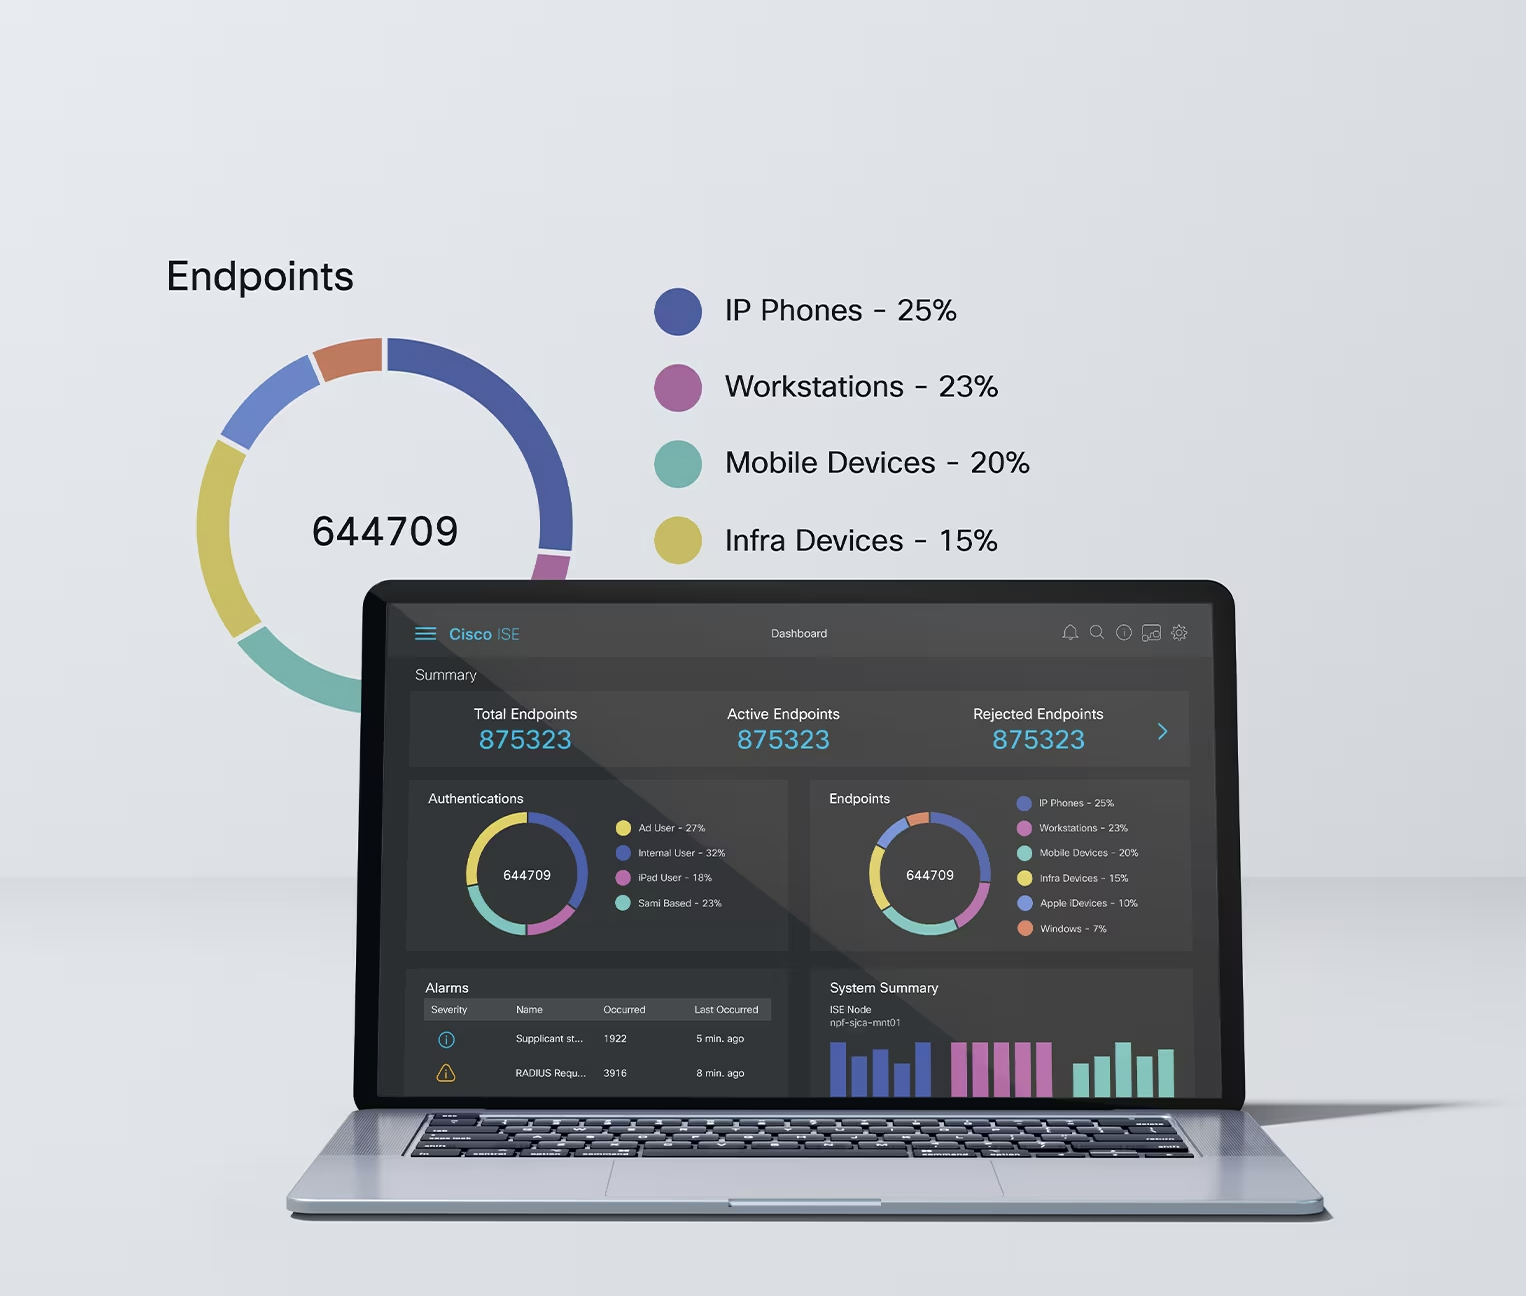
The Cisco Identity Services Engine (ISE) offers a network-based approach for adaptable, trusted access everywhere, based on context. It gives the user intelligent, integrated protection through intent-based policy and compliance solutions.
N/A
Tenable Nessus
Score8.8 out of 10
N/A
Tenable headquartered in Columbia offers Nessus, a vulnerability scanning and security assessment solution used to analyze an entity's security posture, vulnerability testing, and provide configuration assessments.
Well suited... I've used it for both wired and wireless access, and it's perfect for that. In addition to enforcing security on the port, you can also lock down east-west traffic. When you get to the point where you're configuring secure group tags and things like that, you can keep people from getting to places they shouldn't. Basically, you could turn your entire network into a firewall if you wanted to. You can secure access based on the identity of any given user through role-based authentication. For example, if you have salespeople and you don't want them accessing your financial or PCI environment, they authenticate as a salesperson and you can completely stop them from getting to any of that. That's really important, especially for us. Our payment card infrastructure servers are heavily locked down. Granted, in our situation, we firewall all that off anyway, but you still don't want some random individual to be able to even attempt that sort of thing. That's what it's really good for. I'm trying to think of a weakness. I don't know. We don't really struggle with it. There's nothing that I use it for where I wish it were better, at least not that I can think of offhand. I'm sure there are things, I just can't think of anything off the top of my head.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is an excellent tool for scanning servers, workstations, and network devices to identify missing patches and misconfiguration; we regularly use it to confirm patch effectiveness after the update; it also helps us for preparing audits such as iso 27001, and regulatory requirements, it also helps us to identify open ports and services that violate security.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Nessus is best at performing vulnerability scans, in fact, it gives findings and moreover accurate findings of the assessments. It does not do penetration testing or exploit the vulnerabilities because it is concerned about scanning the systems/applications.
In fact, Nessus has multiple profiles/policies to perform different types of scans such as, scans oriented for PCI-DSS, malware scans, web application scans, bad shell shock detection scan to name a few.
Nessus has the ability to classify the vulnerabilities into risk-based categories from critical to even informational which I think is one of the things that separates Nessus from other vulnerability scanners.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The tool has lots of options for setting up before scanning any device, this methodology could be simplified further with default configuration for various devices predefined, anyhow we can use this technique by making use of policies.
For advanced users we cannot disable the plugins inside the plugin groups, we can enable the whole set of plugins at a time, for few hundreds its ok, but thousands of plugins are of waste of resource and time.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Nessus is best and easy to use application for Vulnerabilities finding and reporting, it has multiple platforms and wide scope covering almost all devices for security improvement so far, thus we are very likely to continue its services.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For us the solution is very easily useable on its own. Perhaps that has to do because we started using ISE in the 1.2 days and have seen it grow during the years. Policy creation, etc. is all very visible and thus easy to use. Deployment of multiple nodes is also incredibly easy and flexible. You can easily add or remove nodes as you wish.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Tenable Nessus is a great product and provides a lot of value, but it is difficult to set up and use and the amount of data it generates can be overwhelming. It does help us prioritize based on the severity of the detection, however there are sometimes mitigating factors that we have implemented that Nessus does not account for, which causes lots of noise in the reports.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We do have to occasionally reboot the servers when they get low on memory, but we're also a few versions behind. Availability has generally been pretty good though with no major outages in the time that we've had it implemented.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco support is second to none, both in terms of how you access support but also the knowledge of the individual support teams. If you focus on one technology and provide "manufacturer support" then you can rest assured that you are accessing Cisco's top individuals. I feel like this is a USP for Cisco support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I haven't needed to contact support yet. But issues are easily solved with a quick internet search which means support and by extension, the larger community are involved and knowledgeable.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I think our system integrators lacks some competencies and this has led to an implementation that is still perfectible. (i.e. dedicating an interface for intra-cluster communication)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think all give some visibility of device monitoring and management, but Cisco Identity Services Engine gives a good way to manage more details about the device in a centralized way that gives a wider range of monitoring and control than the other softwares individually. I don't think Cisco Identity Services Engine eliminates the need for these other software as of now, but there is potential for Cisco Identity Services Engine to be able to take over more of these roles.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Sometimes when we identify a vulnerability with Nessus that has an exploit, we made a proof of concept with Metasploit in order to show to the IT managers the importance of the software/hardware hardening.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It's fully customised and comprehensive. only thing is you need to know what you want. Proper research and planning would save lots of time and effort .
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I don't know about negatives because we haven't seen it right now, but positive impact is one is the roadmap we have. And now since we are going ahead with doing the deployment of Cisco ISE, we see that we are getting closure to, so at the end of the day, we have to make sure that operationally we stay excellent. So that's where operational excellence comes in. Cisco ISE is basically addressing that for us. Right now we are in a situation if there is a WIFI issue or if there is an authentication issue, it gets really difficult to isolate the problem. But with Cisco ISE , this functionality is going to come in. So we believe that it would be a good ROI.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Nessus certainly has a positive impact while me while performing my job, either as security research, or performing vulnerability assessments for clients. It gives a lot of information about the system/application after performing scans. The number of false positives is also less compared to other vulnerability scanners.
The professional edition is very useful as policy templates available in this edition are very handy and useful even to perform compliance scan like PCI DSS scan.
Also, the ability to export the scan results into reports in formats like HTML, PDF is very useful which could be for performing system/application reviews.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info