TrustRadius: an HG Insights company

Cybereason Defense Platform vs. Microsoft Security Copilot

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Cybereason Defense Platform

    Score9.1 out of 10
    N/ACybereason EDR consolidates intelligence about each attack into a Malop (malicious operation), a contextualized view of the full narrative of an attack. Each Malop organizes the relevant attack data into an easy-to-read, interactive graphical interface, providing a complete timeline, the flow of the attack in the network, and any malicious communications. Remediation actions can be automated or accomplished remotely with a click. The Cybereason Defense Platform empowers analysts of all…N/A

    Microsoft Security Copilot

    Score8.5 out of 10
    N/AMicrosoft Security Copilot helps security and IT teams to protect organizations at the speed and scale of AI. It is available in a standalone experience or embedded into other Microsoft Security products.N/A
    Pricing
    Cybereason Defense PlatformMicrosoft Security Copilot
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    Cybereason Defense PlatformMicrosoft Security Copilot
    Free Trial
    NoNo
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional Details——
    More Pricing Information
    Community Pulse
    Cybereason Defense PlatformMicrosoft Security Copilot
    Considered Both Products
    LevelBlue
    No answer on this topic
    Microsoft
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    81%
    Would buy again
    22 Answers
    Delivers good value for the price
    No answers on this topic
    95%
    Delivers good value for the price
    19 Answers
    Happy with the feature set
    No answers on this topic
    96%
    Happy with the feature set
    26 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    89%
    Lived up to sales and marketing promises
    17 Answers
    Implementation went as expected
    No answers on this topic
    95%
    Implementation went as expected
    19 Answers
    Features
    Cybereason Defense PlatformMicrosoft Security Copilot
    Endpoint Security
    Comparison of Endpoint Security features of Cybereason Defense Platform and Microsoft Security Copilot
    Feature
    Cybereason Defense Platform
    9.1
    2 Ratings
    7% above category average
    Microsoft Security Copilot
    -
    Ratings
    Anti-Exploit Technology8.32 Ratings00 Ratings
    Endpoint Detection and Response (EDR)9.62 Ratings00 Ratings
    Centralized Management9.62 Ratings00 Ratings
    Hybrid Deployment Support6.01 Ratings00 Ratings
    Infection Remediation10.02 Ratings00 Ratings
    Vulnerability Management10.01 Ratings00 Ratings
    Malware Detection10.02 Ratings00 Ratings
    Best Alternatives
    Cybereason Defense PlatformMicrosoft Security Copilot
    Small Businesses
    SentinelOne Singularity
    Score9 out of 10
    No answers on this topic
    Medium-sized Companies
    BlackBerry Protect (CylancePROTECT)
    Score9.1 out of 10
    No answers on this topic
    Enterprises
    ESET PROTECT
    Score8.8 out of 10
    No answers on this topic
    All AlternativesView all alternativesView all alternatives
    User Ratings
    Cybereason Defense PlatformMicrosoft Security Copilot
    Likelihood to Recommend
    8.7
    (2 ratings)
    8.0
    (30 ratings)
    Likelihood to Renew
    -
    (0 ratings)
    7.8
    (3 ratings)
    Usability
    -
    (0 ratings)
    7.5
    (30 ratings)
    Support Rating
    -
    (0 ratings)
    5.5
    (3 ratings)
    User Testimonials
    Cybereason Defense PlatformMicrosoft Security Copilot
    Likelihood to Recommend
    LevelBlue
    I'd recommend Cybereason due to it's efficacy, low TCO, low false/positive rate. The product was easy to implement and maintain. One of the major advantages of using Cybereason is that it requires minimal training for level 1 users to use the tool.
    Incentivized
    Read full review
    Microsoft
    It's easy to integrate with other tools because it's a native Microsoft solution for generating OAuth tokens and handling other integrations. But as far as querying for data, using the LLM to analyze it and find that needle in the haystack, whatever, I feel it's terrible. In my experience, it just takes so much manipulation to get it to actually do what you want it to do.
    Incentivized
    Read full review
    Pros
    LevelBlue
    • EDR
    • Forensics
    • Mitigation
    • Response
    Incentivized
    Read full review
    Microsoft
    • Sometimes people don't know how to do a certain feature, especially in Excel, for example. It's a little bit more complex and a community for certain people. And with just a couple of questions about using Microsoft Security Copilot, they can get their answers ready, not having to get support from IT, right? So it eliminates multiple tickets and support from personnel on our team, and they can get the response themselves via this assistant.
    Incentivized
    Read full review
    Cons
    LevelBlue
    • Slow support
    • Bugs on their interface
    • Log extraction
    Incentivized
    Read full review
    Microsoft
    • I don't have that as of yet. I do like the product for now. I'm sure that as I use it more, I will find things that can be improved. Just understanding how it integrates with the Microsoft ecosystem, it works just fine for what I use it for.
    Incentivized
    Read full review
    Likelihood to Renew
    LevelBlue
    No answers on this topic
    Microsoft
    We are not going to stop using M365 and our environment is large enough that there is not enough in-house expertise to handle all aspects of security, even with the help of a MSSP. Security Copilot helps us shore up the knowledge gap and keep our organization's security posture tight.
    Incentivized
    Read full review
    Usability
    LevelBlue
    No answers on this topic
    Microsoft
    Anyone can use it. Easy to prompt, also capabilities to become advance with custom agents. It can become custom to your workflow. Many people will have their unique experiences to share and results are generally positive. This is a growth in the product from the effect of community and adoption/usage.
    Incentivized
    Read full review
    Support Rating
    LevelBlue
    No answers on this topic
    Microsoft
    Never contacted support
    Incentivized
    Read full review
    Alternatives Considered
    LevelBlue
    Cybereason provides superior protection than either Microsoft or CrowdStrike and a better TCO. We receive less false positives than with Microsoft Defender and Cybereason is easier for level 1 users to use.
    Incentivized
    Read full review
    Microsoft
    My usage of other products is based on SIEM tools. So far, Microsoft Security Copilot is the only product I've seen that works across multiple technologies/products to provide full visibility into security tooling using AI. I know other vendors are working towards this, but Microsoft has definitely taken a lead.
    Incentivized
    Read full review
    Return on Investment
    LevelBlue
    • Helps on threat hunting
    • MalOps is very good
    • When we face a bug, it takes too much time for them to respond
    Incentivized
    Read full review
    Microsoft
    • I'd say it was initially negative because it took us time to learn it and understand how to build the workflow around it. But since then, we've been able to speed up and adjust and adapt and move a lot faster. So it's overall.
    • It is definitely in the positive area now.
    Incentivized
    Read full review
    ScreenShots

    Microsoft Security Copilot Screenshots
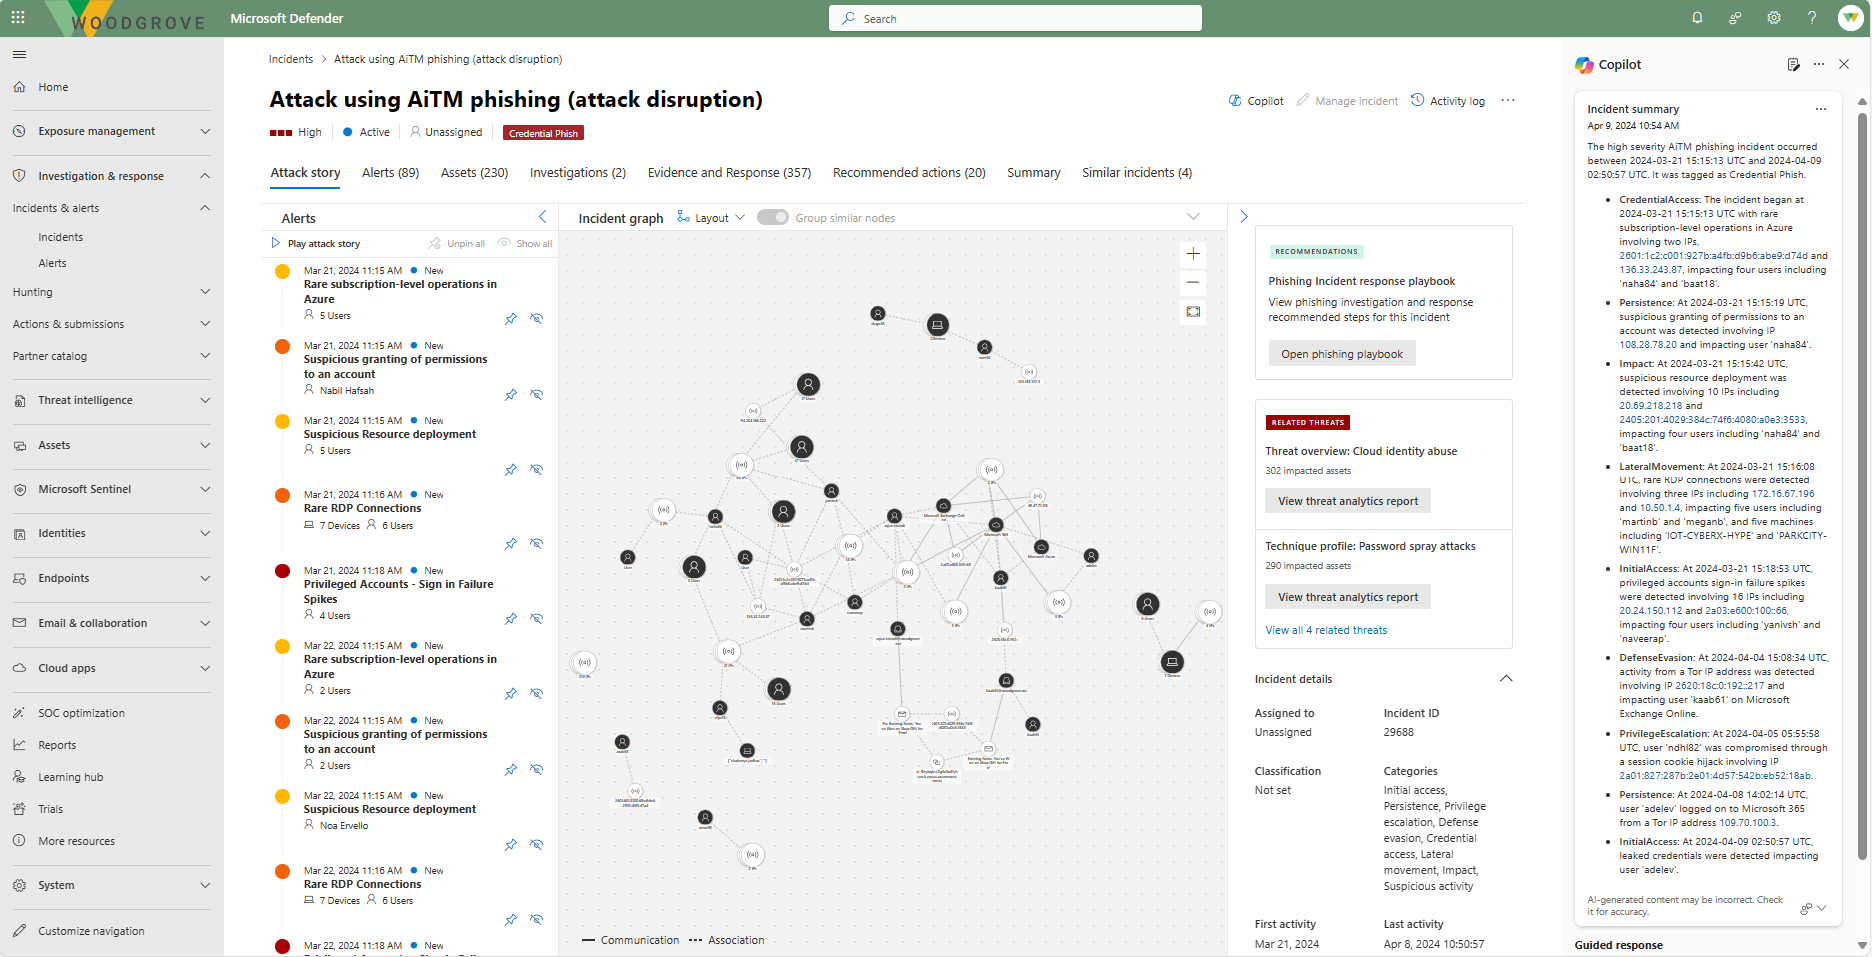
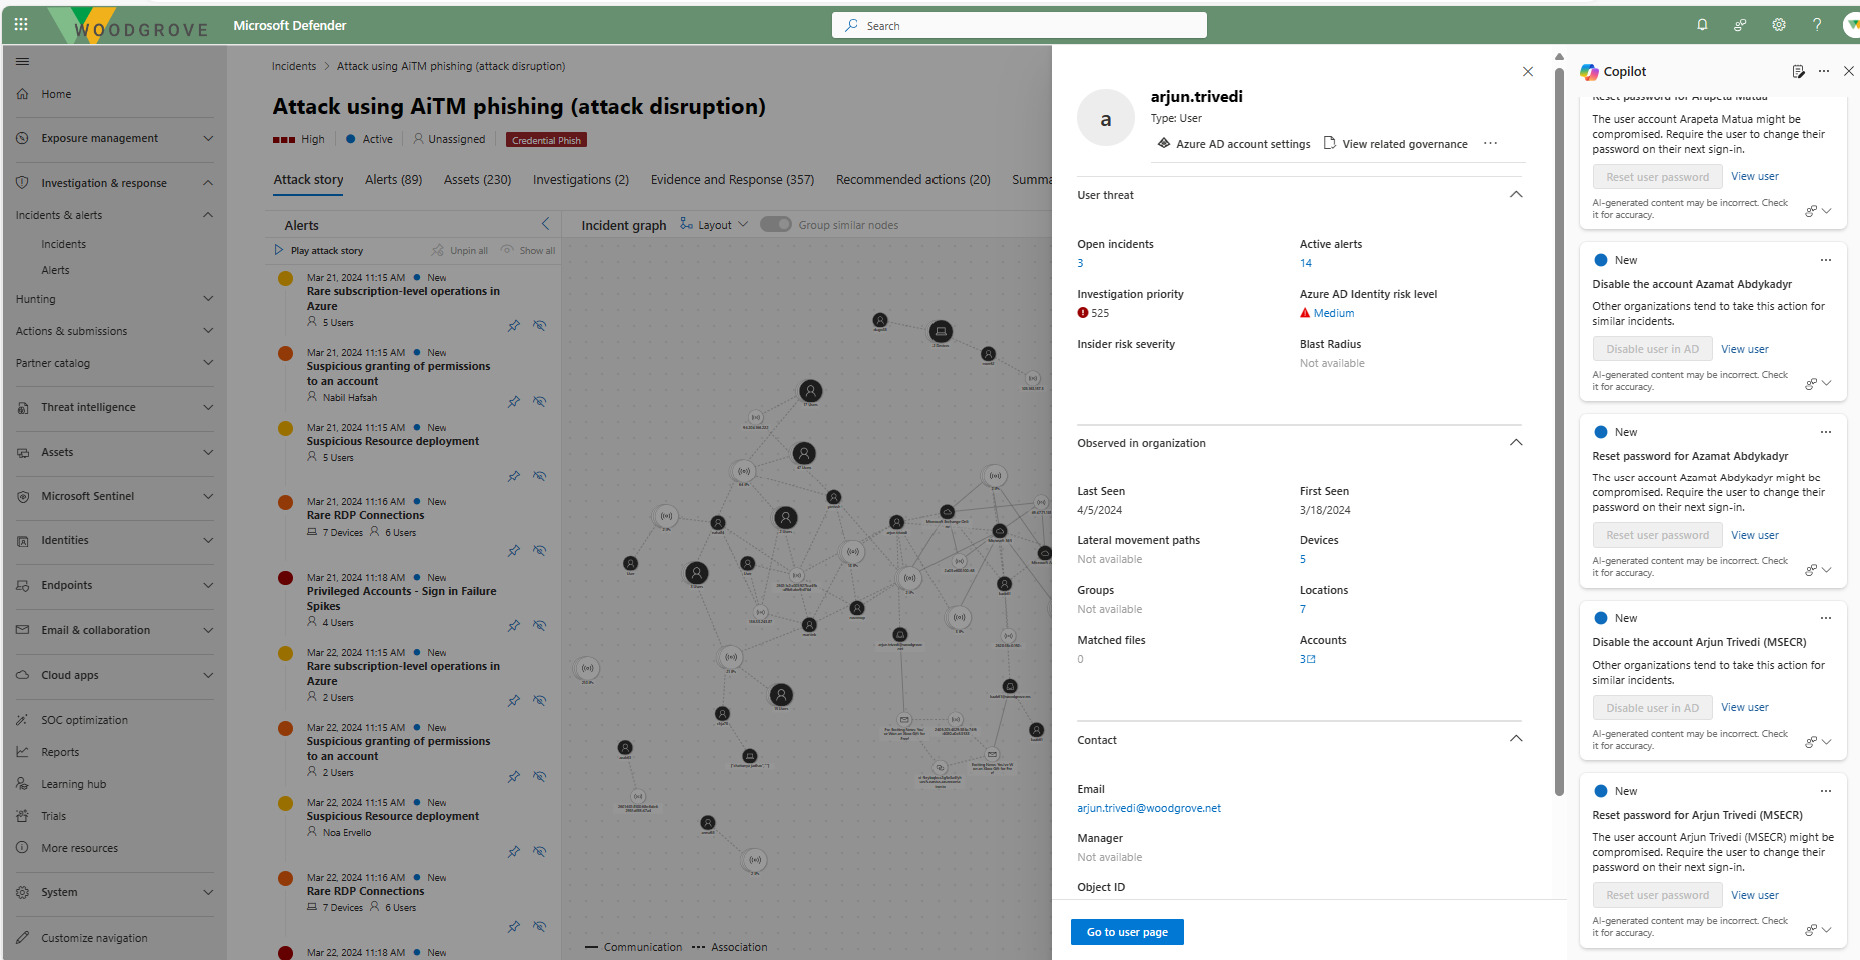
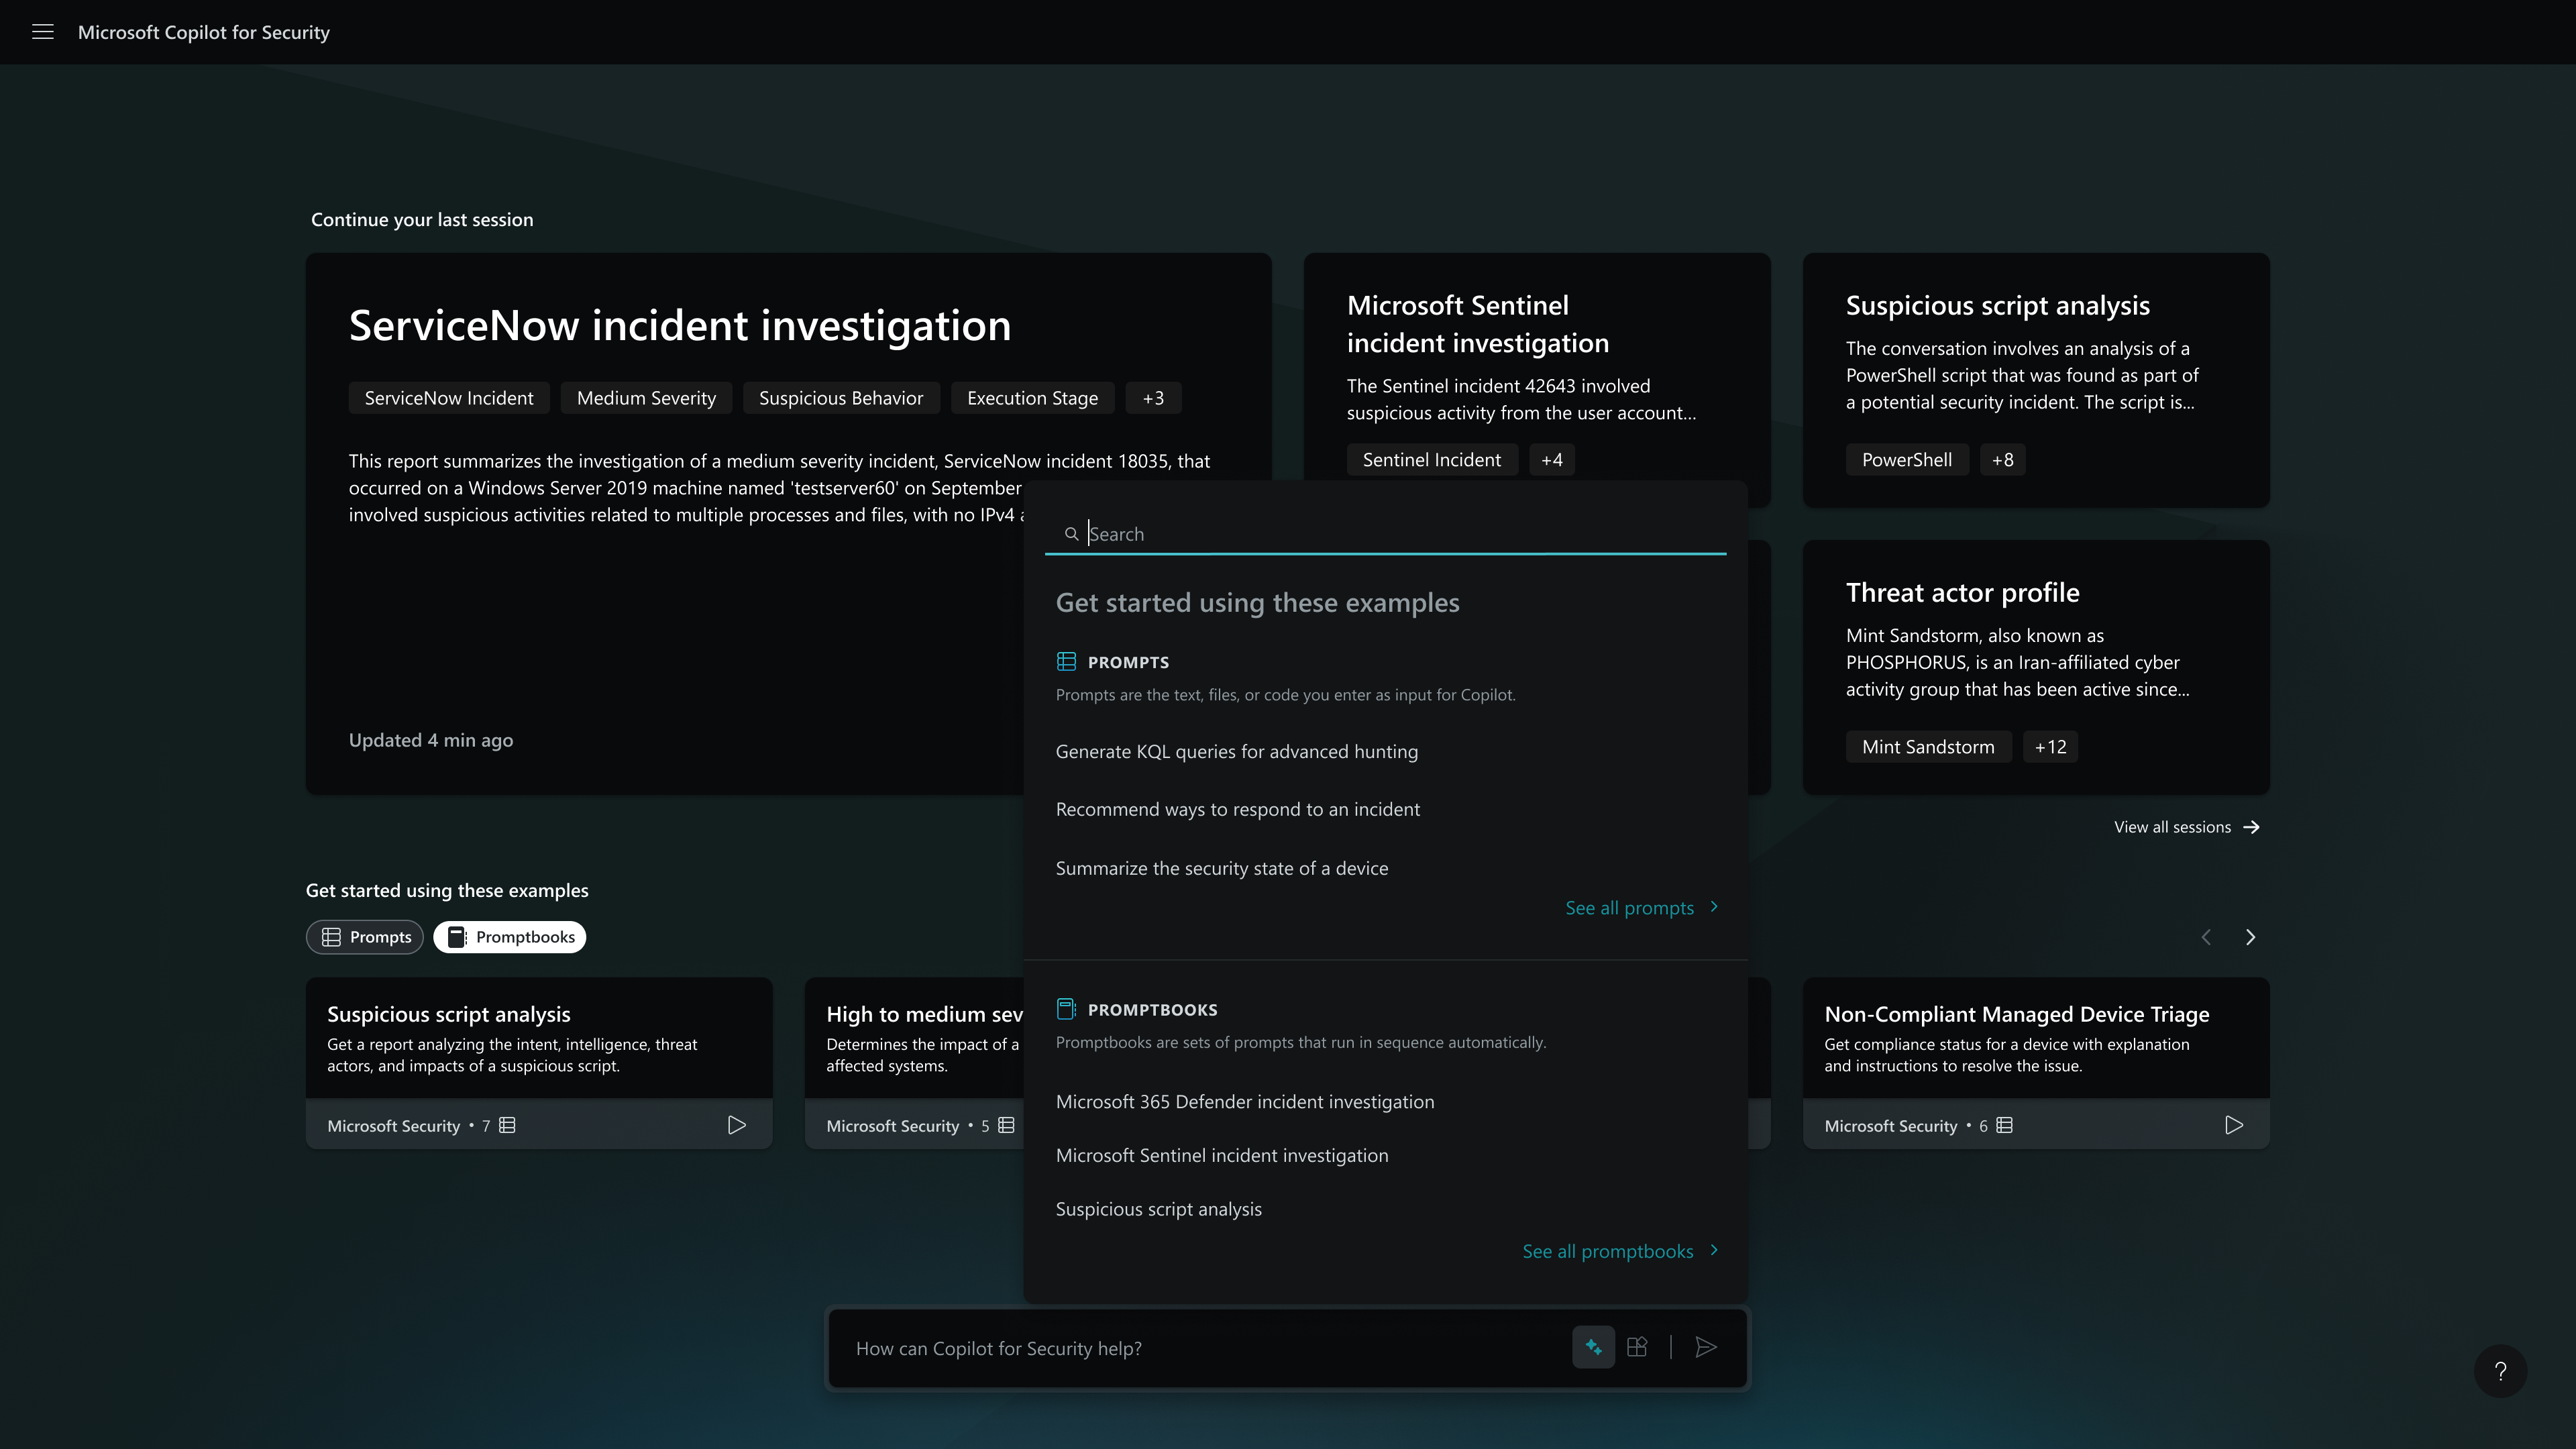
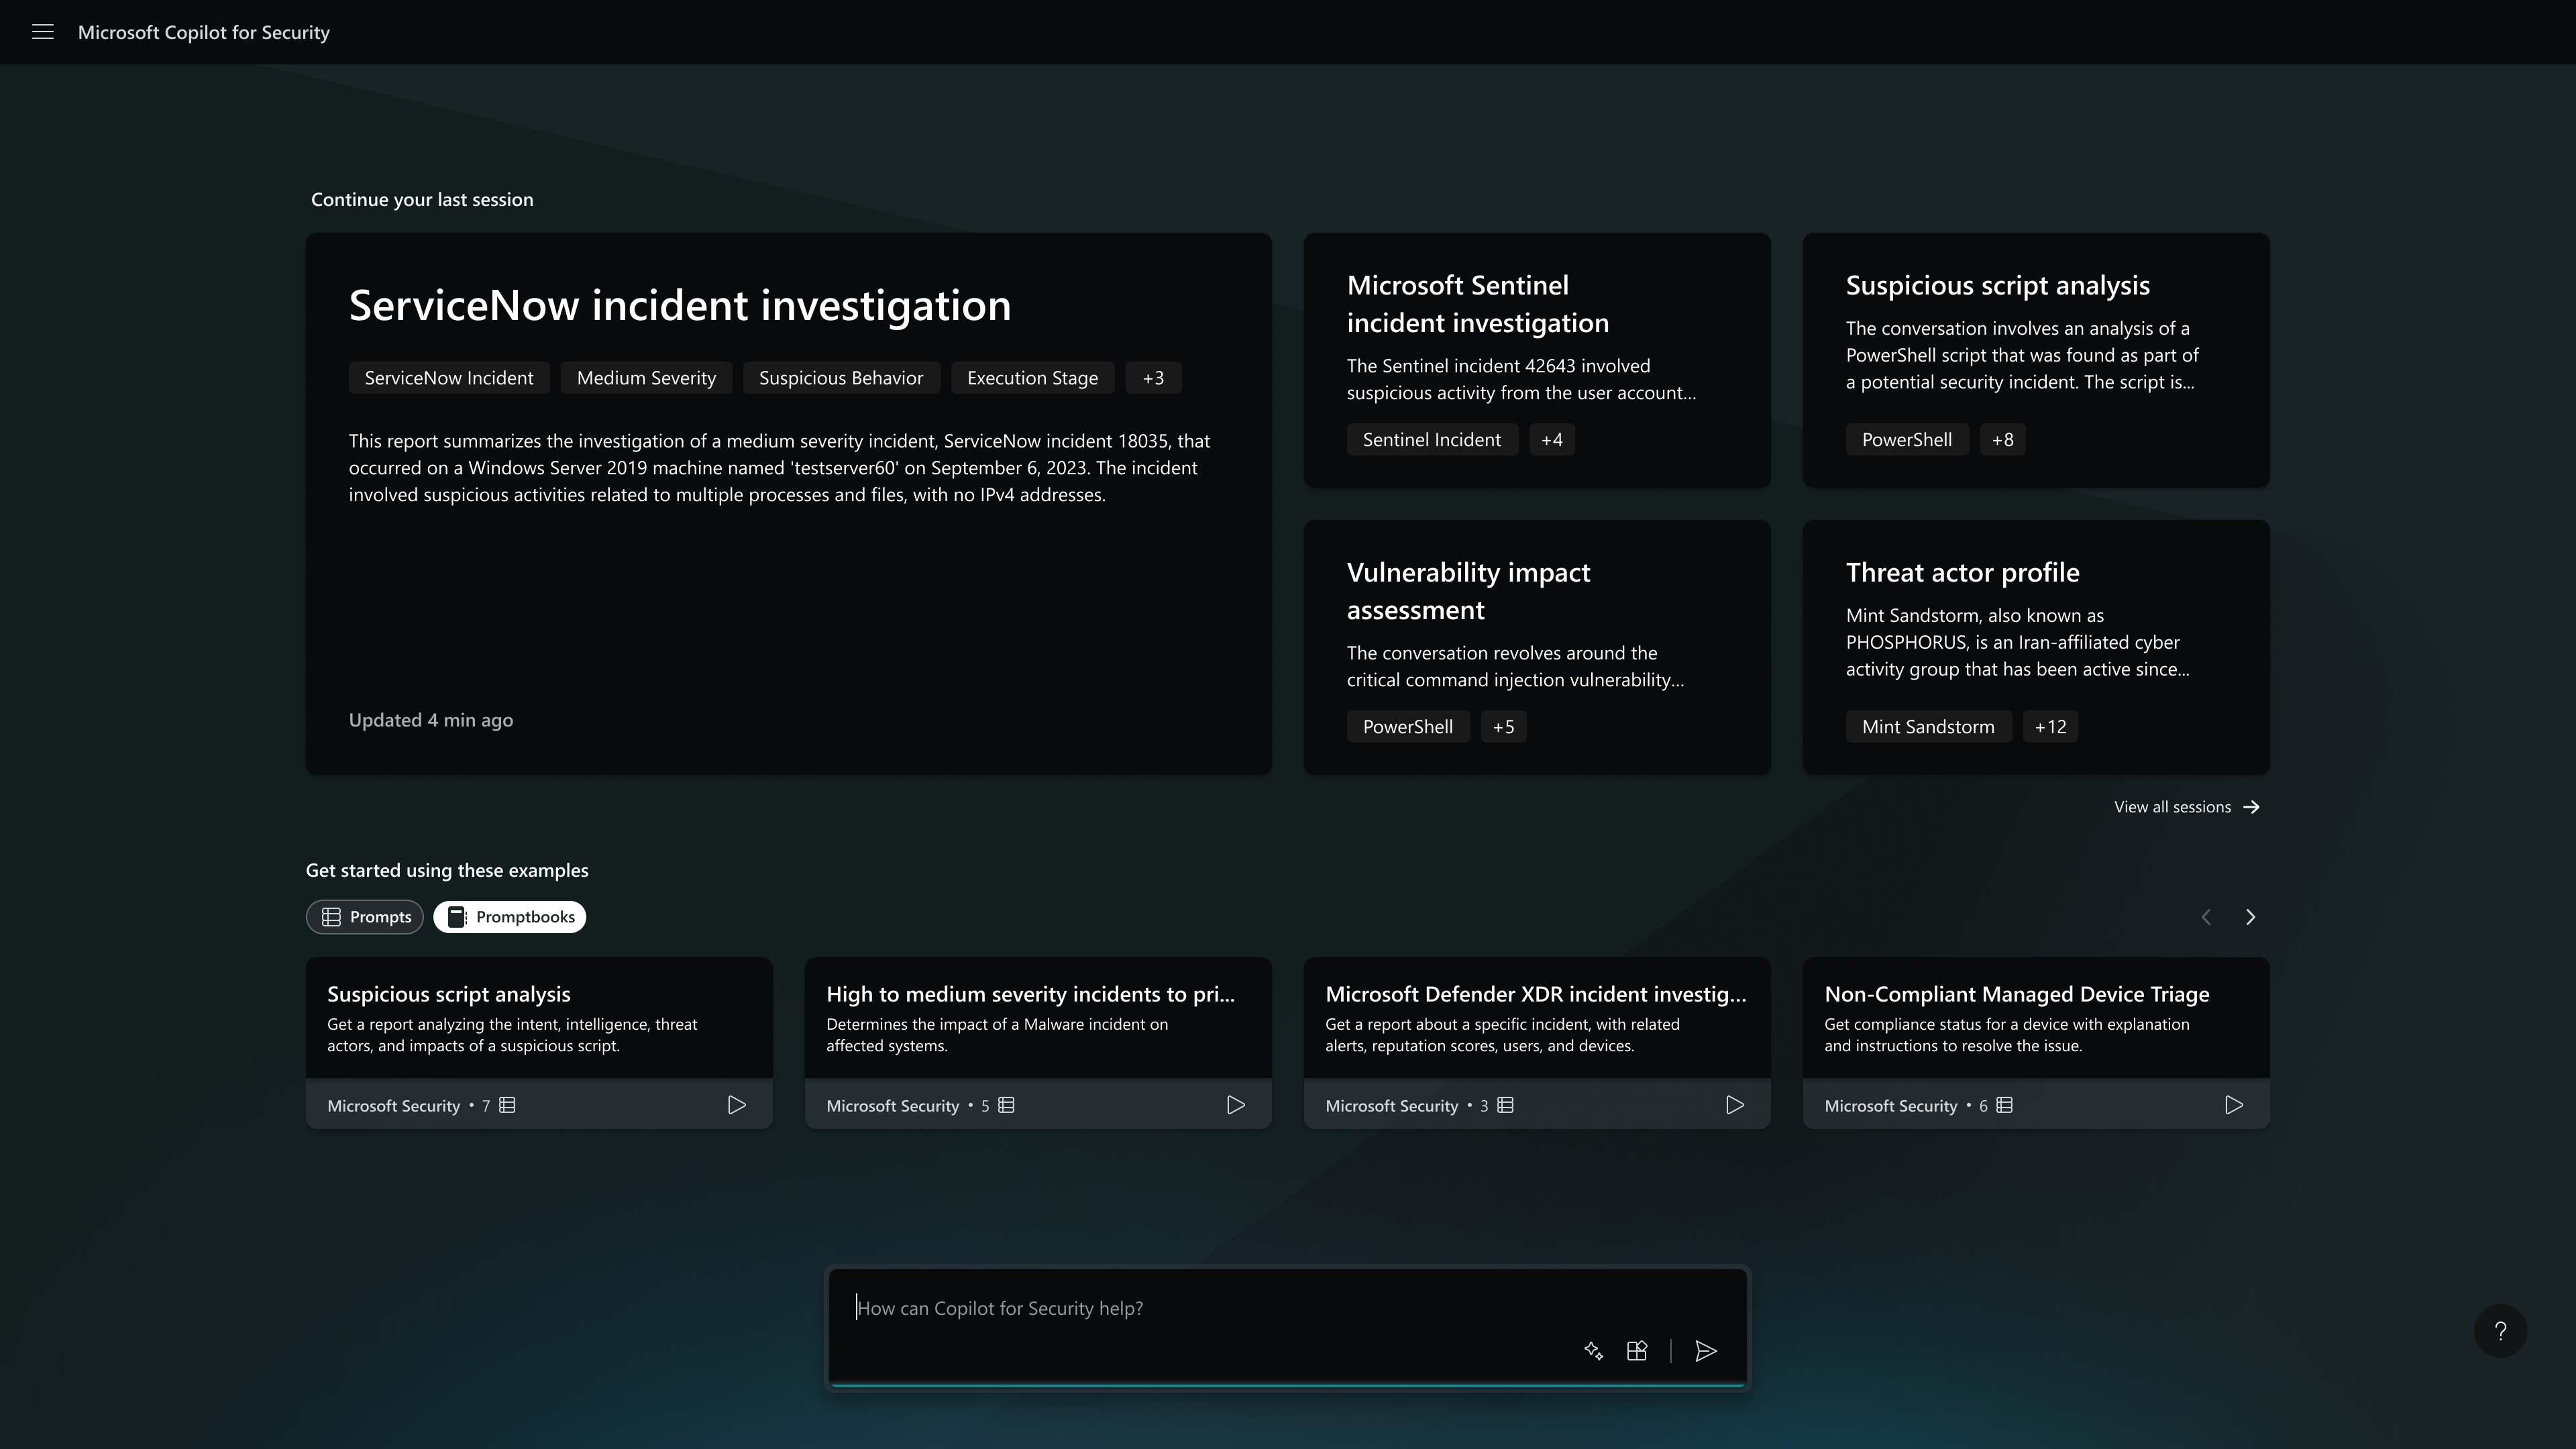
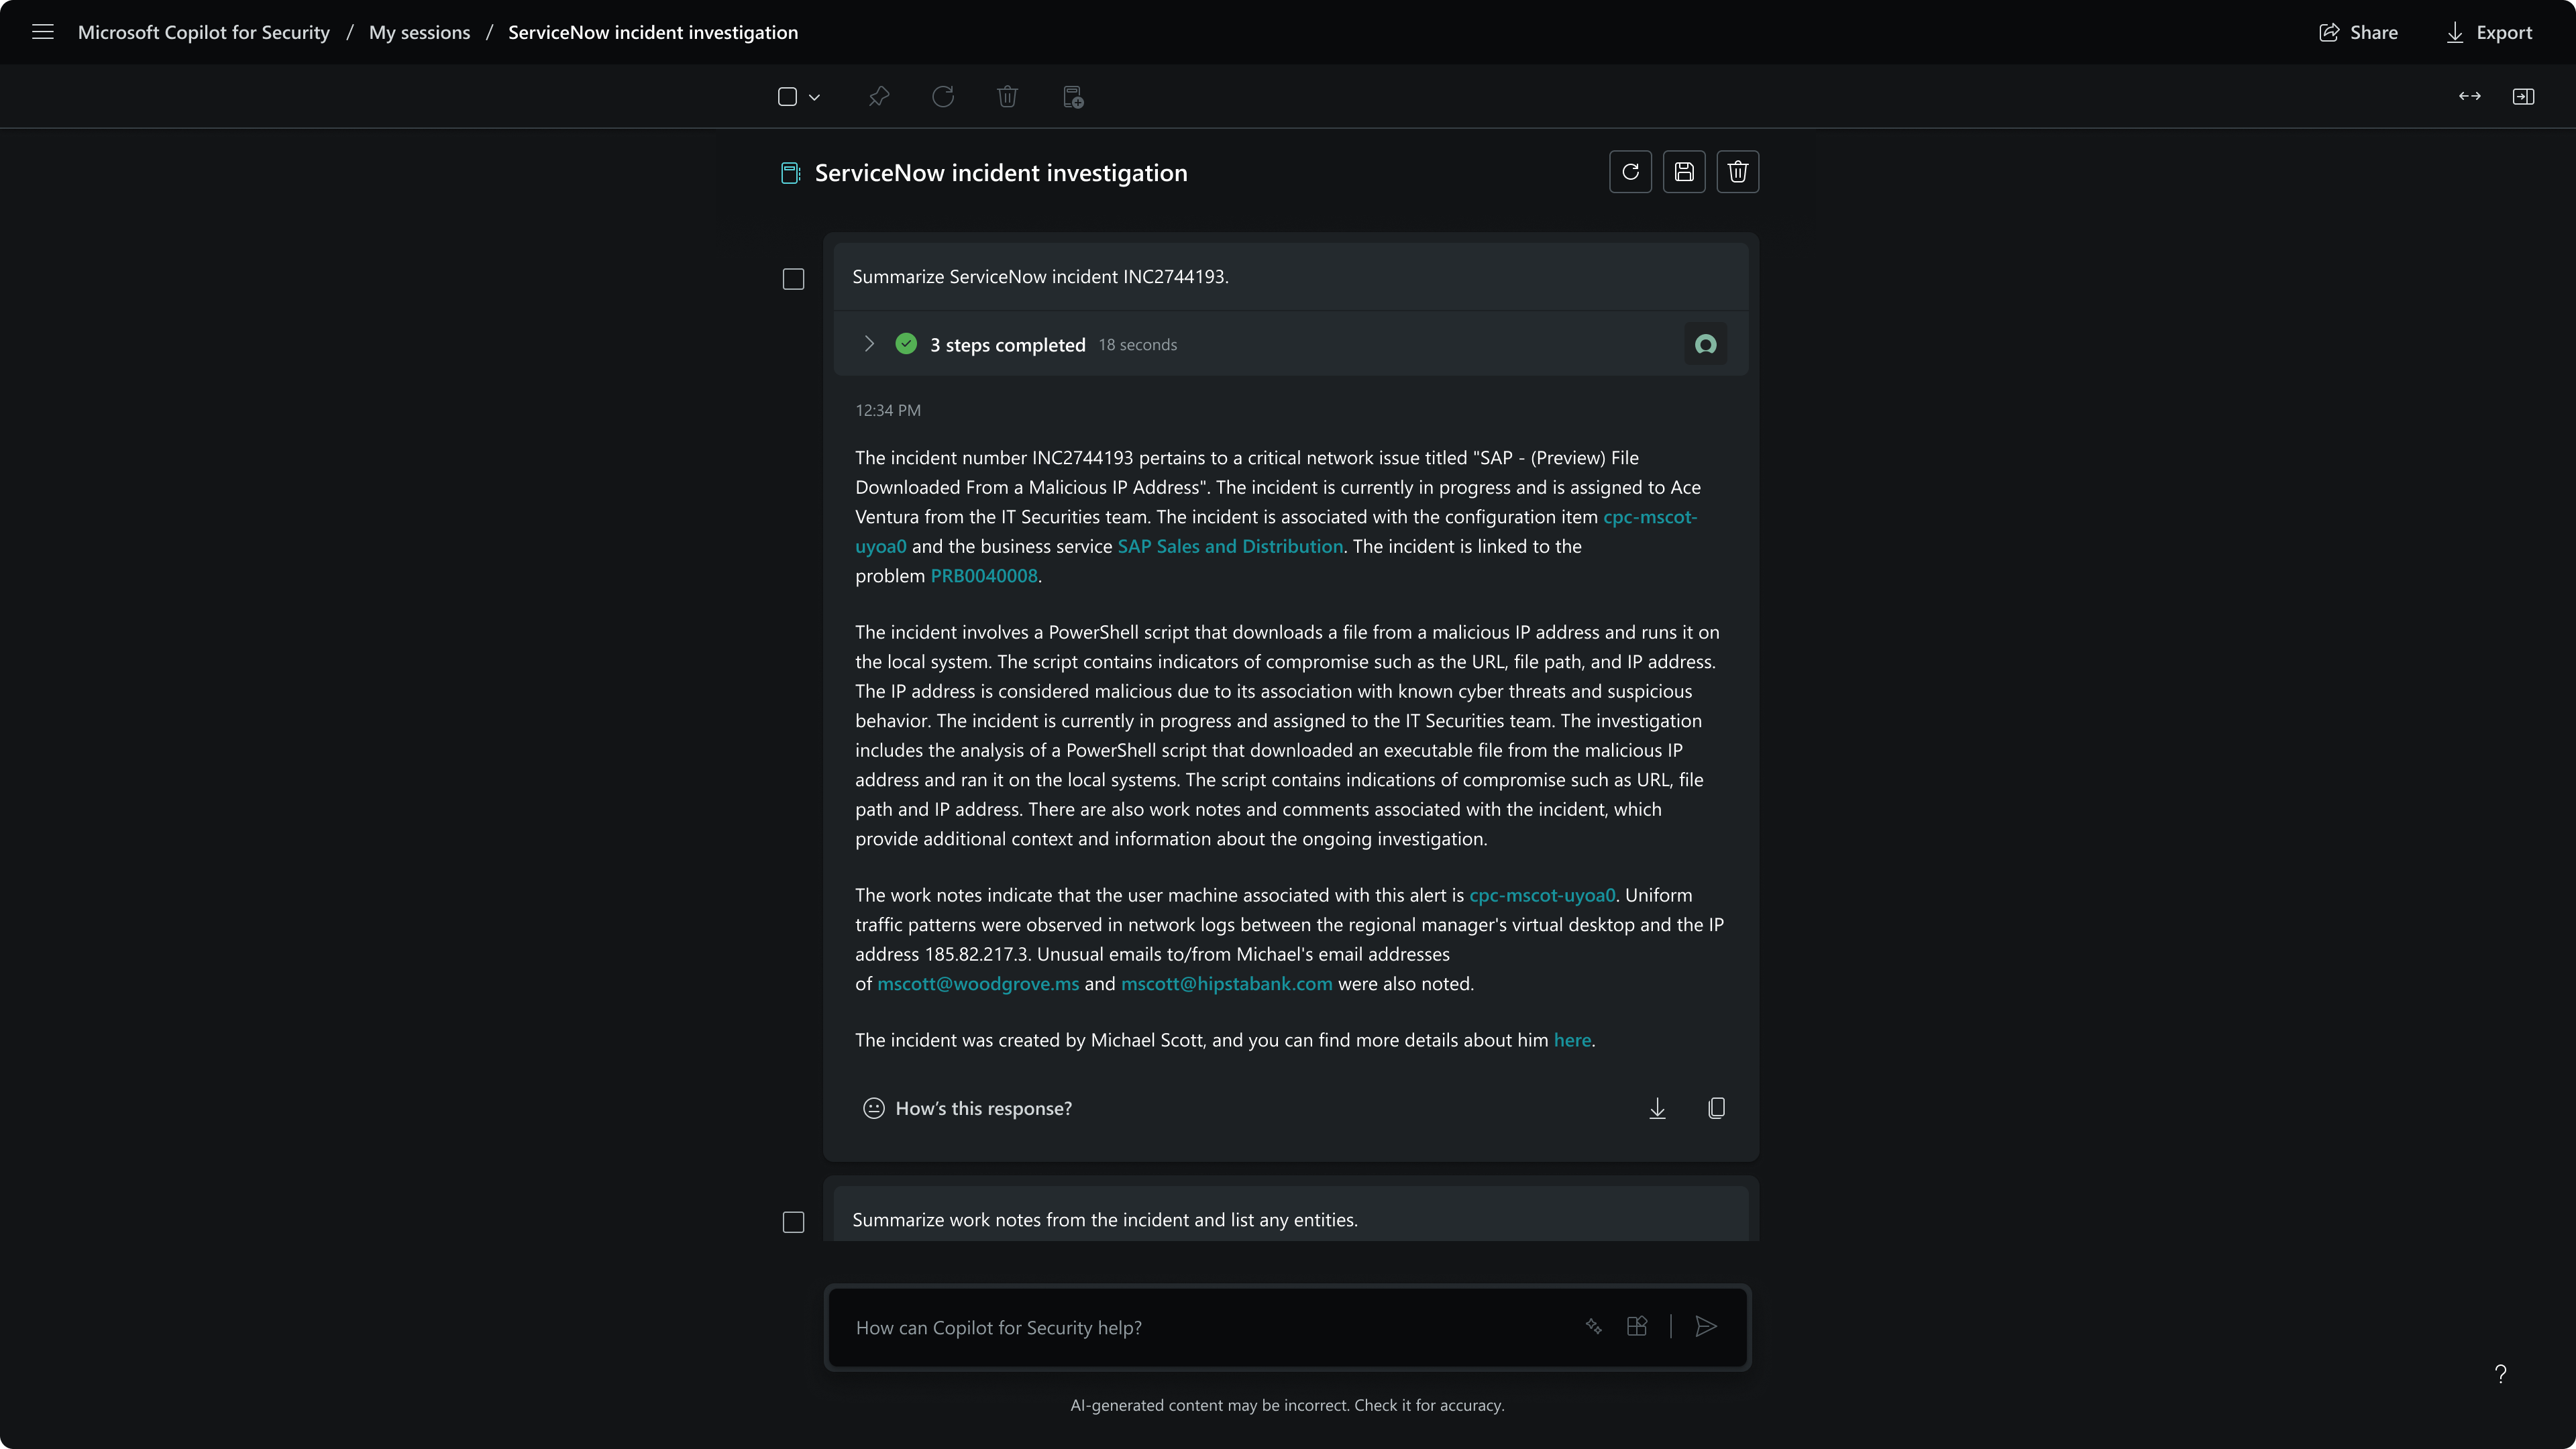
    Screenshot of Defender USX guided responseScreenshot of Defender USX incident summaryScreenshot of the homepage - capabilities menuScreenshot of the homepageScreenshot of MDTI threat intelScreenshot of session - incident summary