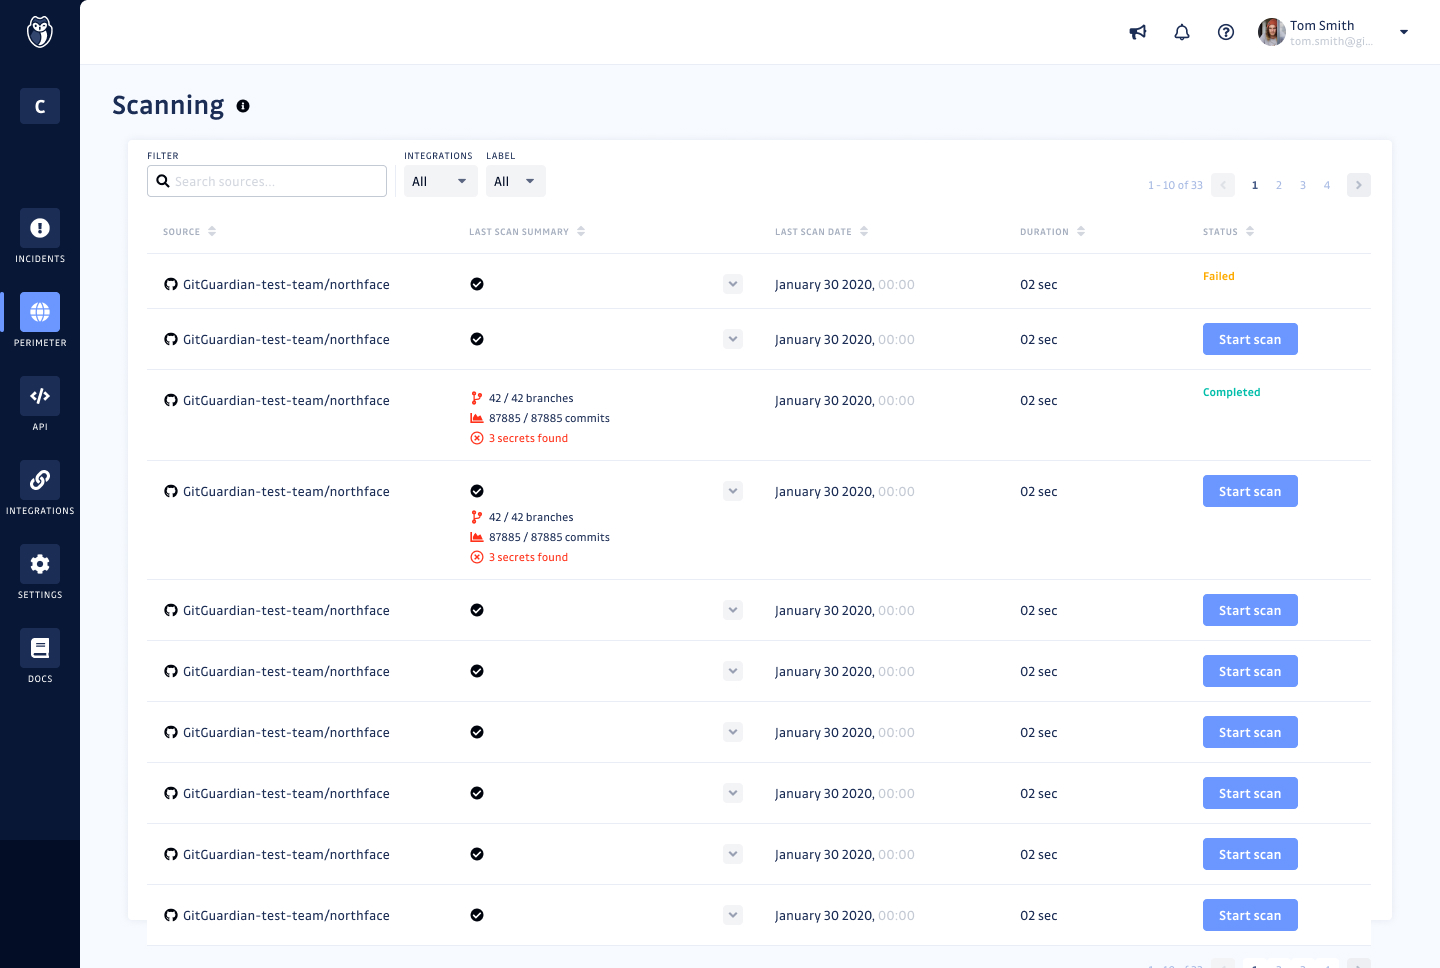
GitGuardian is an end-to-end NHI security platform designed to help organizations strengthen their Non-Human Identity (NHI) security posture and address compliance standards and regulations. As attackers increasingly target NHIs, such as service accounts, service principals, and applications, protecting and managing these critical assets has become paramount. NHIs rely on “secrets” like API keys and certificates for authentication, and their rapid proliferation has led to significant…
$0
(for individuals or up to 25 devs)
OneTrust Privacy Automation
Score8.1 out of 10
N/A
The OneTrust Privacy Automation solution is used to simplify compliance, improve operational efficiency, and enable risk-informed decisions.
I do think it'll absolutely fit everyone who codes integrates with another platform or services. We all forget that one credentials one in a while, and especially those who managed public repository, it is important to keep an eye on accidentally committed credentials. While I think you don't really needs it for personal project, it's a nice to have, you don't want to waie up to 50k USD of sudden surcharge on resources you don't use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I strongly recommend it for general management of personal data privacy programs and risk and contract management, it complies with all major world legislation in addition to being easy and fast. Not recommended for data discovery still requires refinement.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian monitors every public or private GitHub commit ( that have GitGuardian installed) and event in real-time for secrets and sensitive data. In a leak scenario it immediately notifies us.
It uses sophisticated pattern matching techniques to detect credentials that cannot be strictly defined with a distinctive pattern (like unprefixed credentials)
It covers several API providers, database connection strings, private keys, certificates, usernames and passwords etc
GitGuardian have high True Positive Rate of around 91% and reduces alert fatigue with smart occurrences regrouping
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved user interface: It would be beneficial to have a more intuitive and user-friendly interface for Internal Monitoring on GitGuardian. This would make it easier for users to quickly access the data they need and understand the results of their scans.
Automated alerts: It would be helpful to have automated alerts when certain conditions are met, such as when a scan reveals sensitive data or when a new repository is created. This would help users stay informed and take action in a timely manner.
More detailed reports: Currently, Internal Monitoring reports are limited in terms of the depth of information they provide. It would be useful to have more detailed reports that include additional metrics, such as the number of repositories scanned and the types of sensitive data found.
Faster scan times: Scan times can be slow at times, making it difficult to stay on top of changes in repositories quickly. It would be beneficial to have faster scan times so that users can take action quickly when needed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have used a shared hosted tenant managed by OneTrust for over three years with only one instance of a lengthy (4+ hours) unexpected outage which happened years ago.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We selected a European hosting location based on our initial use case, however, our usage of the OneTrust platform has expanded globally to where the majority of users sit in the Americas or Asia-Pacific regions. There is a noticeable lag when navigating the platform for users located far away from the hosting location.
As a user, you can mitigate any sluggish response time by the aggressive use of multiple browser tabs. I commonly have one tab open on an Inventory detail screen, another tab on an Assessment window, and maybe another tab on a customized inventory list screen. If one tab is slow I hop to another tab and work on that tab while the first tab responds.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Both our customer rights access and cookie consent advisors were responsive and helpful in getting us trained on using the platform and the various assets implemented on our website. We had multiple training sessions that were more than enough in getting all of the users on our team familiar with what we needed to do.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
An implementation specialist worked with us remotely during our initial deployment. Due to the diverse geographic locations of my organization's participants, the implementation and training had to be done remotely (this was before COVID-driven remote work).
The implementation specialist was knowledgeable and helpful but to really get full benefit from the platform I encourage organizations to dedicate a specialist within your company to really study and learn the platform.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I've evaluated quite a few other tools, like git-secrets, Git-leaks, scan, and maybe a few more. They're all great but quite surprisingly none of them detected Github OAuth Secrets for us. A lot of the FOSS tools out there focus on much simpler, generic secrets, which is good in itself but with GitGuardian, it was dead simple from day one. I just connected our Github Account and set up the gg-shield cli and that was all.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
First, when we compare OneTrust Privacy and Data Governance Cloud to the software I mentioned above, OneTrust Privacy and Data Governance Cloud software was way more affordable than the other 2. Also, along with the other 2 software, OnTrust was one of the most user friendly tool/software we've ever used.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The platform has exceptional capabilities to customize the user interface, reports, and recorded information. In most cases, the customization can be compartmentalized so that if the customization performed for Department A is determined to not impact Department B, the customization can be hidden from Department B.
We have four different departments using the IT Risk Management module. Three departments share their work in what we call the 'shared data risk management zone'. Another department is using IT Risk Management for a bespoke portfolio risk management task, and the customization for this department is largely hidden from the other departments.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
GitGuardian Internal Monitoring has had a positive impact on our overall business objectives. By providing visibility into our code repositories and alerting us to potential security risks, we have been able to identify and mitigate security issues before they become a problem. This has allowed us to focus more on developing our product and less on responding to security incidents. We have also seen an increase in customer confidence in our product as a result of using GitGuardian Internal Monitoring, which has led to increased customer loyalty and retention. Overall, the ROI of using GitGuardian Internal Monitoring has been very positive for our business.
We have seen an increase in the security of our codebase, as well as an improvement in the speed and accuracy of our code reviews. This has enabled us to quickly identify and address any potential security issues before they become a problem. Additionally, we have seen an increase in our ROI as a result of using GitGuardian Internal Monitoring, as it has allowed us to save time and money by preventing costly security breaches.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info