JetBrains supports .NET development with Rider, a .NET IDE based on the IntelliJ platform and ReSharper.
$14.90
per month per user
SonarQube
Score8.7 out of 10
N/A
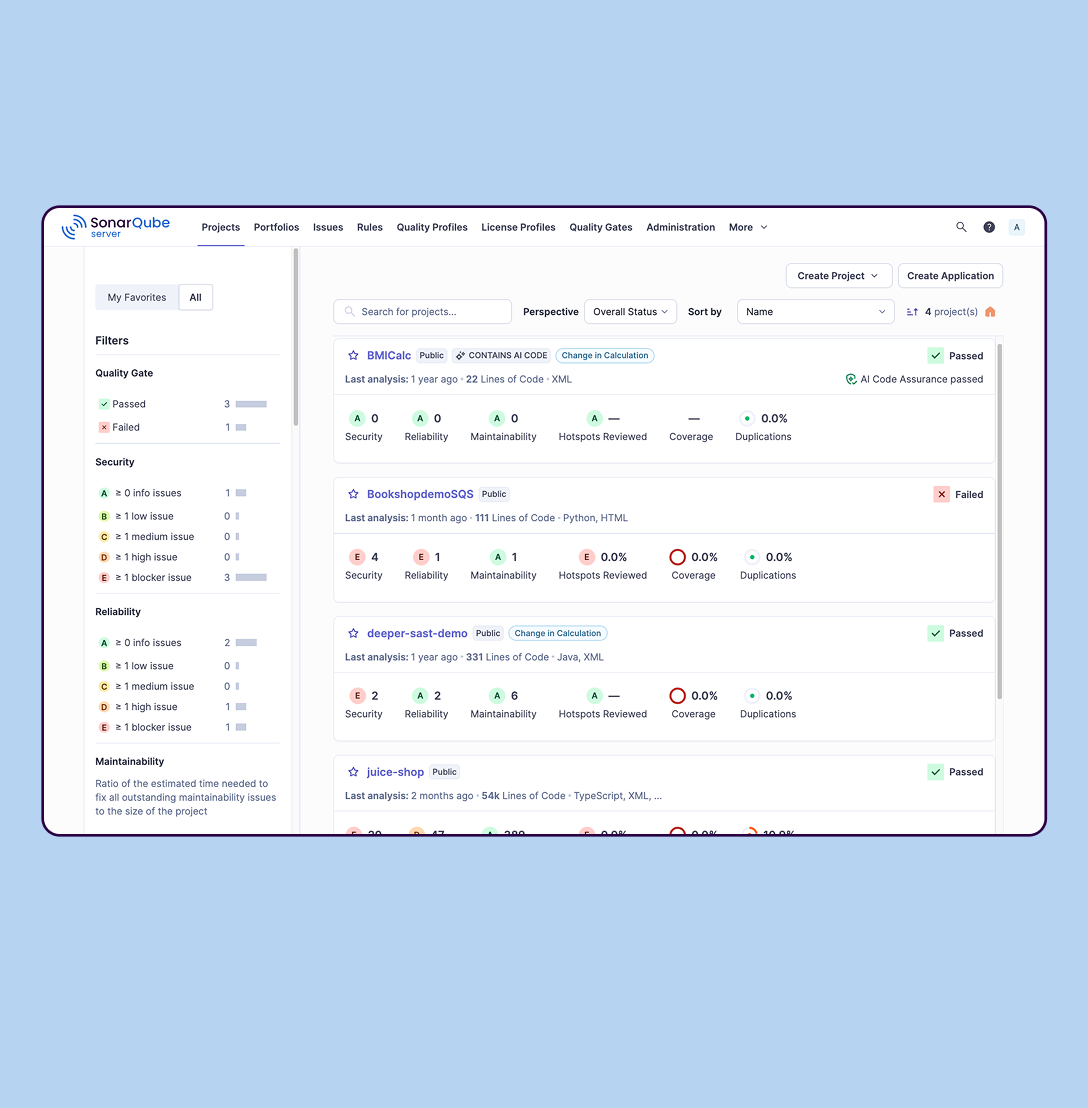
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
$34
per month Recommended for teams <50 developers
Veracode
Score8.5 out of 10
Mid-Size Companies (51-1,000 employees)
Veracode provides advanced application security solutions, trusted by enterprises to develop and maintain secure software. Its platform identifies exploitable risks, speeds up vulnerability remediation, and reduces security debt at scale using a proprietary AI-assisted remediation engine.
N/A
Pricing
Rider
SonarQube
Veracode
Editions & Modules
For Individuals
$149
per year per user
dotUltimate for Individual
$169
per year per user
All Products Pack for Individuals
$289
per year per user
For Organizations
$419
per year per user
dotUltimate for Organizations
$469
per year per user
All Products Pack for Organizations
$779
per year per user
SonarQube Community Build
$0
(open source)
Self-managed: Developer
Starting at $720 annually
per year per installation
Self-managed: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Enterprise
Contact sales for pricing
per year per installation
Cloud-based: Teams
Starting at $34 per month
per month per installation
Self-managed: Data Center
Contact sales for pricing
per year per installation
No answers on this topic
Offerings
Pricing Offerings
Rider
SonarQube
Veracode
Free Trial
Yes
Yes
Yes
Free/Freemium Version
No
Yes
Yes
Premium Consulting/Integration Services
No
No
Yes
Entry-level Setup Fee
No setup fee
No setup fee
No setup fee
Additional Details
dotUltimate: All .NET tools, ReSharper C++ and JetBrains Rider, together in one pack
Tech Lead in Information Technology at Andreani Grupo Logístico (Package/Freight Delivery, 5001-10,000 employees)
Chose SonarQube
SonarQube is more focused on code quality, whereas Veracode does a better job of finding security vulnerabilities. We lean towards SonarQube because we are looking for quality.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose SonarQube
Sonar Qube doesn't do as good of a job of finding security vulnerabilities as dedicated SAST software, but it does more for code quality that the developers want to see. A comparison of Sonar Qube to something like Veracode or Fortify isn't apples to apples since they're not …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose SonarQube
Visual Studio has some nice code analysis tools, most which can be activated at development time.
But they have some shortcomings and using an external tool allows catching issues that were not seen during development.
Using this dual approach makes for a more robust application …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Senior Software Engineer in Research & Development at SRB Education Solutions Inc. (Acquired by PowerSchool) (Information Technology & Services, 501-1000 employees)
Chose Veracode
Sonar cube was quicker, but not as thorough. Both integrated into our CI/CD pipeline, however the integration for Veracode is more straight forward.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
SonarQube doesn't have the required code scanning vulnerability detecting service.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
I have used SonarQube for code quality and security analysis in the past, but Veracode's Software Composition Analysis analysis makes a big difference in terms of identifying vulnerabilities in dependencies. It would make it a lot easier if the IDE plugin could show the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Manager, Information Technology in Information Technology at Broadcom Inc. (Computer Software, 10,001+ employees)
Chose Veracode
Earlier in our organisation, Fortify was used (formerly from HP but now owned by Micro Focus). The general consensus was that there was too much noise (false positives), taking a lot of time to find and then fix the real issues.
SonarQube is also used in our organisation but not …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
SonarQube or Sonar Cloud focuses on scanning for coding good practice and code security is not covered as extensively as Veracode. SonarQube is free but required installation on an on-prem server. Subscription to Sonar Cloud (Saas version of Sonar Qube) is cheaper but does not …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
SonarQube is faster and can be free, but the security scanning capabilities are a joke compared to Veracode. Unlike SonarQube, Veracode goes deeper into finding a very wide variety of vulnerabilities and best practices that should be applied to software and provides reporting …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
VP, System Operations and Security in Information Technology at VirTrial (Hospital & Health Care, 11-50 employees)
Chose Veracode
SonarQube is a great general code quality analyzer, and we do use it as a companion to Veracode. However, it's not security-focused and tends to have a higher false-positive rate for security issues it flags. It's also not as easy to generate reports from the findings unless …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
DevSecOps Engineer II in Engineering at Helpshift (Information Technology Services, 501-1000 employees)
Chose Veracode
Veracode takes compiled code, so integration, regression based test cases can be evaluated well. Now, it has lot of features ranging from API sec to DAST, so have a code which is well working in live env is very essential to setup and hence giving us an edge over other tools. …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
Veracode is much better at uncovering security weaknesses and providing information and consulting. I use Veracode because our company decided for.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
The maturity of the Veracode and the continuous improvements in its products it's one of the principal characteristics of chosee it, Veracode it's a SaaS platform and was born in the cloud, so this is a great option for our clients to be quick to implement also the easy of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
Once we learn how to use Veracode, its simple and very efficient tool to include in any of your devops environments like Dev, QA, Staging , UAT etc. The configuration is much simpler compared to others. The Enterprise license cost is also competitive compared to others. The …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
Veracode has a very good integration within its products, which makes it easy for a developer. Veracode helps in providing support both actively and through resources on their platform to remediate and fix the issues found in one's application. The reporting section being …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Tools and Analytic Monitoring Leader in Information Technology at Entel (Telecommunications, 5001-10,000 employees)
Chose Veracode
Veracode stands out for trusted community results, vendor relationship, and partner channels to support and provide a close relationship. Integration capacity is a good point when deciding to integrate with DevOps framework.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Veracode
Veracode speaks on very practical, actual security issues rather than thousands of code quality issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Initially you may think it’s not worth paying and that there are better free options, which is definitely a lie we once tried to live with. It has everything you may ever need in .NET world, code analysis and debugging works super well and all the SQL/noSQL related integrations are just next level compared to the competition. It’s worth every penny.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Veracode helped us our team's developers in saving time significantly. For instance, if I take a library and assume it's going to work until it reaches QA or UAT, where we find out there's a vulnerability, that can require extensive effort for code refactoring or redesigning; Veracode helps prevent that before the pull request is merged.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
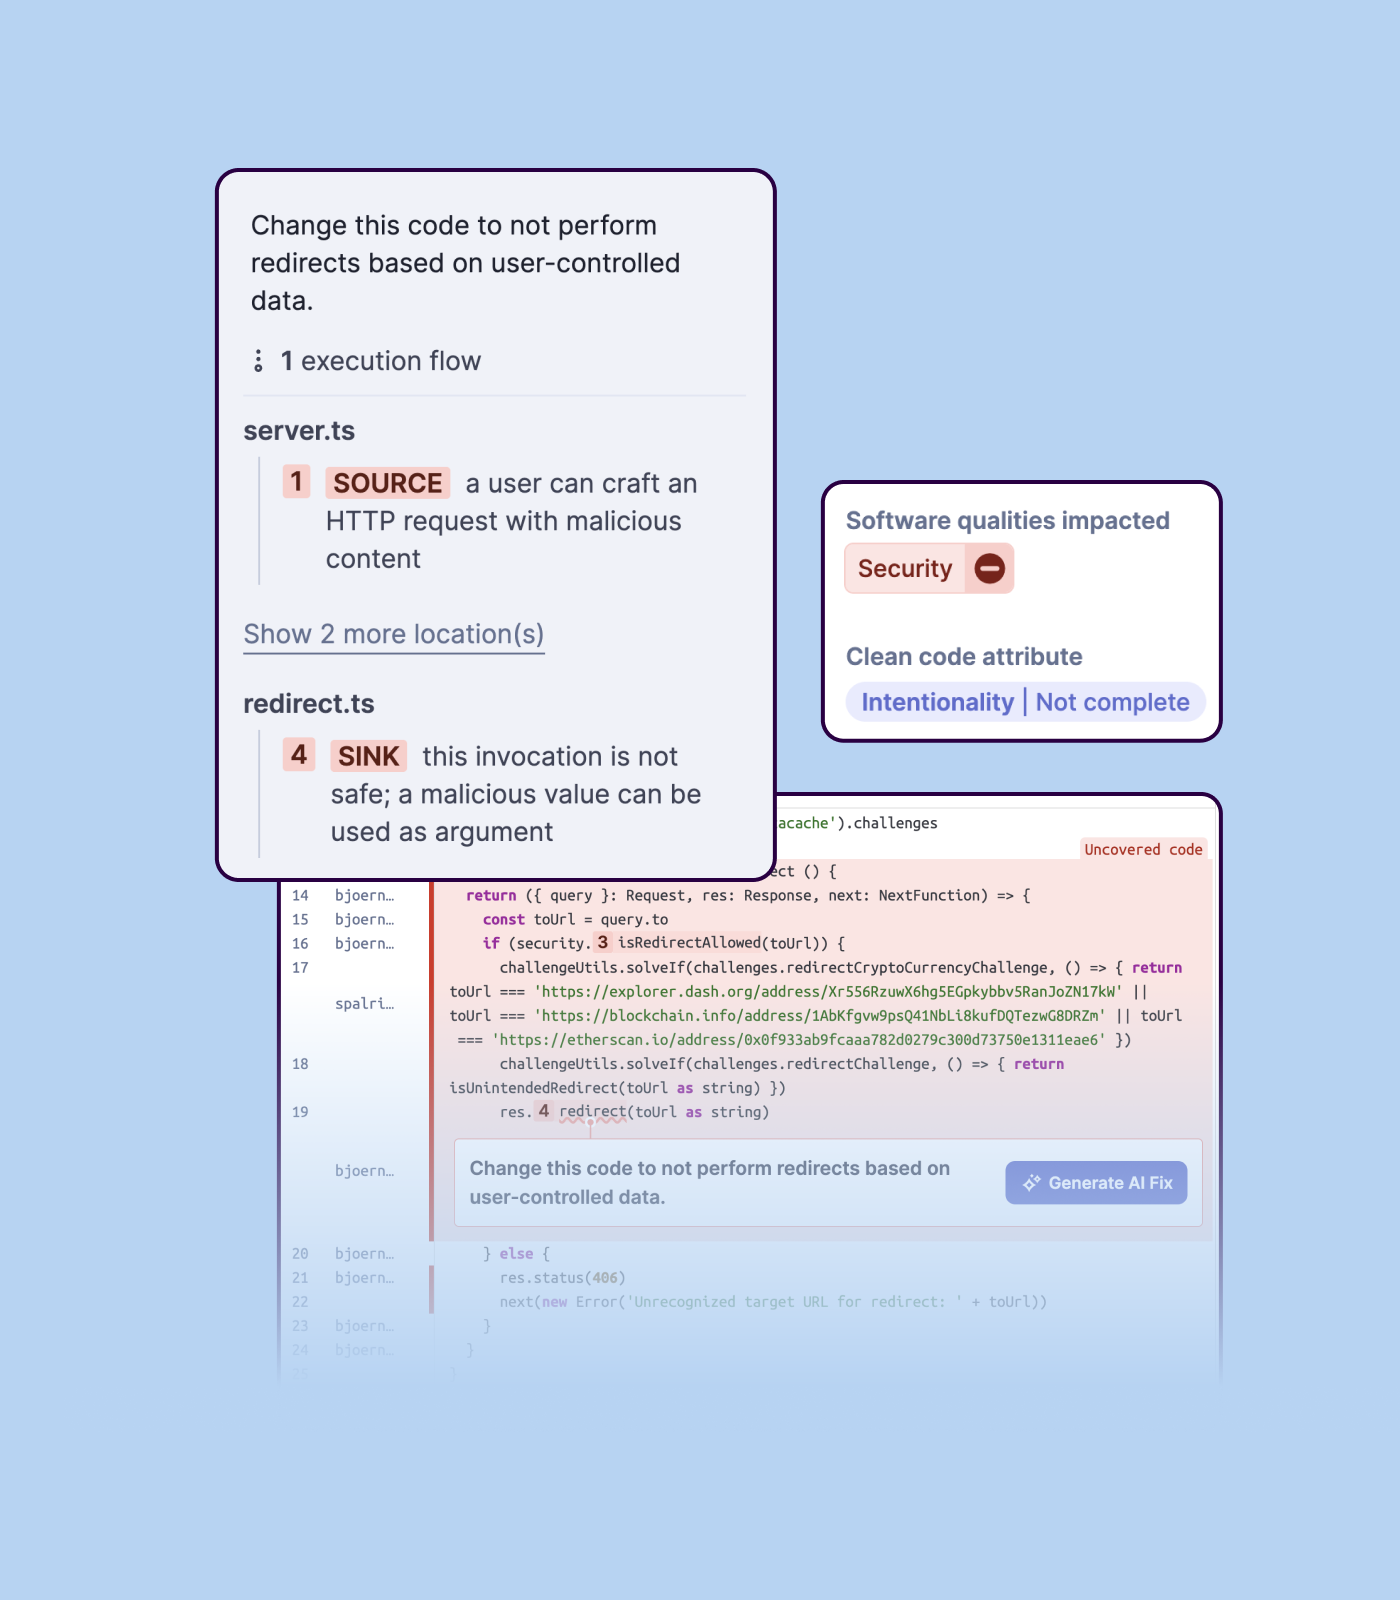
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
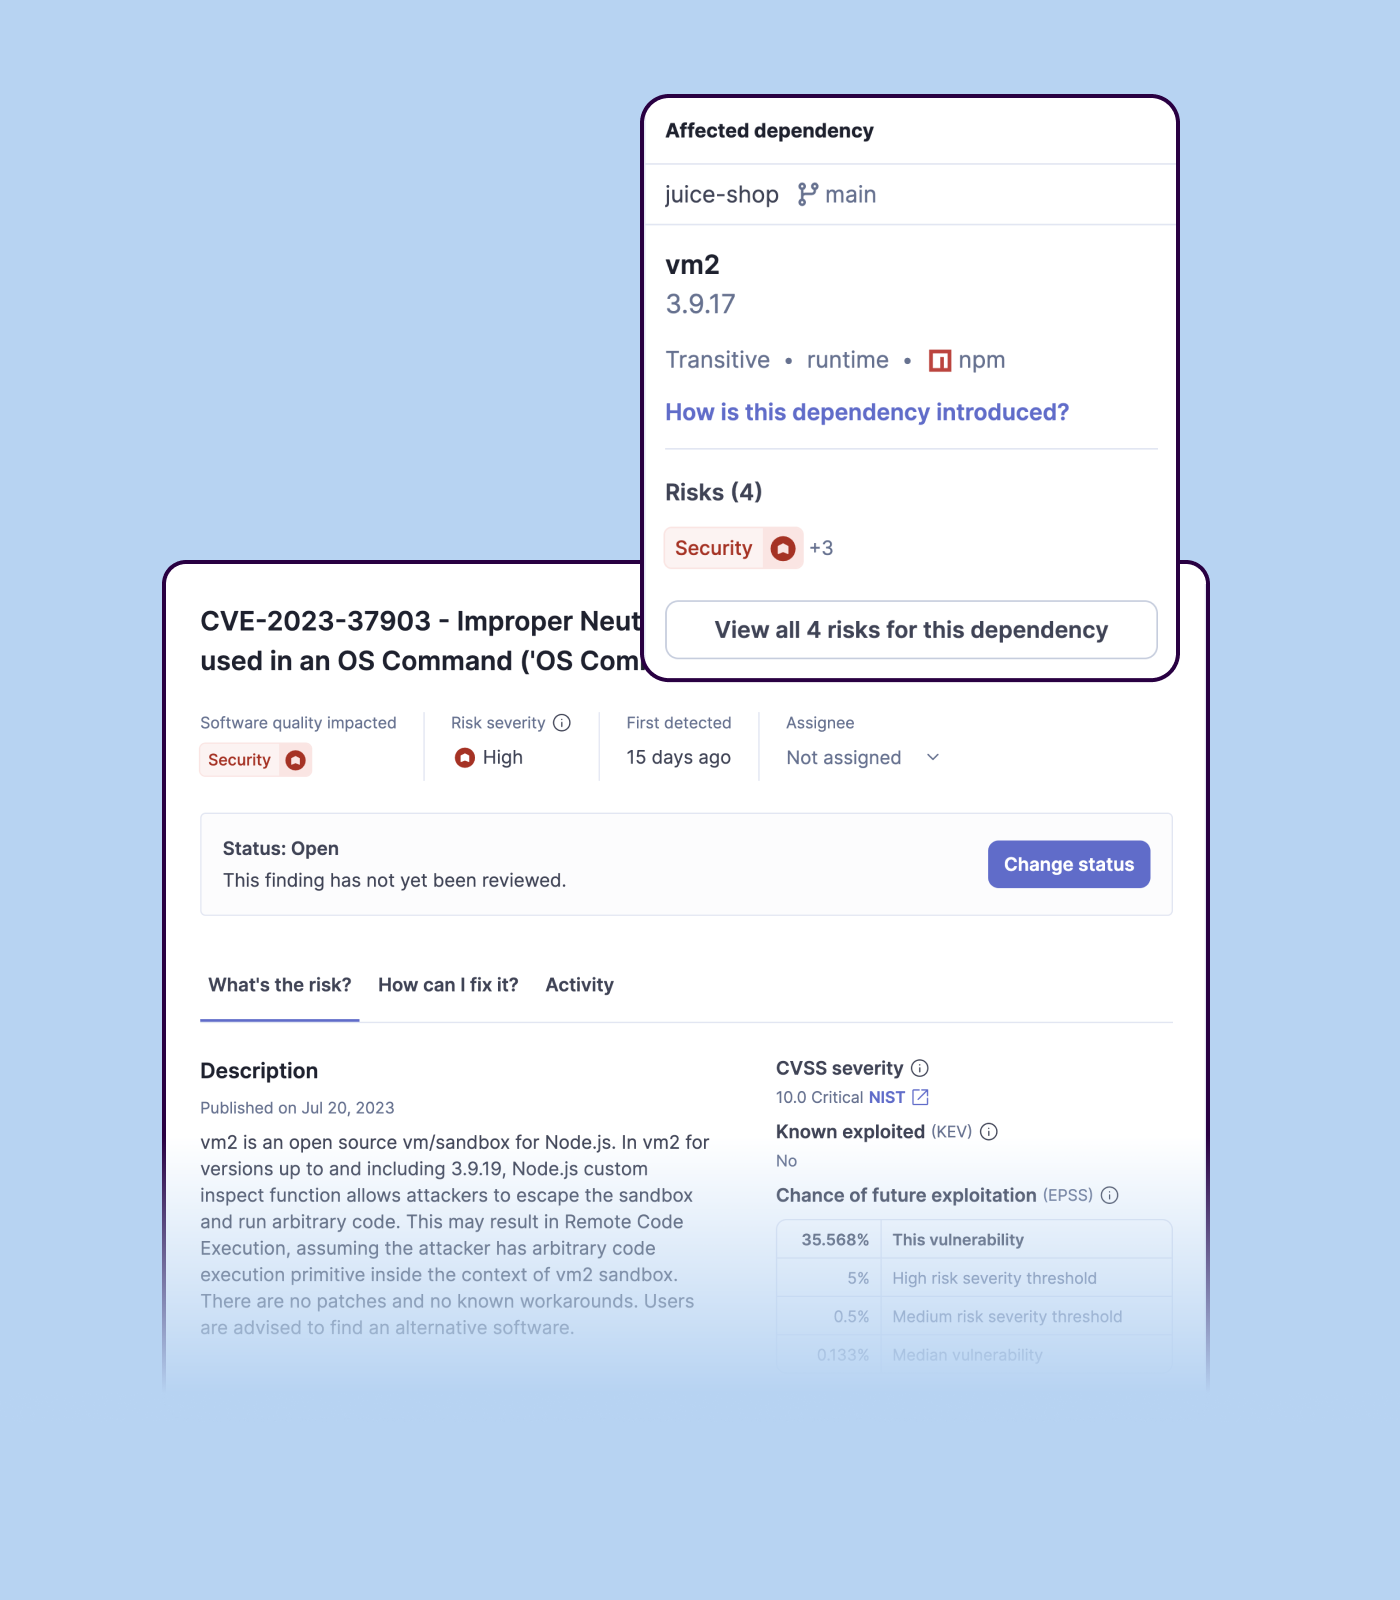
It is good at recommending fixing issues with third-party dependencies used in application code with detailed version information and knowing which version fixes what.
It has a very nice interface for triaging flaws. One can sort the vulnerabilities found in code from Very Likely to be exploited to least likely to be exploited.
There is a collections feature that allows us to group together groups of application profiles belonging to the same suite of applications.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
At this time, and we just renewed a month ago, I dont see any products out there overall that can offer what Veracode does. Yes, its not cheap by any means, but for the money its the best application security scanning tool out there.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Rider is a great IDE with extensive C# refactoring support and .NET-specific knowledge. This is great for building .NET applications but for our purposes, the Unity specific suggestions are really helpful.
JetBrains Rider is great as an editing and debugging environment. It reliably connects to the Unity editor and allows debugging, which some IDEs are not as reliable at doing.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
- Almost no setup required and easy to configure - Very easy to use, intuitive UI with integrated analytics and learning portals. - Seamless to review the results, triage them, generate reports. - Security progression of the product/application is tracked via successive scans. - Privileges/Roles nicely fine grained and tightly controlled to let teams "view" only their products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The support forums and knowledge base are extensive and the JetBrains support staff respond quickly to new posts and help resolve issues. There is also a publicly accessible issue tracking system, which allows you to stay on top of any bug fixes or enhancement requests.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Overall, Veracode support is helpful, community support is great, and documentation is available for self-service. Our Customer Success Manager is very helpful and reaches out regularly to see if we need assistance. We have not utilized many of the other resources offered by Veracode, however, in the future we would like to leverage secure coding training for our Development teams.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We use it as a SAS service, so really just getting our teams to mold the use of Veracode into their SDLC has been a process of years in the making. It comes down to what your teams are ready and willing to accept and change. Management is key in getting their groups on board with using it regularly. If it doesnt have management backing, your security teams have little to no influence in getting this process off the ground fully.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Rider is hands down smoother and way less glitchy than Visual Studio Enterprise. There are way more refactoring capabilities and spell check so that your code is readable, maintainable, and easy to follow. Since Rider is cross-platform, our developers are no longer constrained to only using Windows. We can now get a familiar development environment across Mac, Windows, or Linux!
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Veracode is slower with scan results however the flaws discovered and sites crawled are almost the same. Rapid7 InsightAppSec only does dynamic scans. Veracode did find more links on a site crawl. Rapid7 InsightAppSec has more out of the box reports than Veracode. Both integration to DevOps tools were striaghtforward.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)
Positive: Scanning all our applications on Veracode provides us an overview of our cyber security posture for the organization as a whole.
Positive: Performing the SAST, SCA and DAST scanning for all the applications at the early stages of the SDLC helps us identify and mitigate security vulnerabilities early, reducing the risk of data breaches and cyber-attacks.
Negative: Sometimes Veracode SAST scanner closed and reopens some findings, leading to reliability issues on the scanner itself.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info