TrustRadius: an HG Insights company

LevelBlue MailMarshal vs. Microsoft Defender for Endpoint

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    LevelBlue MailMarshal

    Score7 out of 10
    N/ATrustwave MailMarshal’s layered security helps to reduce false positives and protects against spam, gateway attacks, viruses, phishing attempts, and malicious URLs. It is available on-premise, delivered as a cloud-based service, or as a hybrid implementation.N/A

    Microsoft Defender for Endpoint

    Score8.8 out of 10
    N/AMicrosoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.

    $2.50

    per user/per month

    Pricing
    LevelBlue MailMarshalMicrosoft Defender for Endpoint
    Editions & Modules
    No answers on this topic
    Academic
    $2.50
    per user/per month
    Standalone
    $5.20
    per user/per month
    Offerings
    Pricing Offerings
    LevelBlue MailMarshalMicrosoft Defender for Endpoint
    Free Trial
    NoYes
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional Details——
    More Pricing Information
    Community Pulse
    LevelBlue MailMarshalMicrosoft Defender for Endpoint
    Considered Both Products
    LevelBlue
    No answer on this topic
    Microsoft
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    96%
    Would buy again
    157 Answers
    Delivers good value for the price
    No answers on this topic
    99%
    Delivers good value for the price
    146 Answers
    Happy with the feature set
    No answers on this topic
    95%
    Happy with the feature set
    155 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    97%
    Lived up to sales and marketing promises
    130 Answers
    Implementation went as expected
    No answers on this topic
    95%
    Implementation went as expected
    140 Answers
    Features
    LevelBlue MailMarshalMicrosoft Defender for Endpoint
    Endpoint Security
    Comparison of Endpoint Security features of LevelBlue MailMarshal and Microsoft Defender for Endpoint
    Feature
    LevelBlue MailMarshal
    -
    Ratings
    Microsoft Defender for Endpoint
    8.7
    79 Ratings
    2% above category average
    Anti-Exploit Technology00 Ratings9.075 Ratings
    Endpoint Detection and Response (EDR)00 Ratings9.179 Ratings
    Centralized Management00 Ratings8.679 Ratings
    Hybrid Deployment Support00 Ratings7.110 Ratings
    Infection Remediation00 Ratings9.077 Ratings
    Vulnerability Management00 Ratings8.774 Ratings
    Malware Detection00 Ratings9.278 Ratings
    Best Alternatives
    LevelBlue MailMarshalMicrosoft Defender for Endpoint
    Small Businesses
    Sophos Email
    Score9.1 out of 10
    SentinelOne Singularity
    Score9 out of 10
    Medium-sized Companies
    Sophos Email
    Score9.1 out of 10
    BlackBerry Protect (CylancePROTECT)
    Score9.1 out of 10
    Enterprises
    Microsoft Exchange
    Score8.6 out of 10
    ESET PROTECT
    Score8.8 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    LevelBlue MailMarshalMicrosoft Defender for Endpoint
    Likelihood to Recommend
    7.0
    (1 ratings)
    8.9
    (169 ratings)
    Likelihood to Renew
    -
    (0 ratings)
    8.4
    (10 ratings)
    Usability
    -
    (0 ratings)
    8.6
    (40 ratings)
    Availability
    -
    (0 ratings)
    9.1
    (1 ratings)
    Performance
    -
    (0 ratings)
    9.1
    (1 ratings)
    Support Rating
    -
    (0 ratings)
    9.0
    (7 ratings)
    Implementation Rating
    -
    (0 ratings)
    7.3
    (1 ratings)
    Configurability
    -
    (0 ratings)
    8.2
    (1 ratings)
    Product Scalability
    -
    (0 ratings)
    9.1
    (1 ratings)
    User Testimonials
    LevelBlue MailMarshalMicrosoft Defender for Endpoint
    Likelihood to Recommend
    LevelBlue
    In a medium company, it is suited since the cost can be high for a smaller one.
    I think there are better and more complete products for companies with higher volume or levels of confidentiality. While it is a good product, today there are several that exceed it in quality and functionality.
    Incentivized
    Read full review
    Microsoft
    If you have multiple endpoints in your environment, if you're looking to understand what your environment looks like, if you're trying to identify the health of your environment, or identify any risks or vulnerabilities in your environment pertaining to your endpoints and devices.
    Incentivized
    Read full review
    Pros
    LevelBlue
    • By having the physical appliance, it is more granular the control that is had of the users, which also accelerates the speed of detection of threats.
    • The few options of DLP that it has are very useful when filtering sensitive data, but I stress "few".
    • The interface is intuitive, but for more advanced options, it requires a higher than average knowledge of these systems.
    Incentivized
    Read full review
    Microsoft
    • The big thing for us is on endpoint, it kind of integrates with everything else that we already have because we use Microsoft completely. And so that helps us with being able to integrate, and send things over to Azure Sentinel as we need to as well.
    Incentivized
    Read full review
    Cons
    LevelBlue
    • I know it is not a DLP since there is another specific product for it, but they could do it just a little easier for the average user.
    • An intuitive interface in a broader aspect, not only in the basic functions.
    • The option only in the cloud is good, but only the appliance offers all the functionalities.
    Incentivized
    Read full review
    Microsoft
    • I'd say building out summaries and log reviews for analysts reviewing incidents. So, pivoting from the alerts themselves to actually getting the detail underneath. Trying to understand what caused an alert, where they went from there, et cetera, et cetera. And then trying to get into deeper log review to take that investigation further can be a pain point.
    Incentivized
    Read full review
    Likelihood to Renew
    LevelBlue
    No answers on this topic
    Microsoft
    Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
    Incentivized
    Read full review
    Usability
    LevelBlue
    No answers on this topic
    Microsoft
    Because it's hard to find things sometimes. I can find things now because I know where they are. But you have to work with it a little while to figure out how. I'd basically say it was a security tool designed by developers. So you have to get that mindset to find things. So a new hire, a new person in the SOC would have a difficult time. I know that's sitting in here, or that screen is in here somewhere. So it's gotten better.
    Incentivized
    Read full review
    Reliability and Availability
    LevelBlue
    No answers on this topic
    Microsoft
    Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
    Incentivized
    Read full review
    Performance
    LevelBlue
    No answers on this topic
    Microsoft
    Microsoft Defender for Endpoint is easy on memory and resources on clients.
    Incentivized
    Read full review
    Support Rating
    LevelBlue
    No answers on this topic
    Microsoft
    The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
    Incentivized
    Read full review
    Implementation Rating
    LevelBlue
    No answers on this topic
    Microsoft
    Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
    Incentivized
    Read full review
    Alternatives Considered
    LevelBlue
    Unfortunately all these products are better in almost all aspects. It is not to discredit the Trustwave, but they have much to improve in this area.
    Incentivized
    Read full review
    Microsoft
    Particularly, we're evaluating Symantec Endpoint Protection, the commercial version. We've looked at eSet, a couple of the others, and it's much too heavy or difficult to manage, things like that. Ease of use, ease of integration. It's already there. It's super easy to update it with the regular OS updates and everything. So we can manage it whether we're using SCCM or Intune or Dato, it's very easy to deploy updates and manage things.
    Incentivized
    Read full review
    Scalability
    LevelBlue
    No answers on this topic
    Microsoft
    Microsoft Defender for Endpoint is easily scaled from small orgs to giant enterprises.
    Incentivized
    Read full review
    Return on Investment
    LevelBlue
    • While it is a good product, today there are several that exceed it in quality and functionality.
    • In a medium company it is correct, since the cost can be high for a smaller one and it is not worth it.
    • It is a basic product, compared to others of the same type
    Incentivized
    Read full review
    Microsoft
    • I think the positive impact overall is that we do a lot of sitting in front of assessors- federal assessors, government assessors. And it really comes down to when the assessor has to think about another product that you're bringing in that's not Microsoft, it creates a lot of confusion, more paperwork, more explanation. But the positive impact is that they know it, everybody kind of knows Microsoft. And so when you tell them you have this endpoint for Microsoft Defender for Endpoint, they're like, okay. The questions go away, and it makes the overhead a lot less during an assessment.
    Incentivized
    Read full review
    ScreenShots

    Microsoft Defender for Endpoint Screenshots
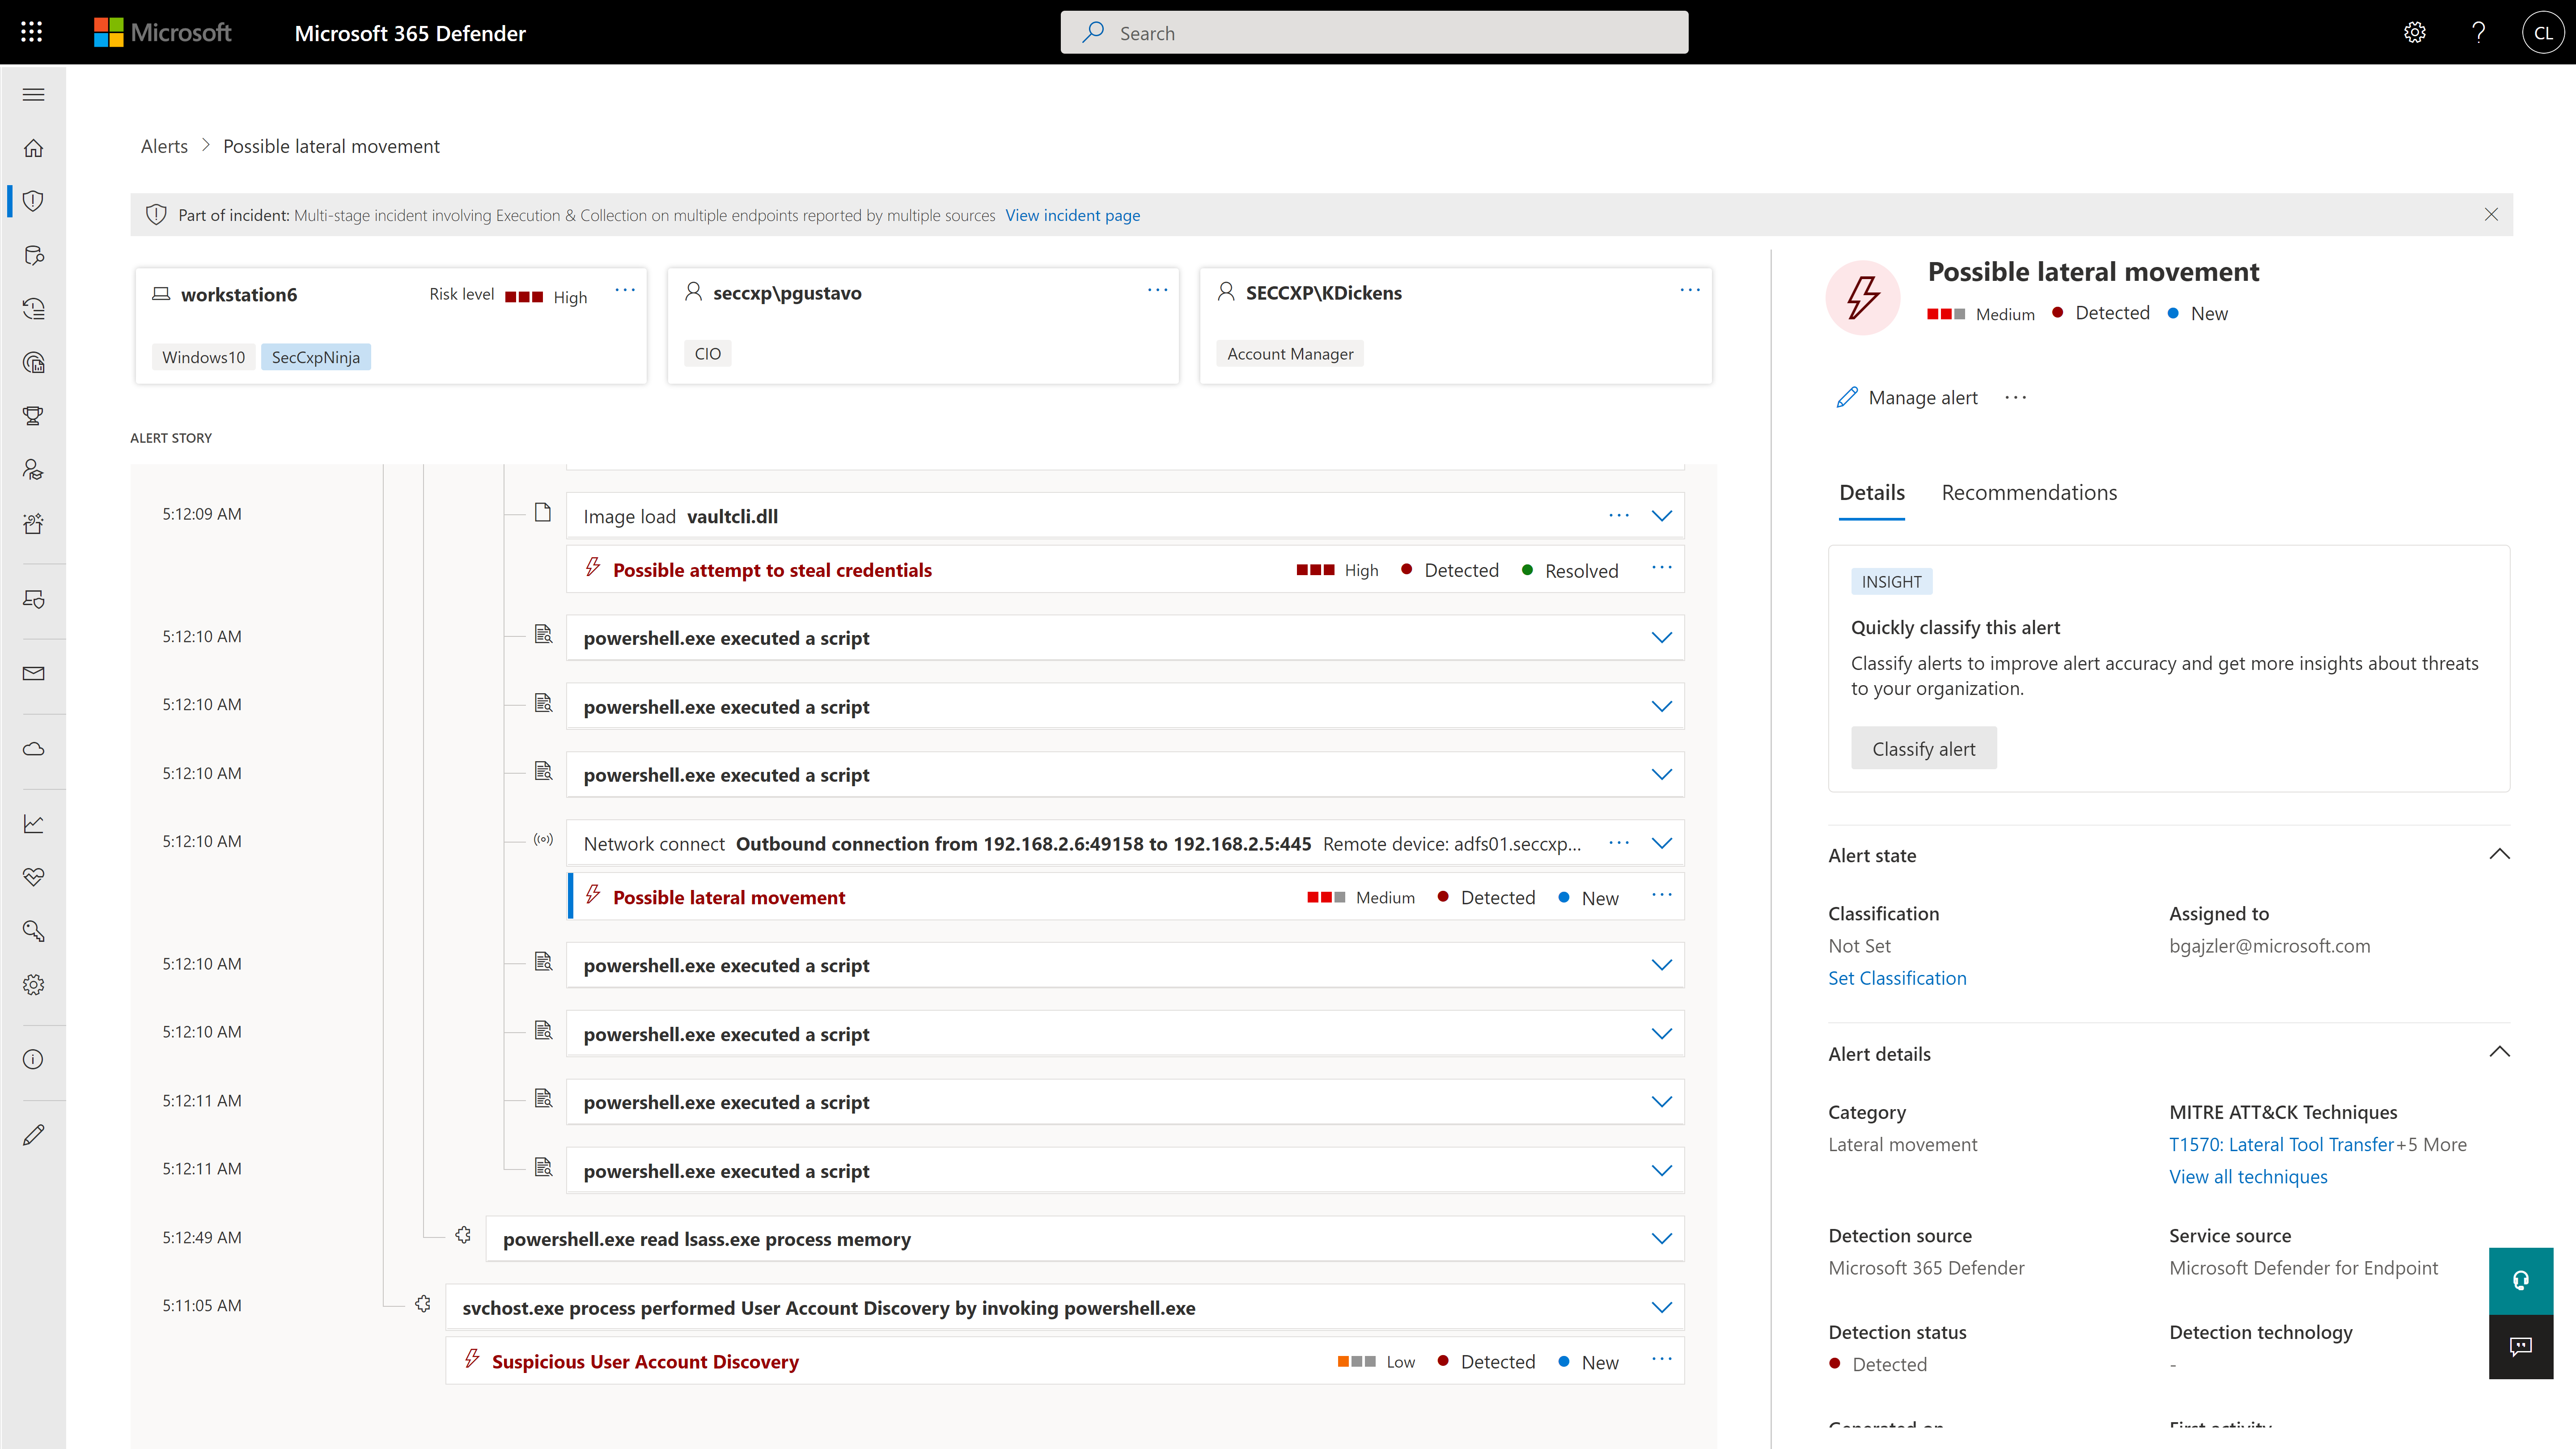
    Screenshot of blocked activitiesScreenshot of Detects & respondsScreenshot of discovers vulnerabilityScreenshot of Eliminates blind spotsScreenshot of Risk management