The LevelBlue USM Anywhere XDR platform (replacing the former AlienVault USM) delivers threat detection, incident response, and compliance management.
$1,075
per month
Microsoft Defender for Cloud
Score8.7 out of 10
N/A
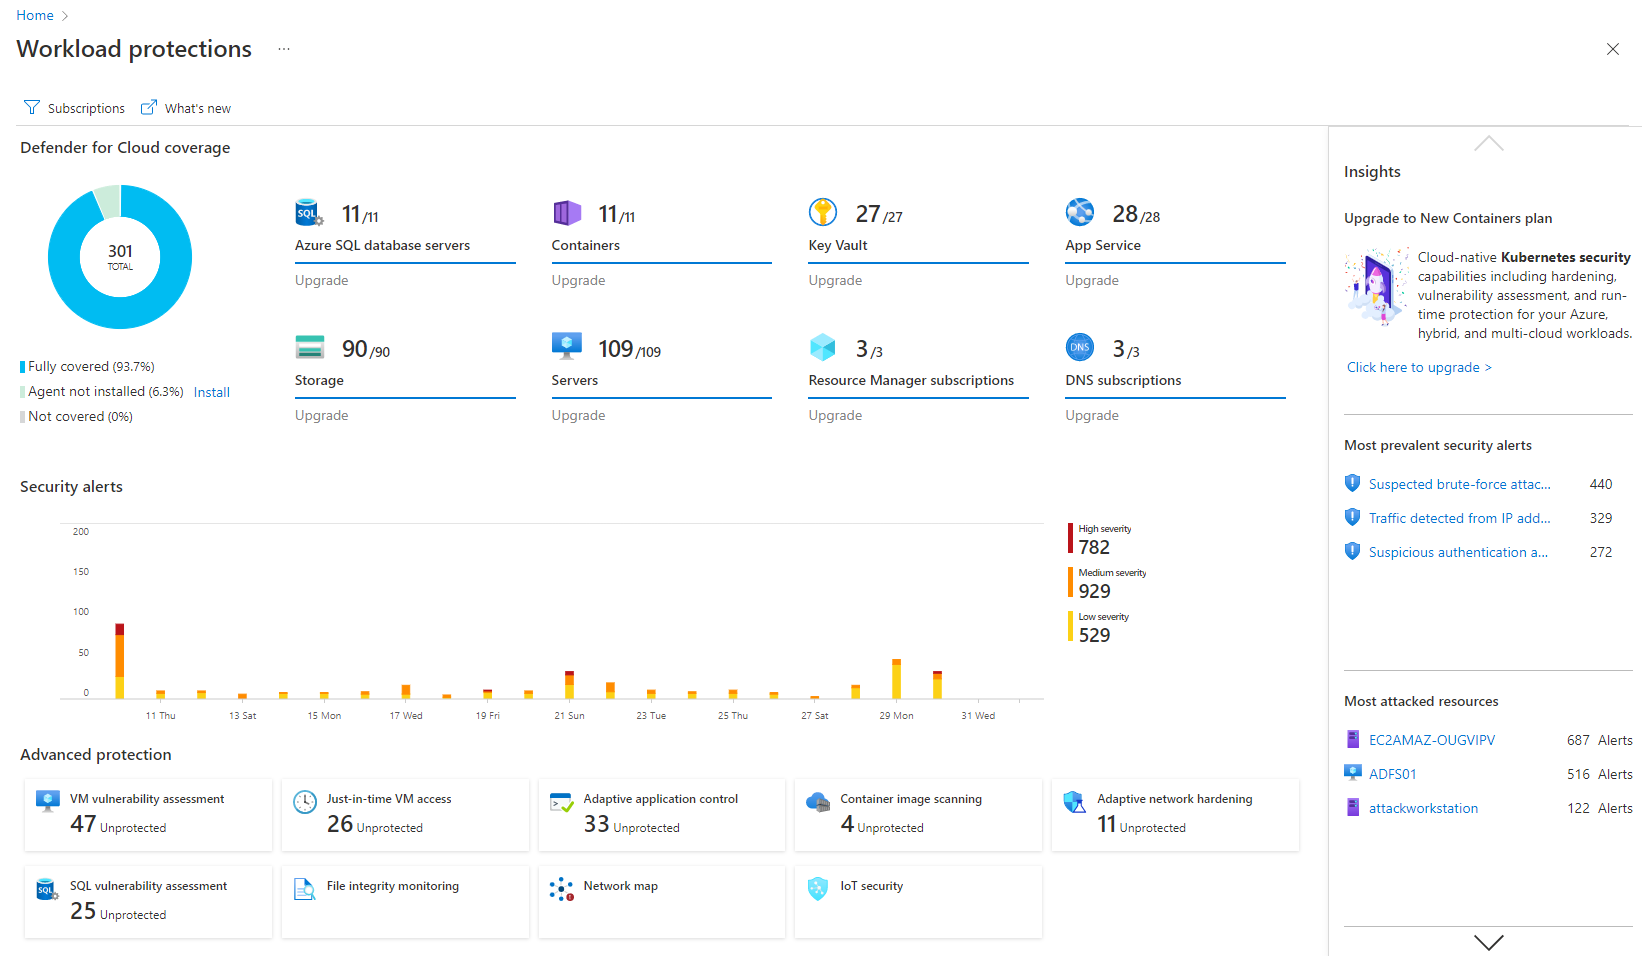
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
At this point I'm saying a 4. While the marketing material make it appear to be easy to use and it was relatively easy to set up, as previously mentioned, each event description is based upon the individual asset making it nearly impossible for the administrator to be a SME for each asset. For example, if one of the assets reporting is a router, the administrator monitoring alerts would need to know what the various events are that can be triggered as an event for the particular router; however, if the asset is a workstation, the administrator would need to know the various events that are triggered for workstations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AlienVault USM is simple and easy to deploy. Sensors can be deployed in as little as 15 minutes through the setup wizard.
The USM UI is easy to understand. I've trained multiple analysts who are able to perform their duties on their first day, in part because of USM Anywhere's ease of use.
Top-notch built-in compliance templates and reporting features.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Personally, I've wished I could purchase a service that would configure AV for my environment. I get a lot of traffic on a daily basis and I almost need to hire an analyst that just works on AV.
Some of the filters when looking for a specific alert aren't that easy to use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The centralized logging and retention for PCI compliance was our main driver, and it is meeting that need. Otherwise there has been enough frustration with the lack of documentation and the need to customize through the CLI that I would be open to alternatives.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
Once you are able to navigate the different panels, finding what you need is quite easily. Before getting used it it can be a bit of challenge . Each panel is quite well laid out and the filtering search capabilities are quite strong.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We do have issues with maintenance on the AlienVault USM as the disk fills up from time to time with other data sources. Sources for scanning logs and net flow data isn't calculated in regular disk maintenance and can easily fill up our disk if we do not keep an eye on it with some custom Nagios plugins. The system does properly trim logging data from logging sources properly.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
With the latest release of AlienVault USM overall performance has not been an issue. We have noticed single source events per second does not scale well with the overall system. 2,000eps on a vmware system with a single source produces delays of up to an hour for us. Pages, reporting and even raw log searches are rather quick though.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The support we received from alienvault was excellent. They went above and beyond in making sure everything was working as it needed to be. They REALLY want their product implementation to be a success and our security goals be achieved. They are like a member of our security team.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I did not have any experience with "in person" training directly. The free online classes offered for a half a day are based on the actual training offered. These little teasers are very good and well worth your time to learn a few quick and dirty ways of getting more information from your SIEM
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It was very well organized and helpful in using the product to the fullest extent. The instructor allowed time for folks who were involved with managed services to receive tuning tips in order to better support their customers. In addition, the course materials were automatically updated when the new version came out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AlienVault USM was a very simple to implement and get up and running. We started with a trial version and had that up and going within an hour of receiving email instructions from the sales engineer. We never had to contact support to get the system up and going. It was extremely easy to convert over to a full license once we started with a paid version.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk's ES is a paid add-on on top of an already pricey product. Finding a MSSP that supports Splunk and isn't a 6 figure annual commitment seems unlikely. LogRhythm did not have a cloud-based solution when we were considering SIEMs. Fantastic product though and have a good MSSP base. Devo did not have a MSSP partner base when we looked. Their product is fantastic too. AlienVault USM has good partners to choose from as well as an affordable cloud model, that's why we chose it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The AlienVault USM is not very scalable. Some scalability can be achieved by installing additional sensors, but this only offers 500eps per sensor and is still overall limited by the installation type of VM or physical. We have also noticed the EPS (events per second) is rated overall and not towards a single source. A single source on a very healthy VMware partition tops out at 2,000eps for us, no matter how we configure it. Maybe this is a problem of the 5.2 release?
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Once you hit the 150 asset mark, you have to jump to their unlimited license. There is no middle ground. We were only 10 or so assets above the 150 so we had to chose to either not monitor those assets or pay the price of the upgrade.
AlienVault brings all the information to one place which makes it much quicker to track down problems.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info