Microsoft Defender External Attack Surface Management
Score9.7 out of 10
N/A
Microsoft Defender External Attack Surface Management is a service available on Microsoft's Azure, that provides insights into vulnerabilities, risks, and exposures for web-based resources. It defines an organization’s unique internet-exposed attack surface and discovers unknown resources to help users proactively manage security posture.
$0.01
per day per asset
Microsoft Defender for Cloud
Score8.7 out of 10
N/A
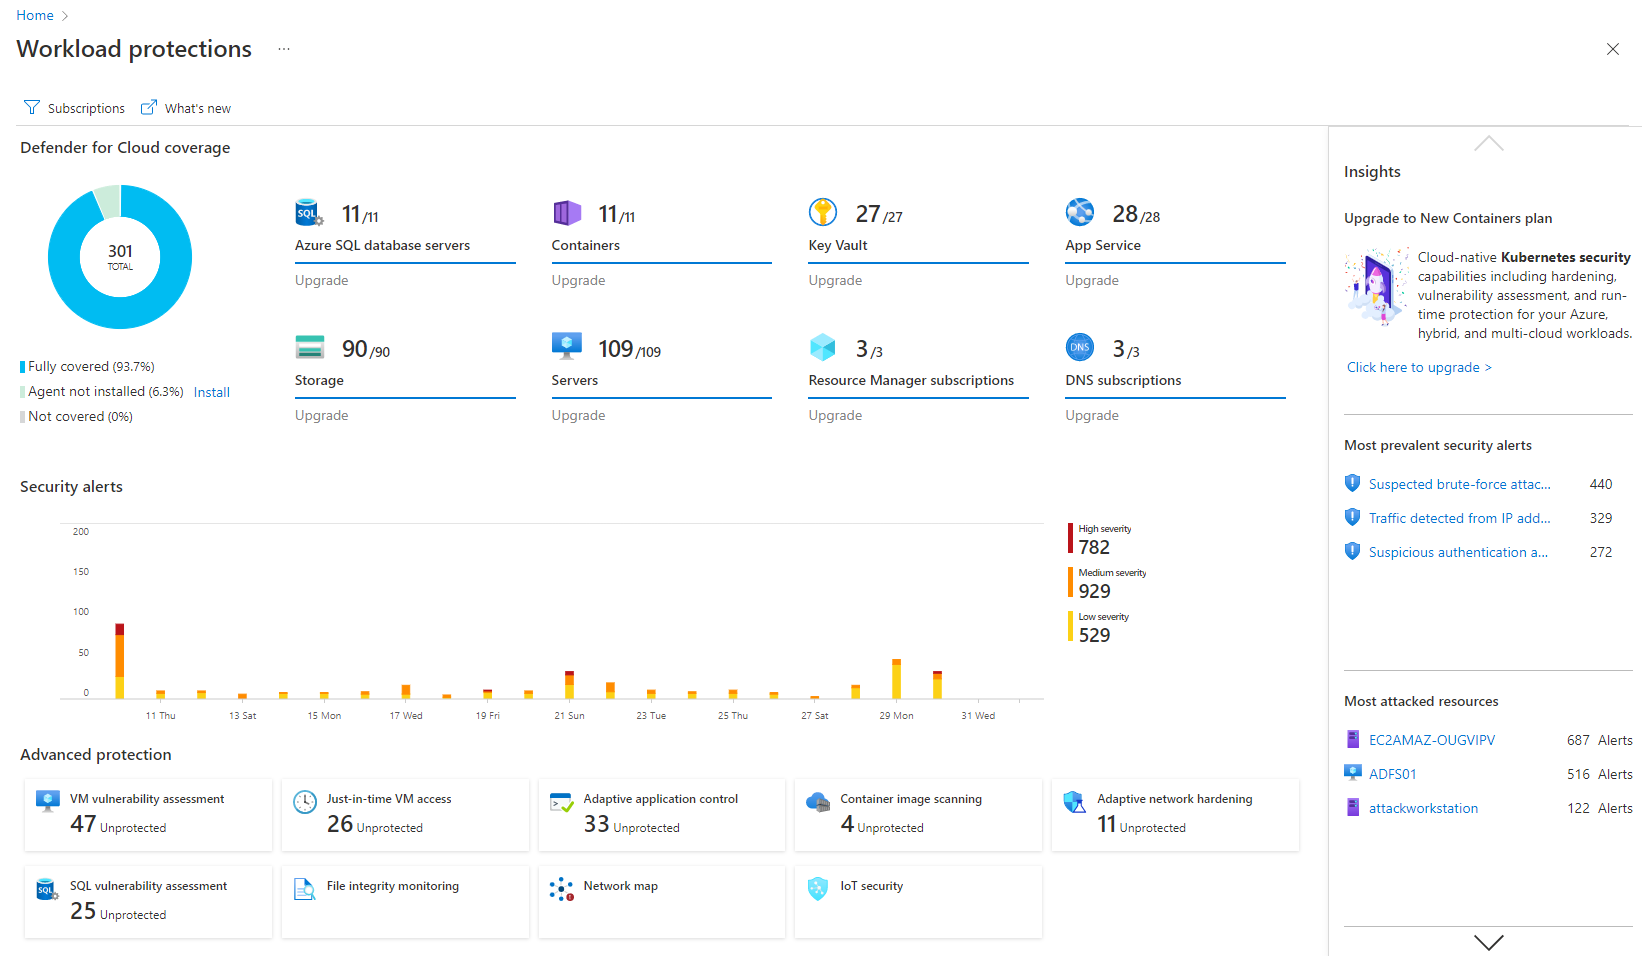
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
N/A
Pricing
Microsoft Defender External Attack Surface Management
Microsoft Defender for Cloud
Editions & Modules
No answers on this topic
No answers on this topic
Offerings
Pricing Offerings
Microsoft Defender External Attack Surface Management
Microsoft Defender External Attack Surface Management
Microsoft Defender for Cloud
Likelihood to Recommend
Microsoft
Microsoft Defender External Attack Surface Management is particularly well-suited for discovering, inventorying, and continuously monitoring the external attack surface, especially in environments with heavy Microsoft adoption. It is less suitable as a standalone solution for internal scanning, real-time attack detection, automated remediation, or advanced application testing. Microsoft Defender External Attack Surface Management es especialmente adecuado para descubrir, inventariar y monitorear continuamente la superficie de ataque externa, sobre todo en entornos con fuerte adopción de Microsoft. Es menos adecuado como solución única para escaneo interno, detección de ataques en tiempo real, remediación automática o pruebas avanzadas de aplicaciones. Parts of this review were originally written in Spanish and have been translated into English using a third-party translation tool. While we strive for accuracy, some nuances or meanings may not be perfectly captured.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
We rate Microsoft Defender External Attack Surface Management’s overall usability as 10 out of 10 because it delivers a strong balance between depth of capability and ease of use, particularly within organizations already operating in the Microsoft security ecosystem.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because Microsoft Defender External Attack Surface Management is part of the broader Microsoft Defender family (including Defender XDR, Entra ID, Azure Security, Sentinel, etc.), it: Shares identity, endpoint, and threat context across tools Reduces the need for custom integrations or connectors Works in a “single pane of glass” experience for SOC analysts Why it matters: Organizations already invested in Microsoft security tools gain greater contextual insight and lower operational overhead.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info