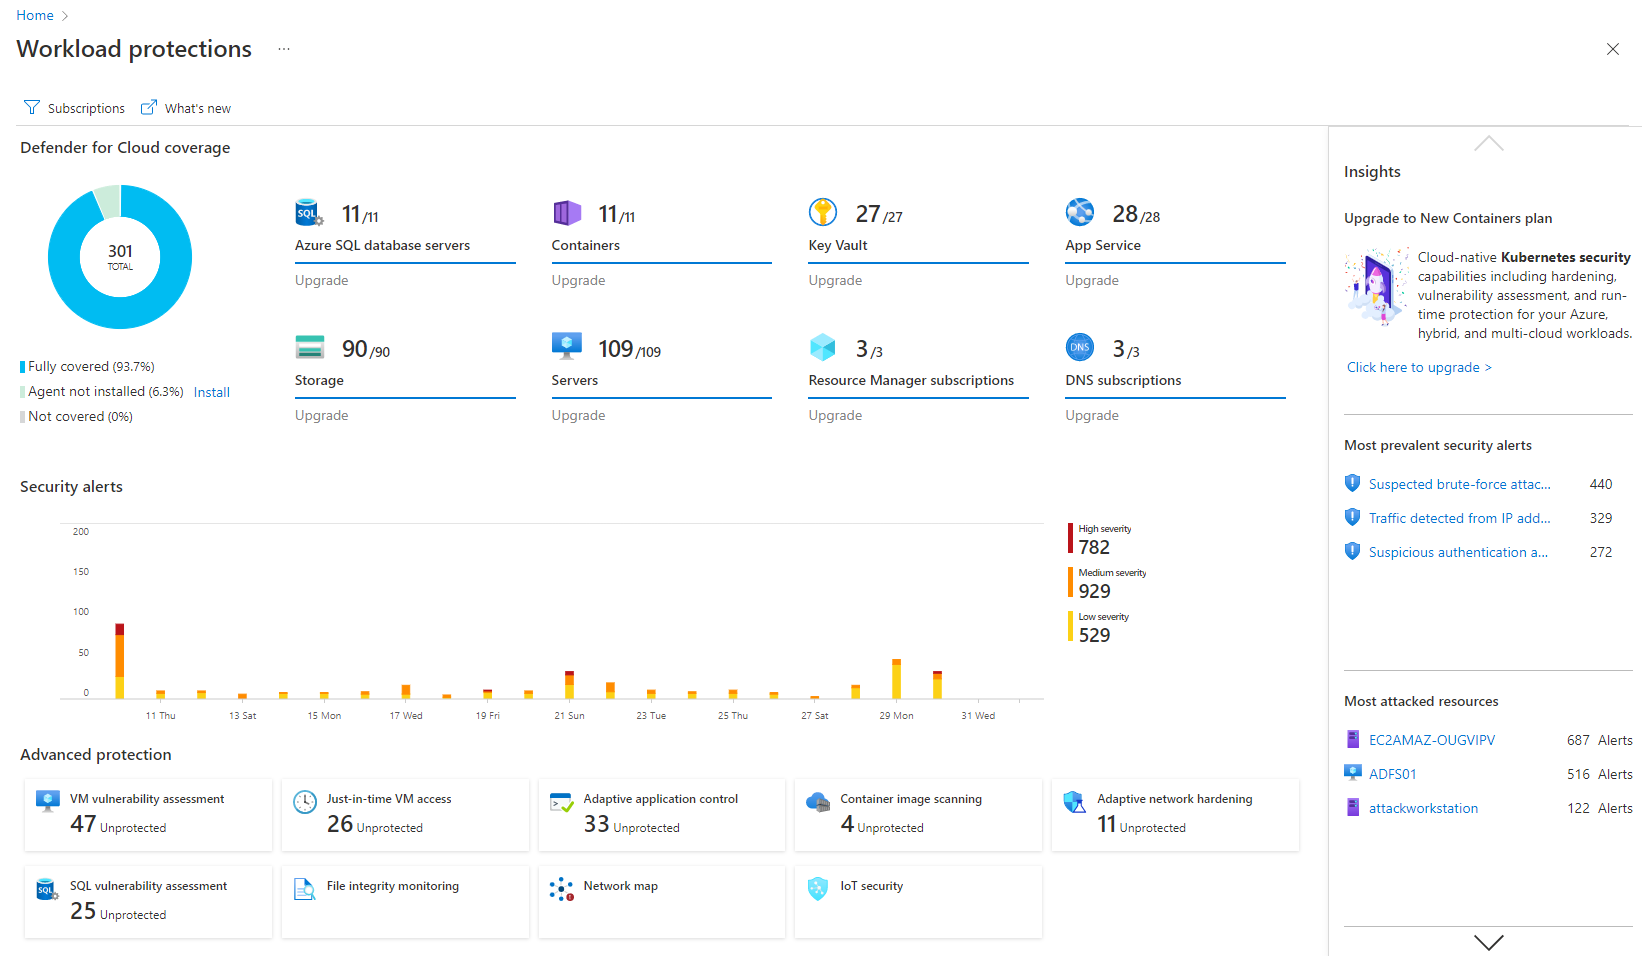
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
N/A
Salt
Score6.2 out of 10
N/A
VMware Salt is an Infrastructure Automation & Configuration Management platform that provisions, configures, deploys, and manages infrastructure components at scale. The solution utilizes an event-driven automation engine to enforce compliant software states across virtual machines, servers, containers, and network devices.
The VMware Salt solution is comprised of software components from both VMware and the open-source Salt Project While the Salt Masters and Salt Minions are a part of the open…
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SaltStack is a very well architected toolset and framework for reliably managing distributed systems' complexity at varied scale. If the diversity of kind or number of assets is low, or the dependencies are bounded and simple, it might be overkill. Realization that you need SaltStack might come in the form of other tools, scripts, or jobs whose code has become difficult, unreliable, or unmaintainable. Rather than a native from-scratch SaltStack design, be aware that SaltStack can be added on to tools like Docker or Chef and optionally factor those tools out or other tools into the mix.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Targeting is easy and yet extremely granular - I can target machines by name, role, operating system, init system, distro, regex, or any combination of the above.
Abstraction of OS, package manager and package details is far advanced beyond any other CRM I have seen. The ability to set one configuration for a package across multiple distros, and have it apply correctly no matter the distrospecific naming convention or package installation procedure, is amazing.
Abstraction of environments is similarly valuable - I can set a firewall rule to allow ssh from "management", and have that be defined as a specific IP range per dev, test, and prod.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We haven't had to spend a lot of time talking to support, and we've only had one issue, which, when dealing with other vendors is actually not that bad of an experience.
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We moved to SaltStack from Puppet about 3 years ago. Puppet just has too much of a learning curve and we inherited it from an old IT regime. We wanted something we could start fresh with. Our team has never looked back. SaltStack is so much easier for us to use and maintain.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We manage two complex highly available self-healing (all infrastructure and systems) environments using SaltStack. Only one person is needed to run SaltStack. That is a HUGE return on investment.
Building tooling on top of SaltStack has allowed us to share administrative abilities by role - e.g. employee X can deploy software Y. No need to call a sysadmin and etc.
Recovery from problems, or time to stand-up new systems is now counted in minutes (usually under eight) rather than hours. This is a strategic advantage for rolling out new services.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info