TrustRadius: an HG Insights company

SolarWinds Engineer's Toolset vs. Symantec Content & Malware Analysis

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    SolarWinds Engineer's Toolset

    Score7.6 out of 10
    N/ASolarWinds® Engineer’s Toolset (ETS) helps users monitor and troubleshoot a network with over 60 tools for network management. ETS allows users to monitor and receive alerts in real time on network availability and health, and perform network diagnostics for faster troubleshooting and resolution of complex network issues. With ETS users can deploy an array of network discovery tools including Port Scanner, Switch Port Mapper or advanced Subnet Calculator, manage Cisco® devices with specialized…

    $1,585

    Per Instance

    Symantec Content & Malware Analysis

    Score8.3 out of 10
    N/ASymantec Content & Malware Analysis is an application which provides advanced threat detection and threat hunting through advanced machine learning, based on intelligence gathered from ProxySG, threat intelligence services, and other sources.N/A
    Pricing
    SolarWinds Engineer's ToolsetSymantec Content & Malware Analysis
    Editions & Modules
    One Time Price
    $1,585
    Per Instance
    No answers on this topic
    Offerings
    Pricing Offerings
    SolarWinds Engineer's ToolsetSymantec Content & Malware Analysis
    Free Trial
    YesNo
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional Details——
    More Pricing Information
    Community Pulse
    SolarWinds Engineer's ToolsetSymantec Content & Malware Analysis
    Considered Both Products
    SolarWinds
    No answer on this topic
    Broadcom
    No answer on this topic
    Key User Insights
    Would buy again
    100%
    Would buy again
    11 Answers
    No answers on this topic
    Delivers good value for the price
    90%
    Delivers good value for the price
    9 Answers
    No answers on this topic
    Happy with the feature set
    100%
    Happy with the feature set
    11 Answers
    No answers on this topic
    Lived up to sales and marketing promises
    100%
    Lived up to sales and marketing promises
    10 Answers
    No answers on this topic
    Implementation went as expected
    100%
    Implementation went as expected
    10 Answers
    No answers on this topic
    Best Alternatives
    SolarWinds Engineer's ToolsetSymantec Content & Malware Analysis
    Small Businesses
    No answers on this topic
    No answers on this topic
    Medium-sized Companies
    No answers on this topic
    Palo Alto Networks WildFire
    Score9 out of 10
    Enterprises
    No answers on this topic
    Trellix Intelligent Sandbox
    Score7.1 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    SolarWinds Engineer's ToolsetSymantec Content & Malware Analysis
    Likelihood to Recommend
    8.6
    (11 ratings)
    8.0
    (1 ratings)
    Usability
    8.2
    (1 ratings)
    -
    (0 ratings)
    Support Rating
    8.2
    (1 ratings)
    -
    (0 ratings)
    User Testimonials
    SolarWinds Engineer's ToolsetSymantec Content & Malware Analysis
    Likelihood to Recommend
    SolarWinds
    I have found the toolset especially useful for scanning subnets to discover devices, and for setting up temporary real-time monitors when we are troubleshooting or setting up new connections. The most useful aspect has been the ability to apply the tools to help troubleshoot and pinpoint intermittent issues. More general tools like Orion often do not have the granularity to detect issues like intermittent packet loss which are especially impactful to applications like Voice. The toolset gives us another level of capability to dig into issues.
    Incentivized
    Read full review
    Broadcom
    If you have Symantec based environment including Symantec proxy and endpoints, Content and Malware Analysis is the obvious choice. You can't run the CAS-MAS as a standalone deployment, you need proxies or ICAP supported devices capable to send the files/URLS. It's not a network security device where you can flow/direct the traffic to C/MAS. It does not have UBA, NBA or NTR features, it is just working for analyzing files as expected.
    Read full review
    Pros
    SolarWinds
    • Various monitoring
    • Stores history
    • Suggests indices
    • Helps to find the SQL query text
    • Helps to see what machines/users the bad queries are coming from
    • Shows current blocking session
    Incentivized
    Read full review
    Broadcom
    • 0 day detection and prevenion
    • Flawless integration with Symantec Ecosystem
    • Integration with other vendors supporting ICAP is also working
    • Custom and golden image support
    • High performance on busy environments
    • Many threats are already detected and prevented through the CAS, it improves the performance drastically.
    • Already builtin virustotal integration
    • Reference to updates and updates information where I can see the product/service detecting which APTs
    • Multiple Antivirus engines which you can select/subscribe
    • Manual submission of file is supported through the gui
    • URL manual submission is also supported
    Read full review
    Cons
    SolarWinds
    • The unifying component that is intended to be the initial interface to the tools seems clunky. I prefer to start the tools individually rather than using it.
    • The port scanner could use some improvements to make it easier to use.
    Incentivized
    Read full review
    Broadcom
    • API support is lacking
    • Symantec/Broadcom security vision in general
    • Symantec support is not perfect
    • You can't run the product as a standalone network device
    • No packet capture capabiliy or work in span mode
    • You need a dedicated hardware to make it run
    • You need to buy
    Read full review
    Usability
    SolarWinds
    Very easy to use and intuitive. Just be careful with the WAN Killer...it does what it says.
    Incentivized
    Read full review
    Broadcom
    No answers on this topic
    Support Rating
    SolarWinds
    Our organization uses it regularly. It is reliable, and we keep finding new uses for it
    Incentivized
    Read full review
    Broadcom
    No answers on this topic
    Alternatives Considered
    SolarWinds
    I haven't compared any tools similar to SolarWinds Engineer's Toolset. This might be because I'm pretty biased when it comes to monitoring, and reporting solutions. I've found that SolarWinds provides the biggest bang for the buck in my opinion. I'm sure there are other solutions on the market that compete, but I haven't tried any of them because I've been very satisfied with SolarWinds.
    Incentivized
    Read full review
    Broadcom
    We have been using many solutions even tested nearly all available 0day sandbox solutions in the market. We choose Symantec CMA as we have already Symantec endpoint protection/EDR on the client, Symantec proxy for the web access, SCMA fits our environment. We have a big bargain when we puchase lots of equipment from the Symantec. Detection and prevention is very good at SCMA but some constant issues; like the product is not designed for heterogeneous environments, we can not integrate the SCMA with WAFs, it's lacking in api and request/reply calls. There's no file scanning, discover the option. SIEM integration is not smooth. I can not run some of the SOAR playbooks through the SCMA.
    Read full review
    Return on Investment
    SolarWinds
    • Spend less time downloading free buggy tools
    • All the tools in one spot, so you don't have to look around for tools
    • Get to the solution sooner
    Incentivized
    Read full review
    Broadcom
    • 0-day and APT risk is covered by the SCMA
    • As the SSL is inspected and analyzed at Bluecoat proxy servers, hidden threats, malicous files are passed to SCMA to be analyzed.
    • Getting full visibility at file trajectory level
    • As it's a full proxy and ICAP integration, we are sure that the files are to analyzed and scanned for malicious activity. This is a big plus compared to NGFW analyze concept, as the NGFWs have special failsafe mechanisms allowing bypass of file analysis. SCMA fully catches the hidden threats.
    • Flawless integration with Bluecoat systems is a big plus, customers are getting the same type of messages within their browsers.
    • A negative impact is the standardization when I deploy SCAM to one of our locations. Then the auditors demand the same coverage within other areas and it comes with the cost. Especially maintaining these devices on premise environment has a significant cost.
    Read full review
    ScreenShots

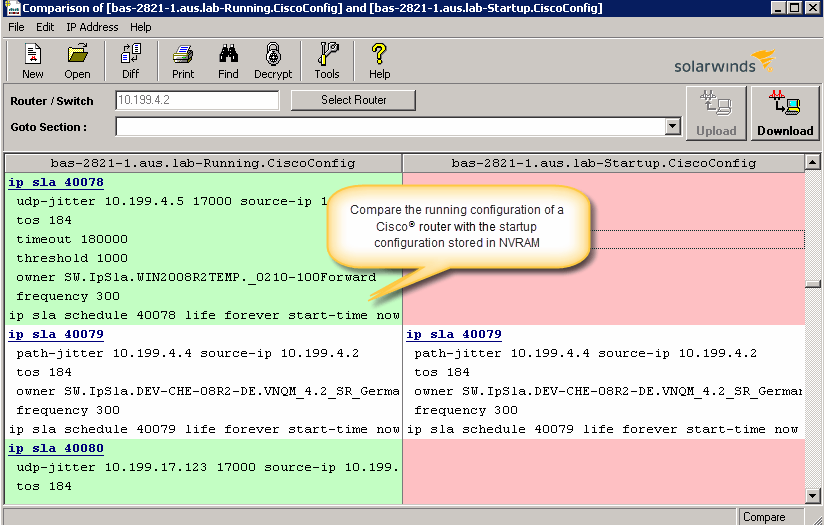
    SolarWinds Engineer's Toolset Screenshots

    Screenshot of Perform network stress tests with Engineer's Toolset WAN Killer. You don’t need to use real traffic for studying network activities, like testing traffic and load balancing. Instead, deploy Engineer's Toolset WAN Killer to help interactively test connections and adjust the IP traffic generated to achieve the desired network load based on your requirements.Screenshot of Quickly troubleshoot your network with enhanced ping capabilities and packet route tracing, among other network bandwidth usage and monitoring tools included in ETS.Screenshot of Using ETS, you can run scans to gain insight into how routers, hubs switches, and other devices are configured by analyzing SNMP queries and viewing MIB attributes. ETS is designed to help you more easily understand whether your network and ports are using appropriate settings.Screenshot of Config Compare, a part of ETS, is built to compare the running configuration of a Cisco router with the startup configuration. With the Cisco configuration compare tool, you can easily detect the changes made to the network, switch, and router configurations that are not committed to non-volatile memory (NVRAM).Screenshot of Manage your IP network from discovery to address tracking. Discover subnets on a seed router and scan the subnet or a range of IP addresses, generate a list of subnets along with their mask, size, range, and broadcast address and actively monitor subnets to identify and track which IP addresses are in use on your network.