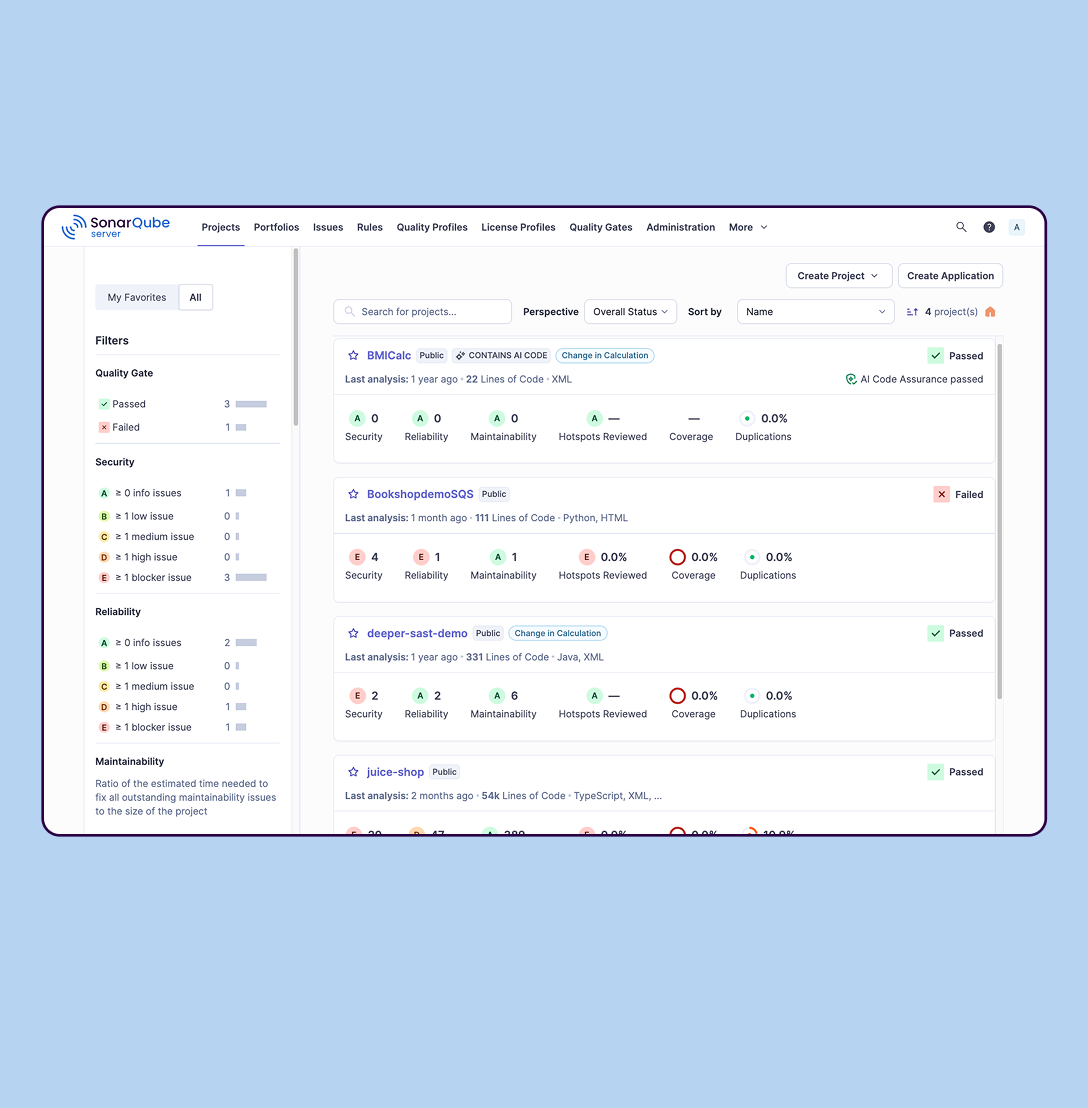
SonarQube is an automated code review solution, serving as the verification layer for code quality and SDLC security. SonarQube is used to ensure that code is secure, reliable, and maintainable. It is available through SaaS or self-managed deployment.
$34
per month Recommended for teams <50 developers
Splunk Enterprise Security
Score8.3 out of 10
N/A
Splunk Enterprise Security is an analytics-driven SIEM that helps to combat threats with actionable intelligence and advanced analytics at scale.
SonarQube is excellent if you start using it at the beginning when developing a new system, in this situation you will be able to fix things before they become spread and expensive to correct. It’s a bit less suitable to use on existing code with bad design as it’s usually too expensive to fix everything and only allows you to ensure the situation doesn’t get worse.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Based on my experience, Splunk is a strong git for some environments and a poor match for others. The distinction is primarily based on infrastructure complexity and budget. It's perfect for large enterprises with a mix of on-prem/cloud infrastructure. It's not a perfect match for small teams with restricted resources.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
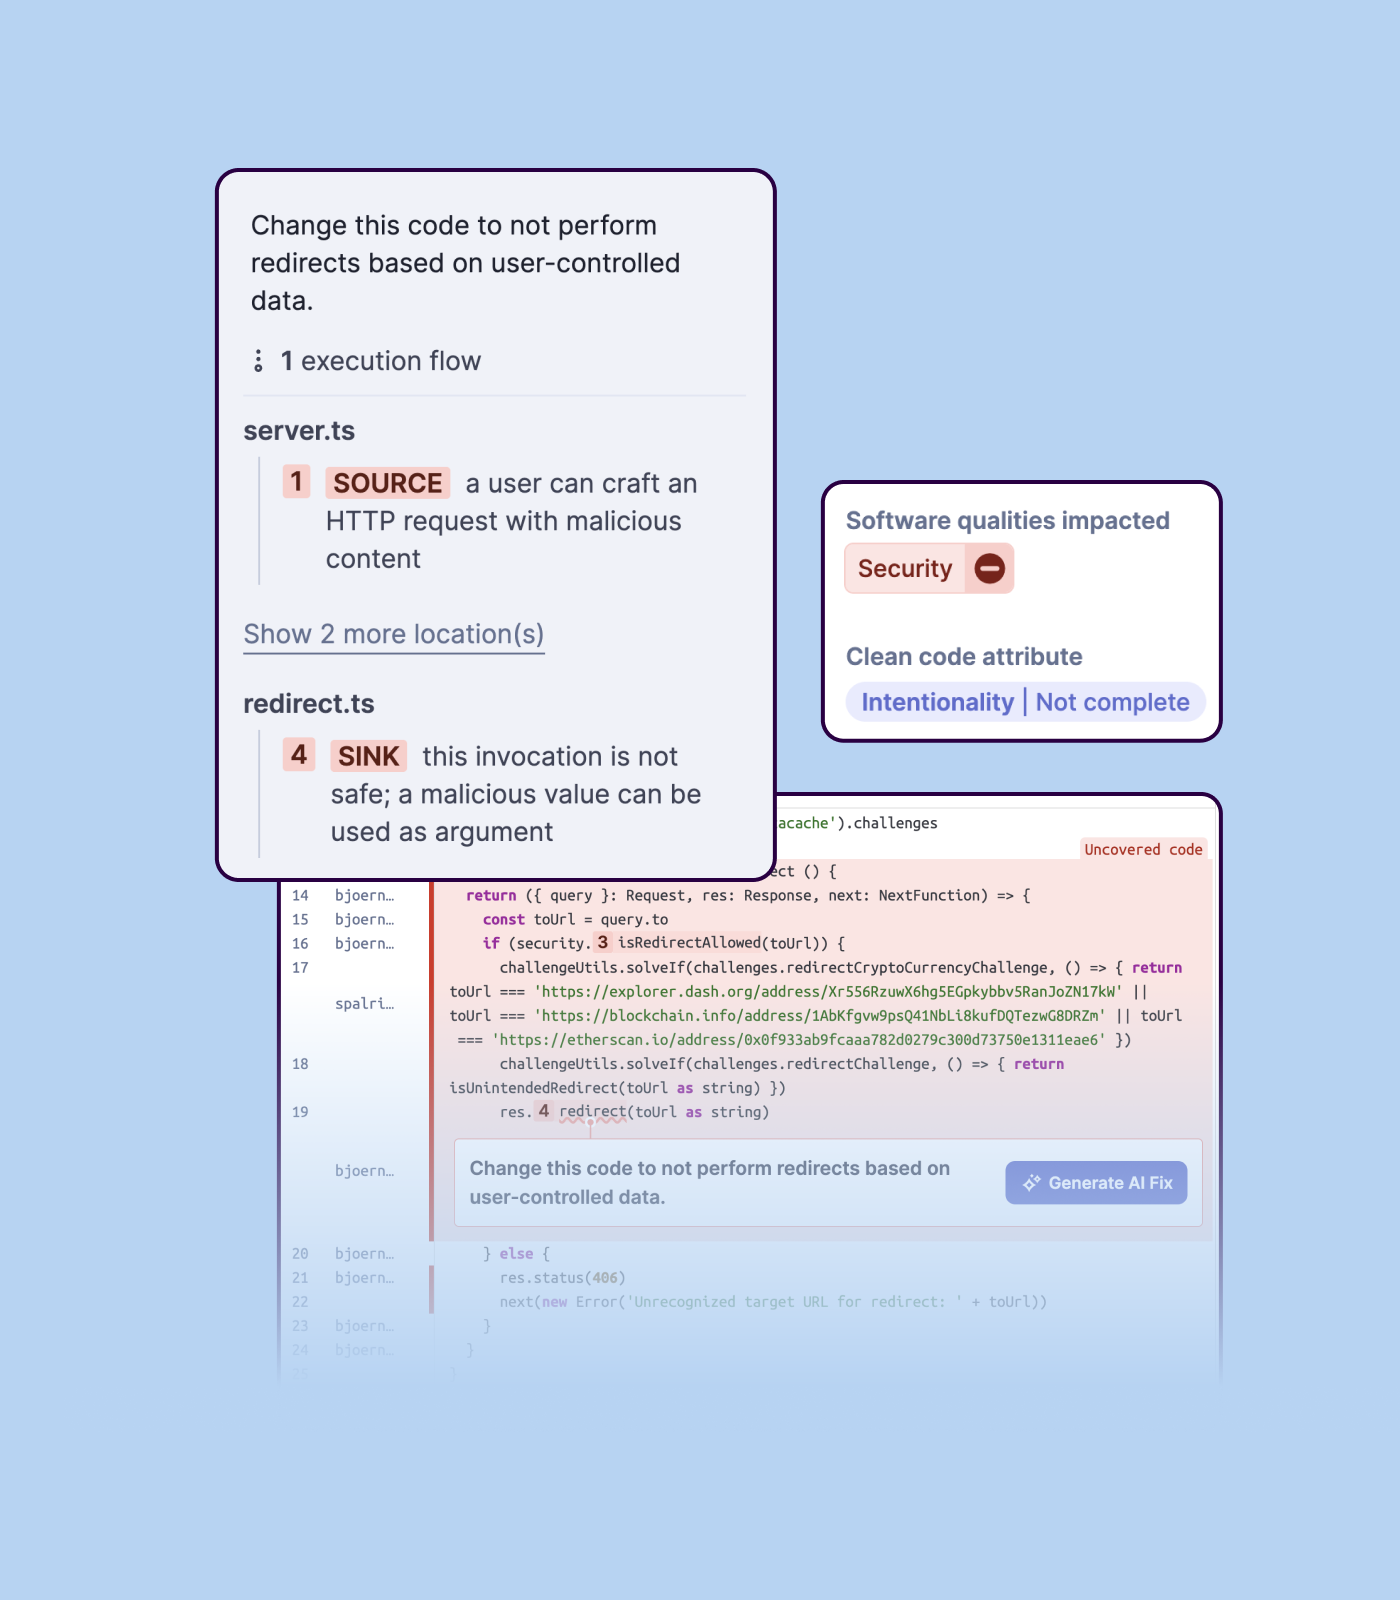
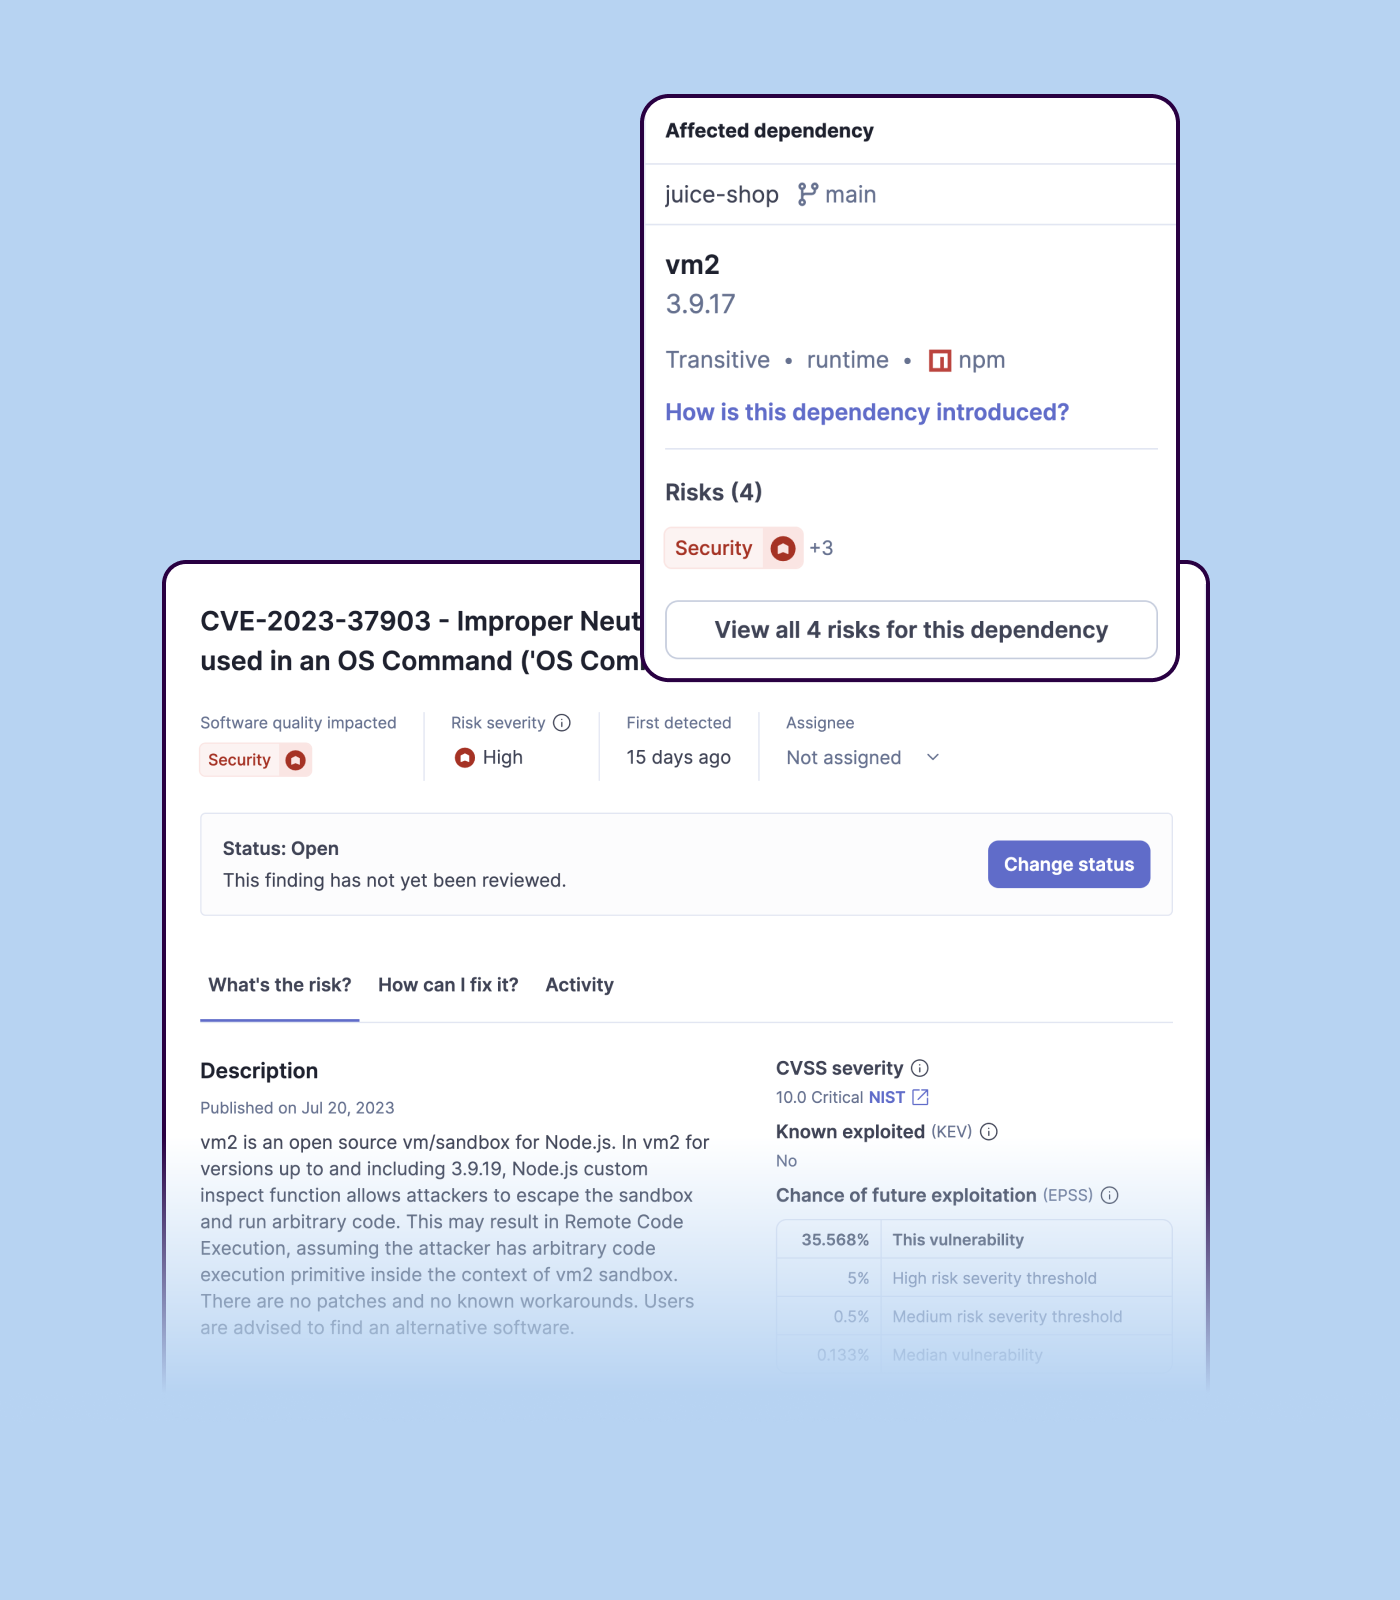
Detecting bugs and vulnerabilities: SonarQube can identify a wide range of bugs and vulnerabilities in code, such as null pointer exceptions, SQL injection, and cross-site scripting (XSS) attacks. It uses static analysis to analyze the code and identify potential issues, and it can also integrate with dynamic analysis tools to provide even more detailed analysis.
Measuring code quality: SonarQube can measure a wide range of code quality metrics, such as cyclomatic complexity, duplicated code, and code coverage. This can help teams understand the quality of their code and identify areas that need improvement.
Providing actionable insights: SonarQube provides detailed information about issues in the code, including the file and line number where the issue occurs and the severity of the issue. This makes it easy for developers to understand and address issues in the code.
Integrating with other tools: SonarQube can be integrated with a wide range of development tools and programming languages, such as Git, Maven, and Java. This allows teams to use SonarQube in their existing development workflow and take advantage of its powerful code analysis capabilities.
Managing technical debt: SonarQube provides metrics and insights on the technical debt on the codebase, enabling teams to better prioritize issues to improve the quality of the code.
Compliance with coding standards: SonarQube can check the code against industry standards like OWASP, CWE and more, making sure the code is compliant with security and coding standards.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Writes Powerful Queries: The queries that can be written using the Splunk Query Language are very powerful and highly customizable to meet every need. Ex: Writing queries to search the intersection of two different sources like Network and Endpoint Logs.
Offers Dashboard Abilities: Helps build complex panels for Dashboards in addition to providing several out-of-the-box panels. Ex: creating panels to calculate the performance of analysts in a given timezone.
Helpful Search Aids: It helps to set up complex custom alerts very easily. The interesting fields section is very helpful while threat hunting. Ex: It shows all the users and the frequency of each in a failed login event. The user list on the interesting fields is useful to look for suspicious logins.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Importing a new custom quality profile on SonarQube is a bit tricky, it can be made easier
Every second time when we want to rerun the server, we have to restart the whole system, otherwise, the server stops and closes automatically
When we generate a new report a second time and try to access the report, it shows details of the old report only and takes a lot of time to get updated with the details of the new and fresh report generated
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Improved User Interface Customization: While the interface is generally intuitive, providing more options for users to customize their dashboards and views would enhance the overall user experience. Tailoring the interface to specific roles or use cases could be a valuable addition.
Simplified Alert Management: Streamlining the process of managing alerts, such as grouping or categorizing them based on severity or type, would make it easier for security teams to prioritize and respond to incidents effectively.
Expanded Threat Intelligence Feeds: Increasing the variety and sources of threat intelligence feeds available within ES would provide a broader context for identifying and mitigating emerging threats, ensuring a more comprehensive defense against evolving attack vectors.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Maintaining hundreds or even 1000+ SOC use cases is really difficult, considering that the Data sources may not always send the data. A module that detects data freshness issues and detect data format changes would be a great help. the main challenge today using Splunk Enterprise Security is making sure that the detection rules are still working properly given all the changes that occur in data source applications. Also, maintaining the data collects on tens of thousands of servers and more than 100k workstations is a real company IT challenge: the splunkbase forwarder may not support old OS anymore, while these are the most important to monitor. Moving to the Open Telemetry collector has become essential so that only 1 agent is required for both SIEM and application observability.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It takes a long time for items to load if you are just generally searching through logs. It is best to use the data models which load faster but can be strange in terms of what is coming from which logs where. Yes, you can look it up, but this also requires familiarity with where things are and how to look them up.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We we easily able to integrate the SonarQube steps into our TFS process via the Microsoft Marektplace, we didn't have the need to call SonarQube support. We've used their online documentation and community forum if we ran into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's good when it's responsive, but I've had times where I had to wait quite a while for a response. But these are typically the exceptions rather than the rule. When you do get a response it is always well-informed and appropriate. I would say they've been trending better over time with this.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I experienced only on-line training, but the trainers were very professional and competent. Maybe it could be more useful if they also have an experience in projects because sometimes they didn't have a real project experience to communicate to the students. Anyway, it was very interesting and I learned many thing that's very difficoult (or maybe impossible!) to have by myself, aven if I have more than 10 years of Splunk activity experience.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It was very interesting and I learned many thing that's very difficoult (or maybe impossible!) to have by myself. The only problem was that, when I worked with the Splunk Professional Services, I found some difference between the training contents and the information from PS. In addition is required a long experience on Splunk Enterprise for the data ingestion part, in other words I'm able to work with ES because I'm worling on Splunk since 11 years, otherwise I'd some problem.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
SonarQube is an open-source. It's a scalable product. The costs for this application, for the kind of job it does, are pretty descent. Pipeline scan is more secured in SonarQube. Its a very good tool and its support multiple languages. Its main core competency is of static code analysis and that is why SonarQube exists and it does it exceedingly well. The quality of scan on code convention, best practices, coding standards, unit test coverage etc makes them one of the best competent tool in the market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Splunk enterprise is the only solution that we’ve been able to identify that provides risk based alerting, which allows our SOC to reduce analyst fatigue which would be a huge problem without it. Before RBA, there were thousands of alerts a day and it was impossible to review all of them
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
for my exterience, unit pricing and billing frequency are correct. As I already said, I hint to have more discount flexibility, expecially with new customers, because there are competitors less expensive and very aggressive that are dangerous. In addition the possibility to don't pay the license for the development period could be a very interesting feature for the final customers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
- 8 out of 10 and took 2 for the data pipeline and administration part. Even if you'd like to improve yourself or your team, you have to pay a lot of money and it could be more than GIAC education + cert. - Normalization for Data models and CPU-based searches can be a problem sometimes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I had a fantastic experience with Splunk Professional Services: they worked with us in our last SON project (a SOC migration for a very large customer) and helped to build a multi tenent environment even if ES isn't a multi tenant platform. Th Splunk PS was a very professional and competent people, he is italian and was able to speak with our italian customers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive ROI from the standpoint of flagging several issues that would have otherwise likely been unaddressed and caused more time to be spent closer to launch
Slightly positive ROI from time-saving perspective (it's an automated check which is nice, but depending on the issues it finds, can take developers time to investigate and resolve)
We have a 100% success rate on all our ES implementations due to the amazing documentation and Splunk enablement on the subject.
Our Splunk ES business has grown 100% YoY for the last 3 years.
In terms of long term management and maintenance, ES has been highly stable and predictable, reducing our overhead on costly services team for ad hoc maintenance work.