AWS Certificate Manager is a service that lets users provision, manage, and deploy public and private Secure Sockets Layer/Transport Layer Security (SSL/TLS) certificates for use with AWS services and internal connected resources.
N/A
AWS Secrets Manager
Score9.8 out of 10
N/A
AWS Secrets Manager enables users to rotate, manage, and retrieve secrets throughout their lifecycle, making it easier to maintain a secure environment that meets security and compliance needs. With Secrets Manager, administrators pay based on the number of secrets stored and API calls made.
$0.05
Per 10,000 API Calls
IBM Vault
Score8.6 out of 10
N/A
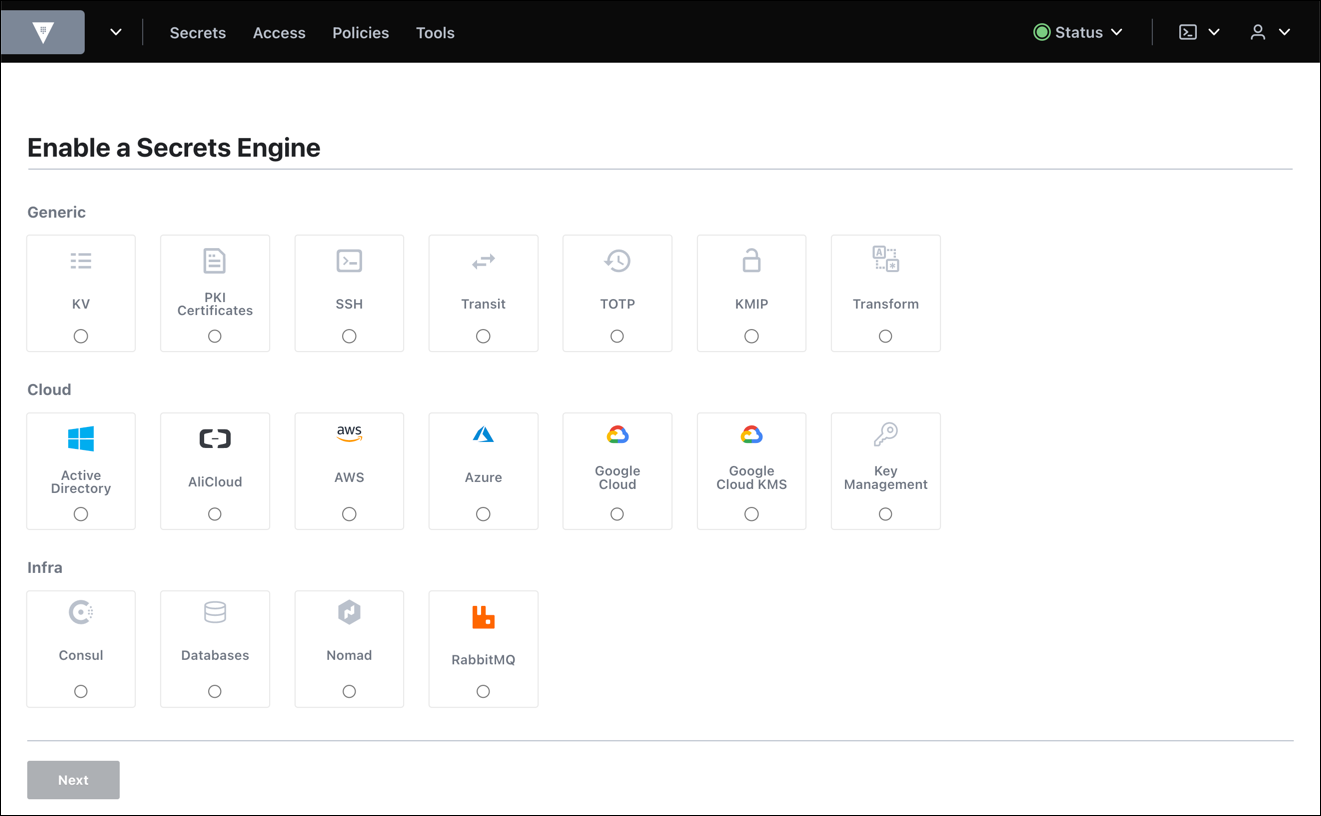
IBM Vault (formerly Hashicorp Vault) is an encryption tool for managing secrets including credentials, passwords and other secrets, providing access control, audit trail, and support for multiple authentication methods. It is available open source, or under an enterprise license.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
DevOps Engineer in Engineering at Kea (Computer Software, 51-200 employees)
Chose IBM Vault
HashiCorp Vault integrates with a lot of tools and systems, and the documentation was pretty robust with a lot of community help. Because HashiCorp Vault is also older than other solutions, it is already well developed with a lot of features you need for storing secrets and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I would always recommend AWS Certificate Manager for anyone using AWS cloud services. The perfect scenario would be with your domain managed by AWS Route 53 as you can obtain auto renewal of certificates with really good security for all your public facing application that uses CloudFront, ALB or API Gateway.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
[AWS Secrets Manager] is really good at managing the secrets for each environment (stage, production, ...), and with a simple command, the users will get all the variables for running the project. Depending on the user role, they could just read and/or edit the variables on the Secrets Manager on AWS. This facilitates the management of the secrets.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
HashiCorp Vault, in my opinion, is a defacto standard for any cloud or automation implementation. They're the best of the best as far as products for secrets management and the ability to use it against relatively any service you have is unheard of for other products. HashiCorp has really taken out all the stops when it comes to creating a nice, extensible tool that people can use to suit their needs.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
HashiCorp Vault is the best there is out there, and it has become critical to our secret management use cases. It would be difficult to find anything that would suit our needs better and that would be beneficial for us to switch over to.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
AWS historically has had very confusing interfaces. But in recent times they have improved them. AWS Certificate Manager is a clear sample of this. The interface is clear and straightforward, with no useless or cryptic options. Really I can't think of a way the interface could be better with the actual options available.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We spent a little more time than we imagined to conceptually understand how HashiCorp Vault operates, as well as how it is configured. This is not trivial, and keep in mind that you will need to take some time to get a thorough understanding of the tool. The documentation could be more helpful in this regard.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
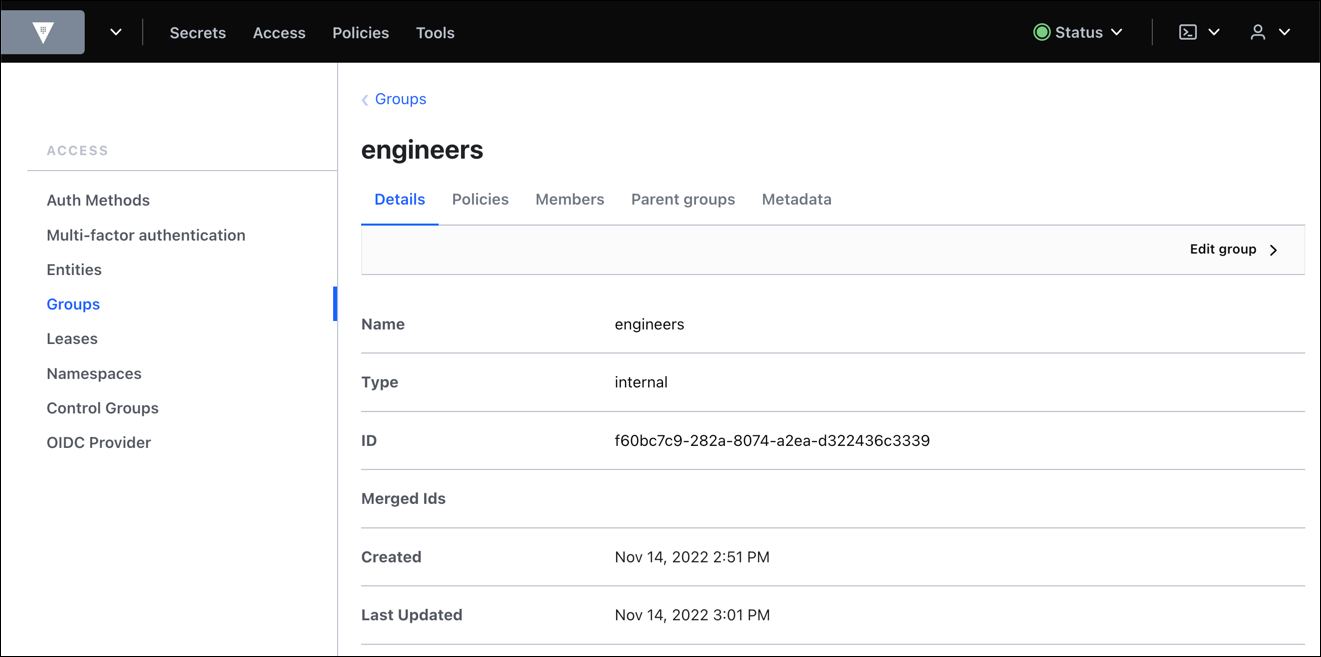
Hashicorp has been very responsive to our questions and inquiries up to this point. We are currently working on them to develop a more granular permissions model within Vault. We are very close to achieving our objectives with the help of their support team. We do not seem to be in the same time zone which makes it hard for escalated issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Easy to implement within a few clicks, or even from command line, the alternatives doesn't integrate that easy with AWS Application Load Balancers or AWS CloudFront
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info