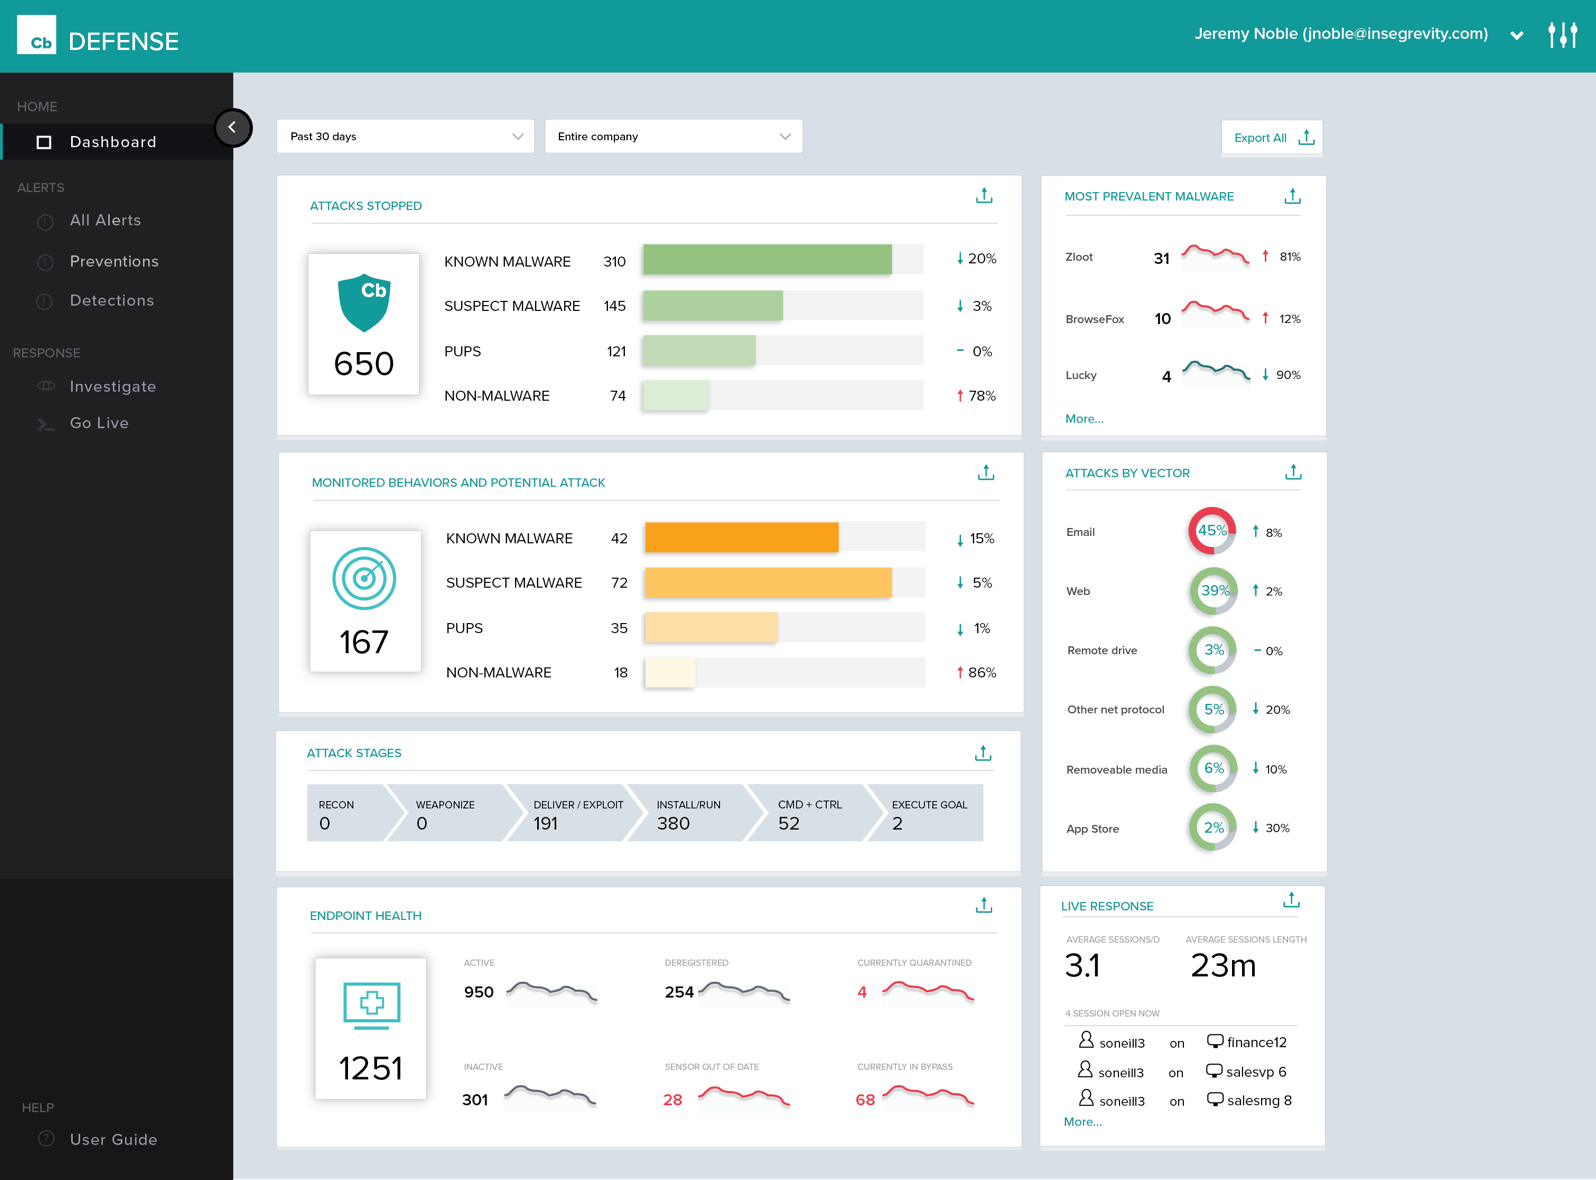
Carbon Black Endpoint is an endpoint security and "next-gen antivirus (NGAV)" that uses machine learning and behavioral models to analyze endpoint data and uncover malicious activity to stop all types of attacks before they reach critical systems.
N/A
Endpoint Protector by CoSoSys
Score9.1 out of 10
N/A
Endpoint Protector by CoSoSys is an all-in-one Data Loss Prevention (DLP) solution for Windows, macOS, and Linux computers, Thin Clients, and Desktop-as-a-Service (DaaS) platforms. The solution protects from data leaks, theft, and exfiltration, it minimizes the risk of insider threats and helps companies to reach compliance with data protection regulations such as the GDPR, CCPA, PCI DSS, HIPAA, and more. It features specialized modules that clients can pick and choose from based on their…
N/A
Pricing
Carbon Black Endpoint
Endpoint Protector by CoSoSys
Editions & Modules
No answers on this topic
No answers on this topic
Offerings
Pricing Offerings
Carbon Black Endpoint
Endpoint Protector by CoSoSys
Free Trial
No
Yes
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
—
More Pricing Information
Features
Carbon Black Endpoint
Endpoint Protector by CoSoSys
Endpoint Security
Comparison of Endpoint Security features of Carbon Black Endpoint and Endpoint Protector by CoSoSys
Feature
Carbon Black Endpoint
9.1
4 Ratings
7% above category average
Endpoint Protector by CoSoSys
-
Ratings
Anti-Exploit Technology
10.04 Ratings
00 Ratings
Endpoint Detection and Response (EDR)
10.04 Ratings
00 Ratings
Centralized Management
8.04 Ratings
00 Ratings
Hybrid Deployment Support
8.02 Ratings
00 Ratings
Infection Remediation
10.04 Ratings
00 Ratings
Vulnerability Management
9.03 Ratings
00 Ratings
Malware Detection
9.04 Ratings
00 Ratings
Data Preparation
Comparison of Data Preparation features of Carbon Black Endpoint and Endpoint Protector by CoSoSys
Cb Defense has been working very well in our organization. It is giving us much better insight into the applications that people are running on their systems (without authorization). This software is also great because it provides visibility into systems that are remote (off the network but still have Internet access). The out of band feature is great to help ensure that the systems are protected even when a user is traveling.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I don't have a single most valuable feature. Every feature is really working for me. One of the reasons I bought it was for the USB block, but that's not as much a use case anymore since I have a lot of people working remotely. It's the DLP part that is more important to me right now, to pinpoint the data that's getting moved. The granularity enables me to not only see a file, but to read inside the file and pull out the data inside it. The granularity is really pretty good on that. It's very important. Let's say somebody just exported a file or emailed a file or uploaded a file on the internet. Seeing the inside of the file is really important to me. Whether it's encrypted or not, I still can see inside the file. I'm the only admin on it, but the role-based access is fine. I have one user that I give access to so he can just see device control and that's it. That's all I need him to see. I was able to do that, so I'm pretty happy with the role-based access. I use the solution's clipboard granularity feature to monitor copying and pasting to specific exit points, and it works great. People are trying to get the data any way they can, from the clipboard and things like that. I'm able to see it, report on it, and block it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
History of Process Execution, really anything that happens in the system is easily seen within the Dashboard. I can determine if a bad actor has infected the system, be it malware, backdoor, rootkit, Trojan, then from that point, I can put the system into Quarantine.
Being able to quarantine the system from the Dashboard. With these type of tools, pulling the power and running a hard drive image is not needed. Put the system in quarantine, start the analysis. A year ago, the network engineer might move the system into a VLAN that has no access to anything, except the system performing the remote analysis... Now I do not have to rely on anyone to move a system, power it down, pull the drive, or image the drive. I can just start the analysis right from my workstation.
The Live Response, again goes hand in hand with the quarantine feature.
By now, I am sure you see a process. Its simple, and easy and all done from a cloud-based console, called the dashboard. .. deploy the agent, create the policy, and active live response, set up email alerts, and monitor your endpoints... you are now ready to perform a triage in the event of an infection. We have step 1, step 2, step 3... but, just remember, things do happen, nothing is perfect, but this product has its advantages.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Policy management can be cumbersome. It is simple to set up a single policy but you have no way to apply the rules to multiple groups. If you need to set up the same rule to multiple policies, you need to type it over again.
Agent updates can be very slow to deploy. We use a mix of rolling out updates via the web console and our management appliance. It can take several weeks to update all agents.
We can be confused on why a rule will apply to a file. Sometimes something is blocked but we don't understand why.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Source code detection is their selling point, they should fix all the problems
Copy/Paste, when you copy paste text, the control applies over the paste, this is correct, but when you copy files, the control is on the copy, not in the paste, so Incan not move protected content not even in a sub folder
Device protection shouldn’t be the main module, there are other software that handle devices, you should focus on DLP
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The console of the product is very easy to use. It provides great detailed information about all aspects of things occurring on the endpoint. It was easy to deploy and set up. The centralized cloud-based interface has made it easy to add two domains and manage them under a single pane with multiple admins. The only reason I wouldn't give it a higher score is a little bit of lag between updated info from the clients and also the lack of accountability in the deployment process. You set the deployment up for multiple machines and can't easily see if it was successful and/or it takes a while to see if it succeeded or failed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
First, I need to disclose that our support is provided by SecureWorks. We purchased CB Defense from them, and they provide 24x7 monitoring and notification services for the solution and its deployment on our endpoints. To date, we are very pleased with this arrangement
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cb is cloud-based and has a more advanced policy management. It also has better forensics information. Cost was similar, but Cb added cost savings in terms of IT management resources. We also have the ability to talk directly with engineers and have input on feature updates.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We've already seen some great return on investments. Endpoint Protector has caught, in it's short time being deployed, a data loss incident we would not have caught otherwise.
Endpoint Protector has given the team leads comfort that the data loss events is being monitored and acted upon.
Endpoint Protector has fulfilled a business objective of protecting intellectual property from leaving the organization through an unauthorized channel.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info