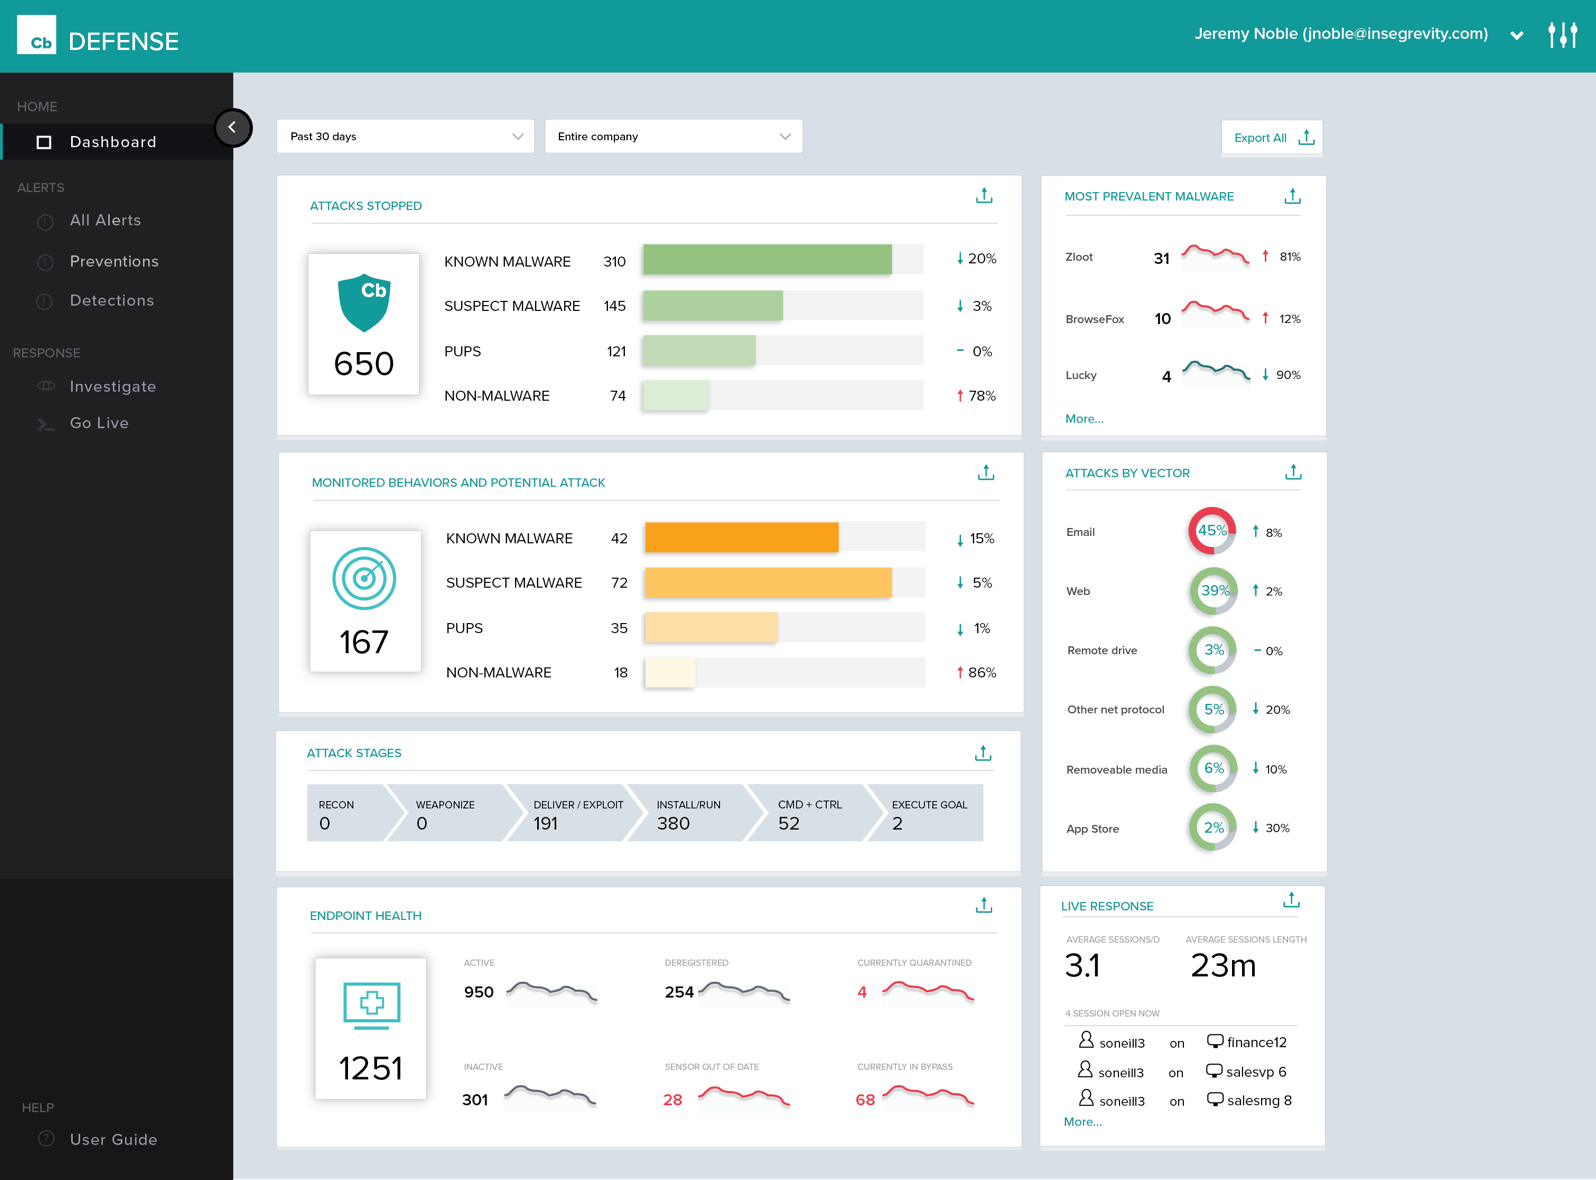
Carbon Black Endpoint is an endpoint security and "next-gen antivirus (NGAV)" that uses machine learning and behavioral models to analyze endpoint data and uncover malicious activity to stop all types of attacks before they reach critical systems.
N/A
Veracode
Score8.5 out of 10
Mid-Size Companies (51-1,000 employees)
Veracode provides advanced application security solutions, trusted by enterprises to develop and maintain secure software. Its platform identifies exploitable risks, speeds up vulnerability remediation, and reduces security debt at scale using a proprietary AI-assisted remediation engine.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cb Defense has been working very well in our organization. It is giving us much better insight into the applications that people are running on their systems (without authorization). This software is also great because it provides visibility into systems that are remote (off the network but still have Internet access). The out of band feature is great to help ensure that the systems are protected even when a user is traveling.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Veracode helped us our team's developers in saving time significantly. For instance, if I take a library and assume it's going to work until it reaches QA or UAT, where we find out there's a vulnerability, that can require extensive effort for code refactoring or redesigning; Veracode helps prevent that before the pull request is merged.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
History of Process Execution, really anything that happens in the system is easily seen within the Dashboard. I can determine if a bad actor has infected the system, be it malware, backdoor, rootkit, Trojan, then from that point, I can put the system into Quarantine.
Being able to quarantine the system from the Dashboard. With these type of tools, pulling the power and running a hard drive image is not needed. Put the system in quarantine, start the analysis. A year ago, the network engineer might move the system into a VLAN that has no access to anything, except the system performing the remote analysis... Now I do not have to rely on anyone to move a system, power it down, pull the drive, or image the drive. I can just start the analysis right from my workstation.
The Live Response, again goes hand in hand with the quarantine feature.
By now, I am sure you see a process. Its simple, and easy and all done from a cloud-based console, called the dashboard. .. deploy the agent, create the policy, and active live response, set up email alerts, and monitor your endpoints... you are now ready to perform a triage in the event of an infection. We have step 1, step 2, step 3... but, just remember, things do happen, nothing is perfect, but this product has its advantages.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is good at recommending fixing issues with third-party dependencies used in application code with detailed version information and knowing which version fixes what.
It has a very nice interface for triaging flaws. One can sort the vulnerabilities found in code from Very Likely to be exploited to least likely to be exploited.
There is a collections feature that allows us to group together groups of application profiles belonging to the same suite of applications.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Policy management can be cumbersome. It is simple to set up a single policy but you have no way to apply the rules to multiple groups. If you need to set up the same rule to multiple policies, you need to type it over again.
Agent updates can be very slow to deploy. We use a mix of rolling out updates via the web console and our management appliance. It can take several weeks to update all agents.
We can be confused on why a rule will apply to a file. Sometimes something is blocked but we don't understand why.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
At this time, and we just renewed a month ago, I dont see any products out there overall that can offer what Veracode does. Yes, its not cheap by any means, but for the money its the best application security scanning tool out there.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The console of the product is very easy to use. It provides great detailed information about all aspects of things occurring on the endpoint. It was easy to deploy and set up. The centralized cloud-based interface has made it easy to add two domains and manage them under a single pane with multiple admins. The only reason I wouldn't give it a higher score is a little bit of lag between updated info from the clients and also the lack of accountability in the deployment process. You set the deployment up for multiple machines and can't easily see if it was successful and/or it takes a while to see if it succeeded or failed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
- Almost no setup required and easy to configure - Very easy to use, intuitive UI with integrated analytics and learning portals. - Seamless to review the results, triage them, generate reports. - Security progression of the product/application is tracked via successive scans. - Privileges/Roles nicely fine grained and tightly controlled to let teams "view" only their products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
First, I need to disclose that our support is provided by SecureWorks. We purchased CB Defense from them, and they provide 24x7 monitoring and notification services for the solution and its deployment on our endpoints. To date, we are very pleased with this arrangement
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Overall, Veracode support is helpful, community support is great, and documentation is available for self-service. Our Customer Success Manager is very helpful and reaches out regularly to see if we need assistance. We have not utilized many of the other resources offered by Veracode, however, in the future we would like to leverage secure coding training for our Development teams.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We use it as a SAS service, so really just getting our teams to mold the use of Veracode into their SDLC has been a process of years in the making. It comes down to what your teams are ready and willing to accept and change. Management is key in getting their groups on board with using it regularly. If it doesnt have management backing, your security teams have little to no influence in getting this process off the ground fully.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cb is cloud-based and has a more advanced policy management. It also has better forensics information. Cost was similar, but Cb added cost savings in terms of IT management resources. We also have the ability to talk directly with engineers and have input on feature updates.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Veracode is slower with scan results however the flaws discovered and sites crawled are almost the same. Rapid7 InsightAppSec only does dynamic scans. Veracode did find more links on a site crawl. Rapid7 InsightAppSec has more out of the box reports than Veracode. Both integration to DevOps tools were striaghtforward.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Positive: Scanning all our applications on Veracode provides us an overview of our cyber security posture for the organization as a whole.
Positive: Performing the SAST, SCA and DAST scanning for all the applications at the early stages of the SDLC helps us identify and mitigate security vulnerabilities early, reducing the risk of data breaches and cyber-attacks.
Negative: Sometimes Veracode SAST scanner closed and reopens some findings, leading to reliability issues on the scanner itself.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info