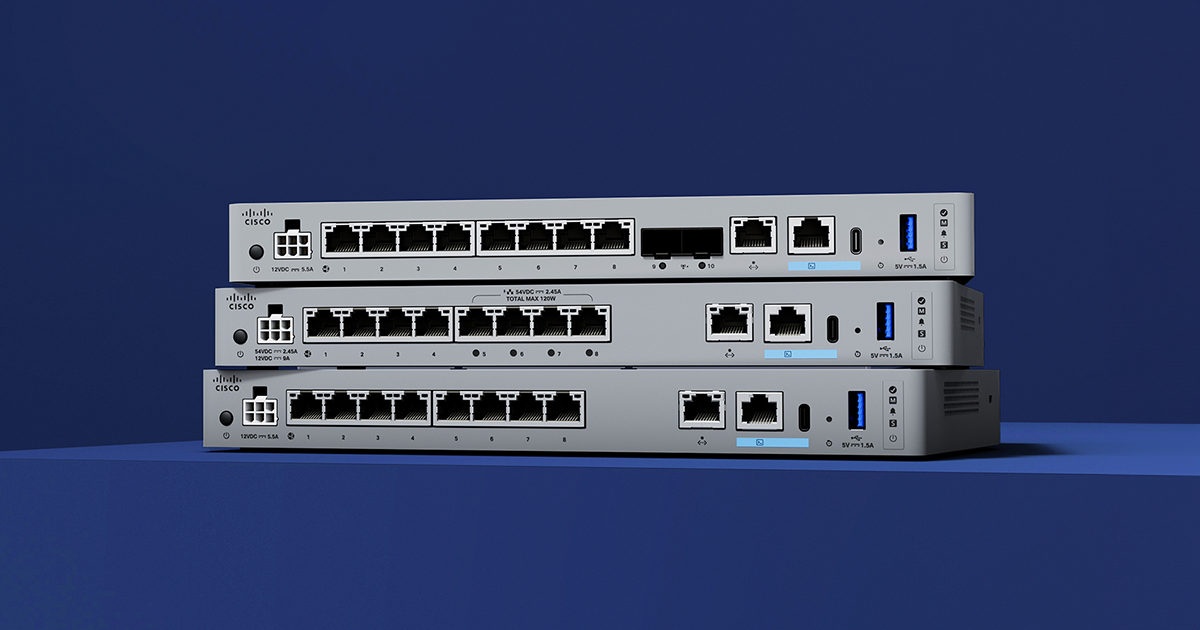
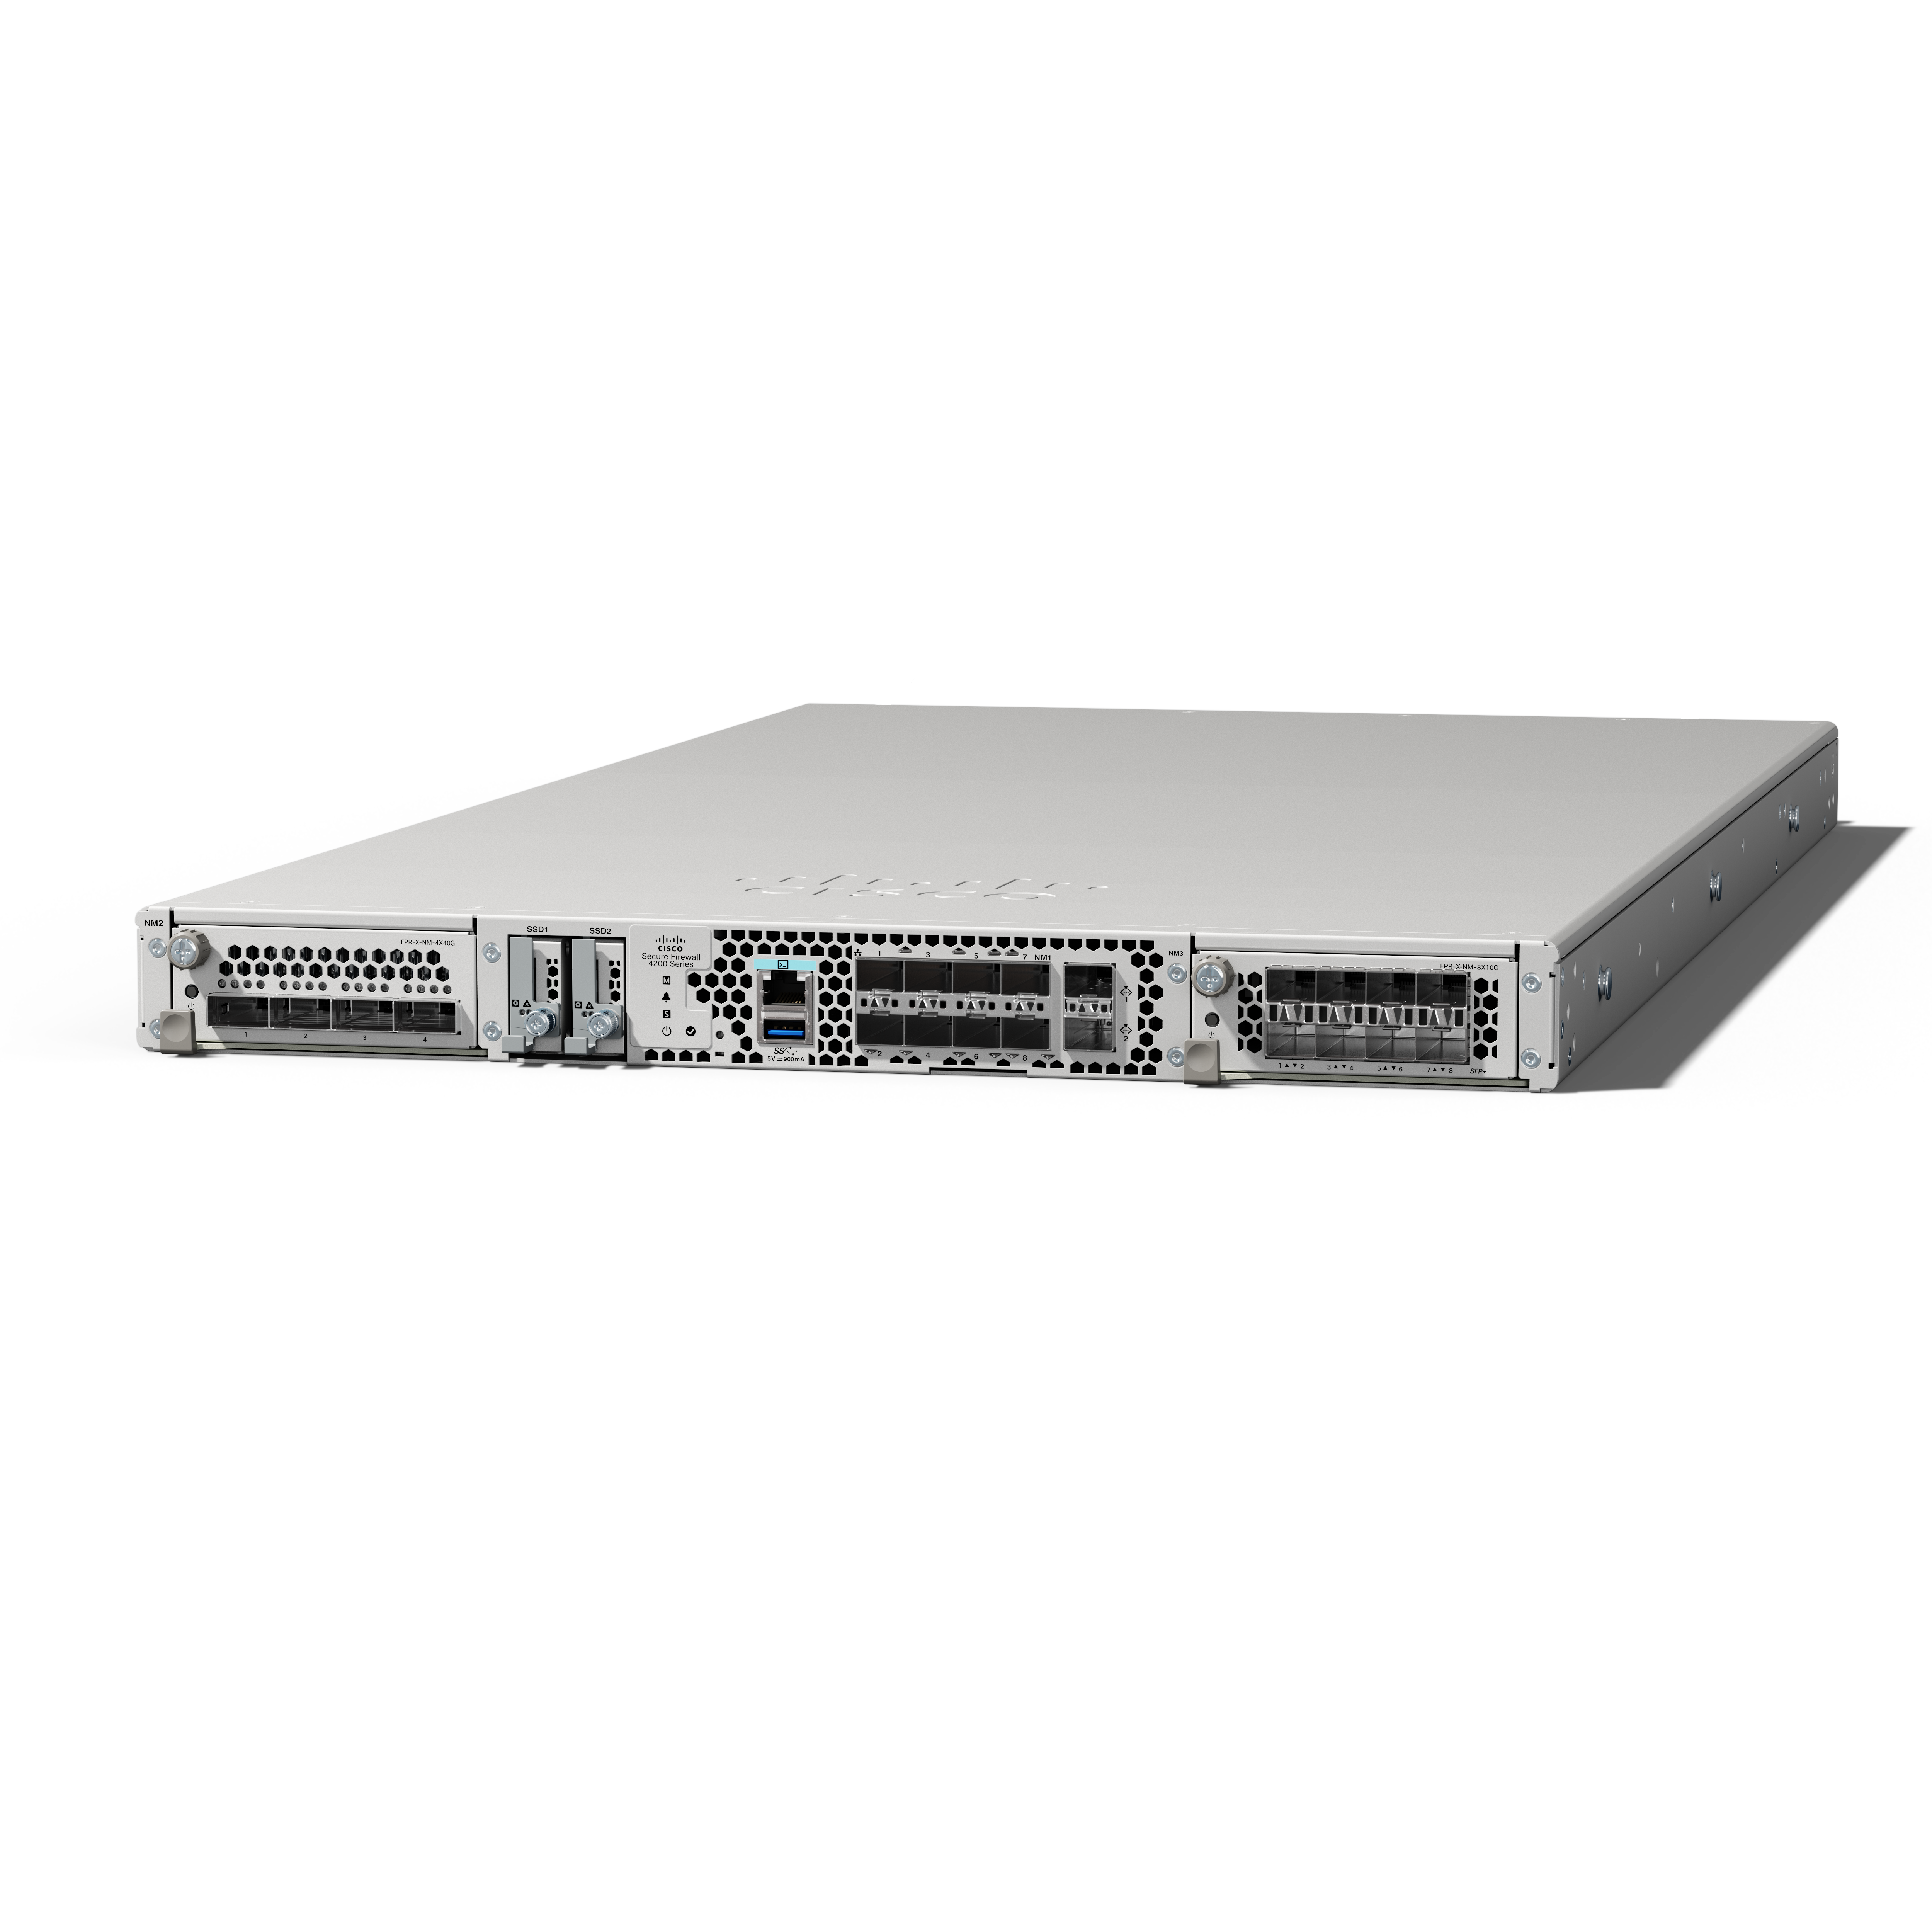
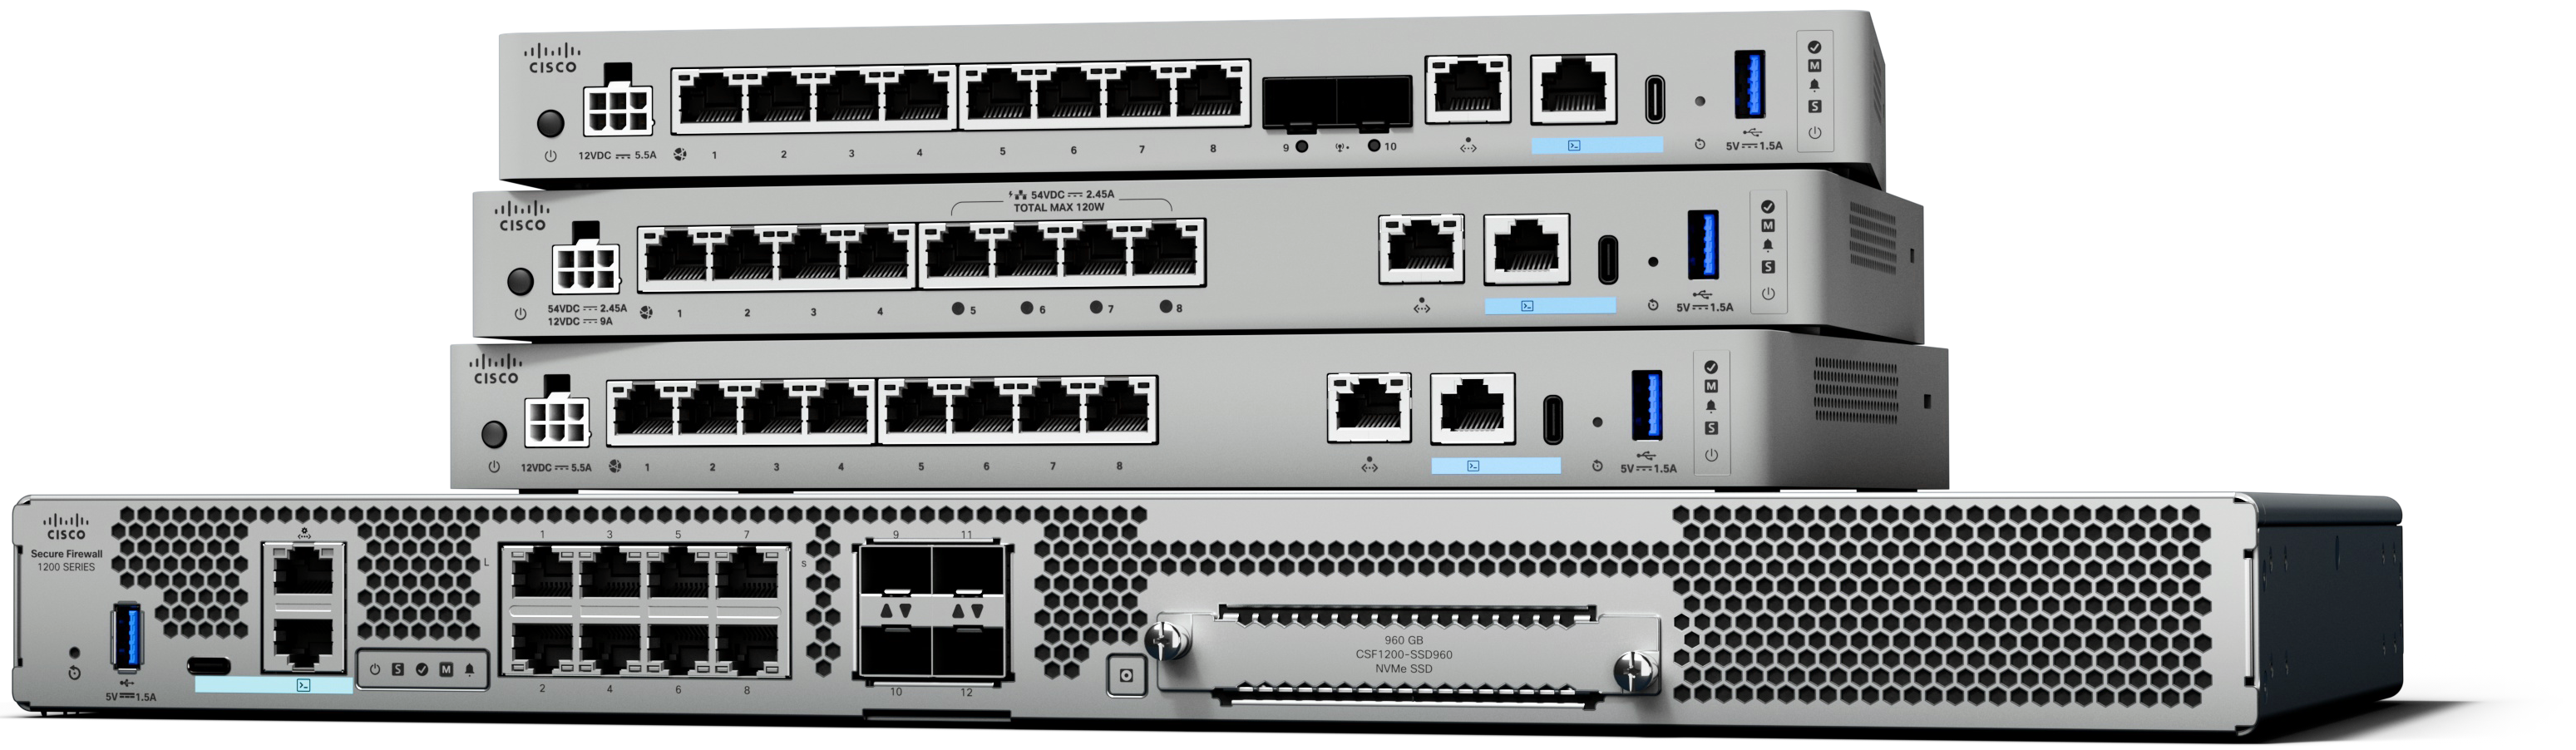
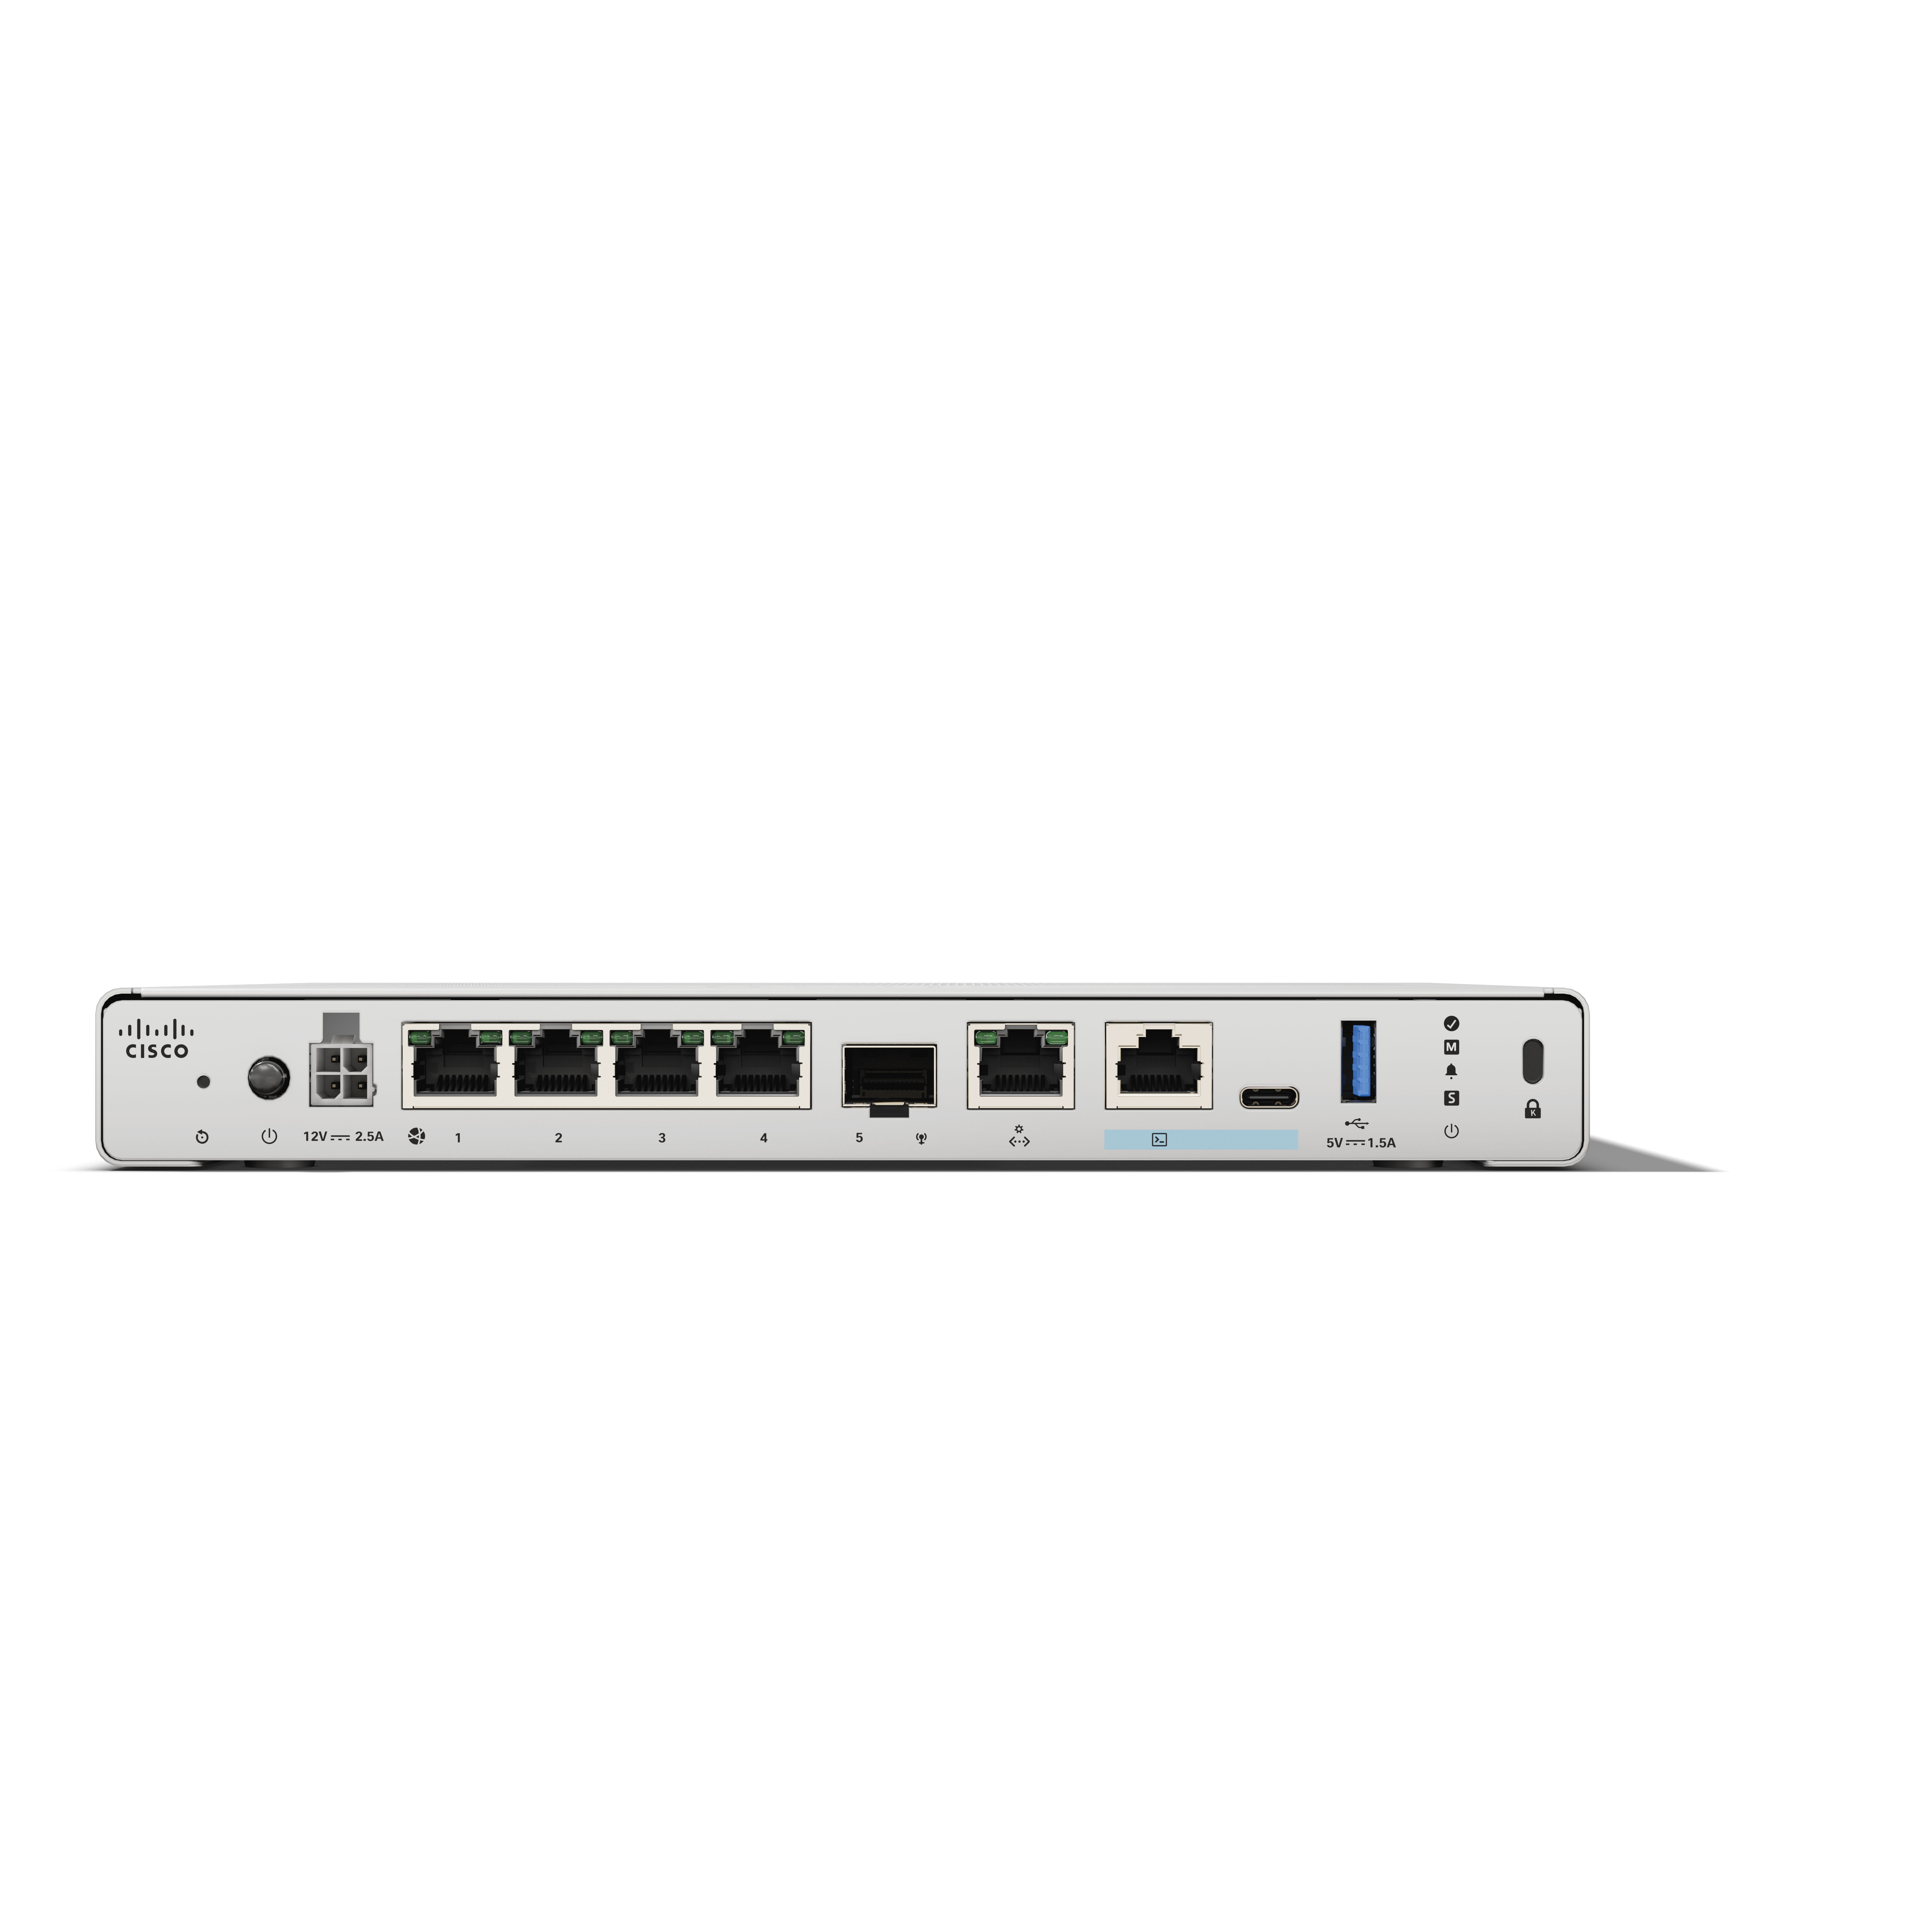
Cisco Secure Firewall delivers comprehensive threat protection for modern, distributed networks. Built to support hybrid workforces and multicloud environments, it enables Zero Trust access, application visibility, and secure remote connectivity. With integration across the Cisco Secure portfolio, including SecureX and Talos threat intelligence, the firewall powers organizations to detect and stop more sophisticated threats. Centralized management simplifies policy enforcement, orchestration,…
N/A
CrowdSec
Score7.9 out of 10
N/A
CrowdSec is a CTI tool leveraging crowdsourced data to identify and block malevolent IPs in real time worldwide. It is an open-source & collaborative IPS able to analyze visitor behavior by parsing logs & provide an adapted response to all kinds of attacks. It also enables users to protect each other. Each time an IP is blocked, all community members are informed so they can also block it. That way, they are generating a real-time crowdsourced CTI database.
I can't think of scenarios where it is less appropriate, unless we are talking about real tiny businesses. More businesses will find Cisco Secure Firewall an outstanding tool to use, love, and trust from a reputable Network giant vendor. It is a must for businesses that want to focus on what they are doing, and leaving the network security for the pros.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Since I've only used CrowdSec in a homelab/small-medium sized business setup, that's really the only market I can safely recommend it and say it's well suited for, because I don't know how much it would cost to run it in an enterprise environment. I've heard some pricing and how they plan on rolling out a subscription model, but it's still in talks. Either way, if you have publicly exposed web applications hosted locally or on a virtual private server, then CrowdSec should be part of every virtual machine and/or network. Even with the lmited number of filter you get out of the free subscription, it provides a nice layer of constantly updated data,
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco's firewall actually does its job of blocking what it is supposed to block. We had an old Firewall that led to slippages. Cisco catches 97% of malware and vulnerabilities during testing. For Coitiar, that means an engineer who clicks a link with malware is handled quickly.
We actually tested if failovers would affect running sessions. We pulled our primary unit during a certification submission period. The firewall just switched, and the connection kept running.
The AI assistant in policy management is excellent, and for our lean team, it makes the whole process easy and efficient. I don't have to audit 200 policies manually; the AI steps in and does its thing.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Provides great integrations with tools you already use, such as fail2ban, Cloudflare, WordPress, NGINX, Linux Firewalls, etc.
Lightweight agents can run on individual servers and report to a main security engine so that if there's an attack on one server and a block is implemented, the entire network can be protected
There are a lot of ways to receive alerts and store logs
CrowdSec Central API is a nice way to manage everything externally
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I mean I think a lot of the technology with managing them is getting better. There's a few cons to the new firewall management console. You can't sort through routes or I think you can with interfaces now, but there's a few caveats that they haven't really worked out yet, but they're implementing AI into it, so it's getting to be a lot easier to use.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Getting CrowdSec to run on OPNsense can be a challenge, but that's also a limitation of the OS
You can only subscribe to a couple of feeds before paying an unknown amount of money that's part of their "Enterprise" package. So, there could be better transparency.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It works really well. We can do most anything we want or need to with it, and you don’t have to have a doctorate or multiple certs to necessarily figure it out. The thing that would probably have to happen to make us switch would be if we just got priced out - Cisco’s more powerful and higher bandwidth models cost a pretty penny.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
i think overall after ALOT of tac cases it works allright now. But still have alot of issues if you use cloud based mangement. fx, if you open 2 windows of access policys, both of the pages, rules starte to jump form side to side. if you then open one more list, its start to jump even faster. if you close the 2 of them, its back to normal. ALSO the extended access lists for VPN, SUCKS. Its the tiniest window when opening the editor, and you are not able to give the rules names, Which means finding and editing rules SUCKS, its a horrible experience, and eveytime we have to we want to yell :P
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We have not had any performance issues with Cisco Secure Firewall, even with DPI and IPS enabled, we have not seen a performance hit. Emoployes have not complained about any slow network speeds that could have been attributed to the secure firewall it has always been something else within the office network.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I rarely get the support I need in the time I need it. Often, while they are "looking at packet captures and going to get back to me" I fix the problem on my own. If you were to look at my TAC cases over the past year, you would see some very lengthy cases that usually ended with me contacting the TAC person and telling them to just close the case
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
was a good training but questions was answered not so good. Training was "Fundamentals of Cisco Firewall Threat Defense and Intrusion Prevention (SFWIPF)".
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Our initial implementation was aided by Cisco's professional services and was excellent. The engineer was very knowledgeable and helped us work through issues while building out our new internet security edge Part of this involved tools to migrate the firewall configuration from old to new.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Firewall works better with the Cisco ecosystem when we can utilize it and feels beefy enough when we utilize it in the data center. The Fortinet we have found are great, small cost boxes for remote offices with a better UI then Cisco Secure Firewalls. The feature set included with the firewalls feels similar from a security point of view.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A solid, realistic rating most people give for Cisco Secure Firewall pricing is 7 or 8 out of 10 (because the product is strong but licensing can be a bit complex)
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Firewall has never given us any trouble, it has stayed up at all times, upgrading the appliance has also become much simpler. We operate the appliance in a HA pair, so 0% downtime within our organisation. During switchover while upgrading, not a single packet seems to get lost, so this has been a very valuable asset to our company.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info