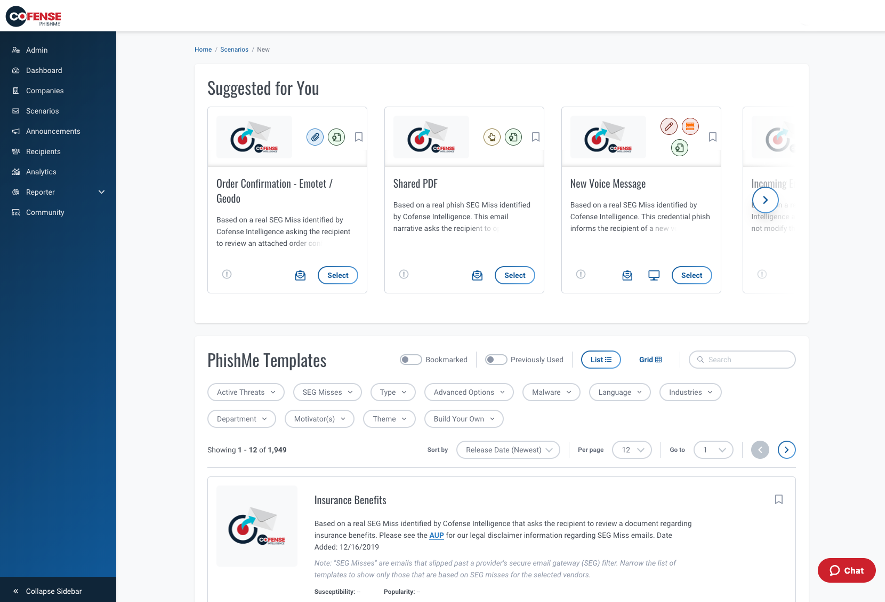
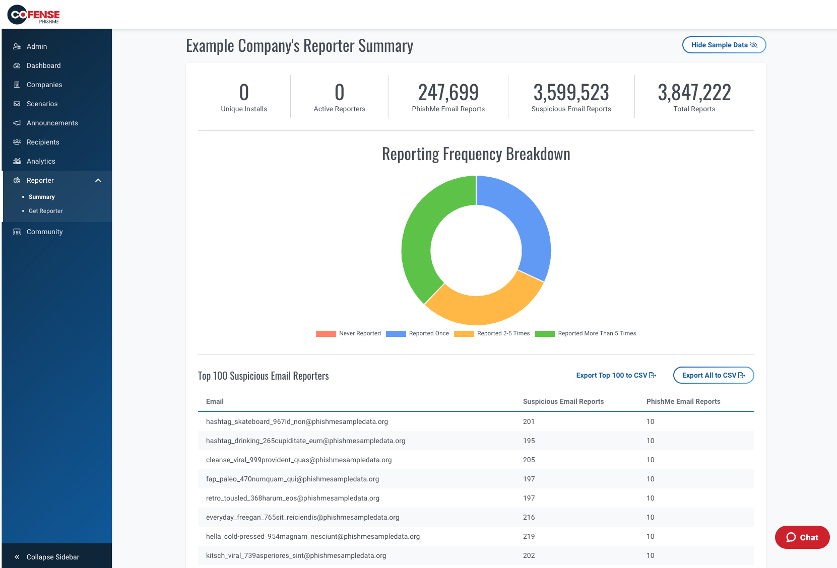
Cofense PhishMe is a cyber threat and phishing simulator meant to be of use in training employees to be wary against threats and also to gain information about general employee threat knowledge and preparedness. A free trial is available for small business.
N/A
Microsoft System Center
Score8.4 out of 10
N/A
Microsoft System Center is an enterprise-grade IT Operations Management (ITOM) suite designed for the centralized administration of data center infrastructure, virtualized environments, and hybrid cloud workloads. The platform provides unified management across heterogeneous environments, including support for Windows Server, Linux, and Azure Stack HCI.
System Center is Microsoft's ITOM stack for organizations that maintain a significant on-premise footprint, vs the company's Azure-based…
Cofense PhishMe is an excellent solution for scenarios where it will be sold as a managed service. I believe that PhishMe is too expensive for many clients and instead would benefit from the economies of scale where an MSSP sells it as part of a whole service, which offers the analysts and reporting included. PhishMe is excellent for training and awareness of Phishing, but shouldn't replace mandatory training for new joiners or yearly refreshers, it should only be used as an additional training option.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
For companies with more than 10 Windows devices and needing to standardize the OS, AV, access, share resources, and install software. SCCM is the way to go. This software is unnecessary if the business is all remote users and not in an office-type setting. There are cloud offerings or none to accomplish what a business needs.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It gives clear-cut segregation of different parts of an email, header, text and HTML body, URL, attachments, HTML preview and some analytical insight like "similar reports." This distinctive approach actually helps reduce data overload during an analysis.
The URLs captured here pass through an automatic reputation check [in our case VirusTotal] and add a tag of the reputation. If it is a well-known bad URL the tag helps us take the decision fast.
For creating automation rules on the reported emails the "Recipes" section is really helpful. We can create easy recipes [or rules ] to handle a huge flow of reports and also we can create more sophisticated rules depending on the Cyber intelligence feed to catch the really bad currently less known attack attempts by malicious emails.
The "Threat Indicators" section is also useful to use as a threat intelligence source to check the URLs for their maliciousness.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The product could improve in the area of having better mechanisms in place with how the SCEP client is deployed/installed from the server on the management side. We have run into this firsthand with the client not installing on an endpoint, and then having to take the time to investigate why it was not installing.
A second improvement that can be made is to keep trying to improve the products detection rate for finding malware/viruses. The case can be made that there are some products out there that do a better job at this and have a higher detection rate.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Its built with UX in mind and is aimed at non-tech people, to ensure that almost everyone can run the campaign. But if we go deeper - sometimes you will need an HTML editor or support in order to figure out some advanced edits you might want to add in your scenarios.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is not user-friendly for the most part. With IT infrastructure, sometimes it cannot handle excess requests. Every few months, you will need an upgrade in terms of server resources to keep up with incoming alerts and requests. This does not happen all of the time, but it does happen when there are too many requests.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have not had to use their support for pretty much anything. The software works well, and is very intuitive. I would imagine their support would be rather basic as there is not too much that can go wrong with a report phishing button, and if it were I would probably consider a different software.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
There is a fair amount of documentation out there to help you when you have questions or run into issues with this product as well as tutorials on some of the more common tasks. Between the documentation and the overall ease of use we haven't had to deal with direct Microsoft support for this product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cofense PhishMe was the first choice for us as the user interface as well as their bundle package with Cofense Triage and Vision has helped the organisation to alleviate the overall security awareness posture. The other vendors did not provide a vast range of phishing scenarios as compared to Cofense PhishMe platform.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
We previously used a mix of FOG and Clonezilla to image machines. The biggest issues with these products is that changing one piece of the image required you to rebuild the entire image itself. These pieces of software also did not allow you to manage applications and Windows Updates, causing IT to have to constantly touch machines after they were imaged and update or manage them with a much more hands on approach.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Recipes in the system are capable of handling almost 2x what an analyst does, which cuts down the efforts [of] an analyst and provides more time for accurate strategies.
With roughly 90% false positives coming through, the remaining 10% of true positives need as much attention as they can get for the full investigation and analysis.
1,500 or more phishing messages can come through in a given week and the amount of time/employees required to review this without a tool like Cofense is surely beyond [the] expected/anticipated budget.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info