The Forcepoint ONE Secure Web Gateway (SWG) is one of the three foundational gateways of the Forcepoint ONE all-in-one cloud platform. Forcepoint ONE SWG monitors and controlsany interaction with any website, including blocking access to websites based on category and risk score, blocking download of malware, blocking upload of sensitive data to personal filesharing accounts, detecting shadow IT, and optionally providingRemote Browser Isolation (RBI) with Content Disarm andReconstruction (CDR).
N/A
Microsoft Defender for Cloud
Score8.7 out of 10
N/A
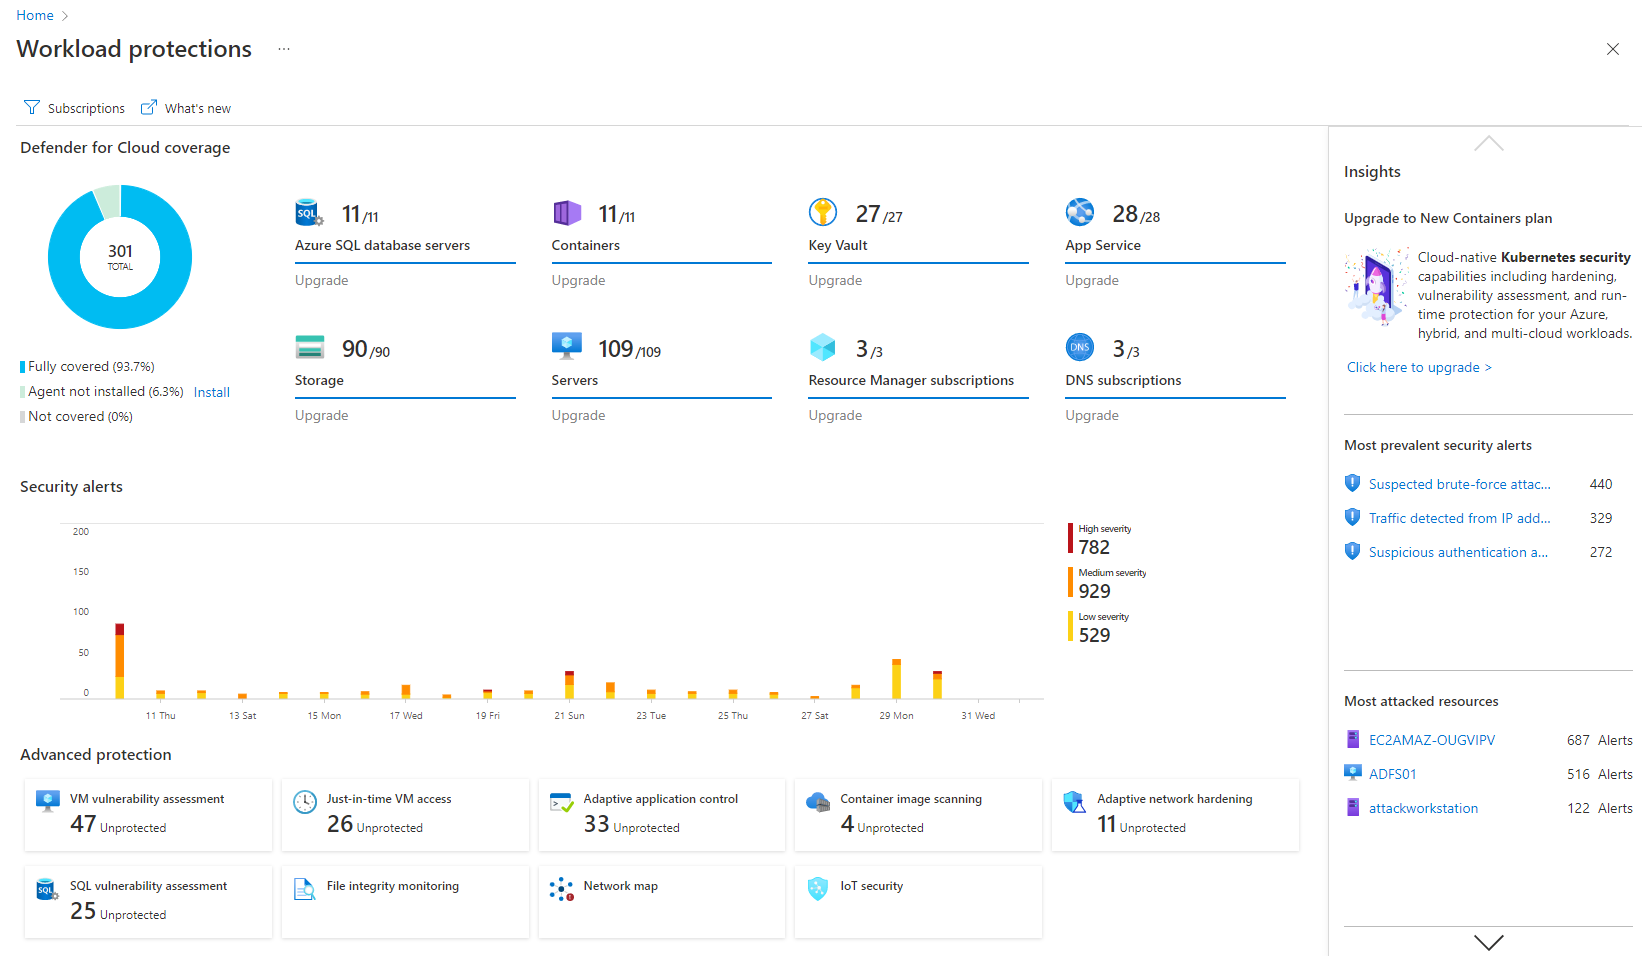
Microsoft Defender for Cloud is a Cloud Security Posture Management (CSPM) and Cloud Workload Protection Platform (CWPP) for Azure, on-premises, and multicloud (Amazon AWS and Google GCP) resources.
Over the years, [in our experience], the maintenance of the Forcepoint Web Security solution proved to be more cumbersome and troublesome with each version upgrade. In addition, it did not transition well to support the large increase of remote workers. We also experienced weird incompatibilities with the client. We have since replaced this solution with Zscaler Internet Access, a cloud-based secure web gateway solution with a client that behaves as expected, is more flexible, and requires significantly less administration.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I think it's good for cloud-native companies. A company that, from day zero, they're like, "We're going cloud, and this is how we're going to do it." They get it. It works well for them. Smaller organizations that are under X amount of resources- I don't know what that X might mean- but I feel like it plays well in smaller, more nimble organizations. If you're an older organization or if you're extremely large, it starts becoming a little difficult to manage at scale. And you have to sometimes throw bodies at the problem. Maybe not the most eloquent way of saying it, but that's what it feels like.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It's really well laid out, with an easy-to-use, accessible UI.
With Microsoft Defender for Cloud, it has everything you need with the Safelink attachment, the Safelink emails for URL, the way it scans those URLs and attachments within the product, and you're seeing the results. And that adds an extra layer of security for the user, so you feel comfortable knowing the product monitors those. That's something I really like about that product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The user access logs contain a lot of useless information. I understand this is very hard to tackle as I've seen this across any product that logs web activity.
I would like to see more customization options of website block pages.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Integrations with on-premise workloads can sometimes be challenging. Needs improvement and well standardised integration points
Vulnerability categories can be difficult to understand. It should allow teams to focus on critical findings and help them keep aside low-severity or suppressed vulnerabilities
Pricing can be improved as it can be over-priced for smaller businesses and would potentially affect their ROI due to the small scale
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It is very stable, the organisation has "locked in" the product and has no plans to change or try another product. We have already renewed our 2019-2020 licenses. It is user friendly and people catch on easily when they first use it. The only downtime is when we install Microsoft updates! It has excellent reporting which help in determining how the organisation's Internet is used and also during both internal and external IT audits.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It is a great product that integrates nicely when running an Azure platform and even multi-cloud environment. Not looking for point-solutions but a suite that answers most requirements. It is very comfortable being able to use KQL, workbooks and automation that is native to the azure platform
Despite the intimidating Linux CLI when you use the appliance for troubleshooting, the web security usability compensates as most of the Administration of the system is done there. It is GUI based and has an easy to use UI where one can navigate around rather easily like getting reports, checking alerts, looking the whole setup under deployment to check if all services are running in one place though there are other parts to the system.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
My visibility is limited because I'm only doing very small pieces of what the overall org does. And also, we have limitations on what we're allowed to use. It's not like we get a new product as users or leadership level users, and everything is on, and we can just do whatever we want. We're very restricted in what we can use any tooling within the org because of the different levels of regulatory constraints we have, because of just the nature of who we are inherently. So that's why. I don't think it's necessarily the product. I think it's more or less of what we're able to do with the product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The is a quick first response to acknowledge your issue and the Engineers never take more than two hours to fix an issue and we hardly get issues looking at the fact that the system is pretty stable. There is also a robust Knowledge Base in the site for known problems.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Research known issues with upgrading from the Support Knowledge base, this will enable you avoid road blocks along the way and reduce your dependence on Forcepoint Support
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
To be honest, once using Forcepoint for our Web Security, I have not wanted to look anywhere else. The dashboard gives me quick insight of threats, productivity, and bandwidth usage. Again, this is a layer in my security and it fills many holes. I feel safe and I do like I can just let it do its thing
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe Microsoft Defender for Cloud stacks up well against the other tools we looked at. It is native to the Azure platform and provides the same insights as the other tools. We selected Microsoft Defender for Cloud because it integrates well with the Azure resources and gives the needed insight, security alerts and recommendations.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Being a non-profit the cost is a bit higher than some competitors so our ROI takes a bit longer to recoup. I would really like to see better non-profit pricing.
The ease of doing a report on someone cuts down on the IT man-hours to do website tracking for managers as we can do it from a central point whereas in the past (prior to Forcepoint/Websense) we would have to ghost their machine to look for activity as well as their local servers.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info